
Keytos Cloud PKI, RADIUS, and Smart Cards Now Available in Azure GCC High
 Keytos Team |
Keytos Security Brings Cloud PKI, Cloud RADIUS, and Smart Cards to Azure GCC High
For the first time in Azure GCC High, you can deploy native cloud PKI, cloud RADIUS, and smart card solutions without the need for self-hosted infrastructure or bloated contracts that charge you extra just because you’re in a government cloud. In just a few clicks, you can deploy Keytos Shield for a complete passwordless solution, or you can deploy EZCA for cloud PKI or EZRADIUS for cloud RADIUS separately.
Keytos Provides the Only Cloud PKI Solution for Azure GCC High
For the first time, Azure GCC High tenants can leverage a fully cloud-native PKI solution without the need for on-premises infrastructure or complex self-hosted setups. Simply deploy Shield or EZCA in a few clicks, connect them to your GCC High Entra ID tenant, and you can begin issuing certificates in minutes.
Since Microsoft Cloud PKI is not available in GCC High, EZCA and Shield bridge this gap by providing a fully cloud-native PKI solution that meets the unique requirements of GCC High tenants. Both solutions work across Intune and 3rd party MDM solutions to make sure the complete end-to-end solution never leaves your GCC High environment.
Keytos Provides the Only Cloud RADIUS Solution for Azure GCC High
Since Microsoft Intune doesn’t have a cloud RADIUS solution in either commercial or government clouds, GCC High tenants have historically been forced to rely on self-hosted NPS servers or third-party solutions that are not fully integrated into the government cloud environment. Shield + EZRADIUS fills this gap by providing a fully cloud-native RADIUS solution specifically designed for Azure GCC High.
Authenticate to your mission-critical networks using your existing GCC High credentials, or using your PKI certificates issued by EZCA, Shield, or your existing on-premises PKI. All authentications and data remain in your gov cloud environment, ensuring compliance and security for sensitive government workloads.
Keytos Provides the Only Smart Card and Passkey Onboarding Solution for Azure GCC High
For your most mission critical and privileged accounts, hardware security keys like YubiKeys and other FIDO2-compliant devices can be used to provide strong, phishing-resistant authentication. Coming soon, Keytos Shield will enable seamless onboarding of these security keys within the Azure GCC High environment for your GCC High Entra ID users, ensuring that your sensitive accounts are protected without compromising compliance or security. Stay tuned for updates on how you can easily move to Certificate Based Authentication (CBA) and modern passkey based authentication using Shield.
What is the Azure GCC High Cloud?
Azure GCC High (Government Community Cloud High) is a separate instance of Microsoft Azure that runs in dedicated US data centers, and is built for organizations handling sensitive government data, primarily defense contractors and organizations supporting the Department of Defense. Users within the GCC High environment must meet strict personnel and residency requirements, such as being United States citizens.
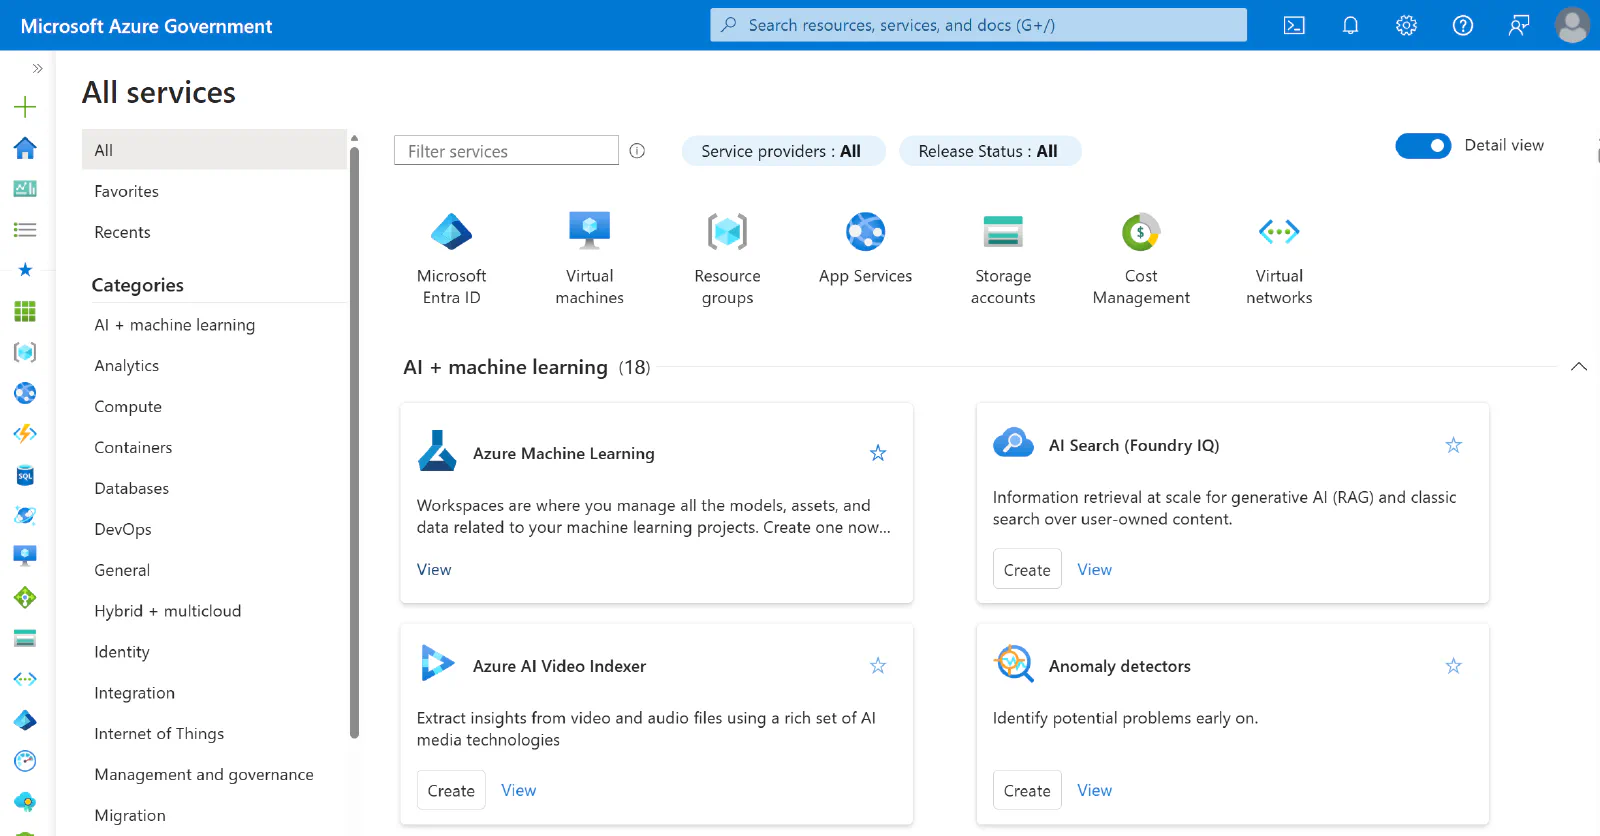
Azure GCC High operates as a completely separate instance from commercial Azure, with its own dedicated infrastructure, endpoints, Entra ID service, and compliance controls tailored to meet the stringent requirements of US government agencies and contractors. If you’ve used commercial Azure, you’ll notice that many familiar services and features are either absent or implemented differently to comply with government regulations and security standards.
Is Microsoft Cloud PKI Available in GCC High?
No. As of this writing, Microsoft Cloud PKI is not available in the Azure GCC High environment, leaving tenants to rely on self-hosted or third-party solutions for their PKI needs. While they have cloud PKI in their backlog, there is no publicly available timeline for its release in GCC High.
For defense contractors and other organizations handling sensitive government data, this means that implementing a fully cloud-native PKI or RADIUS solution within GCC High has historically been challenging, requiring significant investment in self-hosted infrastructure and specialized personnel. Shield and EZCA now provide a purpose-built solution to address this gap, enabling GCC High tenants to achieve secure, compliant, and scalable certificate-based authentication without the overhead of managing on-premises infrastructure themselves.
Was There a Cloud RADIUS Solution in GCC High?
No. Up until now, there has not been a native cloud RADIUS solution available in the Azure GCC High environment. Organizations have had to rely on self-hosted or third-party RADIUS solutions to meet their authentication needs. Shield and EZRADIUS aim to fill this gap by providing a fully cloud-native RADIUS solution tailored for GCC High tenants.
Both services provide a cloud RADIUS and RadSec endpoint that you can point your networks to, and begin authenticating using Entra ID credentials or certificate-based authentication in minutes. This eliminates the need for maintaining on-premises RADIUS infrastructure while ensuring secure and compliant access for your GCC High environment.
How Does Keytos Work in Azure GCC High?
Every Keytos solution is built by ex-Microsoft engineers to be native to the Azure GCC High environment, ensuring seamless integration with the unique compliance, security, and operational requirements of US government cloud tenants. This includes using native Entra ID authentication instead of manual integrations or secrets management, natively connecting to Microsoft Graph endpoints for Entra ID and Intune, and adhering to the strict data residency and personnel requirements mandated for GCC High environments.
Can I Migrate Off AD CS (Active Directory Certificate Services) in Azure GCC High?
Yes! With EZCA and Keytos Shield available in GCC High, organizations can migrate off of AD CS and adopt a fully cloud-native PKI and RADIUS solution, reducing the operational overhead and complexity associated with self-hosted infrastructure. This allows GCC High tenants to implement certificate-based authentication and Zero Trust network access without needing to maintain on-premises PKI or RADIUS servers/VMs.
Shield and EZCA support all the most popular certificate issuance protocols, including SCEP, EST, and ACME, ensuring compatibility with a wide range of devices and applications commonly used in enterprise and government environments. This allows GCC High tenants to seamlessly integrate cloud-native PKI and RADIUS solutions into their existing infrastructure while maintaining compliance with stringent security requirements.
Learn how to migrate off of AD CSCan I Migrate Off NPS (Network Policy Server) in Azure GCC High?
Yes! With EZRADIUS and Keytos Shield available in GCC High, organizations can migrate off of NPS and adopt a fully cloud-native RADIUS solution, reducing the operational overhead and complexity associated with self-hosted infrastructure. This allows GCC High tenants to implement certificate-based authentication and Zero Trust network access without needing to maintain on-premises NPS servers/VMs.
Shield and EZRADIUS support all the most popular RADIUS authentication protocols, including EAP-TLS, PEAP, and EAP-TTLS, ensuring compatibility with a wide range of network devices and client platforms commonly used in enterprise and government environments. This allows GCC High tenants to seamlessly integrate cloud-native RADIUS solutions into their existing network infrastructure while maintaining compliance with stringent security requirements.
Learn how to migrate off of NPSCan I Meet CMMC Requirements in Azure GCC High with Keytos?
Yes! Azure GCC High is designed to help organizations meet stringent government compliance requirements, including the Cybersecurity Maturity Model Certification (CMMC). By leveraging Keytos solutions in GCC High, organizations can implement secure, compliant, and fully cloud-native PKI and RADIUS solutions that align with CMMC standards, ensuring the protection of Controlled Unclassified Information (CUI) and other sensitive government data.
Learn how Keytos helps meet CMMC requirementsHow Much Does Cloud PKI and Cloud RADIUS Cost in GCC High?
For Keytos solutions in Azure GCC High, there is no extra markup compared to our commercial offerings. The price you see on our website is the same for GCC High tenants as it is for commercial tenants. That means you can deploy a complete cloud PKI and RADIUS environment for $1.50 or less per user per month, or implement individual components like EZCA cloud PKI or EZRADIUS cloud RADIUS for even less if you only need a specific service.
Which tier are you comparing?
Cost for Cloud PKI + Cloud RADIUS
EZCA + EZRADIUS
Lower cost
$0
per month
Keytos Shield
Lower cost
$0
per month
Assumes EZCA Root + Issuing CA at $400/mo (Basic) or $1,000/mo (Premium), plus EZRADIUS shared infrastructure pricing. Shield pricing reflects its published Basic and Premium tiers. Actual costs can vary by configuration.
Learn more about Keytos pricingWhat Payment Methods Are Accepted in Azure GCC High?
For Azure GCC High tenants, the accepted payment methods generally align with those available for commercial Azure subscriptions, including:
- Credit cards (month to month, no contracts)
- Invoicing directly through us (prepaid)
- Invoicing through a government channel partner (e.g., Carahsoft)
Can I Purchase Through Carahsoft in Azure GCC High?
Yes! Organizations can purchase Keytos solutions through Carahsoft, a government channel partner, for Azure GCC High deployments. This allows government agencies and contractors to acquire cloud PKI and RADIUS solutions while adhering to procurement policies and leveraging existing government contracts.
Learn more about purchasing through Carahsoft here.
Is There a Free Trial Available in Azure GCC High for Keytos Solutions?
Yes! Keytos offers a 30 day free trial for Shield, EZCA, and EZRADIUS in Azure GCC High, allowing organizations to evaluate the full capabilities of cloud PKI and RADIUS without any upfront commitment.
Get Started with Keytos Shield PKI + RADIUSWant to Talk to a Keytos Engineer About The Best Option For Your Environment?
Want to talk to a Keytos Engineer to discuss your organization’s specific needs? You can reach out to us for a personalized consultation here.
Schedule a Demo