



How-To: Enable WiFi Certificate Authentication For Linux in Intune
While Intune does not have a specific profile for Linux devices, we have created some custom profiles that will allow you to issue certificates to Linux devices and enable WiFi Certificate Authentication.
Prerequisites
- Registering the application in your tenant
- Creating Cloud Radius Instance
- Being a Subscription Owner or Network Administrator
- Being an MDM Administrator.
- Have a certificate in the Device, if you do not have one, follow the guide on how to create Intune SCEP profiles for Linux.
How to Linux Enable WiFi Certificate Authentication in Intune
-
Go to your Intune portal: https://aka.ms/Intune
-
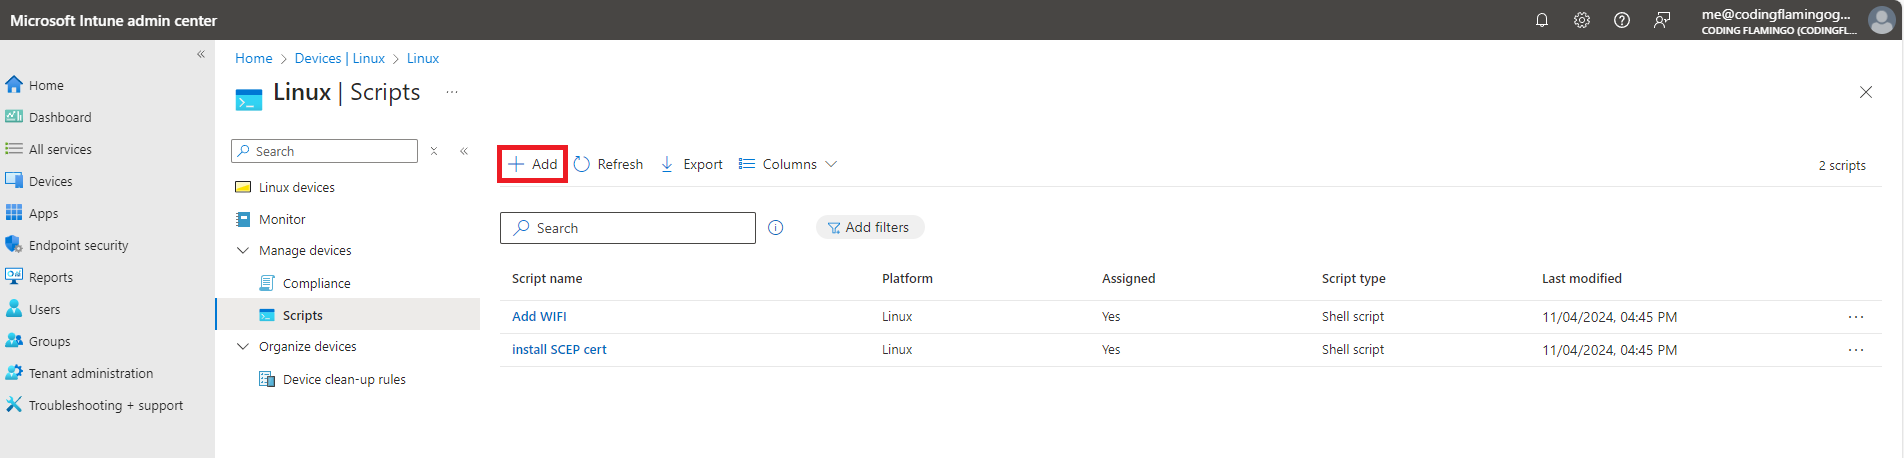
Select: Devices -> Linux -> Scripts.
-
Click the “Add” button.
-
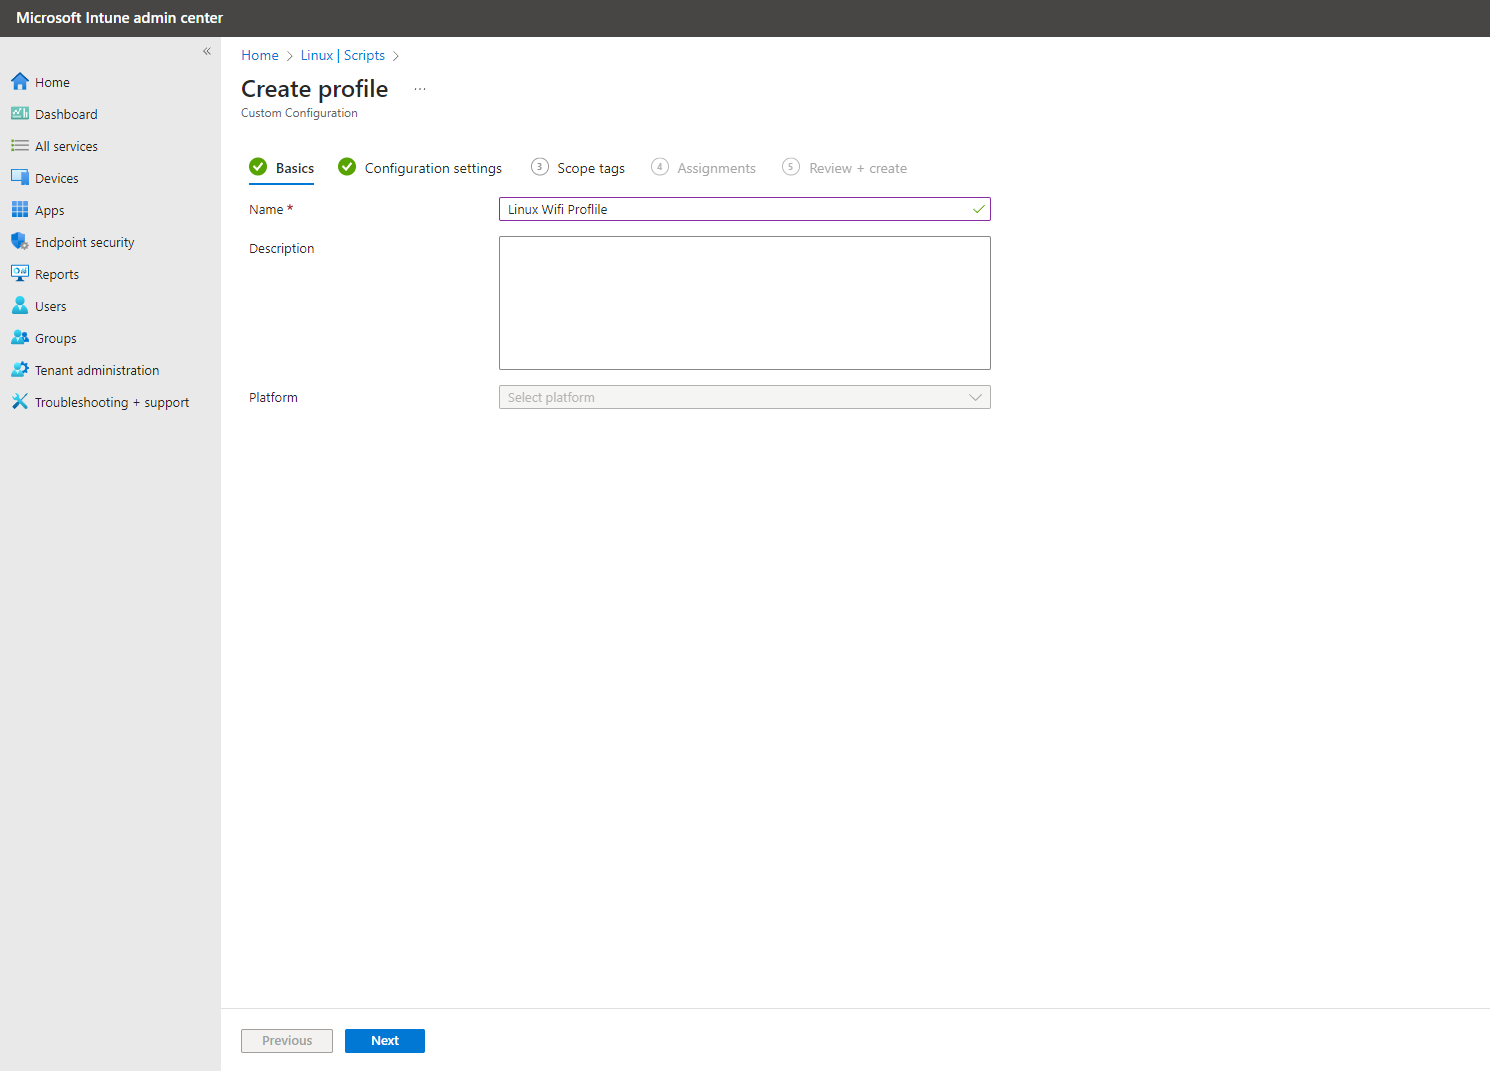
Enter a name for the profile and click “Next”.
-
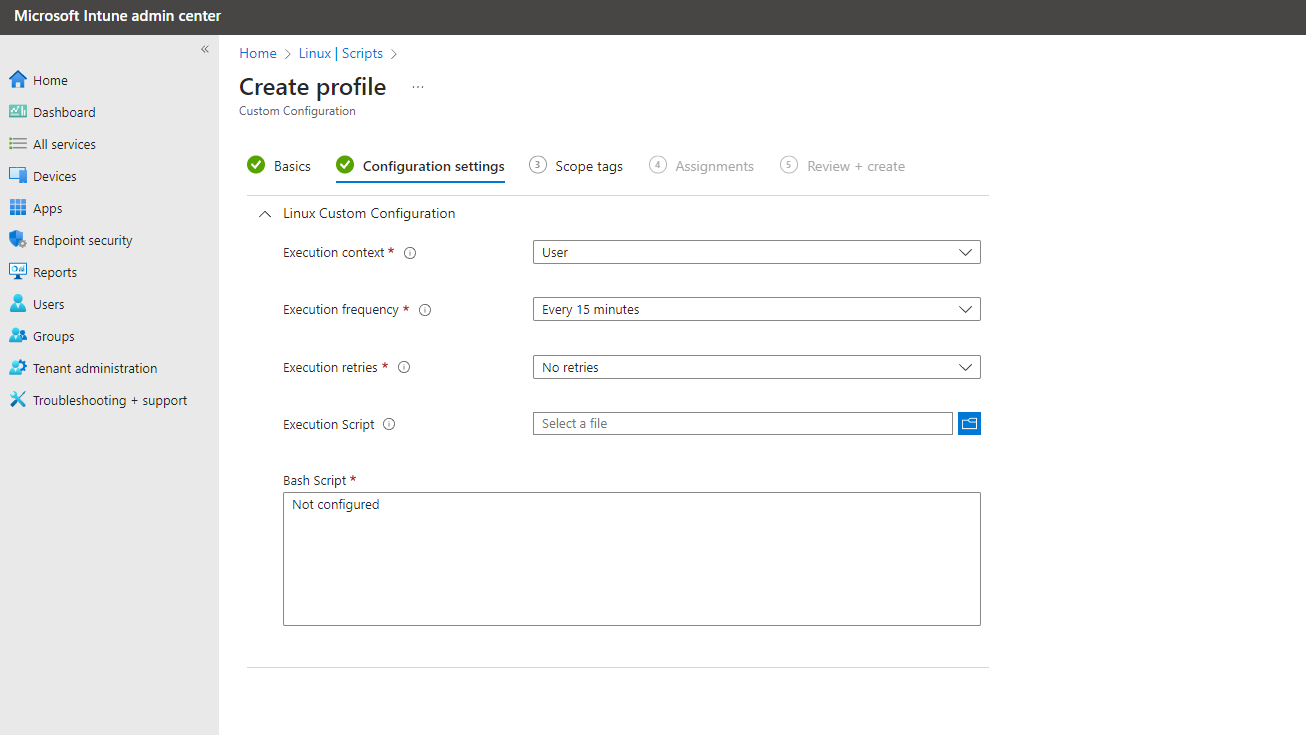
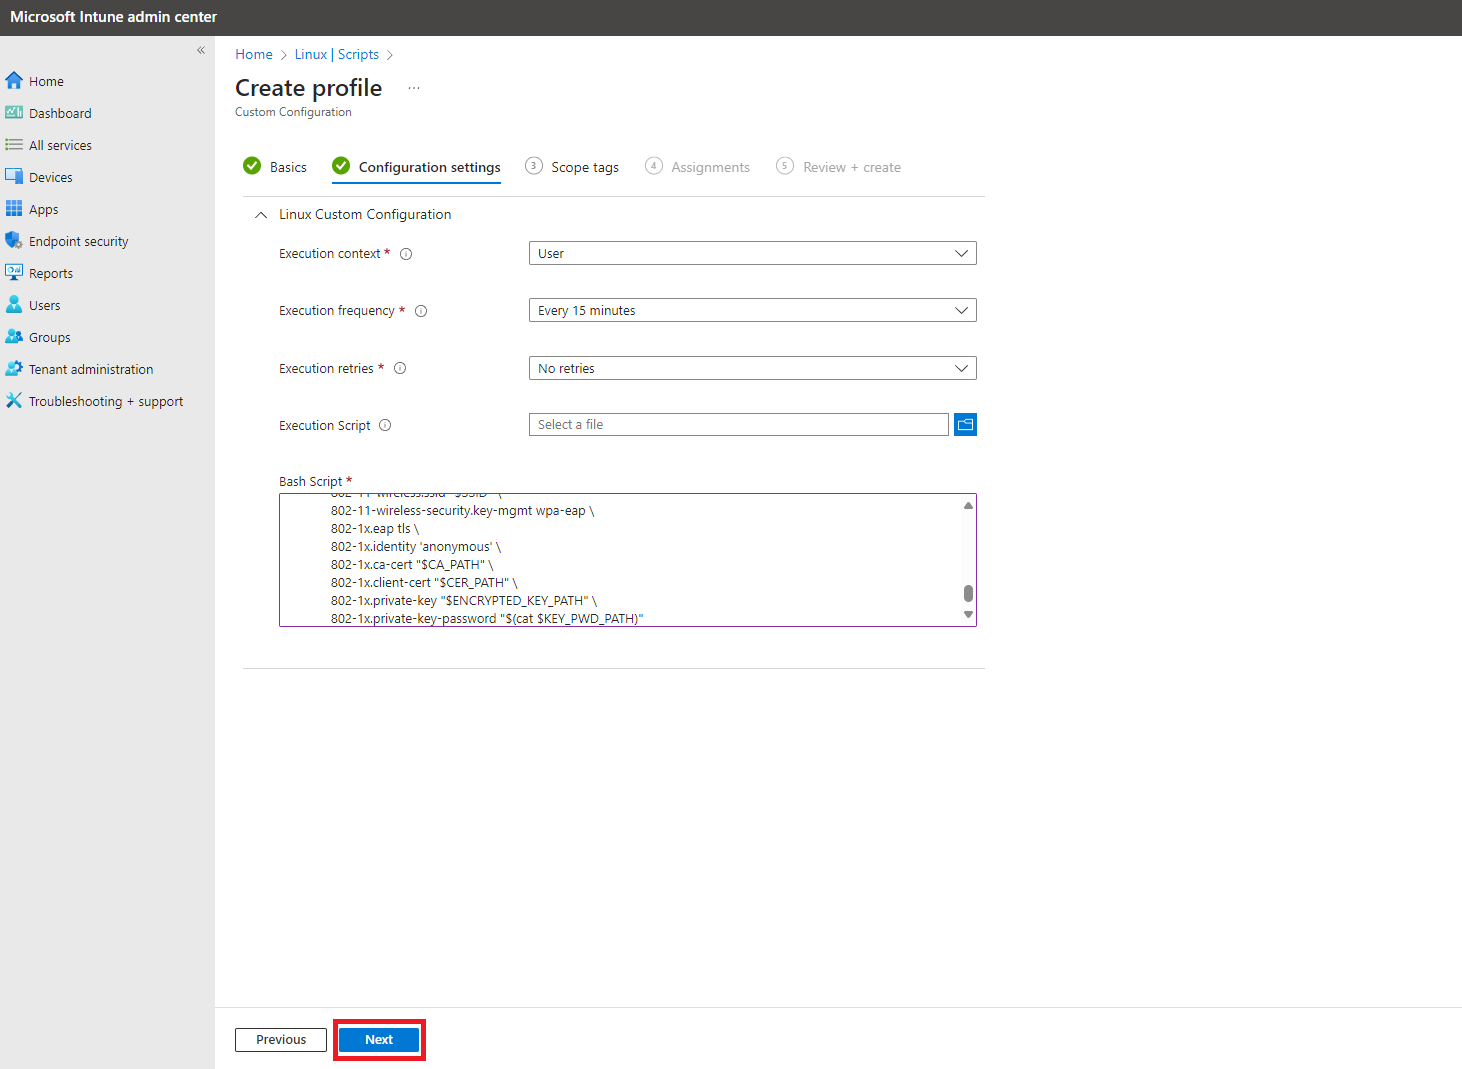
Set your execution values.
-
Copy the following Script (Modifying the values for your CA and SSID). You must set either
CA_PATHorEZCA_SERVER_CA_STATIC_SCEP_URL, or the script will exit:- If your EZRADIUS server certificate is Auto-Generated, it is not issued by a SCEP CA, so you must place the RADIUS server CA certificate (Download CA Certificate in your EZRADIUS policy) on your Linux devices and set
CA_PATHto its absolute path. - If your server certificate was issued by an EZCA SCEP CA, set
EZCA_SERVER_CA_STATIC_SCEP_URLto that CA’s static SCEP URL and the script will download the CA certificate automatically.
#!/bin/bash # User-set values # CA_PATH="" # Set to the absolute path of the server certificate CA EZCA_SERVER_CA_STATIC_SCEP_URL="" # Set to the static scep URL of the server certificate CA SSID="test-wifi" # Set to the SSID of the network # NOTE: set ONE of the two values above: # - If your RADIUS server certificate is auto-generated by EZRADIUS, download the server CA # certificate from EZRADIUS ("Download CA Certificate"), copy it to the device, then # uncomment CA_PATH and set it to the absolute path of that file. # - If your RADIUS server certificate was issued by an EZCA SCEP CA, you can instead set # EZCA_SERVER_CA_STATIC_SCEP_URL and the script will download that CA certificate for you. ## ---------- ## ---------- ## ---------- ## ---------- ## ---------- ## # Check all required executables exist req_execs=("base64" "cat" "curl" "cut" "grep" "head" "mkdir" "nmcli" "sed") for exe in "${req_execs[@]}"; do if [ ! $(command -v "$exe") ]; then echo "Required executable $exe not found" exit 1 fi done if [ -z "$EZCA_SERVER_CA_STATIC_SCEP_URL" ] && [ -z "$CA_PATH" ]; then echo "Either EZCA_SERVER_CA_STATIC_SCEP_URL or CA_PATH must be set" exit 1 fi SSID=${SSID:-'DEFAULT_SSID'} CONNECTION_NAME=${CONNECTION_NAME:-'keytos-ezradius-eap-tls'} INSTALL_DIR=${INSTALL_DIR:-"$HOME/.local/share/keytos/scep_certs"} PFX_PATH=${PFX_PATH:-"$INSTALL_DIR/scep-client-cert.pfx"} PASSWORD_PATH=${PASSWORD_PATH:-"$INSTALL_DIR/scep-client-cert_password.txt"} ENCRYPTED_KEY_PATH=${ENCRYPTED_KEY_PATH:-"$INSTALL_DIR/scep-client-cert-key.pem"} CER_PATH=${CER_PATH:-"$INSTALL_DIR/scep-client-cert.pem"} WIFI_NIC=$(nmcli -t -f DEVICE,TYPE device | grep wifi$ | head -n 1 | cut -d: -f1) if [ -z "$WIFI_NIC" ]; then exit 1 fi nmcli -f GENERAL.STATE con show "$CONNECTION_NAME" >/dev/null 2>&1 if [ $? -eq 0 ]; then echo "$CONNECTION_NAME already exists, skipping wifi setup" exit 0 fi # If CA_PATH was not provided, download the server certificate CA from the EZCA static SCEP URL if [ ! -f "$CA_PATH" ]; then echo "Getting CA Certificate" INSTALL_DIR=${INSTALL_DIR:-"$HOME/.local/share/keytos/scep_certs"} mkdir -p $INSTALL_DIR CA_PATH=$INSTALL_DIR/server_ca_certificate.pem curl ${EZCA_SERVER_CA_STATIC_SCEP_URL}?operation=GetCACert | base64 | sed '1i -----BEGIN CERTIFICATE-----' | sed '$a -----END CERTIFICATE-----' \ >$CA_PATH echo "CA Certificate download to $CA_PATH from $EZCA_SERVER_CA_STATIC_SCEP_URL" fi # Check files exist if [ ! -f "$CA_PATH" ]; then echo "Required file not found: $CA_PATH" exit 1 fi if [ ! -f "$CER_PATH" ]; then echo "Required file not found: $CER_PATH" exit 1 fi if [ ! -f "$ENCRYPTED_KEY_PATH" ]; then echo "Required file not found: $ENCRYPTED_KEY_PATH" exit 1 fi if [ ! -f "$PASSWORD_PATH" ]; then echo "Required file not found: $PASSWORD_PATH" exit 1 fi nmcli c add type wifi ifname "$WIFI_NIC" con-name "$CONNECTION_NAME" \ 802-11-wireless.ssid "$SSID" \ 802-11-wireless-security.key-mgmt wpa-eap \ 802-1x.eap tls \ 802-1x.identity 'anonymous' \ 802-1x.ca-cert "$CA_PATH" \ 802-1x.client-cert "$CER_PATH" \ 802-1x.private-key "$ENCRYPTED_KEY_PATH" \ 802-1x.private-key-password "$(cat $PASSWORD_PATH)" - If your EZRADIUS server certificate is Auto-Generated, it is not issued by a SCEP CA, so you must place the RADIUS server CA certificate (Download CA Certificate in your EZRADIUS policy) on your Linux devices and set
-
Click “Next”.
-
Select your Scope, and click “Next”.
-
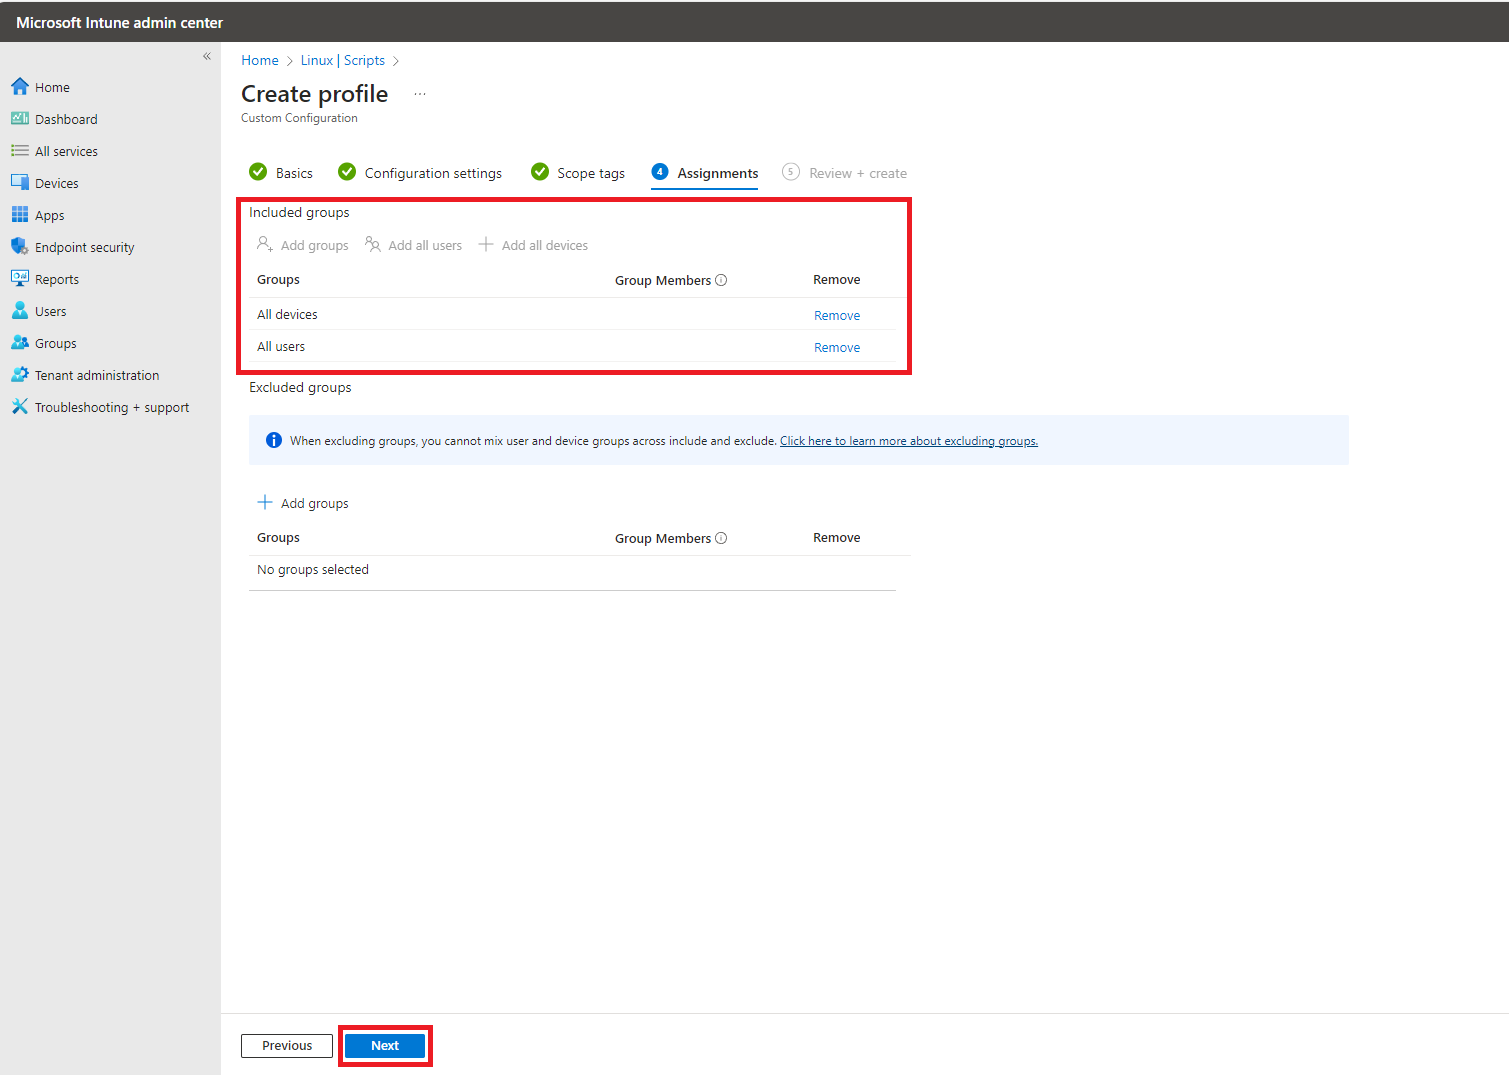
Select your Assignments, and click “Next”.
-
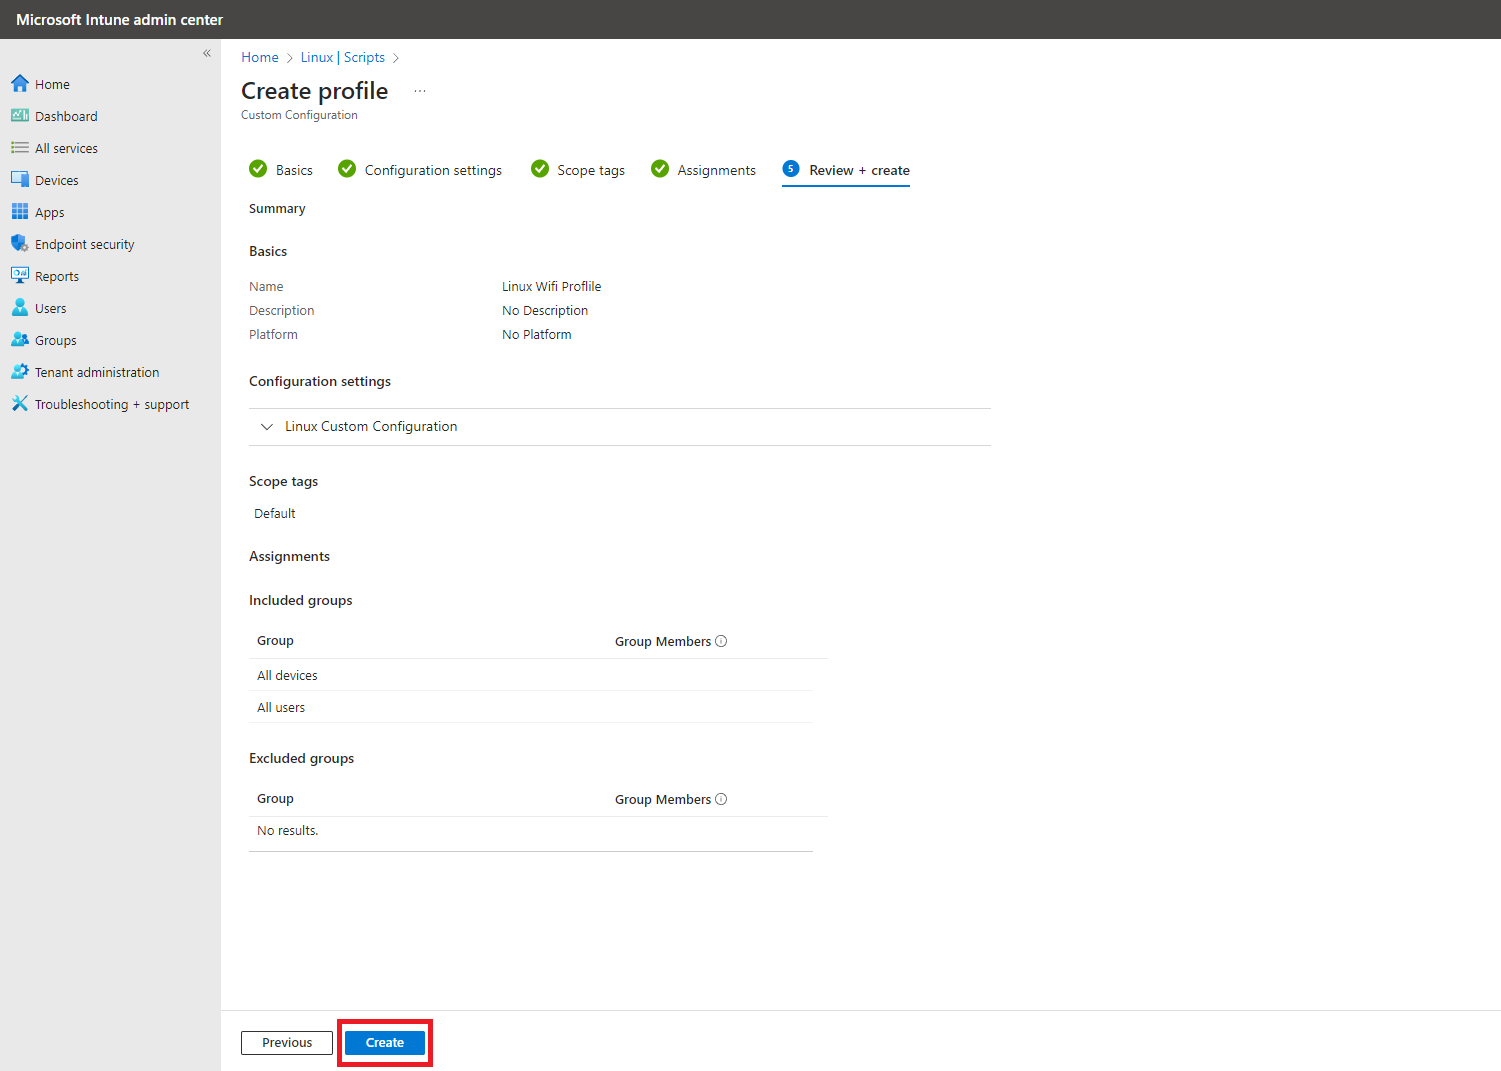
Review your settings and click “Create”.
-
Your Linux device will now be able to connect to the WiFi network using the certificate you provided.