



How-To: Create Cloud RADIUS Network Policies for Certificate Authentication
Prerequisites
- The Keytos Entra applications are registered in your tenant
- You have an active EZRADIUS plan
- You are a Subscription Owner or Network Administrator on your EZRADIUS plan
How to Create Cloud RADIUS Network Policies - Video Tutorial
Introduction to Managing Cloud RADIUS Network Policies in EZRADIUS
The Policies page in EZRADIUS allows you to create and manage your Cloud RADIUS network policies. Each policy defines the conditions under which a user or device can connect to your network, including authentication methods, accepted certificate authorities, and access policies.
Visit the Manage RADIUS Policies guide to learn more about the Policies page layout and features.
How to Create Cloud RADIUS Network Policies with Certificate Authentication
Now that you are familiar with the layout of the Policies page in EZRADIUS, you can set up a new RADIUS network policy that uses Certificate Authentication for authentication. The following steps will guide you through the process.
Step 1: Name Your RADIUS Server Policy
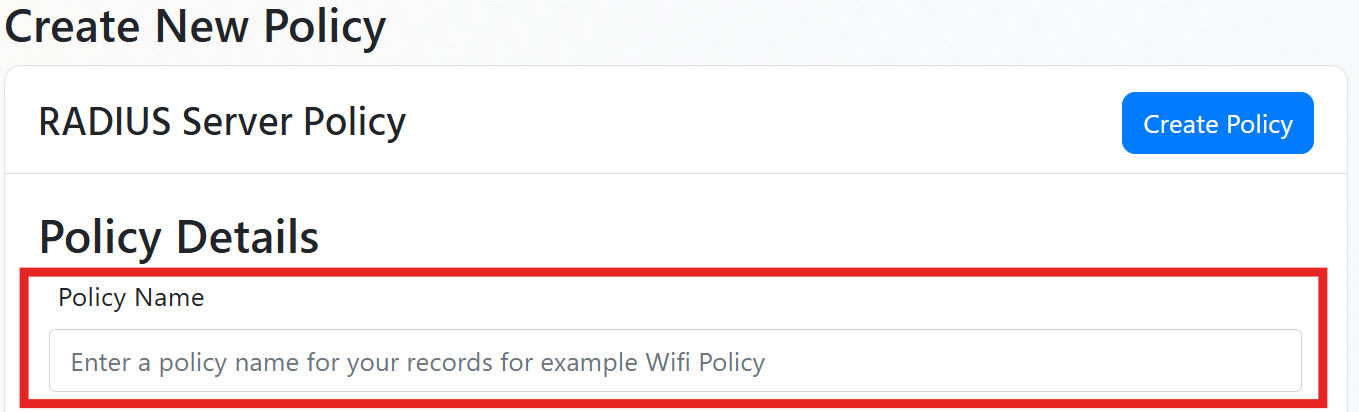
Begin by entering a friendly name for your RADIUS server policy. This name is for your records to help you identify the policy later. Behind the scenes, EZRADIUS will create a unique identifier for the policy, so feel free to choose a name that makes sense to you.
Step 2: Enable RadSec and/or Classic RADIUS
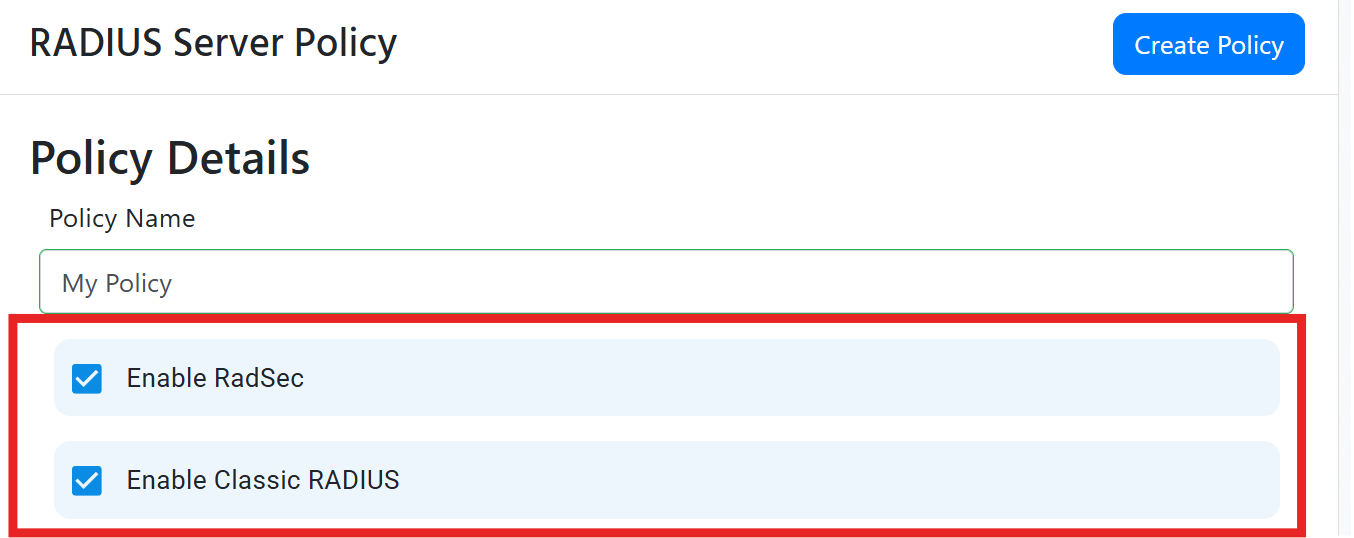
Next we have to enable which authentication methods you are going to use, you can use RadSec, Classic RADIUS, or both.
How to Set Up Classic RADIUS for Cloud RADIUS
Classic RADIUS uses the public IP address of your RADIUS client (access point, switch, etc.) and a shared secret to authenticate incoming requests. In this section, you will add your public IP addresses and create a shared secret so we know which requests are coming from your authorized network devices.
When specifying an IP address, make sure to use the external IP address for your network. It should not start with 192.168.***, 10.0.***, 172.16.***, or any other private IP address range. If you’re unsure, visit What is my IP to find your public IP address, or click the My IP Address button in the EZRADIUS portal to automatically add your current public IP address if you’re connecting from within your network.
There are two ways to add IP addresses to your RADIUS policy: either manually adding them one by one or uploading a CSV file for multiple IP addresses.
How To Manually Add Your IP Address(es)
To manually add your IP address(es) to the RADIUS policy, follow these steps:
-
Select Manual from the dropdown.
-
Enter the public IP address of your router or VPN server.
-
Provide a friendly name for the IP address (for your records).
-
Click Add to add the IP address to the list of allowed RADIUS clients.
-
A randomly generated shared secret will be created for the IP address. You can change this shared secret if needed.
-
Repeat the process for each additional public IP address that will connect to Keytos Shield. Make sure to include any backup/failover IP addresses as well.
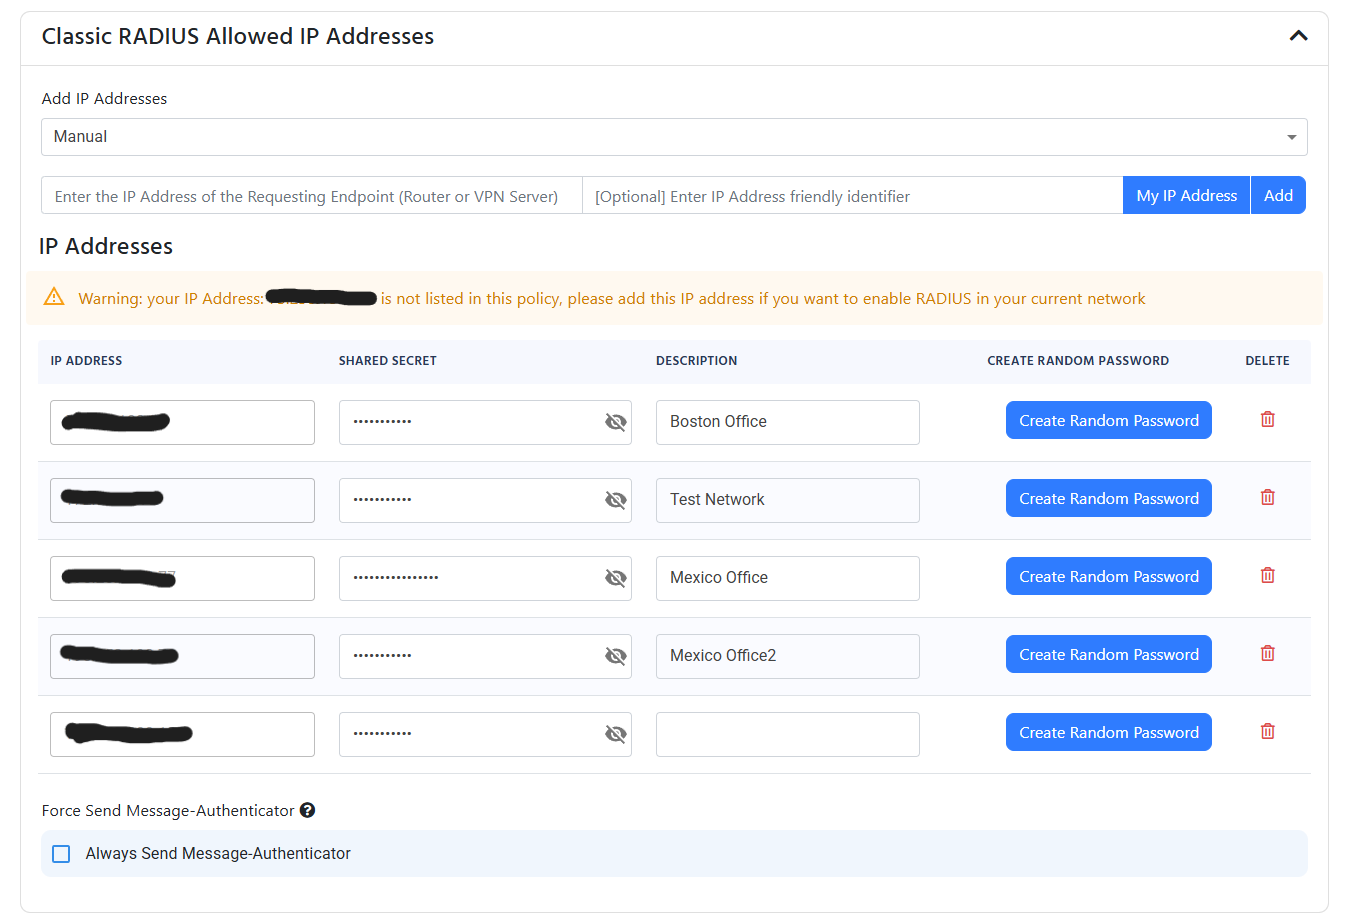
If you have multiple IP Addresses you can add them using a CSV file (if you have an CIDR range and want to convert it to IP range, use this site).
How To Create a CSV File for Uploading IP Addresses
Before uploading, you need to prepare a CSV file containing all the IP addresses you want to add. Follow the instructions below to create and upload the CSV file.
- Create a new file named
ip_addresses.csvon your computer. - Open the file in a text editor or spreadsheet application and enter your IP addresses, friendly names, and shared secrets following the format
IP Address,Friendly Name,Shared Secret. Don’t include headers in the file.
For example, a CSV file with two IP addresses would look like this:
12.12.12.12,First Name,SharedSecret1
12.12.12.13,Second Name,SharedSecret2
Make sure to save your CSV file before proceeding to the upload steps.
How to Upload the CSV File
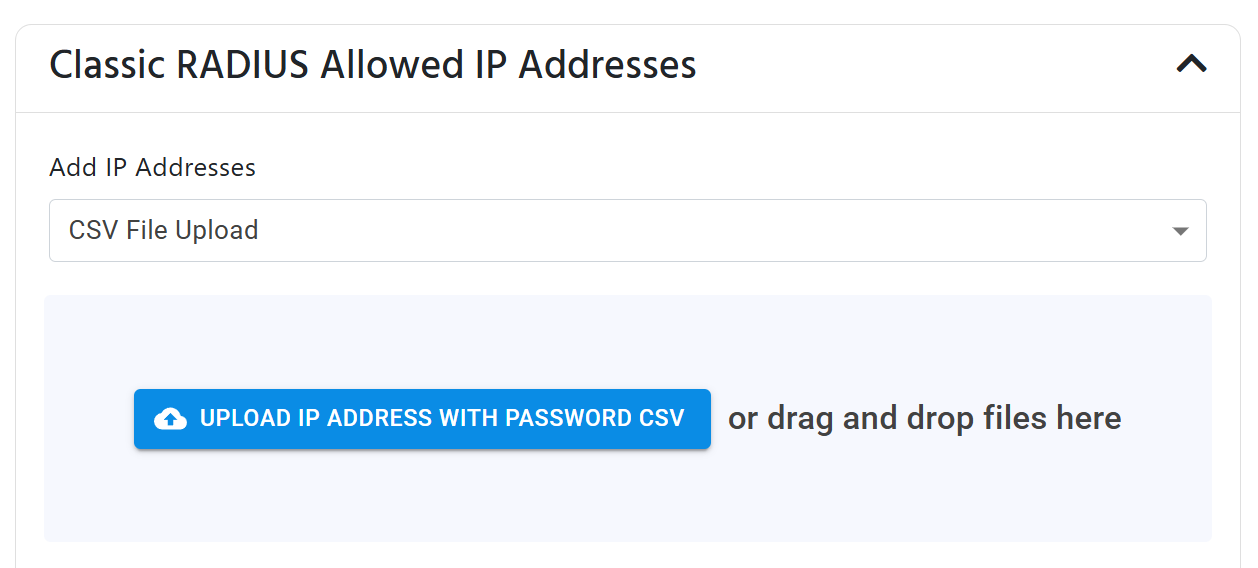
Now that you have your CSV file, follow these steps to upload it:
-
Drop down the Add IP Addresses menu and select CSV File Upload.
-
Either drag-and-drop your CSV file into the upload area or click on the area to browse and select your CSV file.
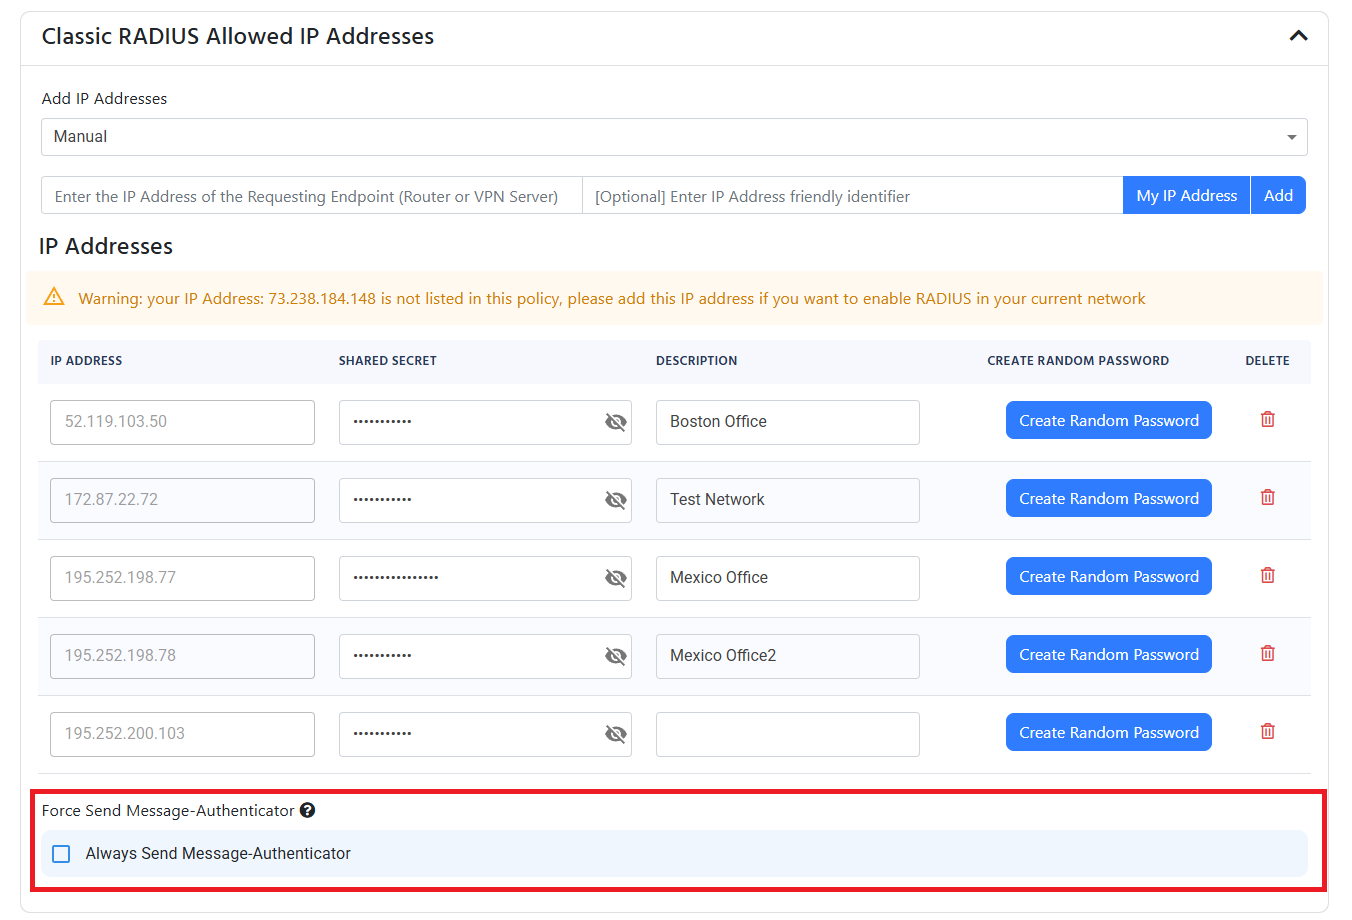
(optional) Always Send Message Authenticator
Depending on your networking device, you may need to enable the “Always Send Message Authenticator” option. This is required by some devices to ensure proper RADIUS communication, especially for devices from Fortinet.
If using Fortinet devices, After Fortigate 7.2.10 you will need to enable the “Always Send Message Authenticator” option in the RADIUS server settings.
How to Configure RadSec for Cloud RADIUS
RadSec (RADIUS over TLS) uses the incoming RadSec client certificate to authenticate the connecting device and associate it with your network profile. To configure RadSec for your network, you need to add a trusted CA which issues your RadSec client certificates (recommended), or specific certificate thumbprints (ok for testing/troubleshooting).
Certificate Authorities can only be associated with a single EZRADIUS network profile. If you are a Managed Service Provider (MSP) or have multiple customers sharing a public IP address, each customer must use a distinct RadSec CA in their EZRADIUS network profile. EZRADIUS identifies which profile a RadSec request belongs to by the CA that signed the client certificate, so it cannot be shared across multiple profiles. Instead, use distinct CAs for each customer’s network profile or create multiple access policies within one network profile.
How to Add an EZCA CA as a Trusted Certificate Authority for RadSec
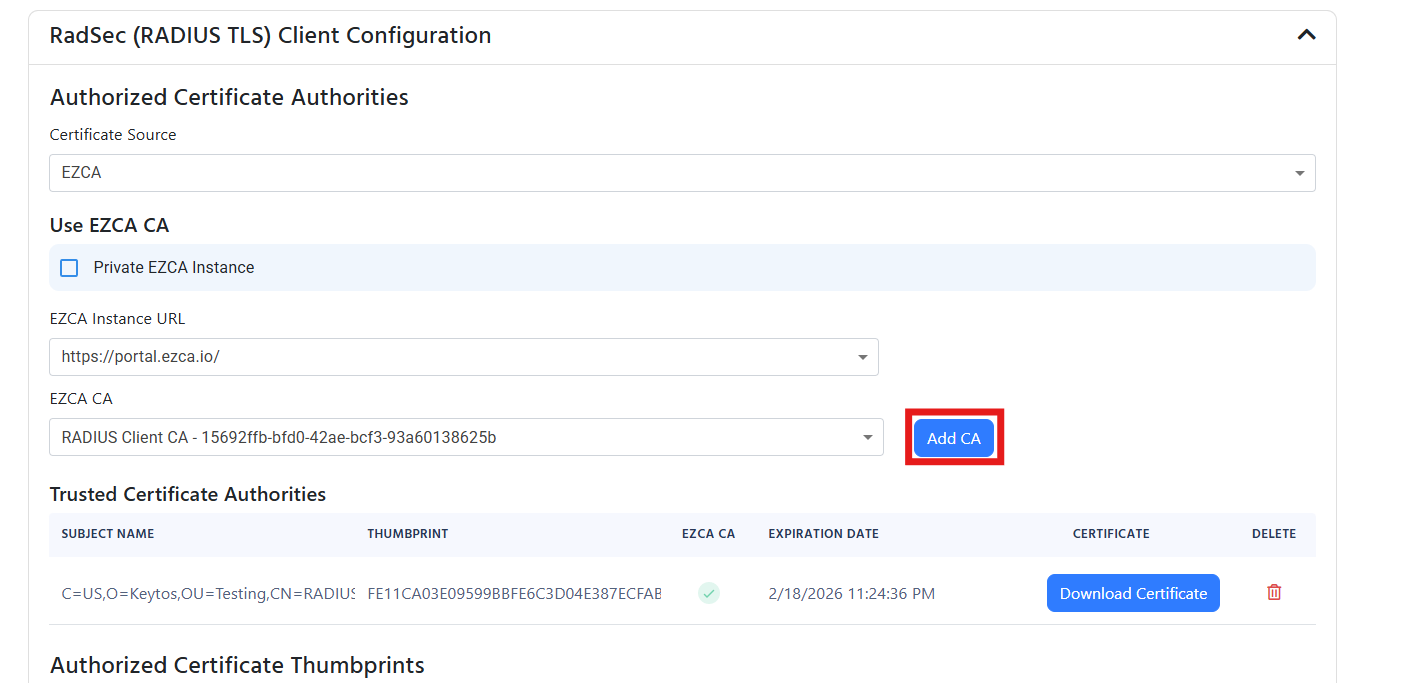
If your RadSec certificate is issued by your EZCA Certificate Authority, then you can easily add the CA to the cloud RADIUS server by:
-
From the Certificate Source dropdown, select EZCA.
-
Under the EZCA Instance URL dropdown , select your EZCA instance.
-
Under the EZCA CA dropdown, select the CA you want to add.
-
Click Add CA to add the CA to the RADIUS server.
-
Your CA will now be listed under the Trusted Certificate Authorities section.
How to Add Certificate Authorities to RadSec Using 3rd Party CA
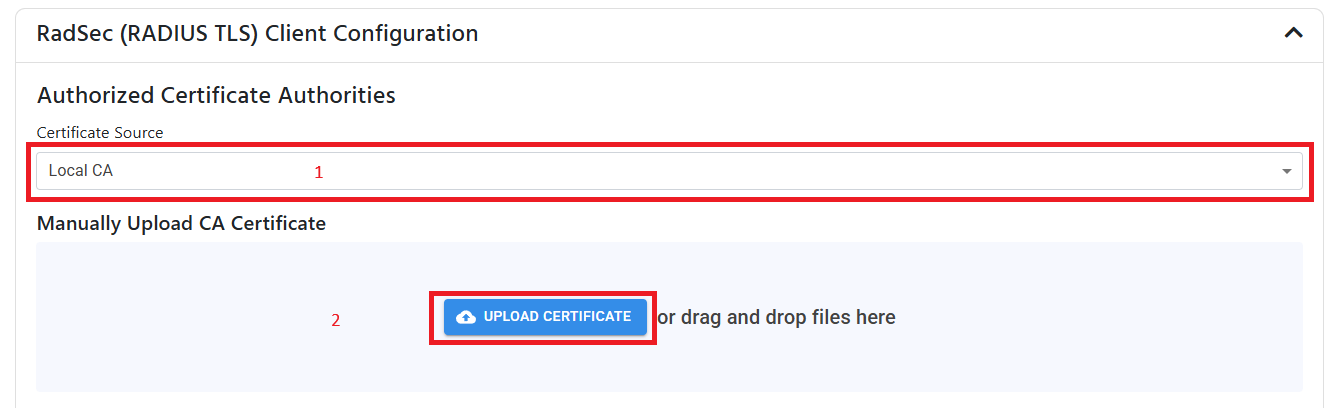
If your device uses a certificate from a 3rd party CA, you can add the CA to the cloud RADIUS server by following these steps:
-
From the Certificate Source dropdown, select Local CA.
-
Upload your CA certificate in PEM format.
-
Your CA will now be listed under the Trusted Certificate Authorities section.
How to Add a Self-Signed Certificate as a Trusted Certificate for RadSec
If your networking device only supports self-signed certificates for RadSec, you can upload the single certificate to your cloud RADIUS policy by following these steps:
-
Leave the Authorized Certificate Authorities section empty. You don’t need to add any CAs for self-signed certificates.
-
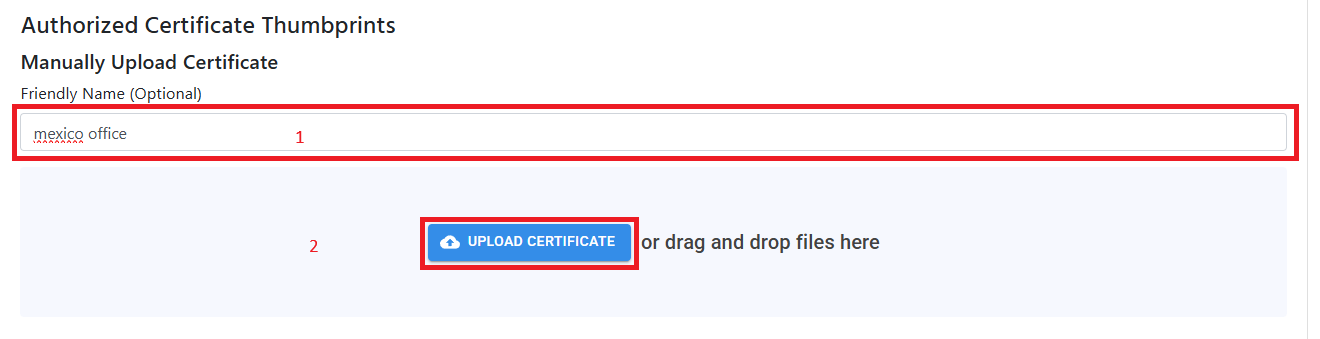
Under Authorized Certificate Templates, enter a certificate Friendly Name (This is just for your records, useful if have multiple locations).
-
Upload the certificate in PEM format.
-
Your certificate will now be listed under the Trusted Certificates section.
Step 3: Add Certificate Authorities to RADIUS for Certificate Authentication
This section is only needed if you plan to use EAP-TLS certificate-based authentication in at least some of your network connections. If you only plan to use username and password authentication, you can skip this section.
A Trusted Certificate Authority (CA) is the CA which issues your user and/or device certificates which are used for network authentication. You can add one more more CAs in this section to control which certificates can authenticate to your network.
How to Add an EZCA Certificate Authority as a Trusted CA
To add an EZCA Certificate Authority as a trusted CA in your network profile, follow these steps:
-
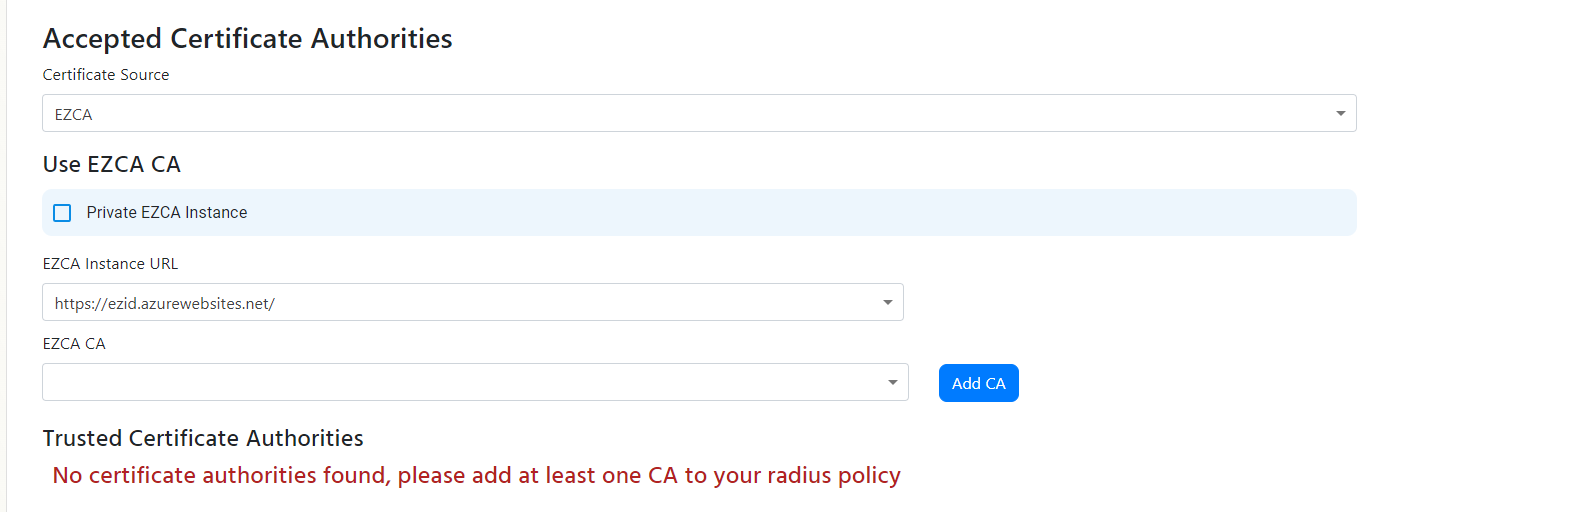
From the Certificate Source dropdown, select EZCA.
-
If you are using a private EZCA instance, check the Private Instance checkbox and enter your EZCA URL.
-
Under the EZCA CA dropdown, select your EZCA CA.
-
Click the Add button to add the CA.
-
If you have a 2 tier hierarchy, add both your Root CA and your Issuing CA.
-
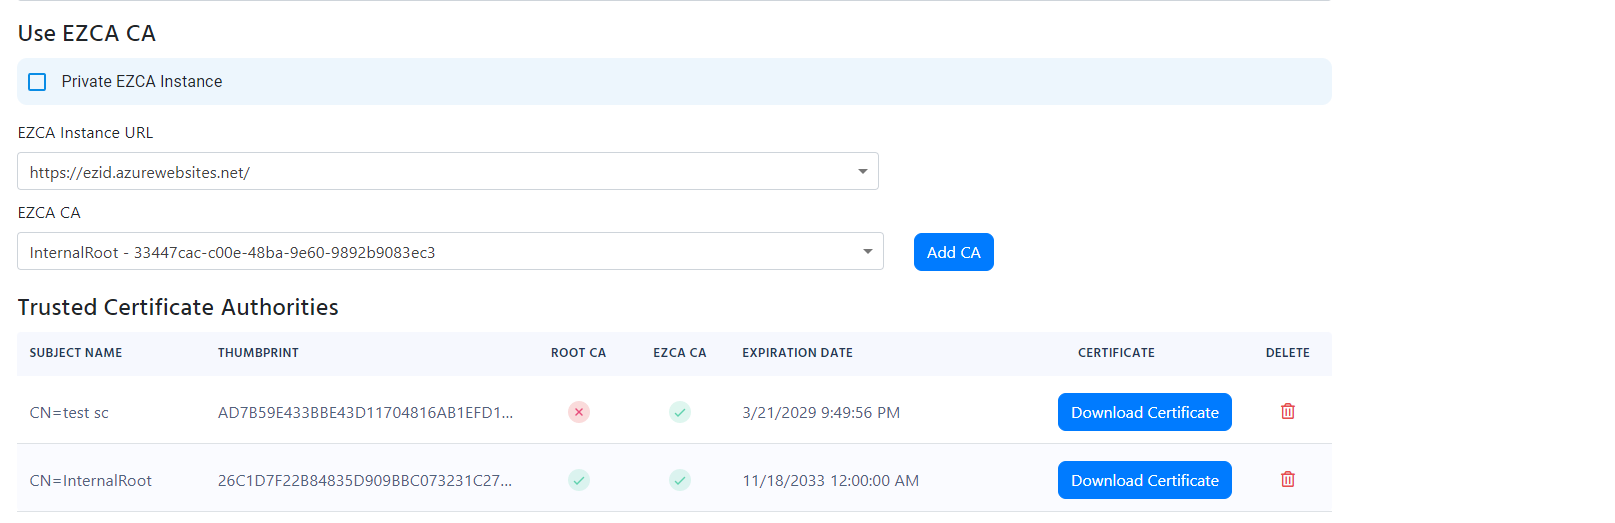
You should now see your CA(s) listed under your Trusted Certificate Authorities:
How to Add a Third-Party Certificate Authority as a Trusted CA
To add a third-party Certificate Authority as a trusted CA in your network profile, follow these steps:
-
From the Certificate Source dropdown, select Local CA.
-
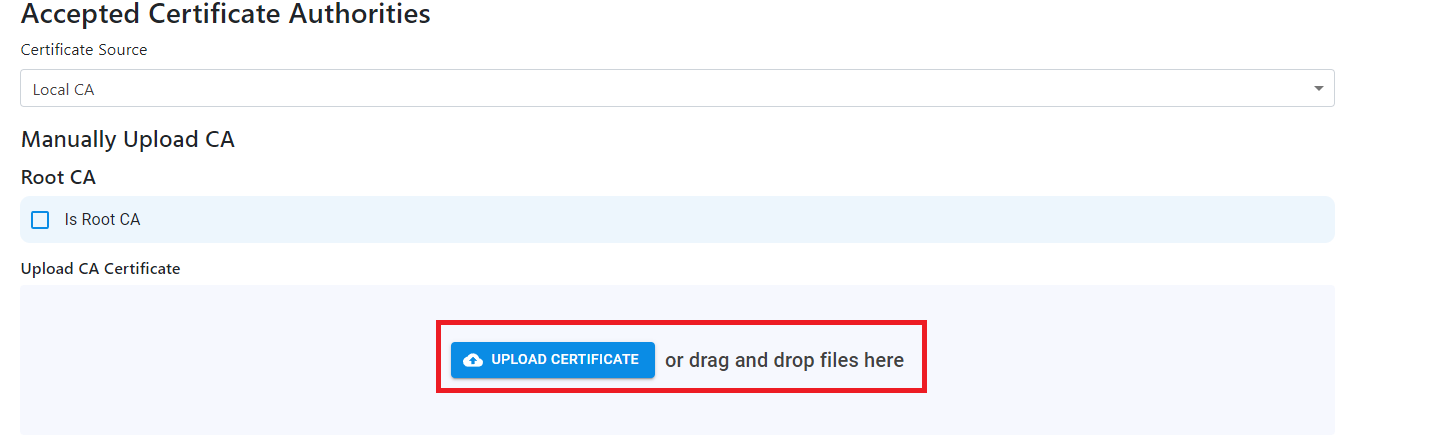
If you are uploading a Root CA, check the IS Root CA checkbox. If you are uploading an Intermediate/Issuing CA, leave the checkbox unchecked.
-
Click on the Upload Certificate button and select your CA certificate in PEM format.
-
If you have a multi-tier hierarchy, make sure to add both your Root CA and your Intermediate/Issuing CA(s).
-
Repeat the process for each additional CA chain you need to add.
Step 4: Add Server Certificate to RADIUS
A certificate is required to uniquely identify the RADIUS server to the devices connecting to the network. Without it, your clients will not be able to connect and will return errors. There are three ways to add a server certificate:
- Use a free, auto-generated certificate
- Use EZCA to create and manage the certificate
- Upload a certificate from a 3rd party CA.
Create a Free Certificate with Certificate Authority in EZRADIUS
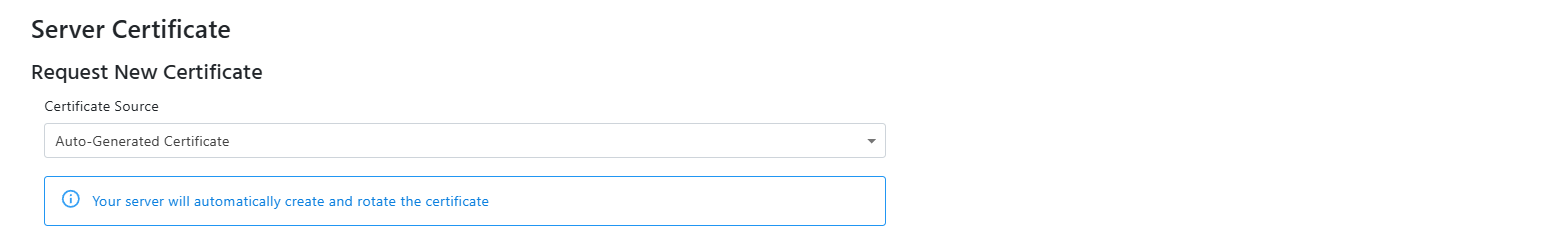
If you do not have a your own CA, you can use the EZRADIUS integrated CA to create a free certificate. The certificate will be automatically created and renewed by EZRADIUS.
-
From the ‘Certificate Source’ dropdown, select Auto-Generated Certificate.
Add Server Certificate to RADIUS Using EZCA
If you are already an EZCA customer, you can leverage your existing EZCA CA to issue a RADIUS server certificate.
-
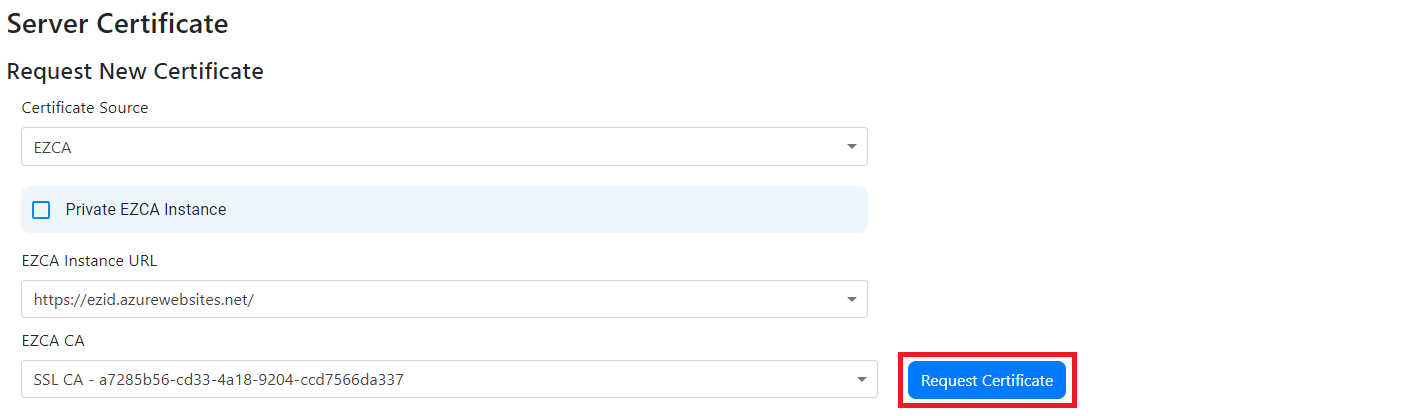
From the Certificate Source dropdown, select EZCA.
-
If you are using an EZCA private instance, select the Private Instance checkbox and enter your EZCA Issuance URL.
-
From the EZCA CA dropdown with the certificates authorities you have in your EZCA instance, select the CA you want to use.
-
Click Request Certificate to create a new RADIUS server certificate. EZRADIUS will automatically create the certificate for you. You do not need to specify an existing certificate or create a CSR. The certificate will be automatically renewed before it expires.
-
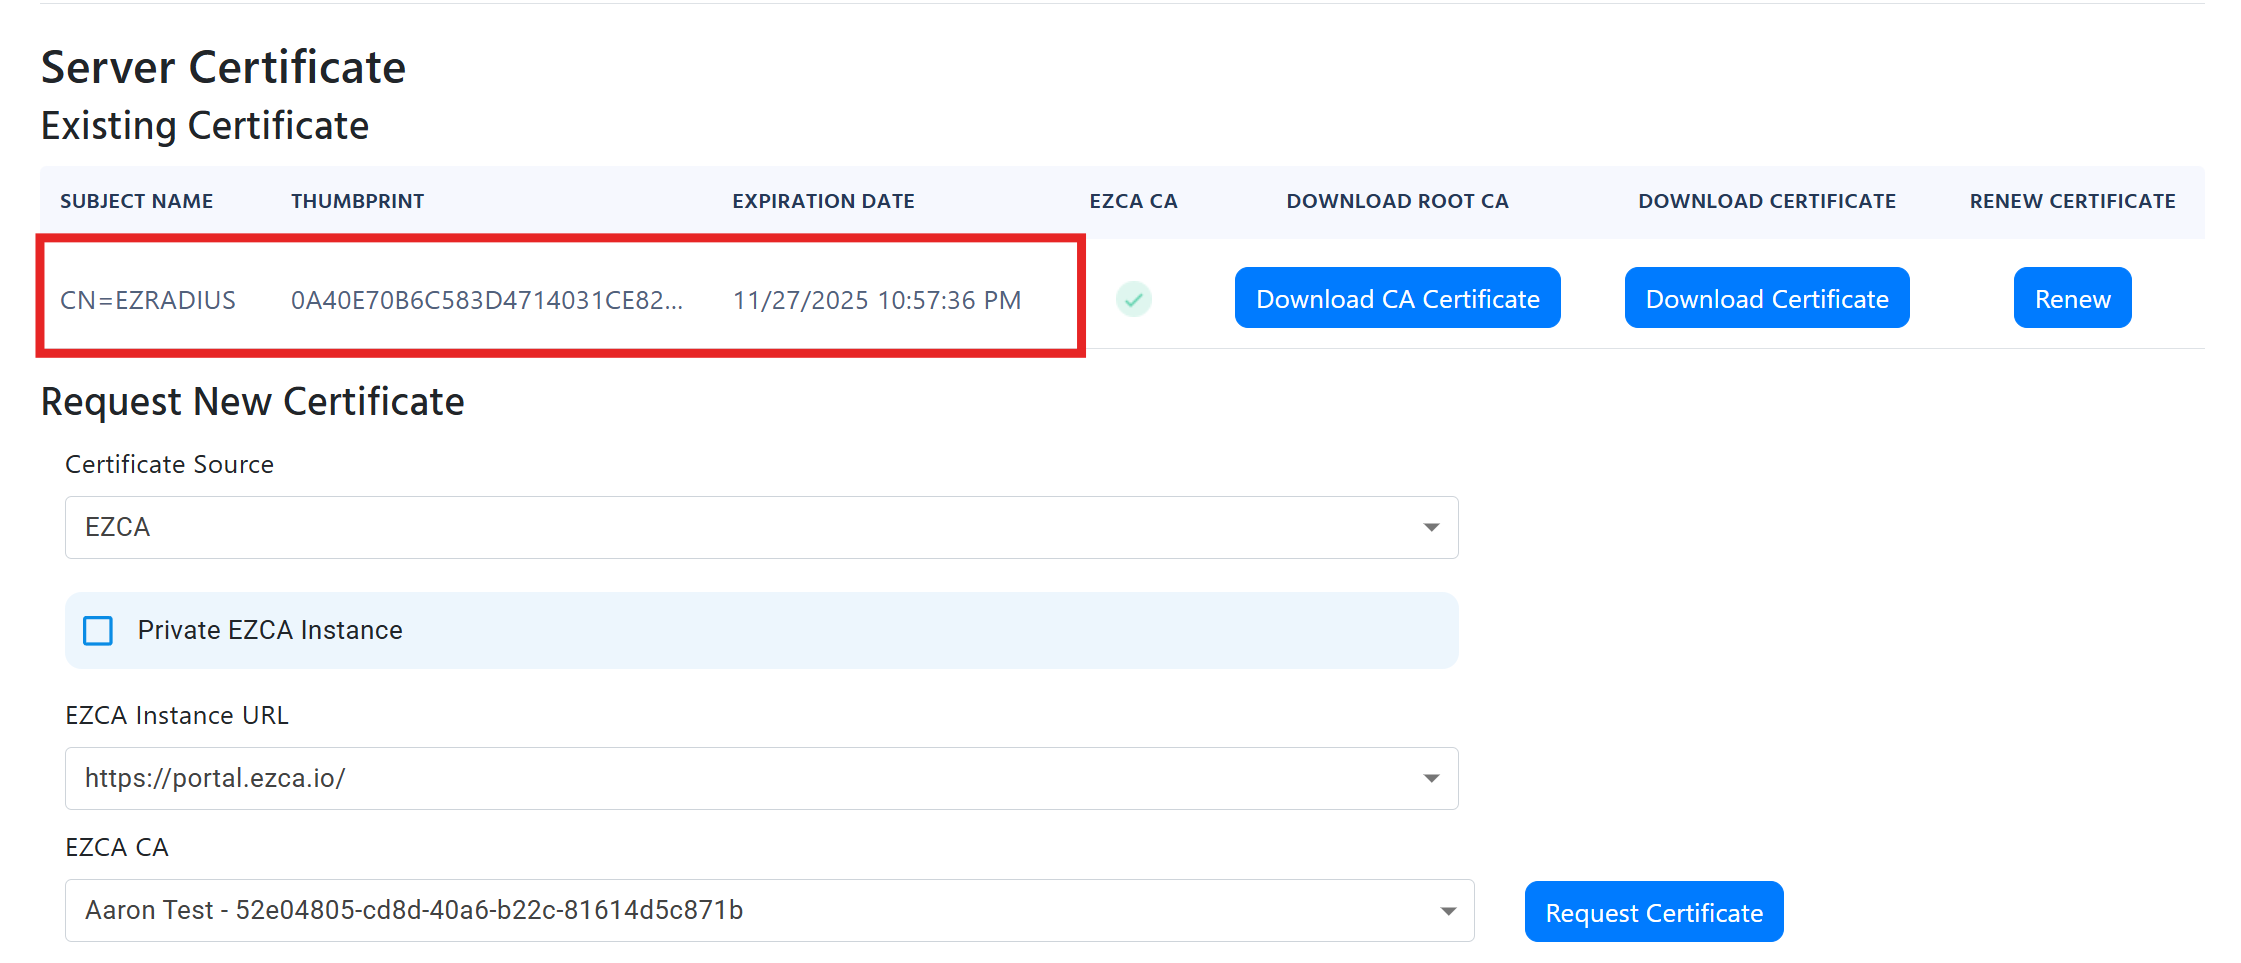
You should now see the certificate in the list of certificates:
Add Server Certificate to RADIUS Using 3rd Party CA
If you are using a 3rd party CA, you can generate a CSR in EZRADIUS, submit it to your CA, and then upload the signed certificate back to EZRADIUS.
-
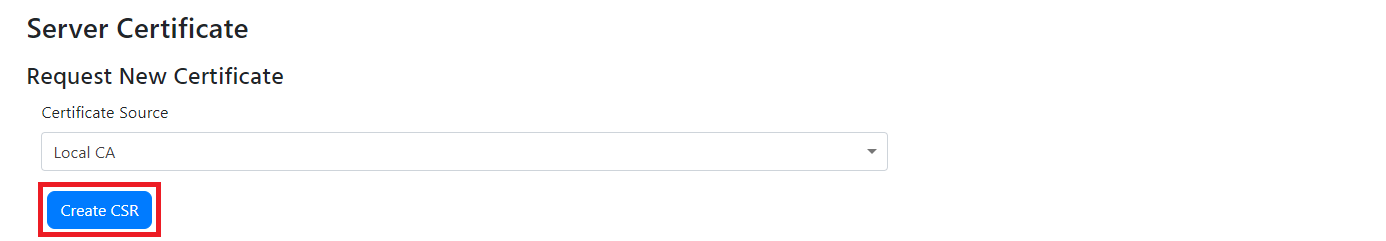
From the Certificate Source dropdown, select Local CA.
-
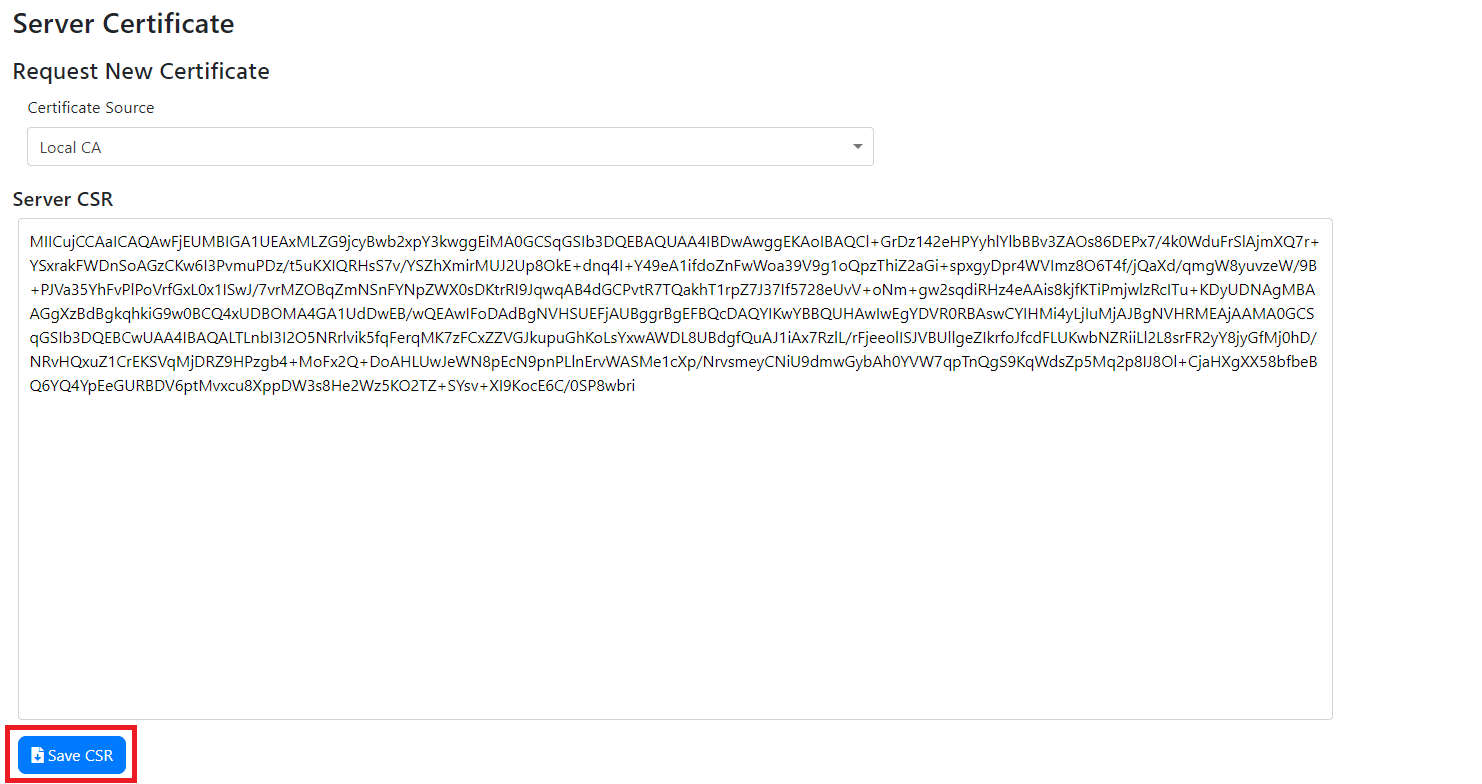
Click the Create CSR button.
-
Download the CSR by clicking the Save CSR button.
-
Submit the CSR to your CA and download the certificate.
-
Also download the certificate of your root CA.
-
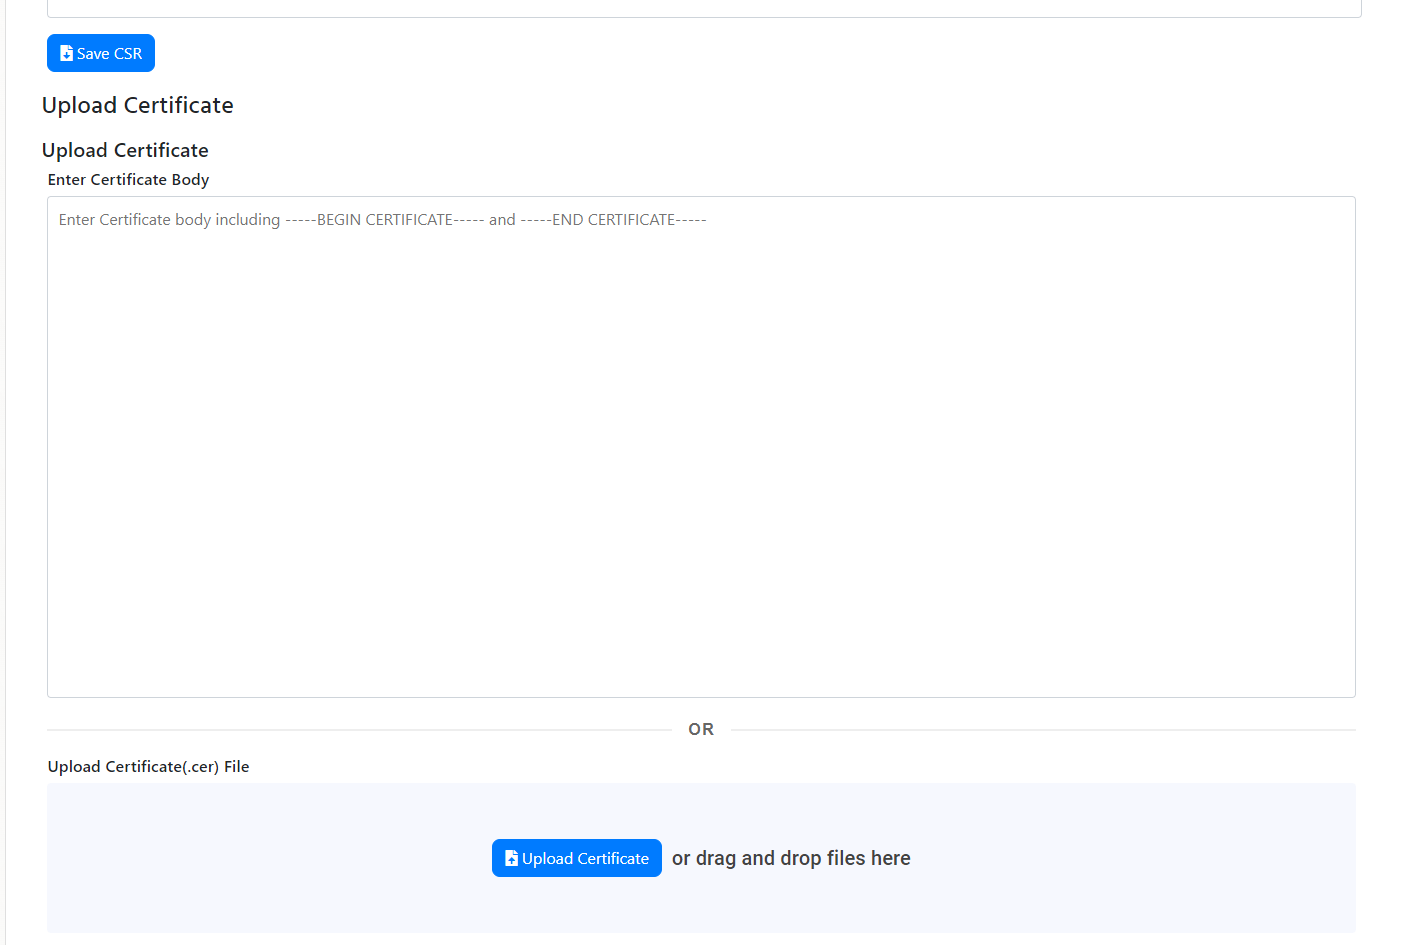
Once you have the certificate, scroll down and either copy and paste the certificate PEM content or click on Upload Certificate and select the certificate in PEM format.
-
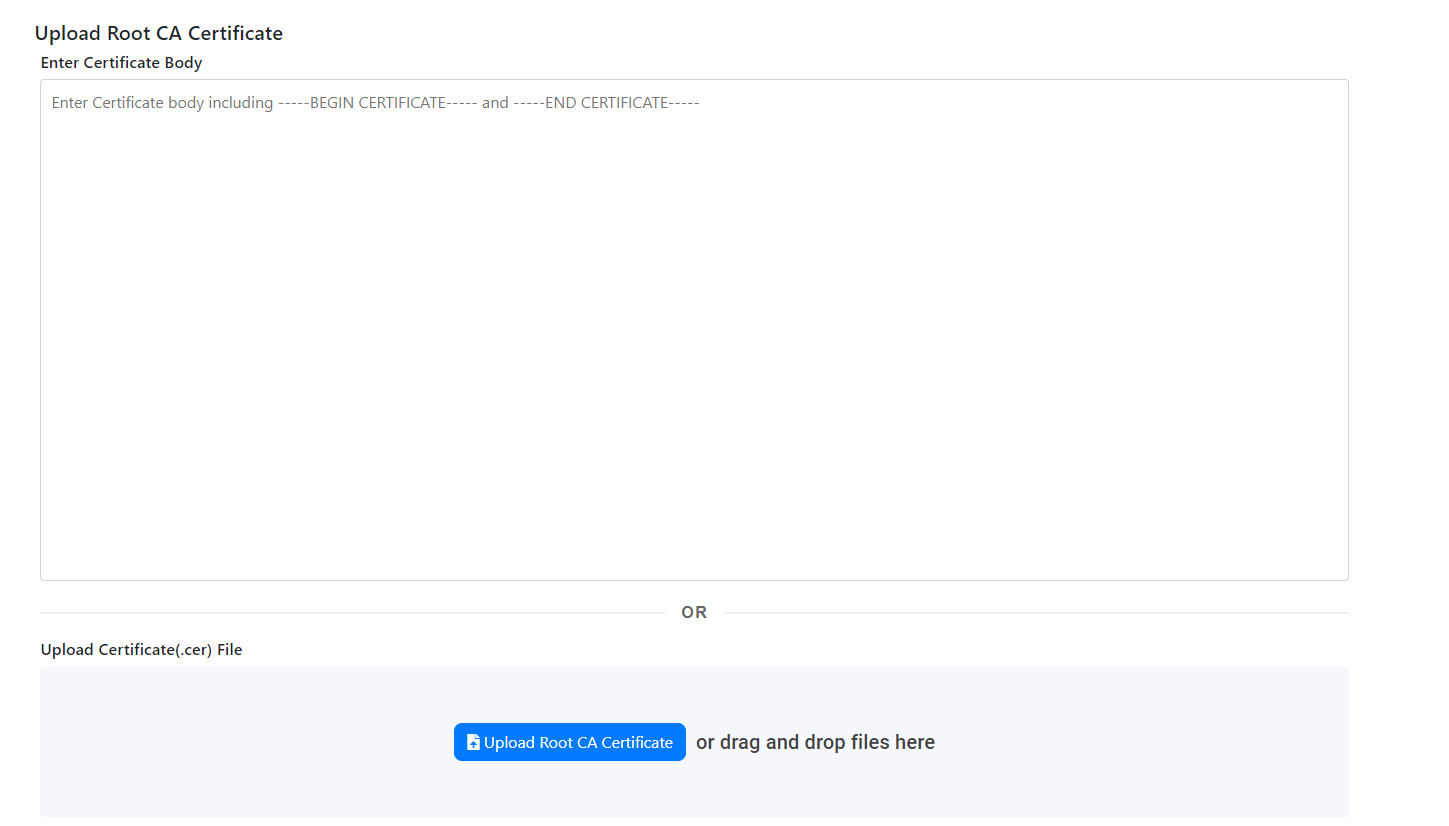
After you upload your certificate, you must upload the certificate of the Root CA that signed the certificate. Scroll down and either copy and paste the certificate PEM content or click on Upload Root CA Certificate and select the certificate in PEM format.
-
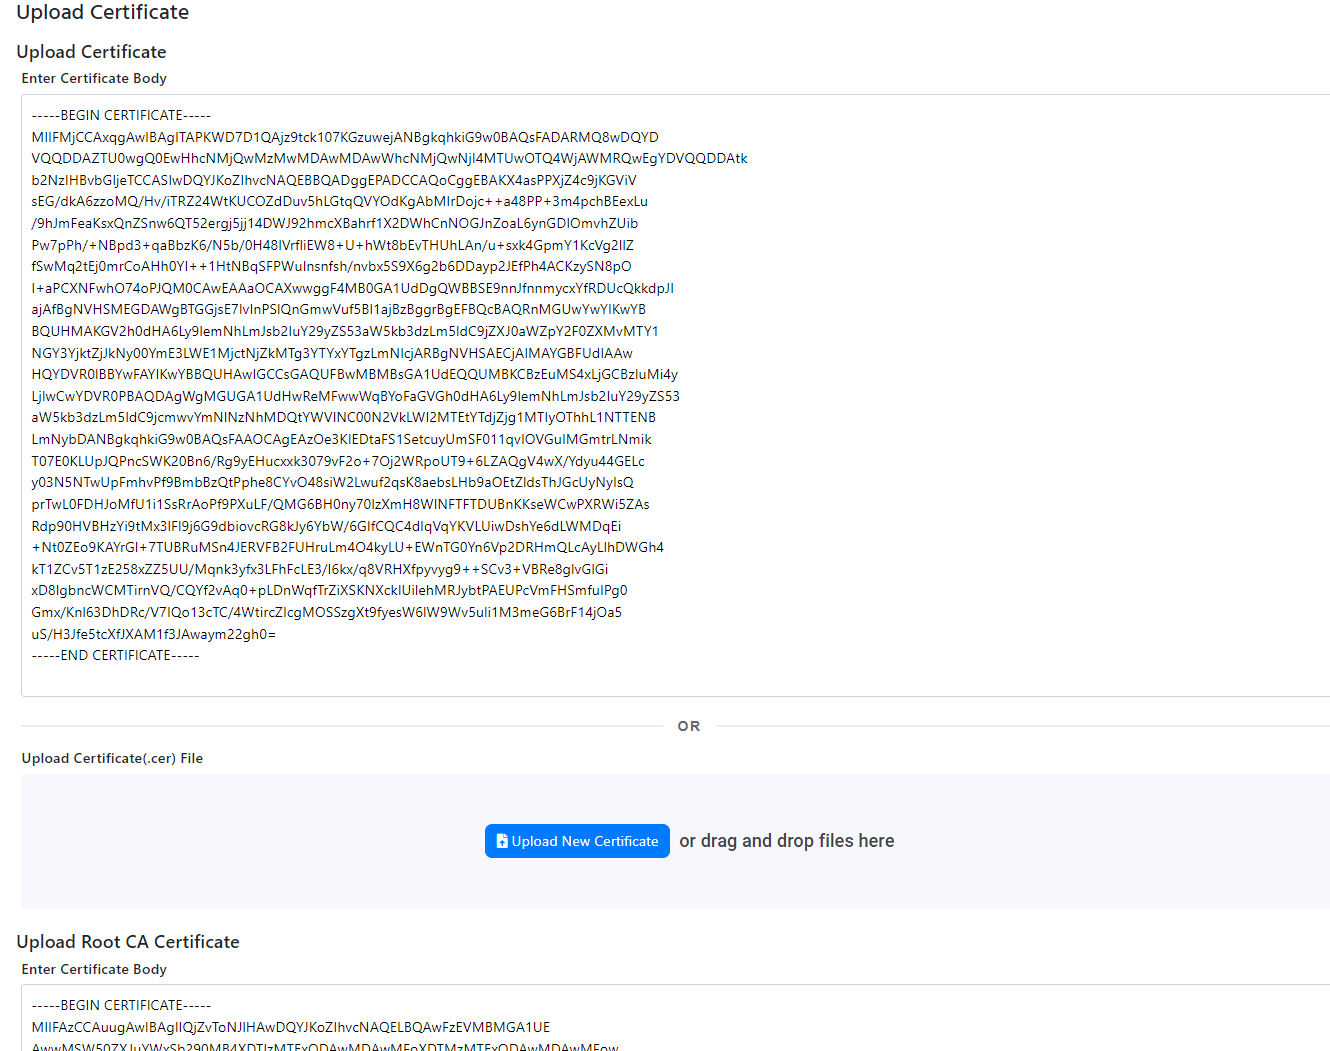
You will now have both the RADIUS server certificate and the Root CA certificate listed under your certificates.
Step 5: Add Certificate Access Policy to RADIUS Network Policy
Now that you have configured Classic RADIUS and/or RadSec, setup your CAs, and added the server certificate, you can add your access policies. Access policies define the conditions under which a user or device can connect to your network. Each policy can have multiple access policies and they are evaluated in the order they are sorted.
-
Begin in the Access Policies section of the RADIUS network policy. By default, there will be no access policies listed.
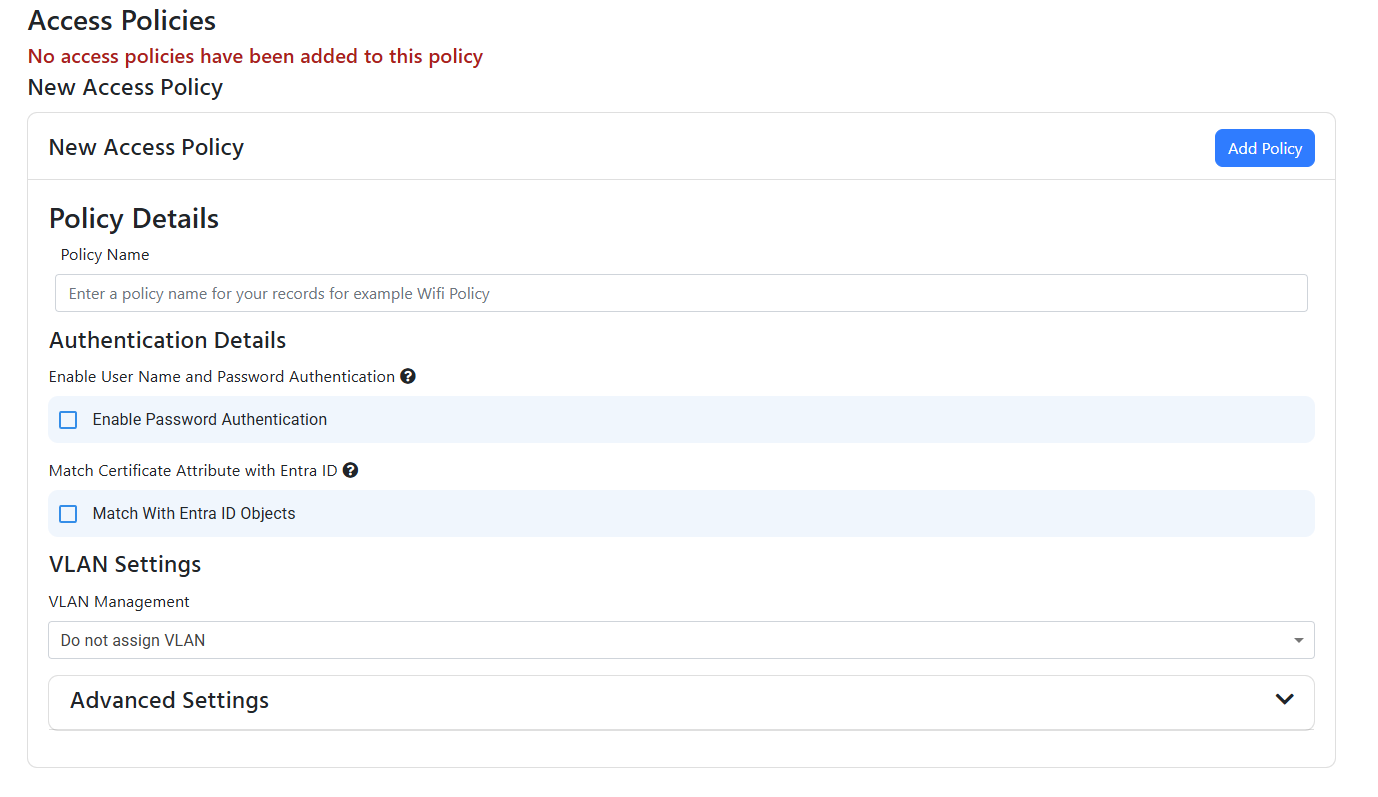
-
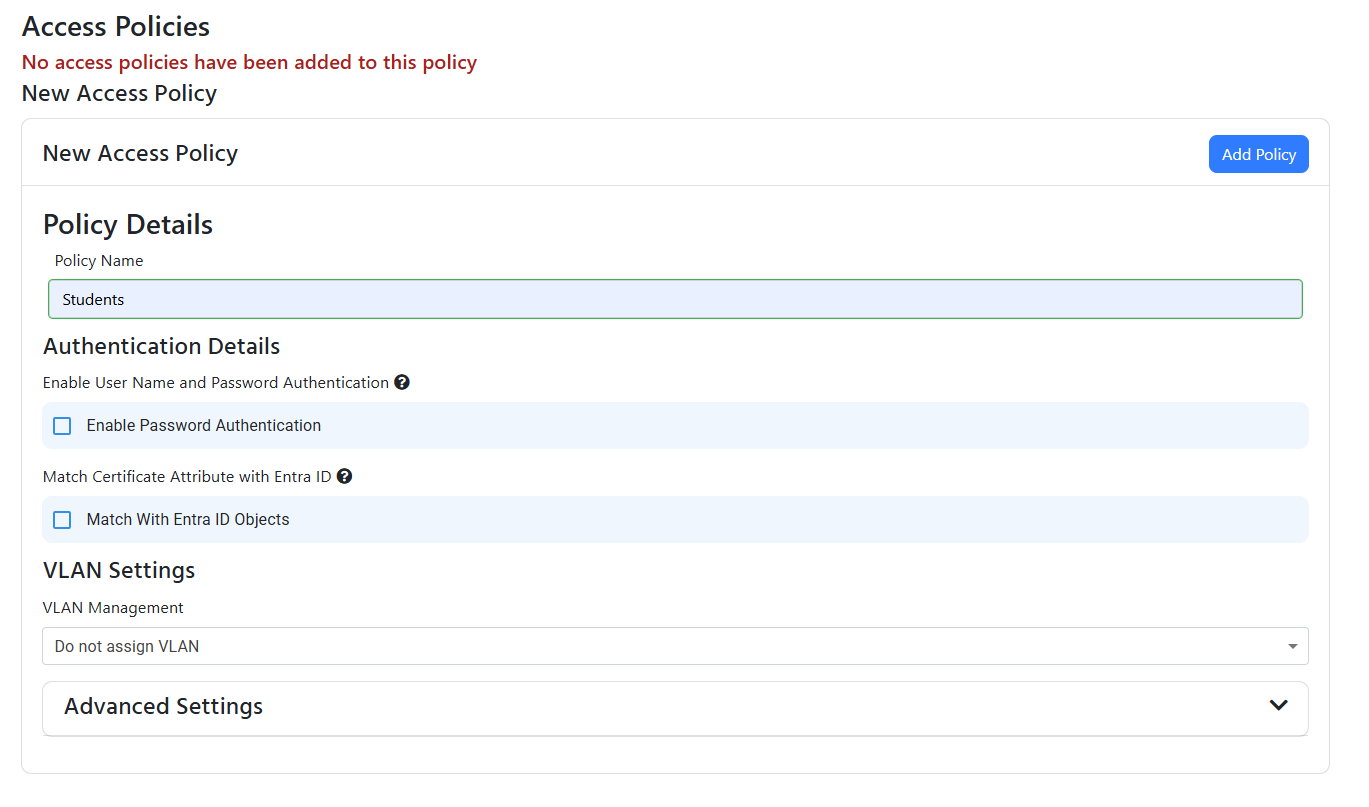
Enter the friendly name of the access policy which is used for your records to easily identify the policy. In this example we’ll configure the RADIUS server as if it was for a school, so we will name the access policy “Students”. Replace this with a name that makes sense for your use case.
-
For this policy we only want to enable EAP-TLS, so we will leave the Enable Password Authentication checkbox unchecked.
Configure Certificate Matching Options for Cloud RADIUS Policies
There are a few different ways you can match the certificate presented by the user or device to the access policy. In this guide we will focus on the four most common methods:
- CA Matching: If you only issue certificates for students from these CAs, then you can leave everything unchecked. and just assign the VLAN if required.
- Entra ID User Matching: EZRADIUS can extract the user UPN or user ID from a field of the certificate and validate with Entra ID that the user exists and even assign VLAN based on the groups the user is a member of.
- Entra ID Device Matching: EZRADIUS can extract the Entra ID device ID from a field of the certificate and validate with Entra ID that the device exists and even assign VLAN based on the groups the device is a member of.
- Intune Device Matching: EZRADIUS can extract the Intune device ID from a field of the certificate and validate with Intune that the device exists and is compliant with your Intune policies.
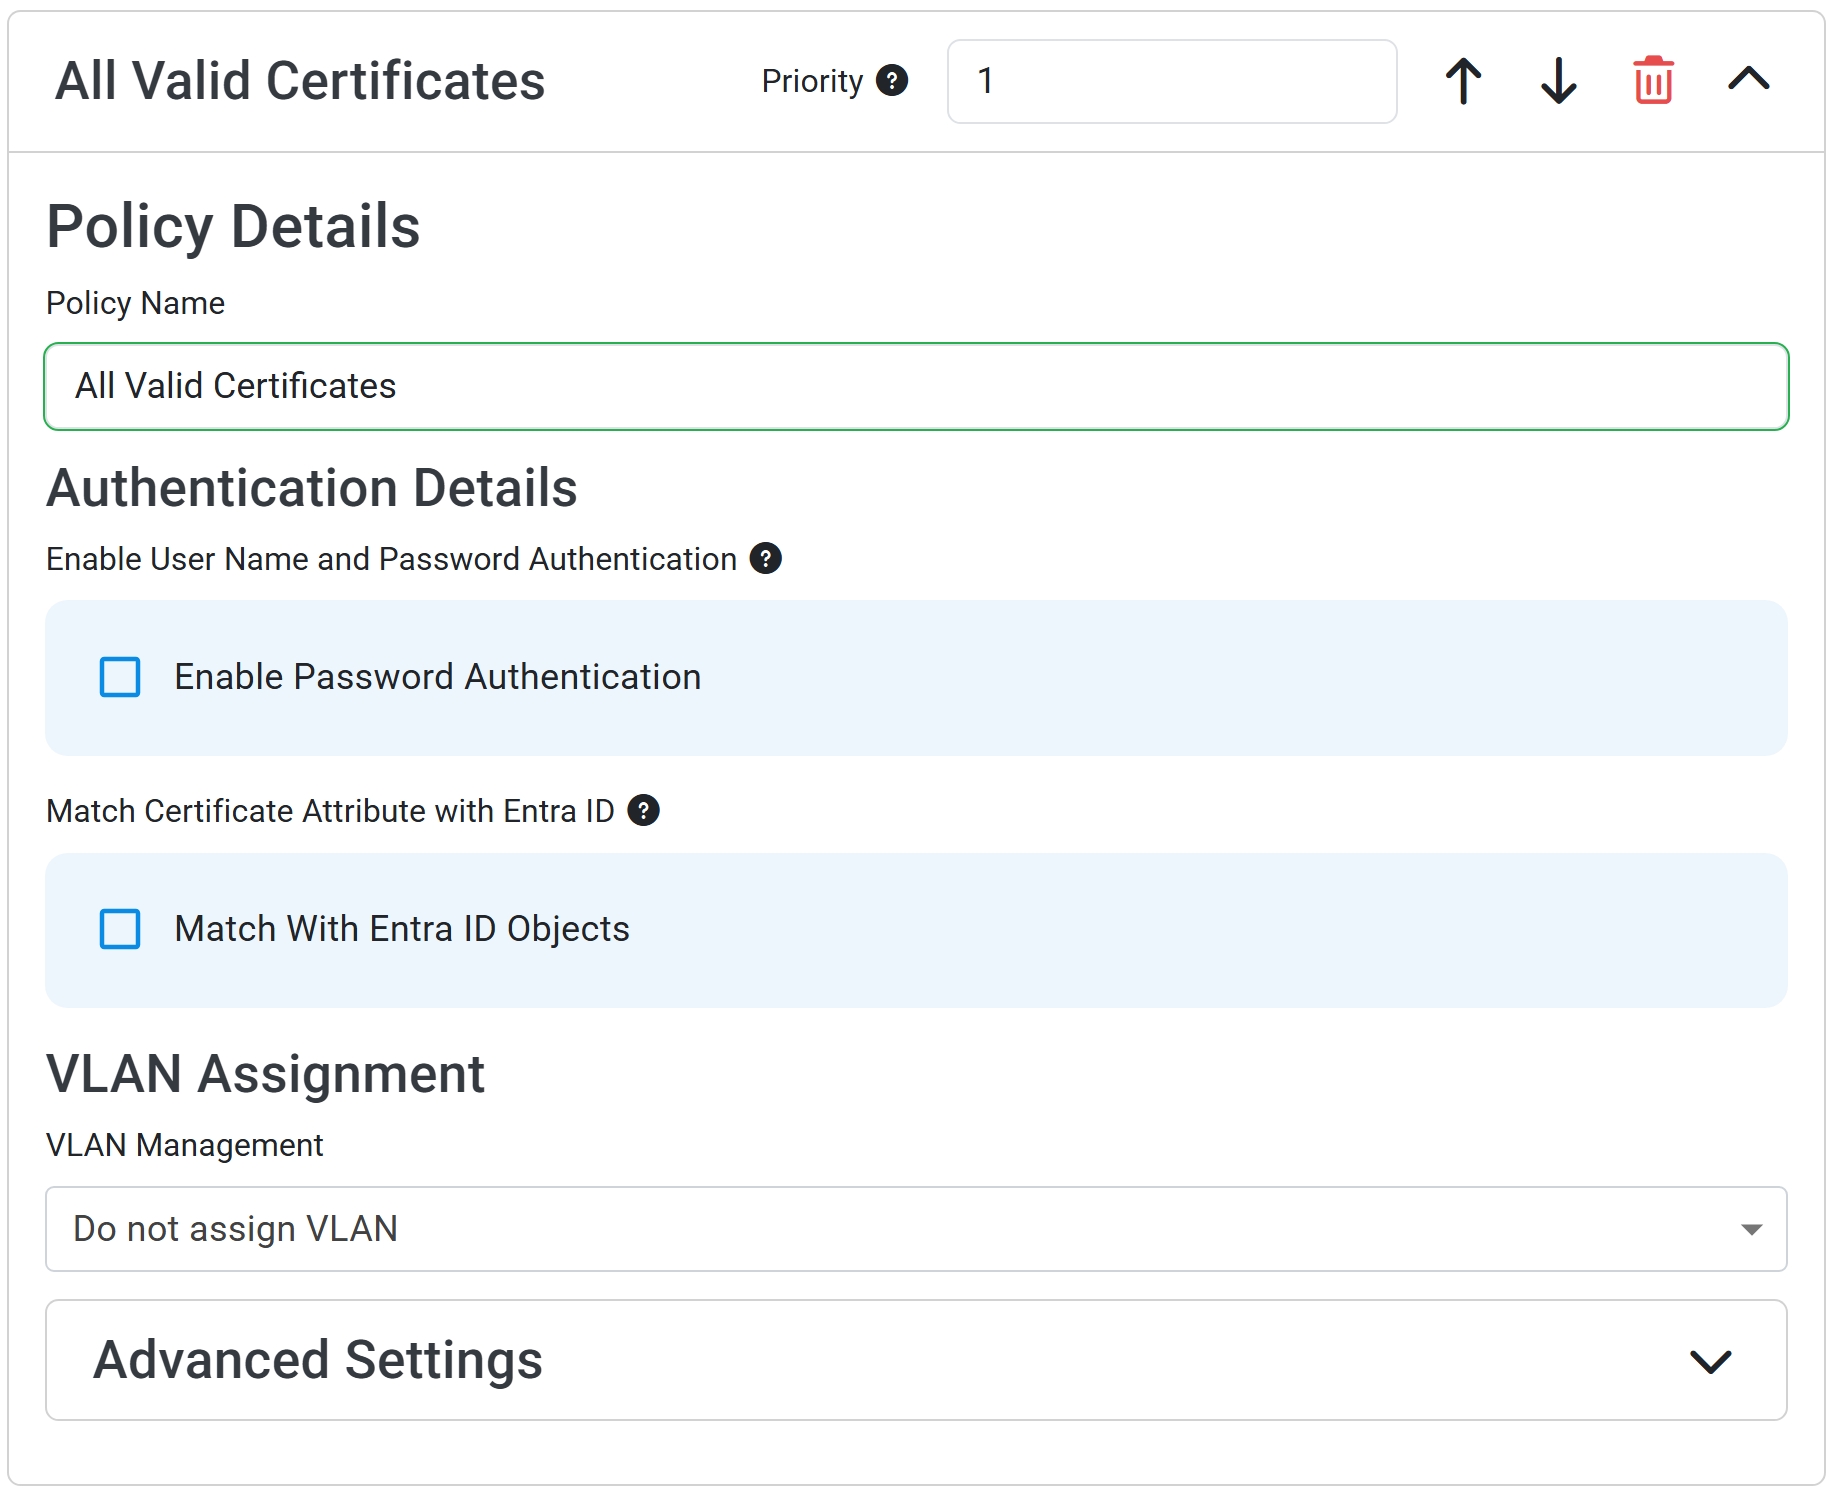
By default, EZRADIUS will allow any certificate issued by a Trusted CA to authenticate, without requiring any additional matching criteria. If you want all valid certificates to be accepted:
-
Click Add Access Policy to create a blank access policy.
-
Provide a Policy Name, such as “All Valid Certificates”.
-
Leave all fields unchecked and in their default state.
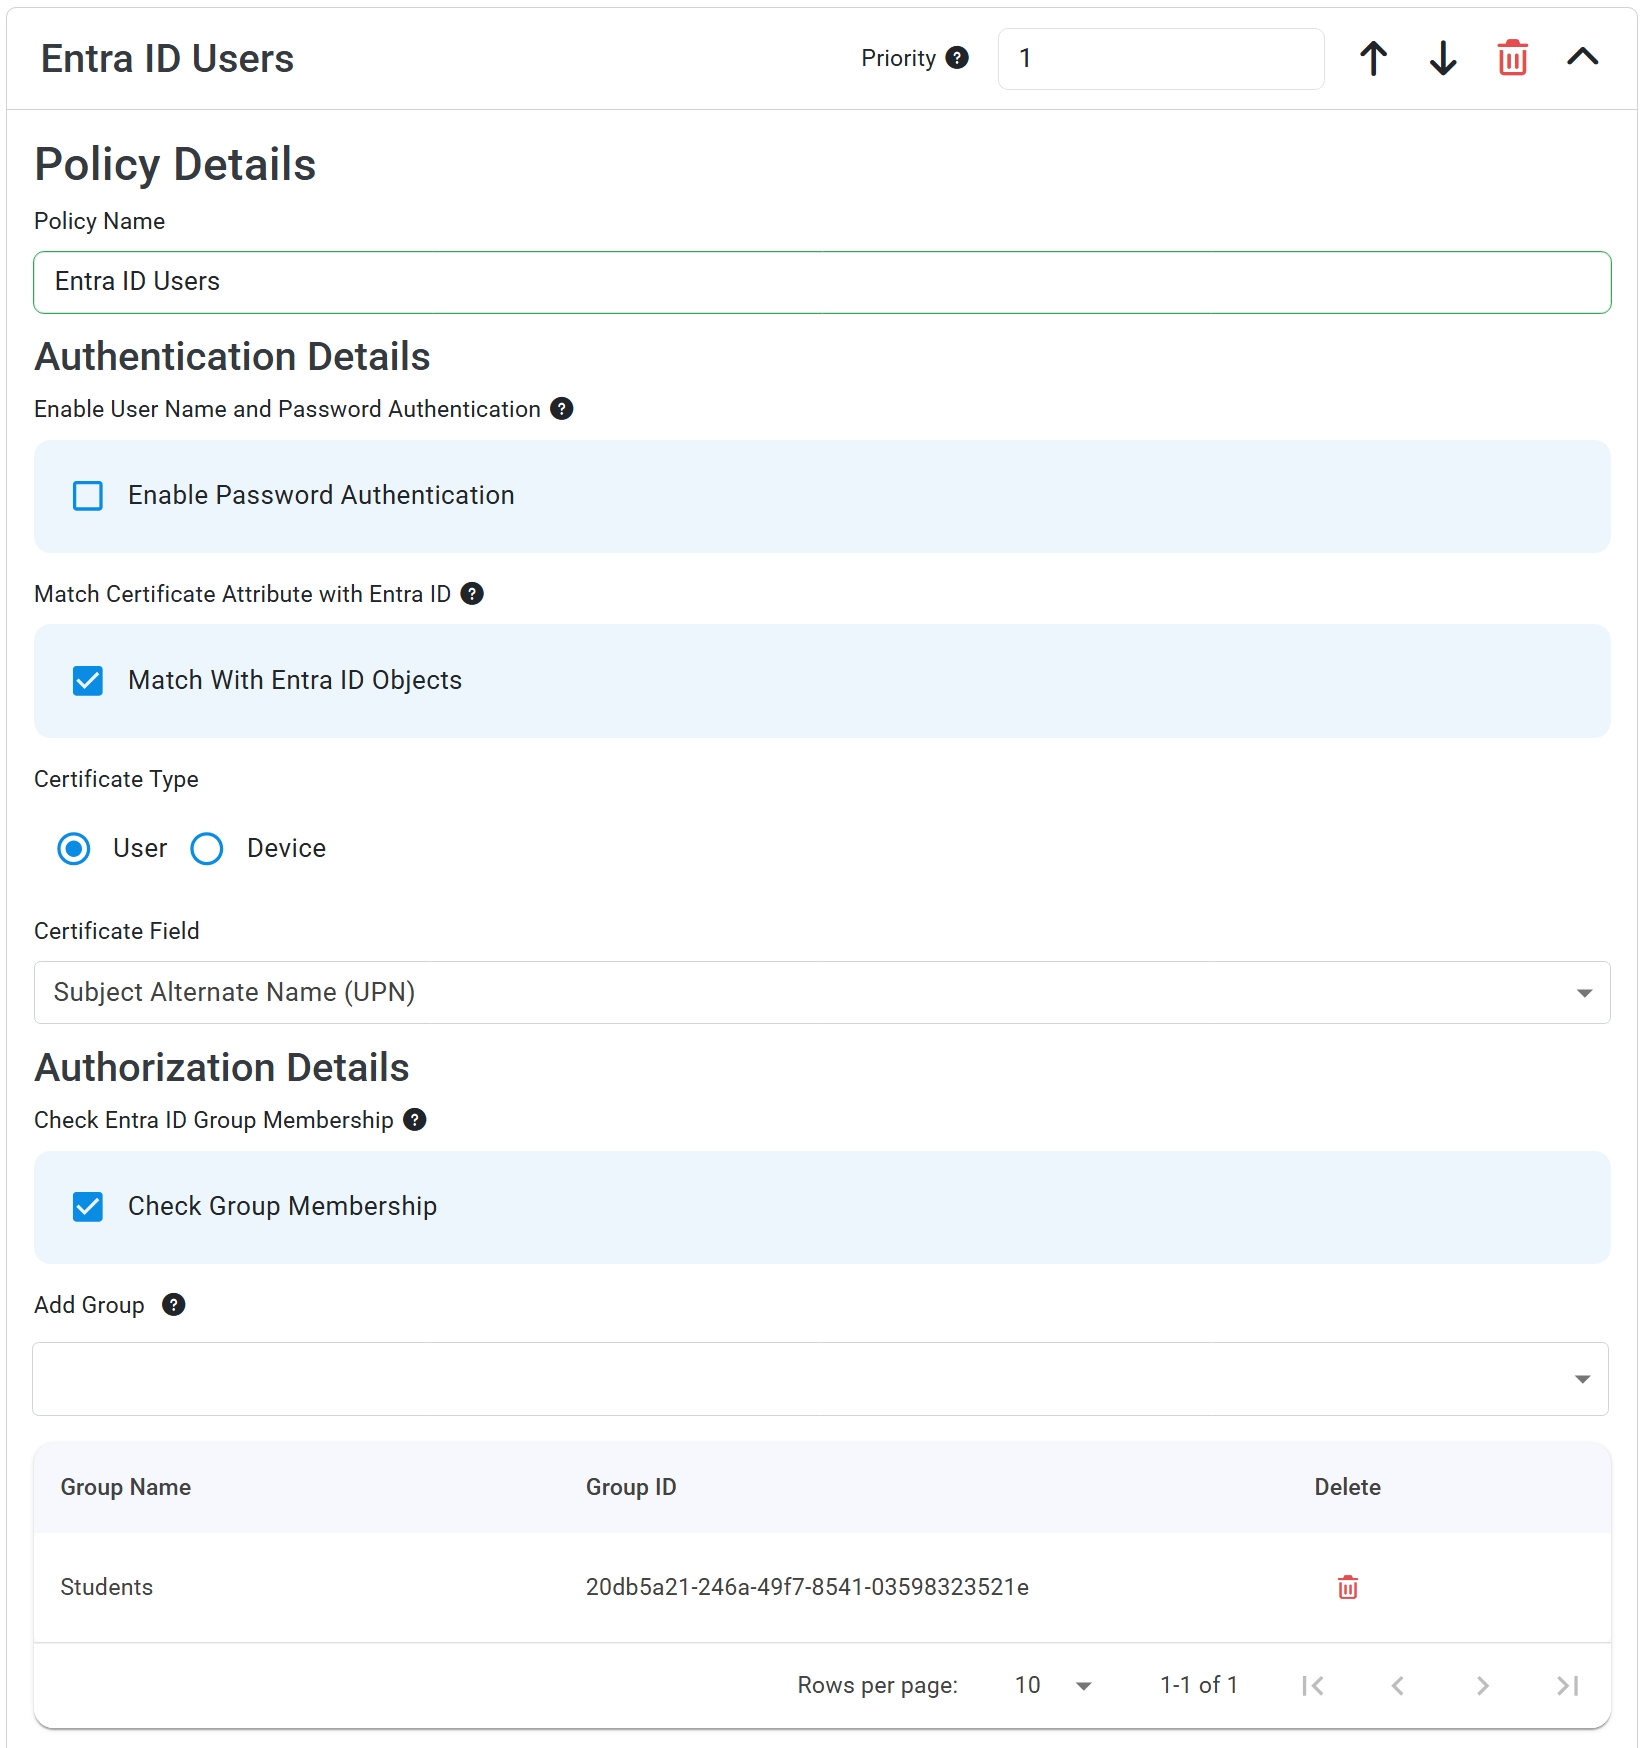
If you want to restrict an access policy to only allow user certificates from valid Entra ID users, follow these steps:
- Check the Match With Entra ID Objects checkbox.
- For Certificate Type, select User.
- Under Certificate Field, select which certificate field contains the user’s User Principal Name (UPN). Usually this is Subject Alternative Name (UPN).
Now that you have matched the certificate with a valid Entra ID user, you can optionally also check that the user is in a specific Entra ID group.
- Check the Check Group Membership checkbox.
- Under the Add Group section, type in the name of the Entra ID group you want to check for membership. Select it from the dropdown list.
You should now have an access policy that only allows user certificates from valid Entra ID users, optionally restricted to specific Entra ID groups:
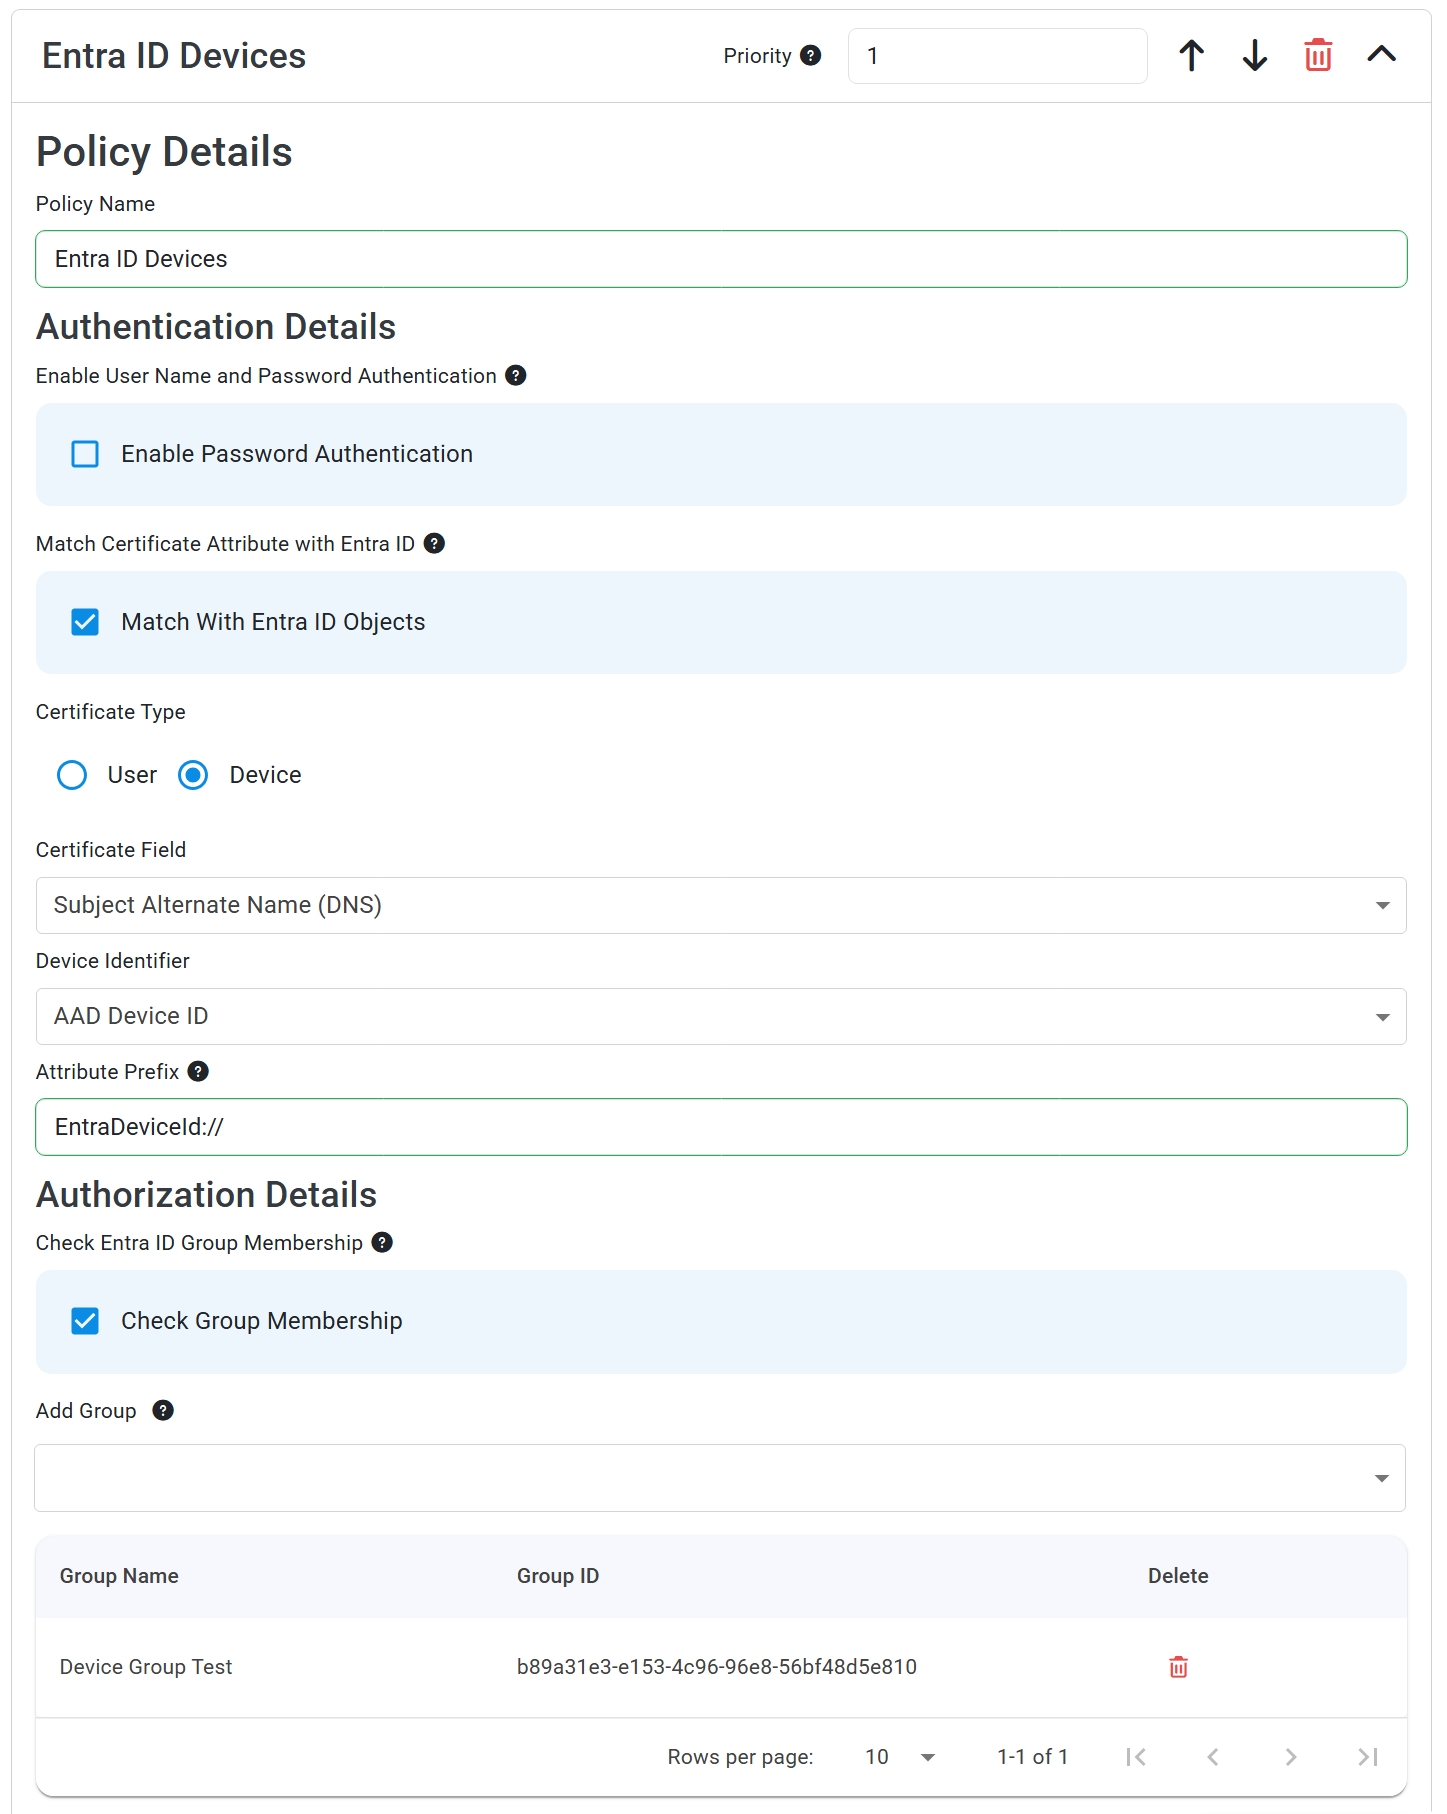
If you want to restrict an access policy to only allow device certificates from valid Entra ID devices, follow these steps:
- Check the Match With Entra ID Objects checkbox.
- For Certificate Type, select Device.
- Under Certificate Field, select which certificate field contains the device’s ID. Usually this is Subject Alternative Name (DNS).
- For Device Identifier, set this to AAD Device ID, which is the Entra ID identifier for the device.
- If your certificate value has a prefix before the actual device ID, you can specify it here so that the system correctly extracts the device ID from the certificate.
Now that you have matched the certificate with a valid Entra ID device, you can optionally also check that the device is in a specific Entra ID group.
- Check the Check Group Membership checkbox.
- Under the Add Group section, type in the name of the Entra ID group you want to check for membership. Select it from the dropdown list. Note that this group has to contain the device itself, not the user who owns the device.
You should now have an access policy that only allows device certificates from valid Entra ID devices, optionally restricted to specific Entra ID groups:
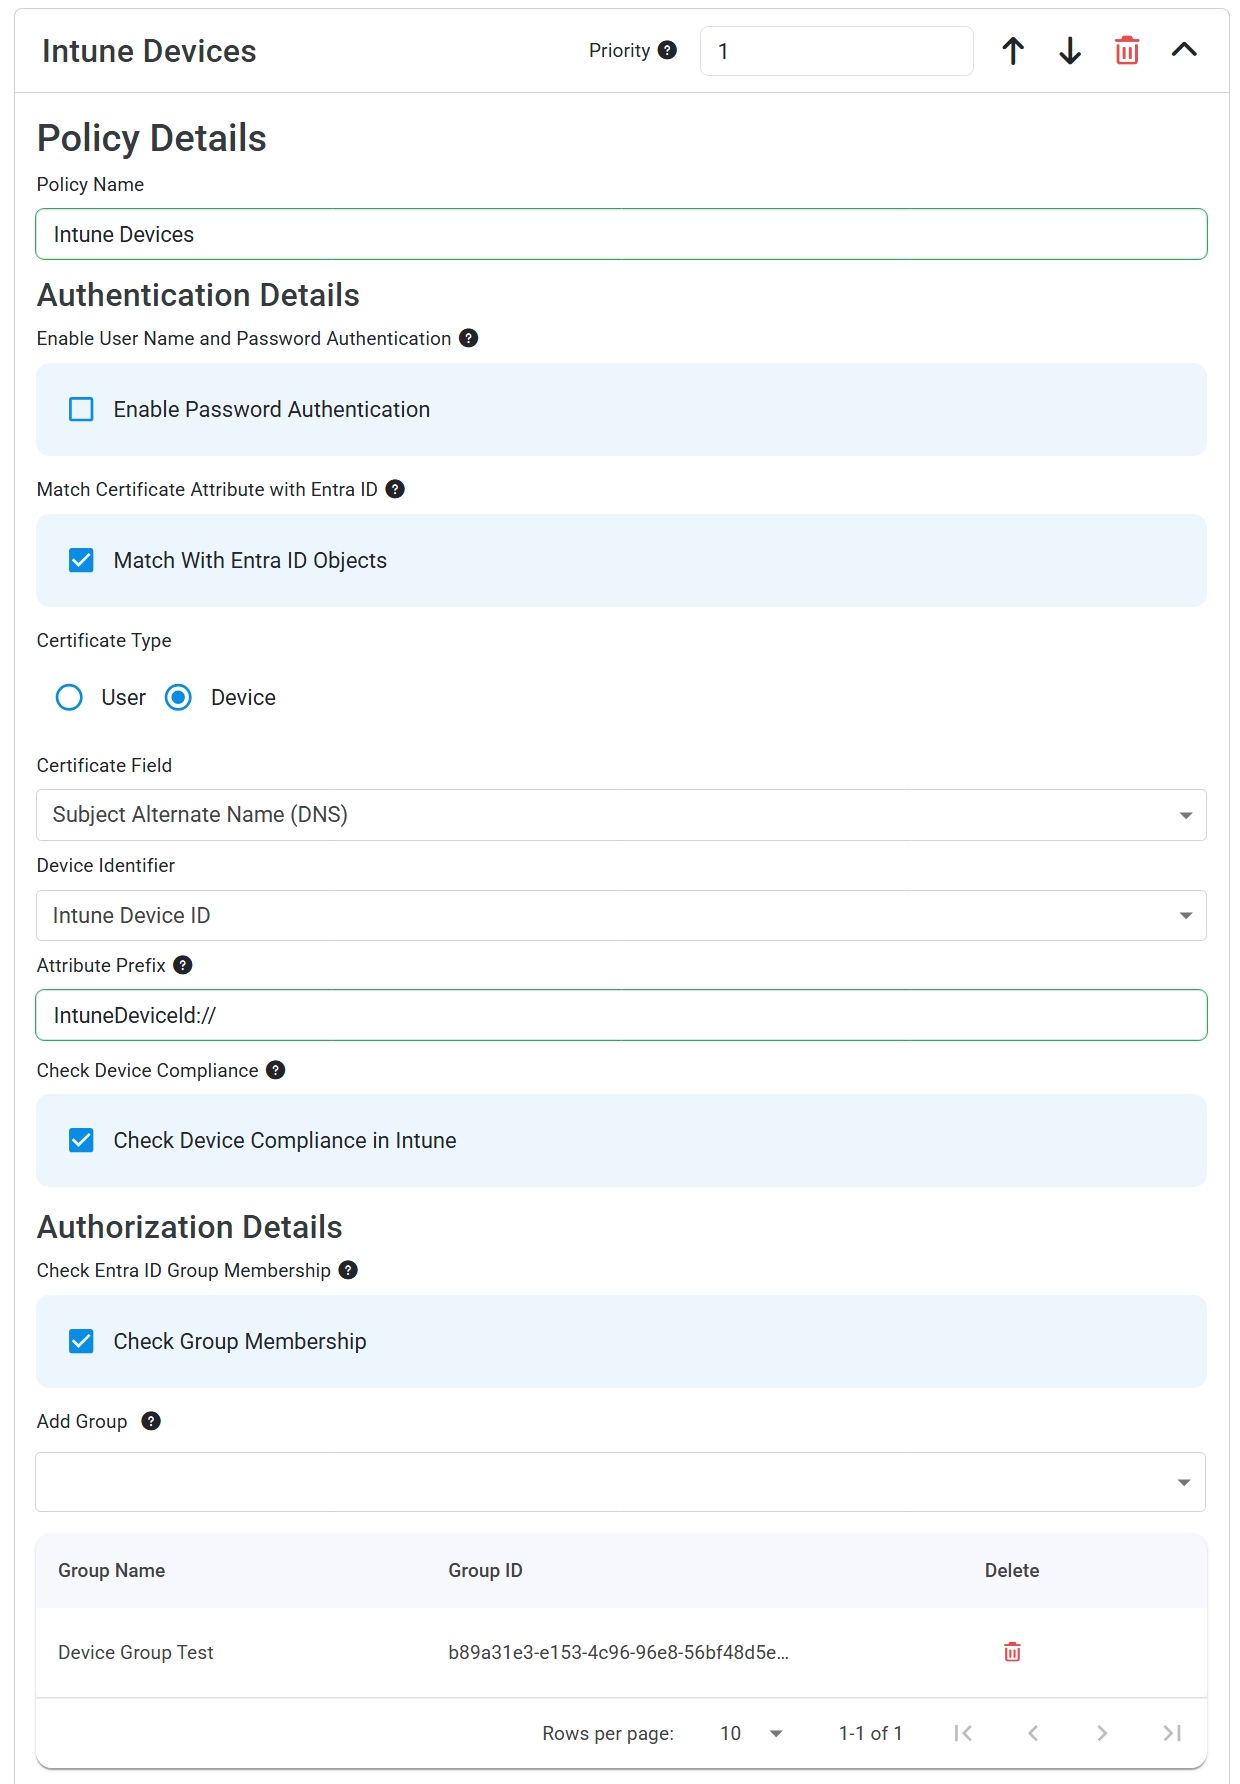
If you want to restrict an access policy to only allow device certificates from valid Intune-managed devices, follow these steps:
- Check the Match With Entra ID Objects checkbox.
- For Certificate Type, select Device.
- Under Certificate Field, select which certificate field contains the device’s ID. Usually this is Subject Alternative Name (DNS).
- For Device Identifier, set this to Intune Device ID, which is the Intune identifier for the device.
- If your certificate value has a prefix before the actual device ID, you can specify it here so that the system correctly extracts the device ID from the certificate.
Now that you have matched the certificate with a valid Intune-managed device, you can optionally check if the device is compliant in Intune before granting access. This ensures that only devices meeting your organization’s compliance requirements are allowed to match against this policy.
- Check the box for Check Device Compliance in Intune.
If you want to also restrict access based on group membership, follow these steps:
- Check the Check Group Membership checkbox.
- Under the Add Group section, type in the name of the Entra ID group you want to check for membership. Select it from the dropdown list. Note that this group has to contain the device itself, not the user who owns the device.
You should now have an access policy that only allows device certificates from valid Intune-managed devices, optionally restricted to specific Entra ID groups:
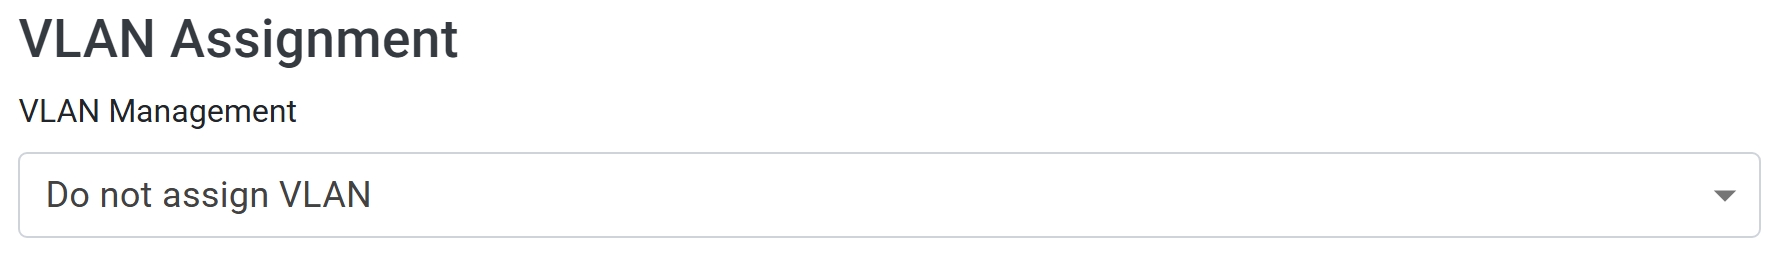
By default, EZRADIUS will not set a Virtual LAN (VLAN), and your network will use its own default VLAN. However, you can specify a specific VLAN in each access policy to assign specific users and devices to their own VLAN and override the default.
This is useful for putting specific Entra ID users or groups into their own VLANs, or putting compliant devices into a separate VLAN from non-compliant devices.
If you do not want to assign a VLAN for this access policy, keep VLAN Management set to Do not assign VLAN. This will ensure that the network uses its default VLAN for all users and devices under this access policy.
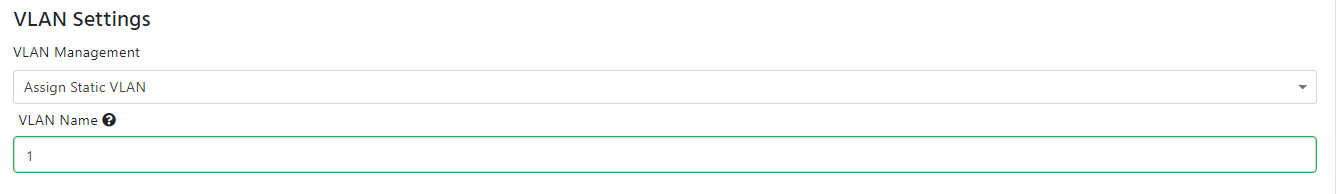
If you want to assign a specific, static VLAN to all devices that match against this access policy, set VLAN Management to Assign Static VLAN and enter the VLAN ID in the VLAN Name field. This ensures that all matching devices are placed in the specified VLAN, overriding the network’s default VLAN.
If you want to assign different VLANs to different users or devices based on their attributes, you should either:
- Set up multiple access policies, each with a different static VLAN and different matching attributes.
- Use dynamic VLAN assignment based on certificate values to automatically assign VLANs according to the information contained in the user’s certificate.
More information on how to use this field is available in our reference architectures
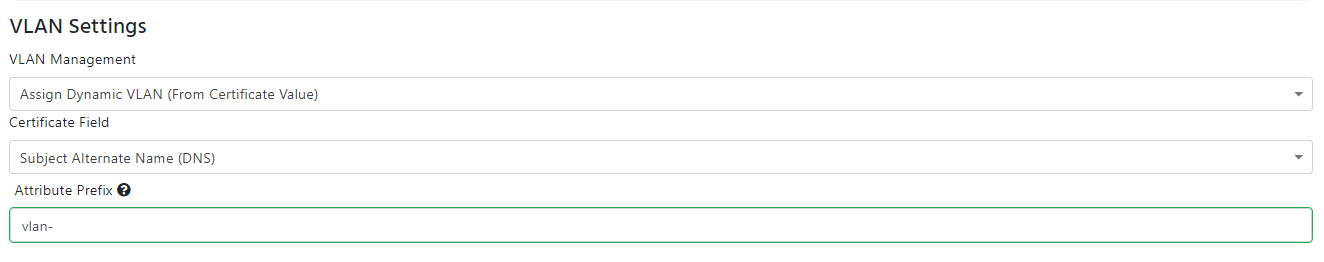
VLANs can also be set based on a VLAN ID specified within the certificate authenticating to the network. To configure this:
-
From the VLAN Management dropdown, select Assign Dynamic VLAN (From Certificate Value).
-
Under Certificate Field, select the field in the certificate that contains the VLAN ID.
-
If there’s a prefix in front of the VLAN ID in the certificate, enter the prefix in the Prefix field. EZRADIUS will ignore this prefix when assigning VLANs.
Done!
You have successfully created a Cloud RADIUS network policy that uses certificates for authentication. Make sure to test the configuration with a device to ensure everything is working as expectedAdvanced Settings
If you have more advanced requirements for your access policies, you can configure them by expanding the Advanced Settings tab and configuring the available options.
Advanced Access Policy Settings
Optionally configure advanced settings for your access policies
If you want to bypass authentication for devices based on their MAC address, you can:
- Check the box for Enable MAC Authentication Bypass (MAB).
- Either directly add your MAC addresses, or enable Bulk Upload Addresses to add multiple MAC addresses at once.
Collapses this section and completes the checkmark.
EZRADIUS checks CRLs (Certificate Revocations Lists) by default but if you also want to check OCSP, you can check the Enable OCSP checkbox. you can read more about the difference between CRL and OCSP here
Collapses this section and completes the checkmark.
If you want to require that the certificate being used for authentication has specific Extended Key Usages such as “Client Authentication”:
- Check the box for Require Extended Key Usage.
- Either select an EKU from Predefined Extended Key Usages, or enter a custom EKU in the Custom Extended Key Usage > Name and Object Identifier fields.
- Click Add Extended Key Usage to add the EKU configuration.
Collapses this section and completes the checkmark.
If you want to match attributes in the request (for example, matching the SSID name sent as a called station ID), you can add the attributes in the Match Attributes in Request and enter the value and the matching scheme (either contains or equals). Some common attributes to match are:
- Called-Station-ID: Usually set-up to contain the SSID of the network or the MAC address of a device when carrying out MAC-Authentication-Bypass.
- NAS Identifier (NAS-ID): Usually set-up to contain the SSID of the network or the MAC address of a device when carrying out MAC-Authentication-Bypass.
Collapses this section and completes the checkmark.
If you want to send attributes in the response (for example, sending the Filter-Id to the device), you can add the attributes in the Sent Attributes in Response and enter the value. Supported attributes are:
- Filter-Id: Can be used to assign a pre-defined access control list (ACL) to the user that successfully authenticates with the access policy
- Cisco-AVPair: Cisco-specific attribute
Collapses this section and completes the checkmark.
Priority Order of Access Policies
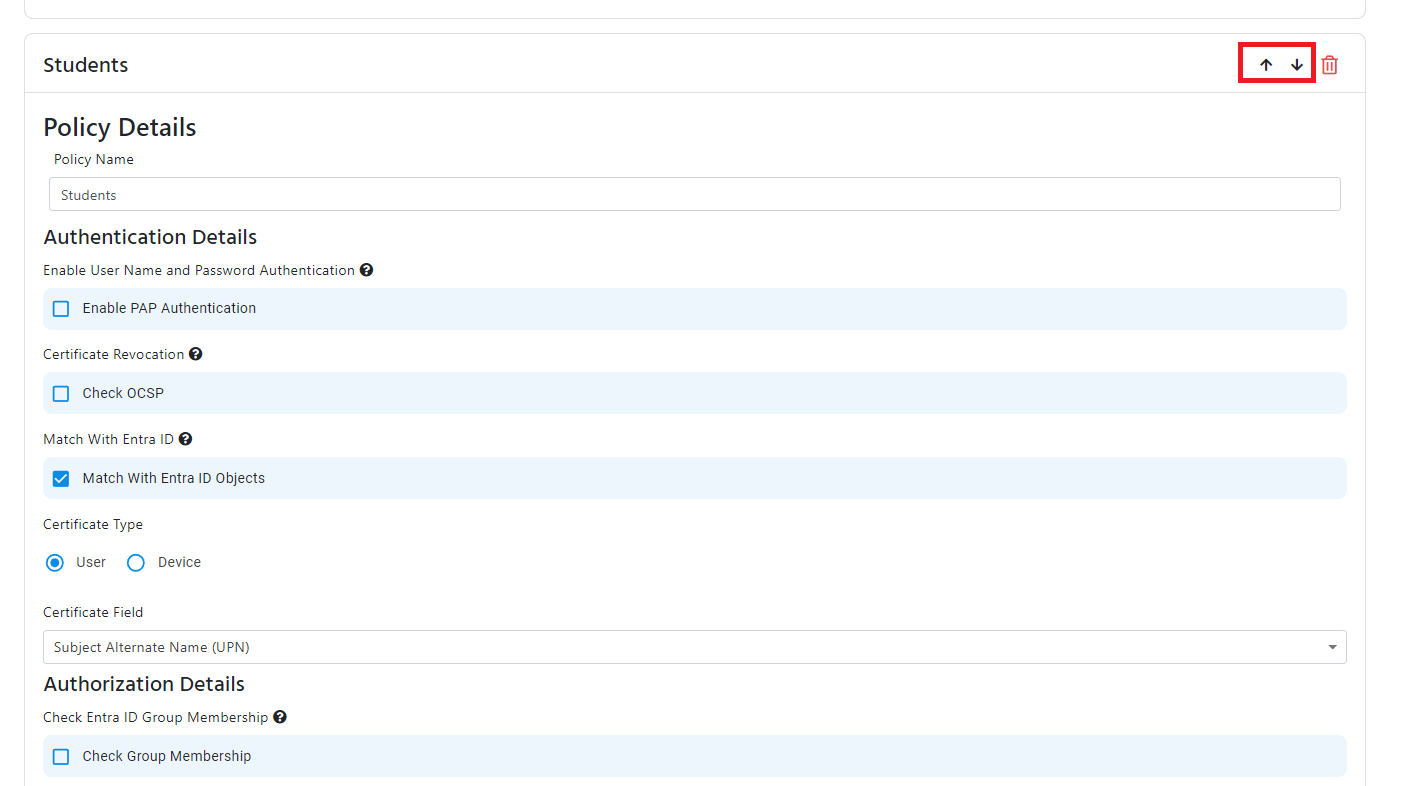
The access policies are checked in the order they are sorted, you can change the order of the access policies by clicking on the up and down arrows on the right side of the access policy.
- Once your policy is ready, save the policy.