



How-To: Distribute Keytos Shield Network Profiles to Apple Devices with Iru (formerly Kandji)
Overview - How to Set Up Certificate-Based Wi-Fi for Iru Managed Apple Devices with Keytos Shield
Iru (formerly Kandji) is a device management platform for macOS, iOS, iPadOS, tvOS, and visionOS devices, among others. Pairing Iru with Keytos Shield lets every managed Apple device get its own certificate from your Shield Cloud PKI and use it to join your Wi-Fi with passwordless EAP-TLS authentication, so there is no shared Wi-Fi password to leak or rotate.
This guide walks you through enabling static SCEP in Keytos Shield, adding your Shield Root CA to Iru, and building an Iru Wi-Fi Library Item that requests a certificate from Shield and connects your devices to your network automatically.
How Does Keytos Shield Work with Iru on Apple Devices?
Connecting an Iru managed Apple device to your Shield-protected network takes three pieces, which you will configure in this guide:
- Trusted certificate: Your Shield Root CA certificate is pushed to your devices so they trust your Shield RADIUS servers and the certificates Shield issues.
- SCEP certificate: Each device requests its own unique certificate from Keytos Shield using the Simple Certificate Enrollment Protocol (SCEP). Iru uses Shield’s static SCEP URL and password to request the certificate on the device’s behalf.
- Wi-Fi profile: The Wi-Fi profile tells the device which network to join, to authenticate with EAP-TLS using its SCEP certificate, and which RADIUS servers to trust.
In Iru, the SCEP certificate is configured inside the Wi-Fi Library Item. Apple devices require the identity certificate to be in the same configuration profile as the Wi-Fi settings that use it, so you don’t need a separate SCEP Library Item.
Prerequisites for Distributing Keytos Shield Network Profiles with Iru
Before you begin, make sure you have completed the following:
- The Keytos Entra ID applications are registered in your tenant.
- You have signed up for a Keytos Shield Plan.
- You have existing access policies in Keytos Shield.
- You are a Subscription Owner or Network Administrator.
- You are an Iru Administrator.
This guide creates device certificates containing a serial number, not an Entra ID user or device identifier. It requires the All Valid Certificates (CA matching) configuration described in Shield network access policies. This configuration accepts any valid certificate from a trusted CA without checking Entra ID identity, group membership, or Intune compliance. Only proceed if CA-based authorization meets your network’s access requirements. If you require those identity checks, use a certificate configuration that supplies the identifier your policy expects instead of following this serial-number recipe.
You also need Apple Push Notification service (APNs) configured in Iru, with your devices enrolled, so Iru can push profiles to them.
Step-by-Step Guide - How to Issue SCEP Certificates and Push a Wi-Fi Profile to Apple Devices with Keytos Shield and Iru
Step 1 - How to Enable Static SCEP for Iru in Keytos Shield
Iru requests certificates from Keytos Shield with static SCEP. To turn it on, tell Shield that you manage devices with an MDM other than the ones listed by name by enabling Other MDM. Enabling it also updates your certificate authority to support static SCEP.
In step 2, Tell us about your environment, of the Keytos Shield network security onboarding guide, ensure you have checked Other MDM, in addition to any other MDMs in your environment.
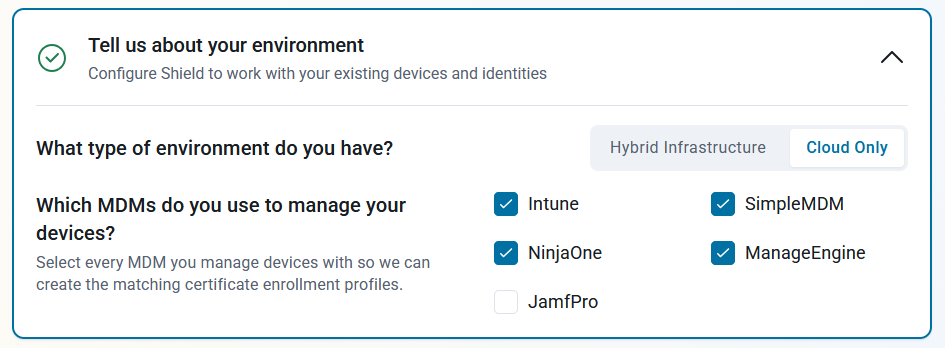
If you’ve already gone through the onboarding guide, you can update the list of MDMs you manage devices with.
-
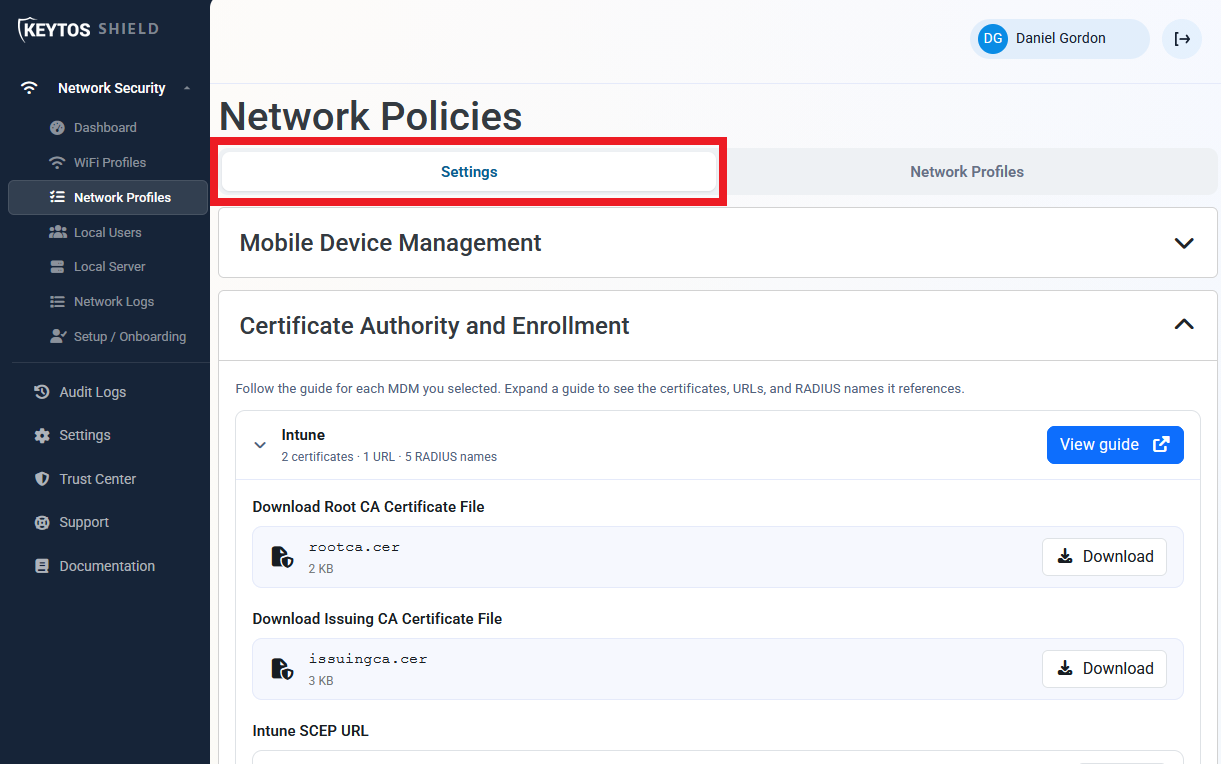
Navigate to the Keytos Shield Network profiles page from the left-hand menu.
-
At the top of the page, select the Settings tab.
-
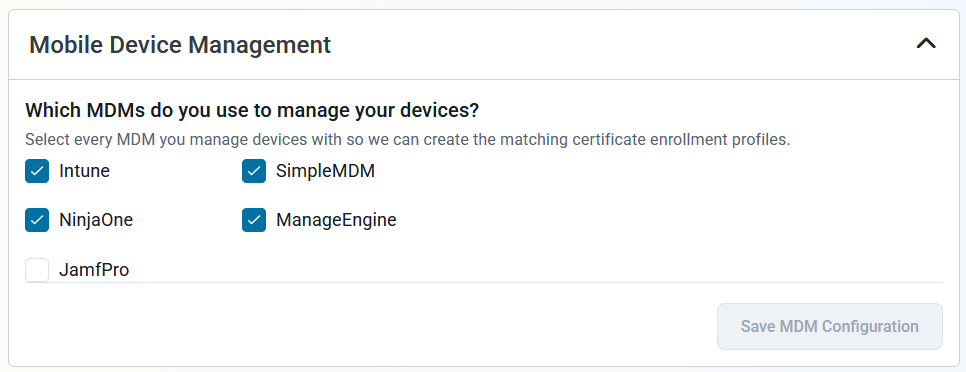
Scroll down to the bottom of the page and expand the Mobile Device Management section.
-
Ensure you have checked Other MDM in addition to any other MDMs in your environment.
Step 2 - How to Download Your Keytos Shield Root CA Certificate
Your devices need your Shield Root CA certificate so they trust your Shield RADIUS servers and the certificates Shield issues.
You can download your Shield Root CA certificate from the onboarding guide or from the network profiles page.
If you’re currently going through the onboarding guide, you can download your Shield Root CA certificate in step 6, Set Up Mobile Device Management (MDM).
-
In step 6 of the Keytos Shield onboarding guide, expand Other MDM.
-
Under Download Root CA Certificate File, click Download next to
rootca.cerand save it to your local machine.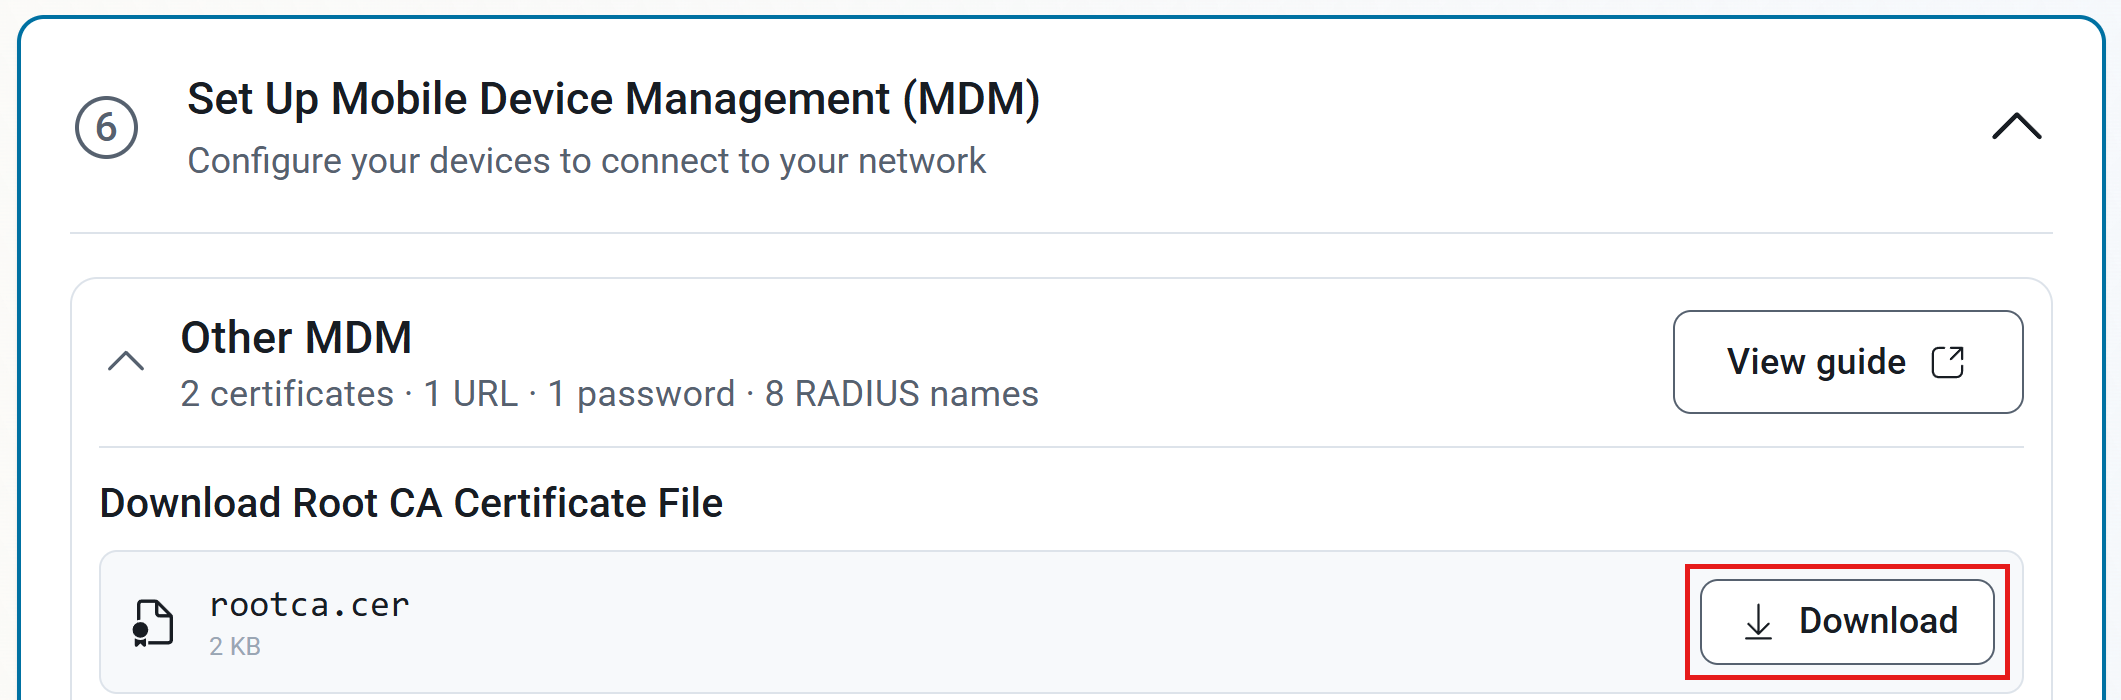
If you’ve already gone through the onboarding guide, you can download your Shield Root CA certificate from the network profiles page.
-
Log in to your Keytos Shield portal.
-
From the left-hand navigation bar, click on Network Profiles.
-
At the top of the page, select the Settings tab.
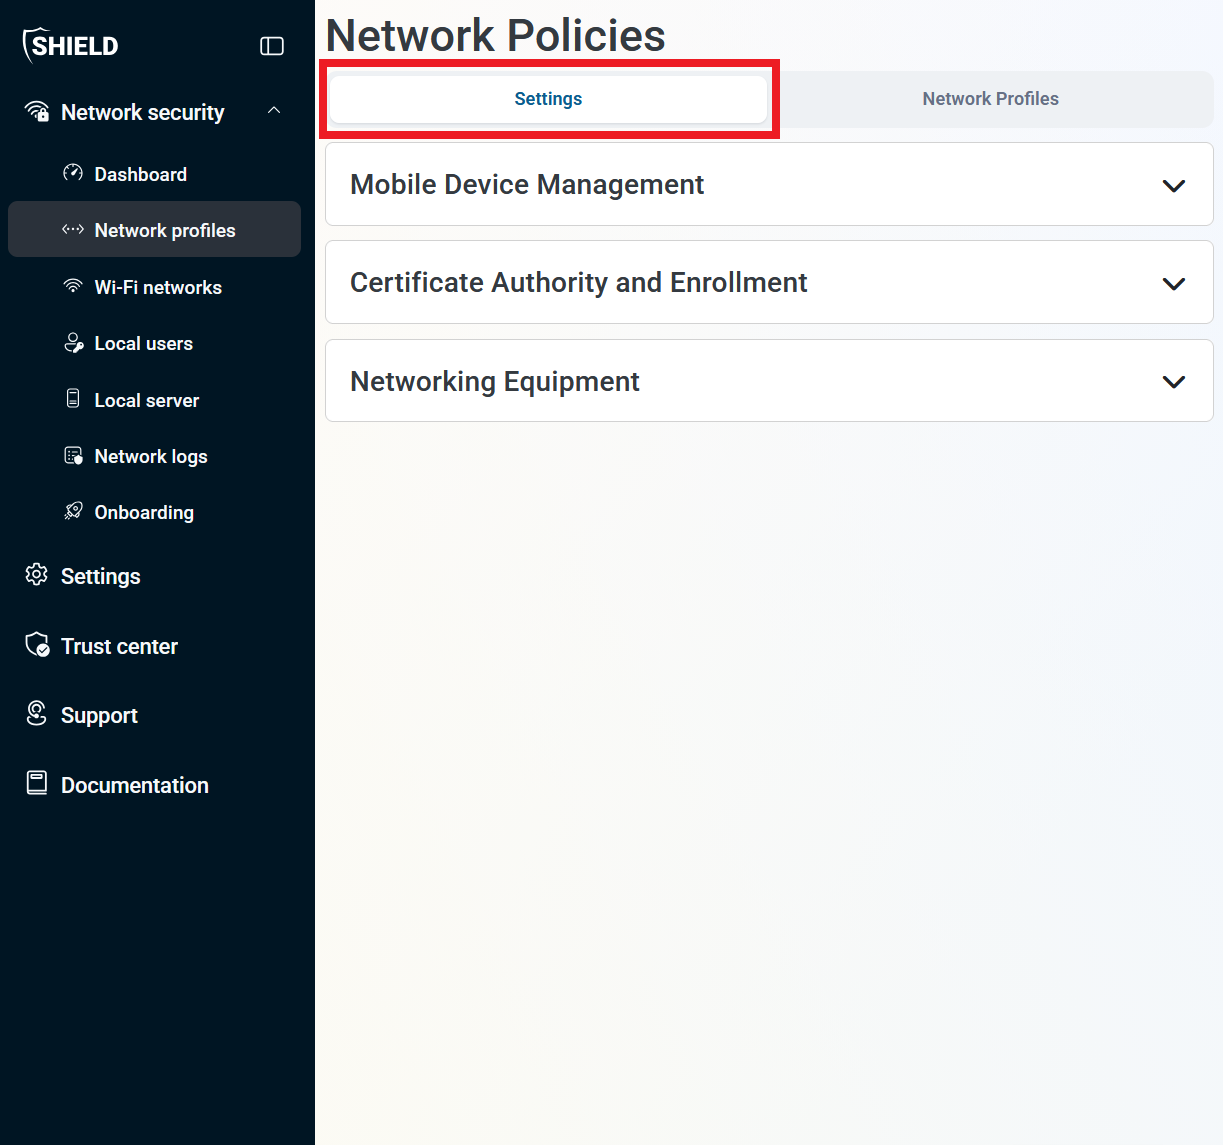
-
Scroll down to the Certificate Authority and Enrollment section and expand the Other MDM subsection.
Not seeing the Other MDM subsection? Make sure to enable Other MDM under the Mobile Device Management section further up on the page and save your changes.
-
Next to
rootca.cer, click Download and save it to your local machine. -
Next to
issuingca.cer, click Download and save it to your local machine as well.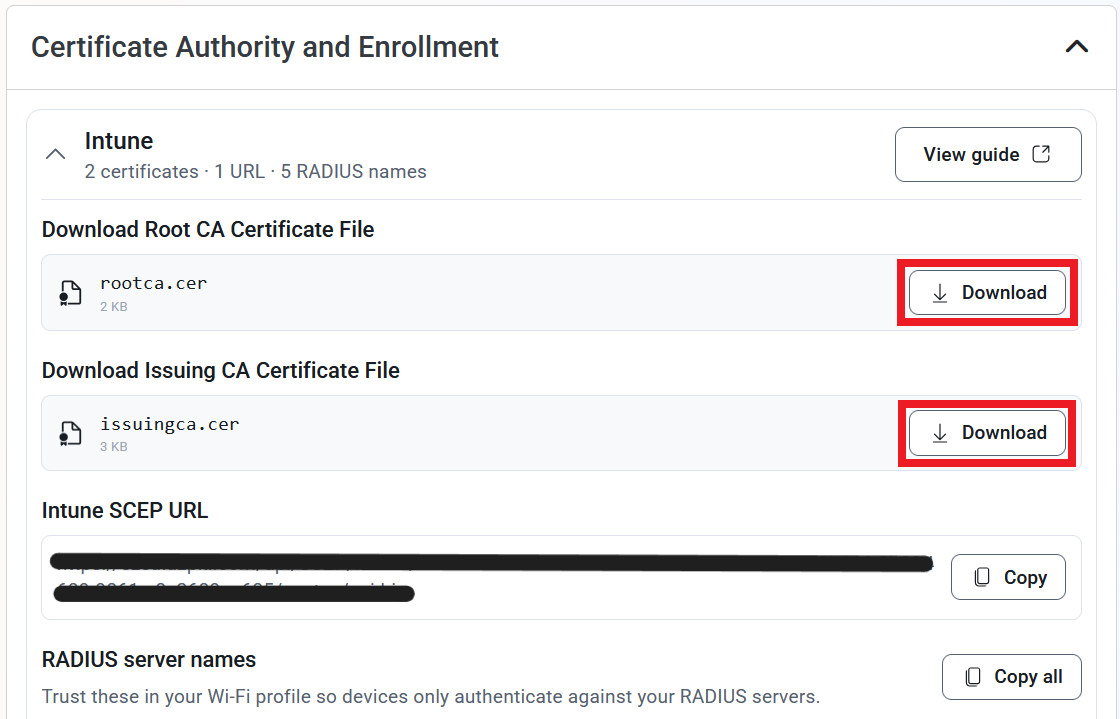
Iru only needs the rootca.cer file. You use it in the next step and again when you configure RADIUS server trust in the Wi-Fi profile.
Step 3 - How to Add Your Keytos Shield Root CA as a Trusted Certificate in Iru
Now push your Shield Root CA to your devices so they trust the certificates Shield issues. You do this with a Certificate Library Item in Iru.
-
Log in to your Iru tenant.
-
From the left-hand menu, click Library.
-
Click Add Library Item.
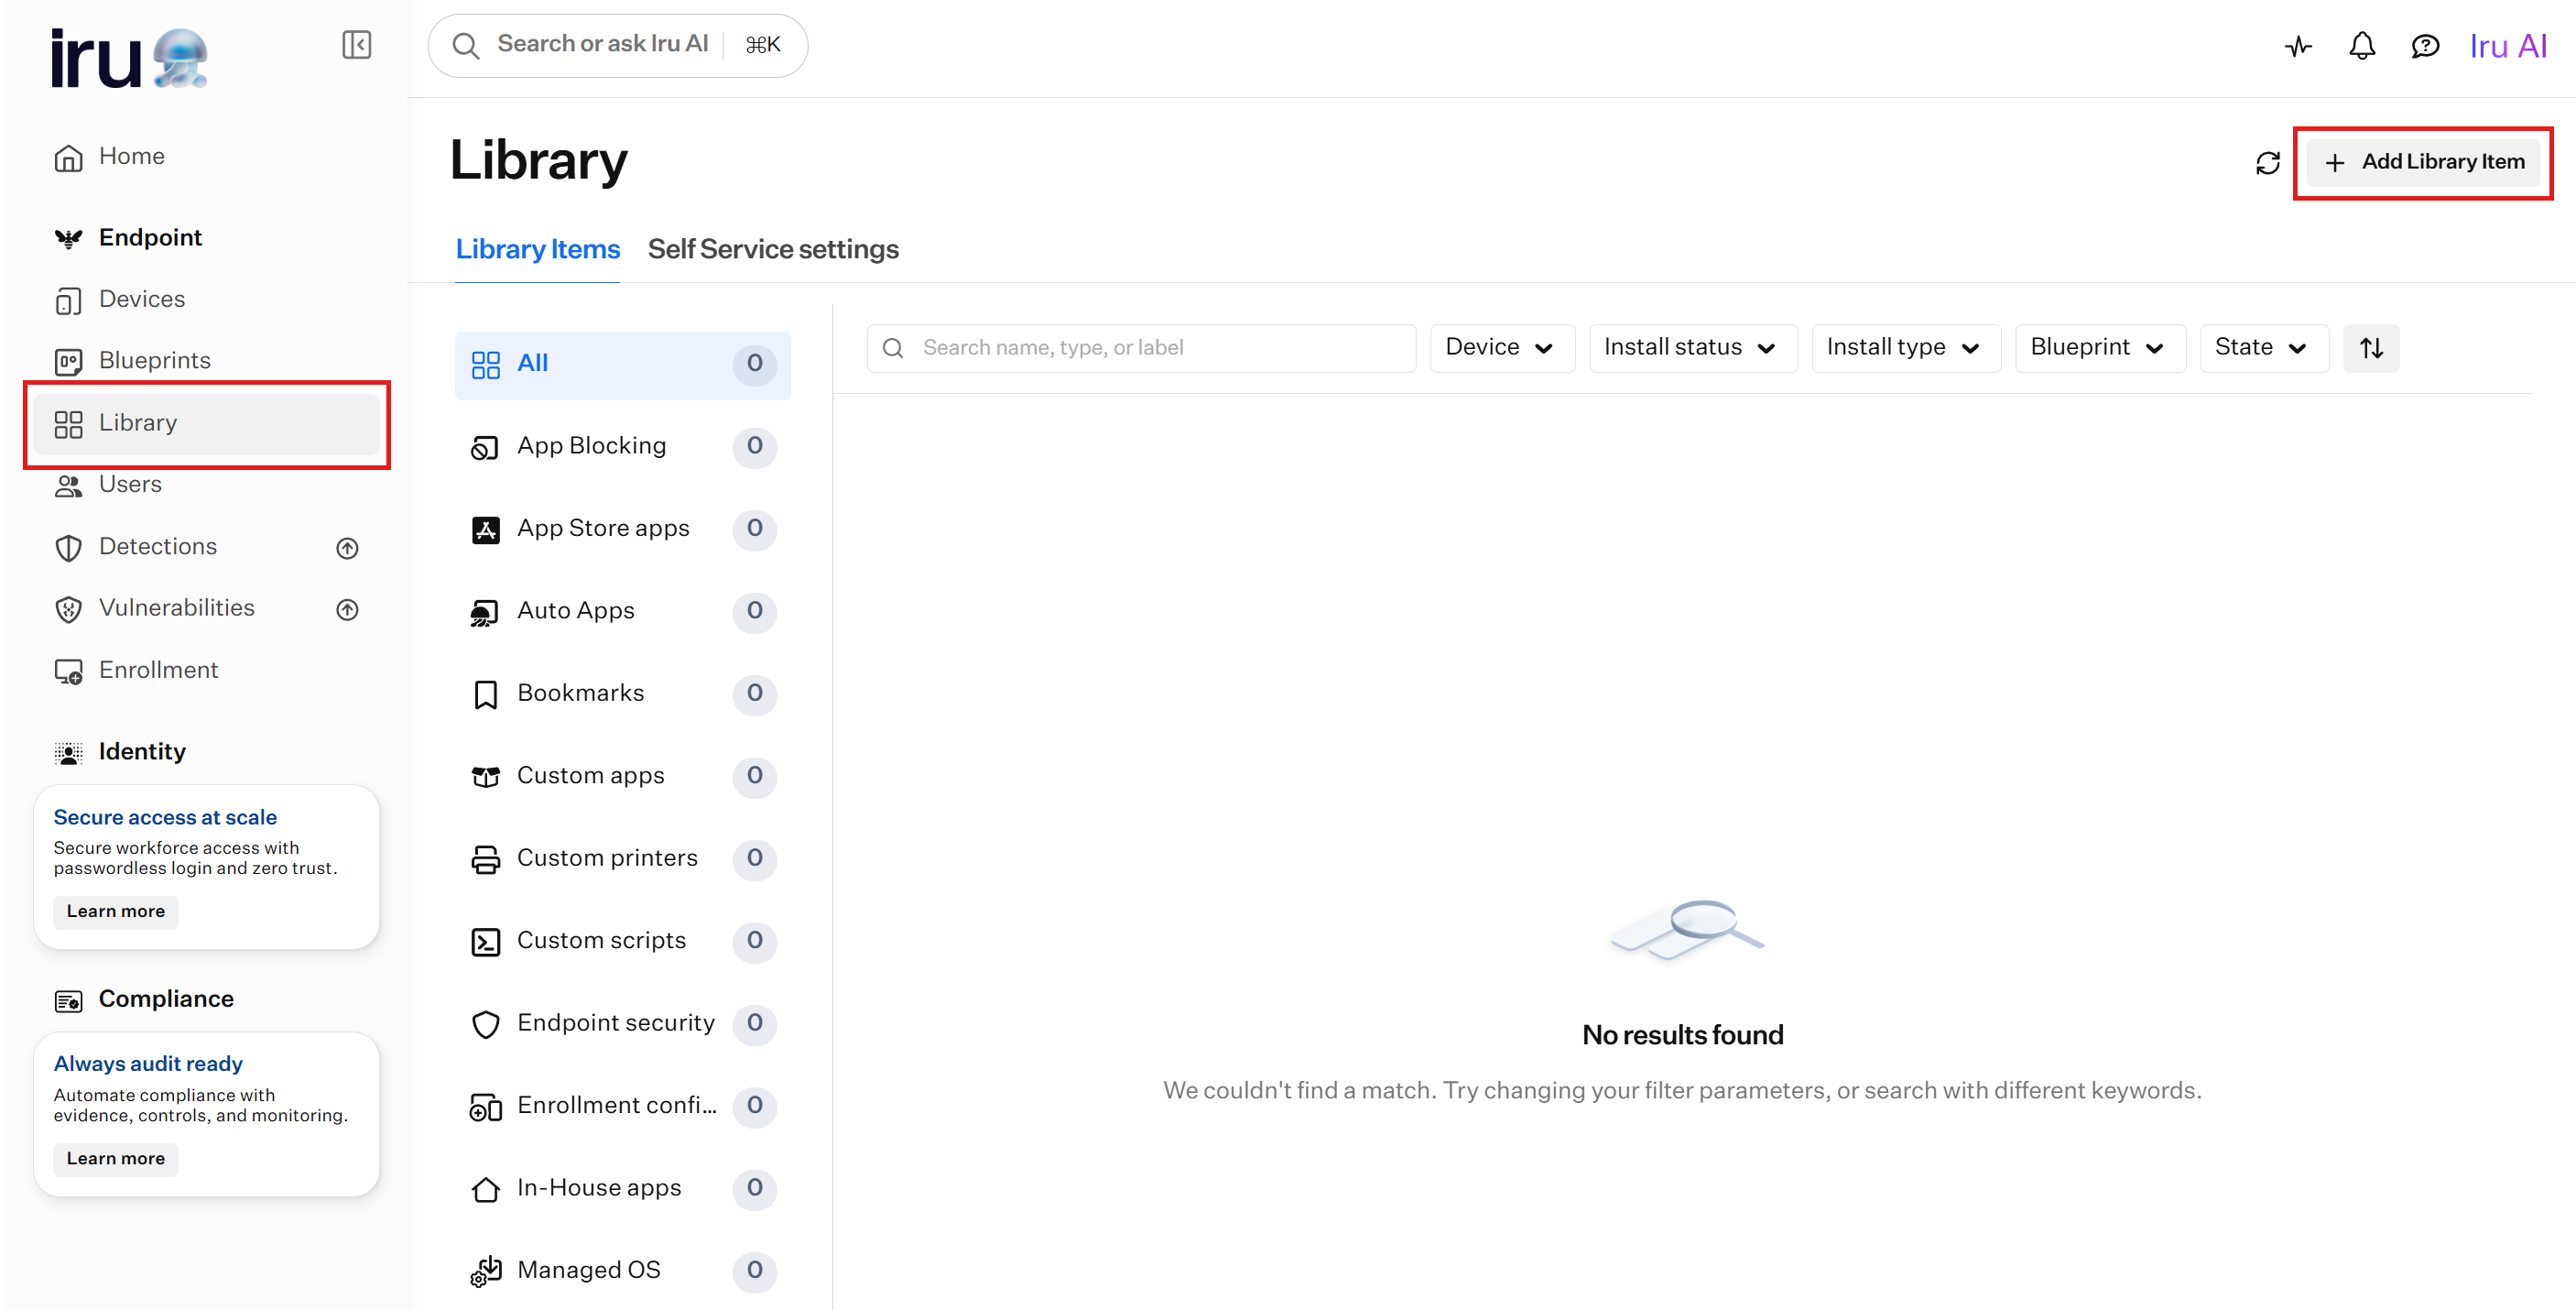
-
Search for
Certificate, select the Certificate profile, and click Add and configure.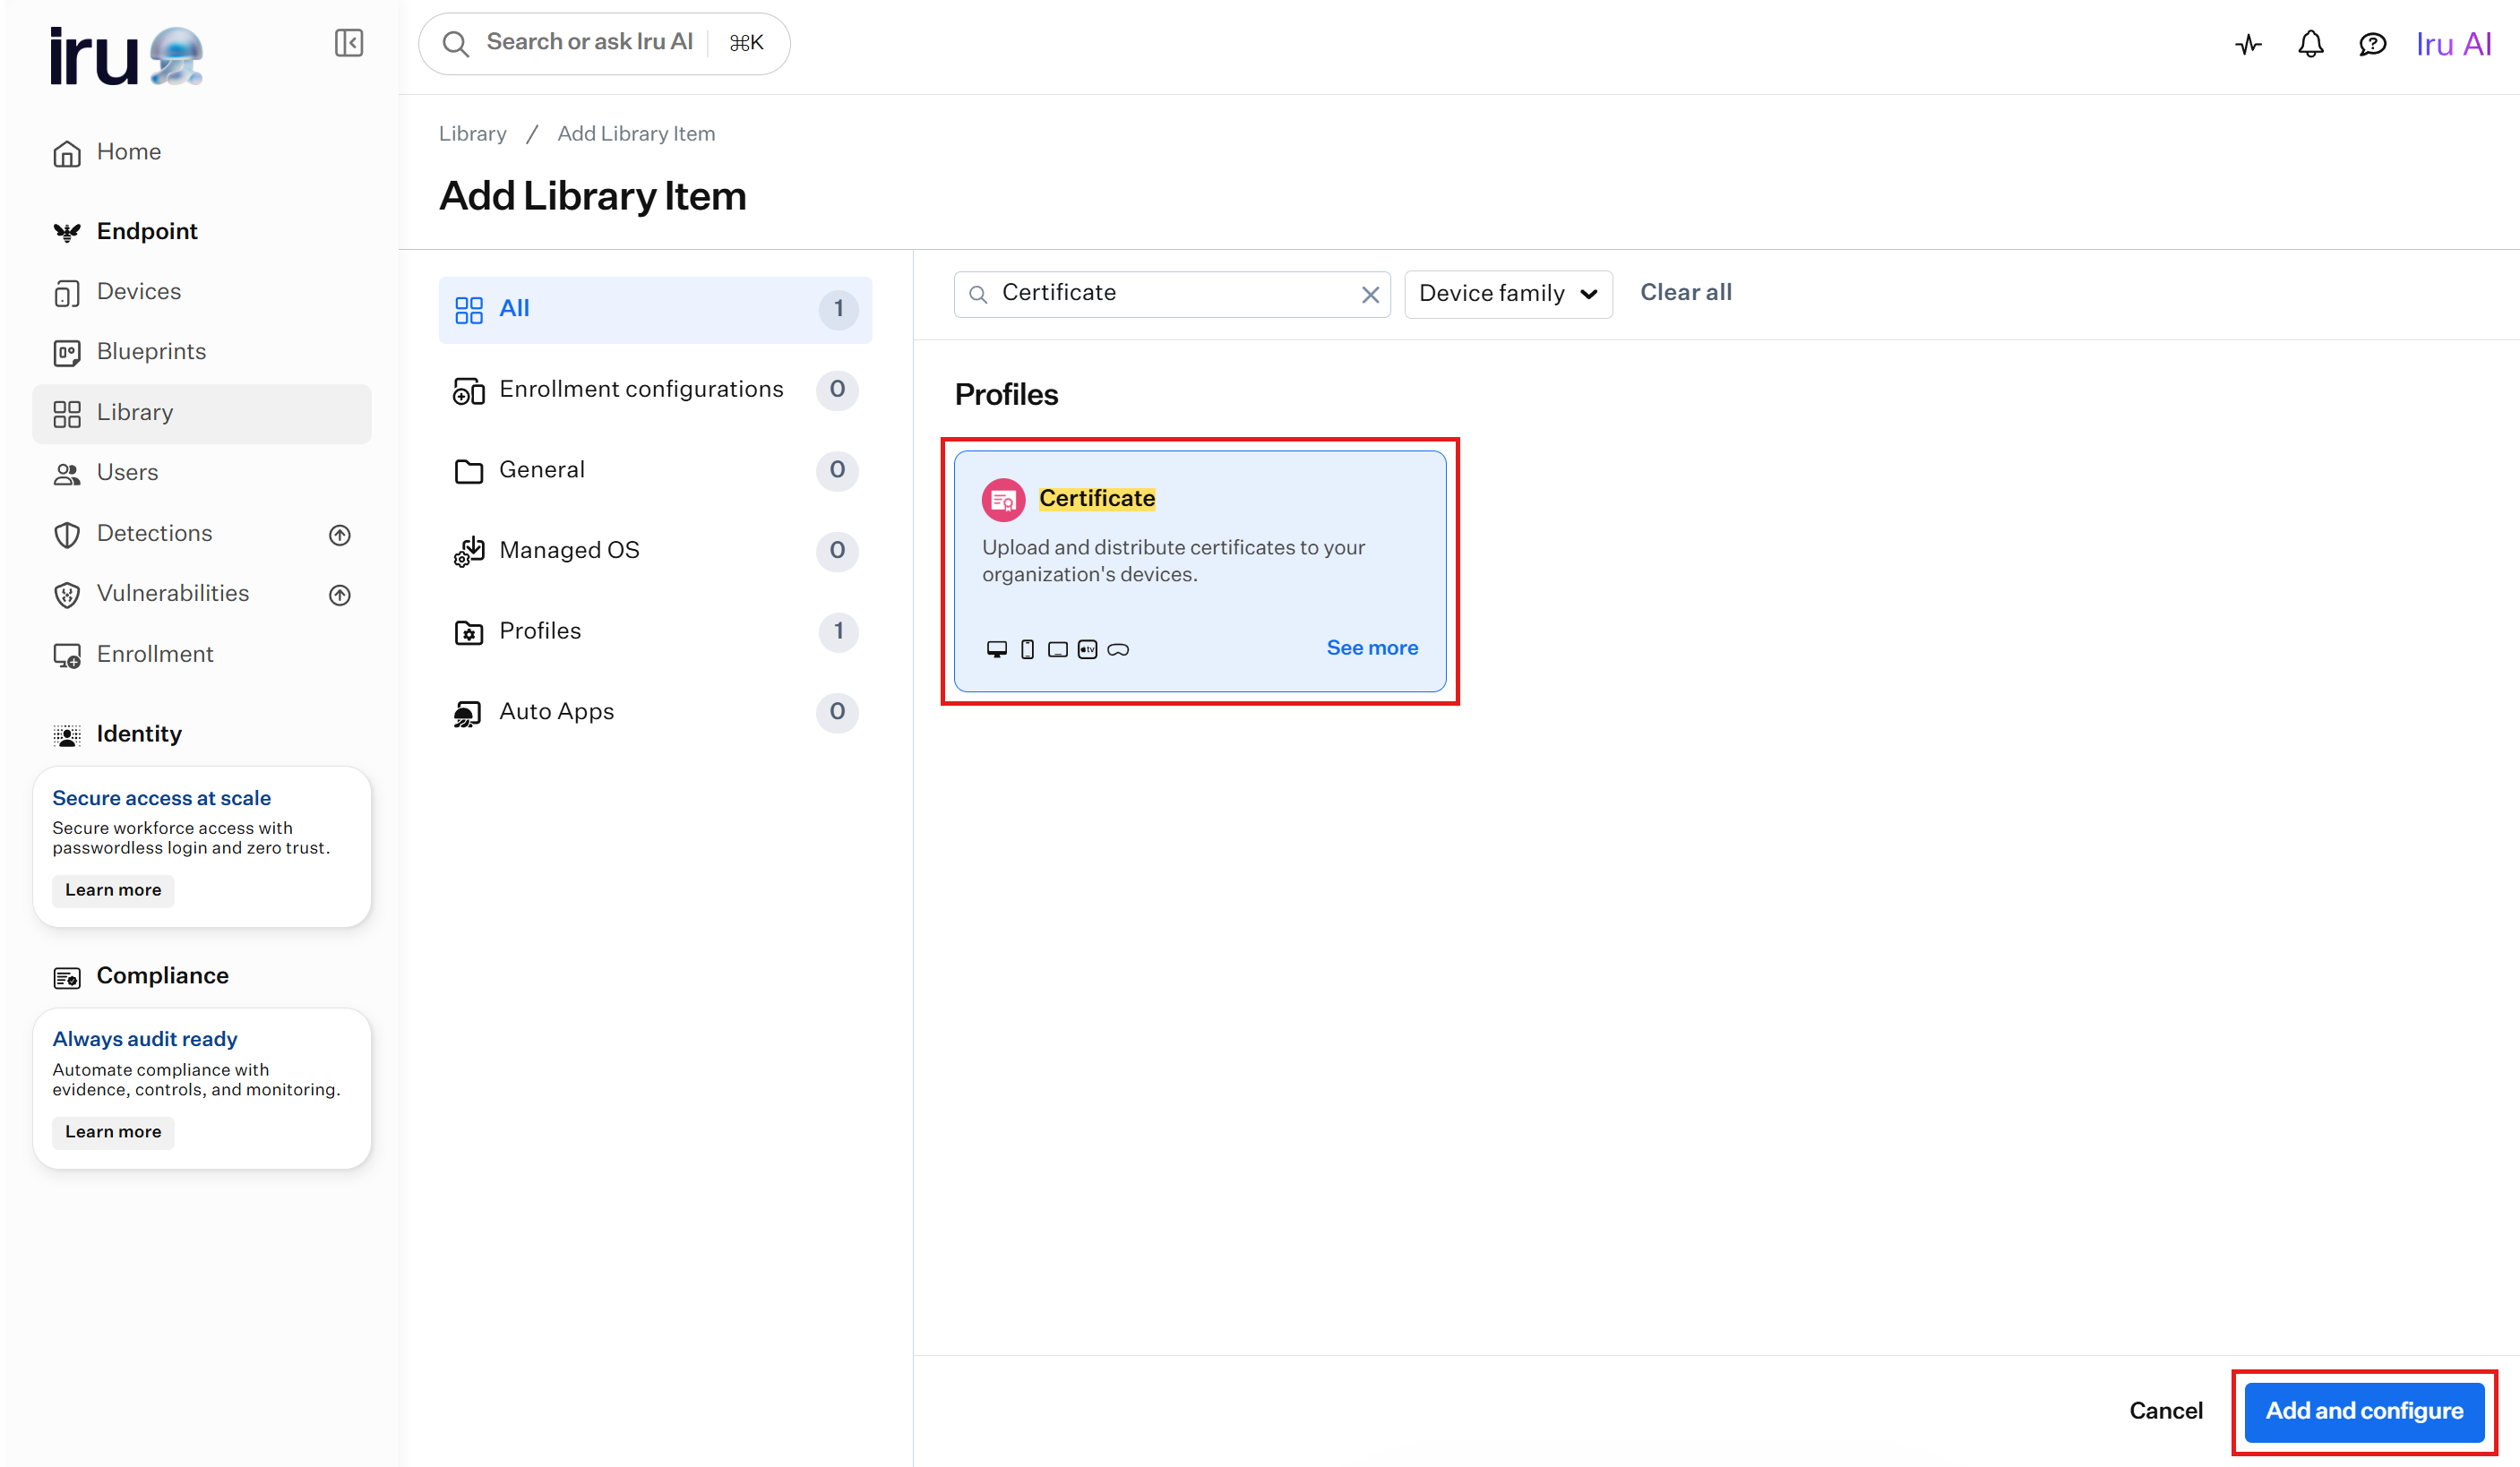
-
Enter a title for the Library Item, such as
Keytos Shield Root CA. -
For Certificate type, select PKCS #1-formatted certificate.
-
Under Certificate, upload the
rootca.cerfile you downloaded from Keytos Shield.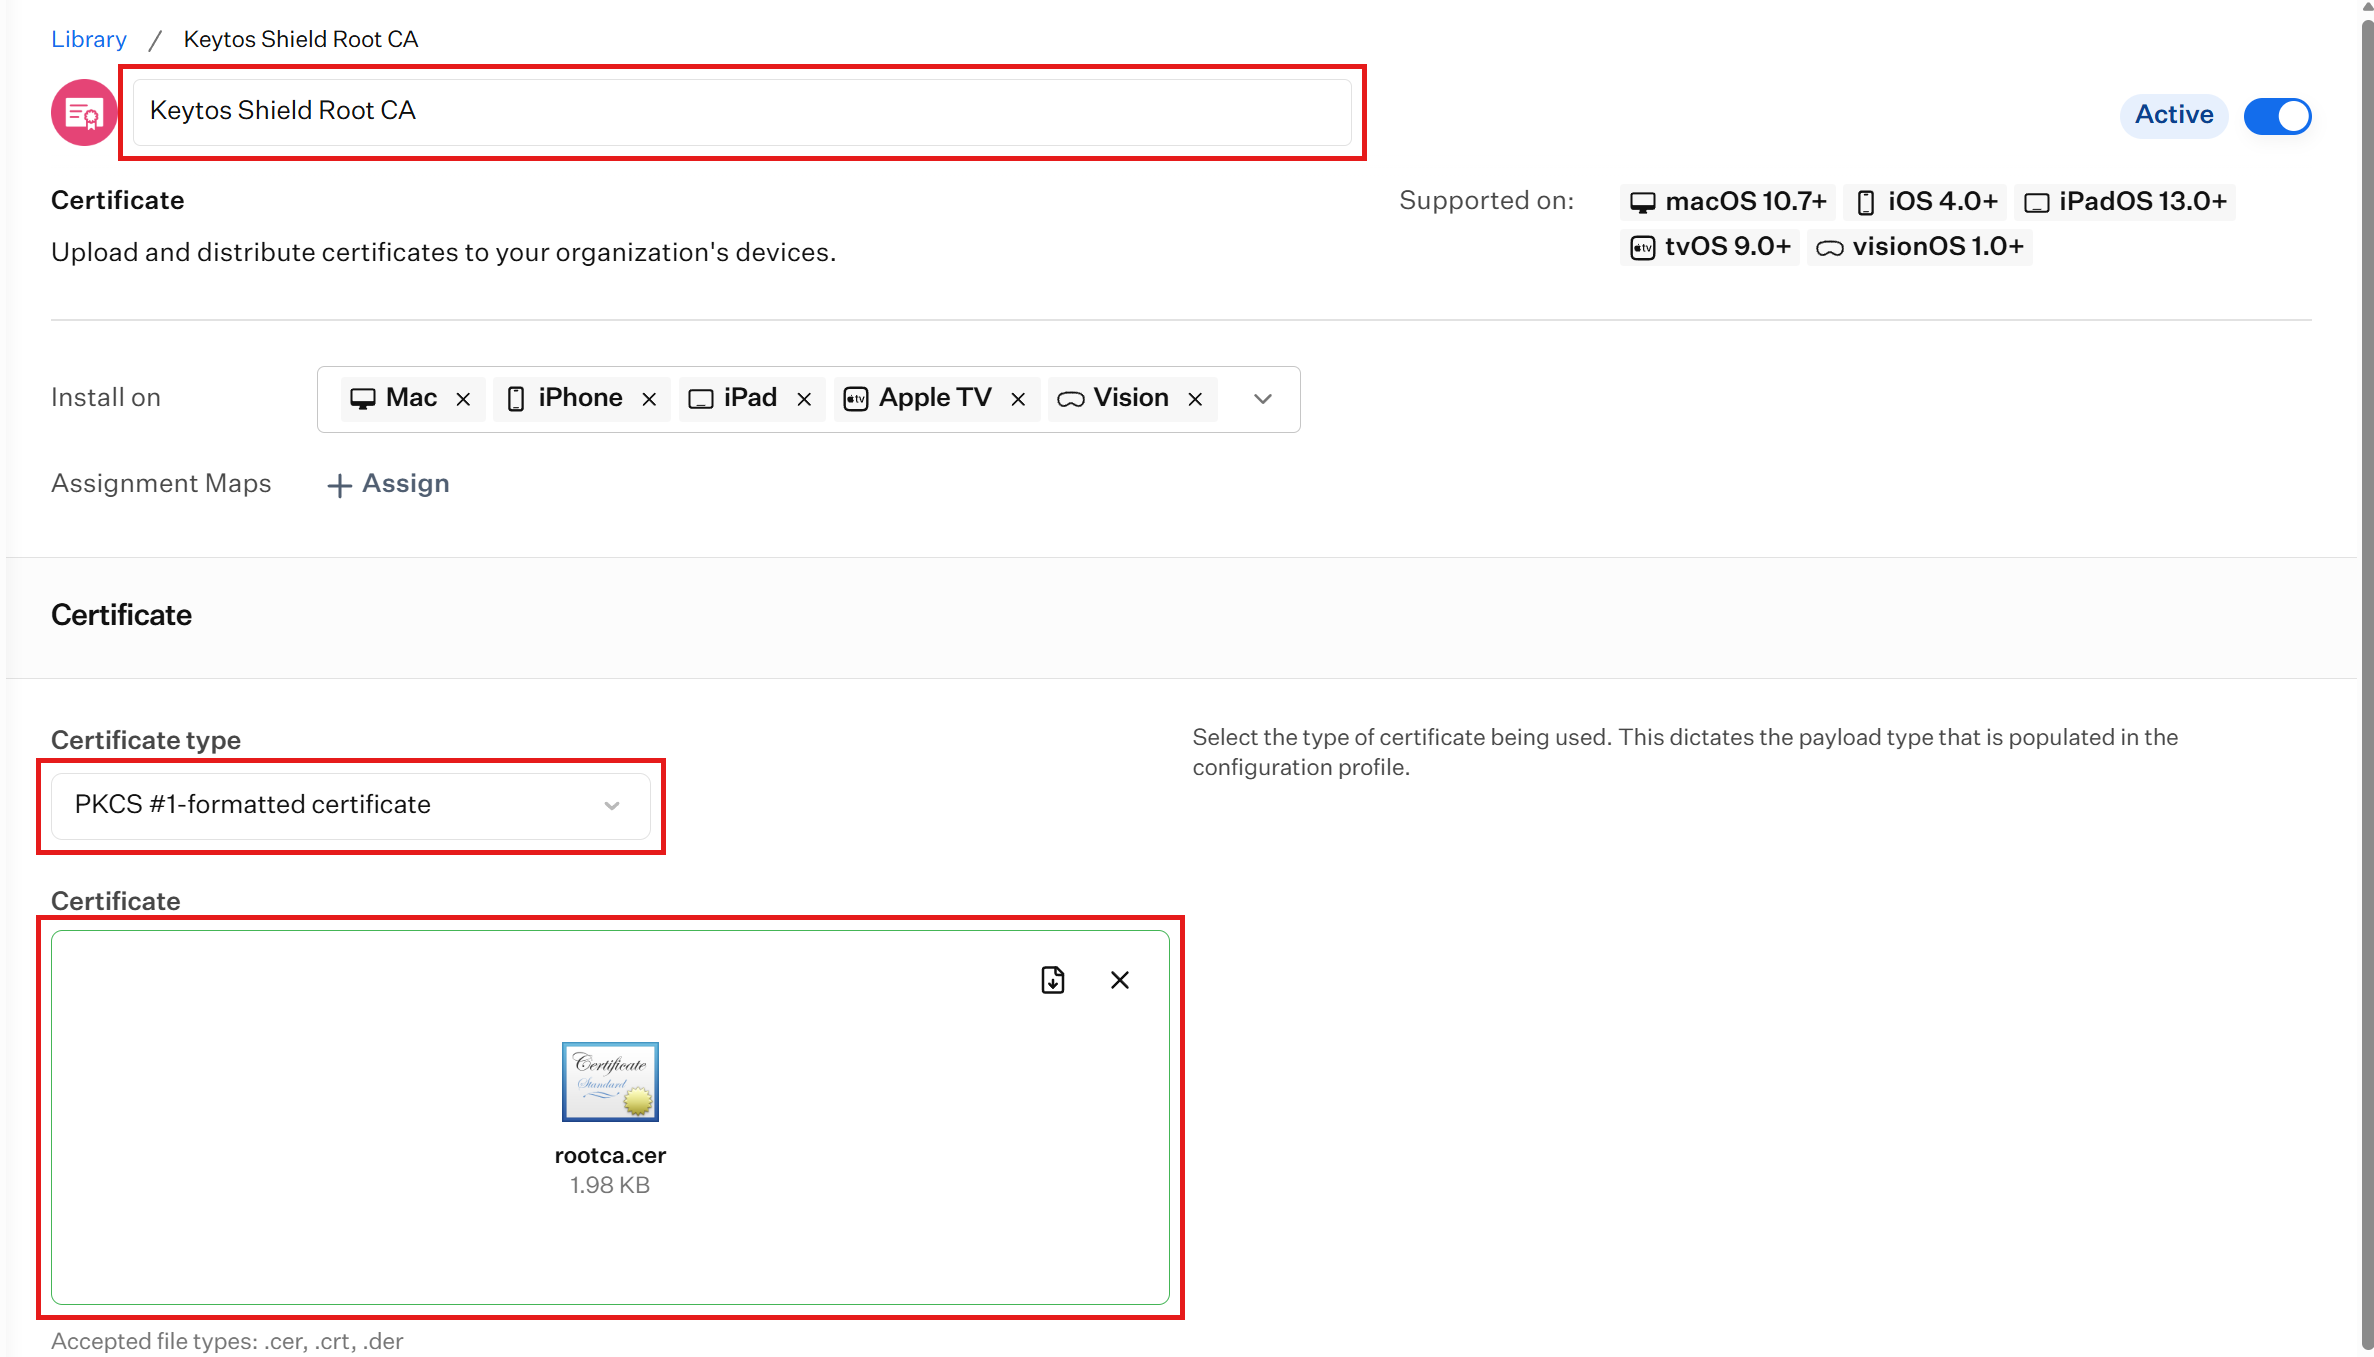
-
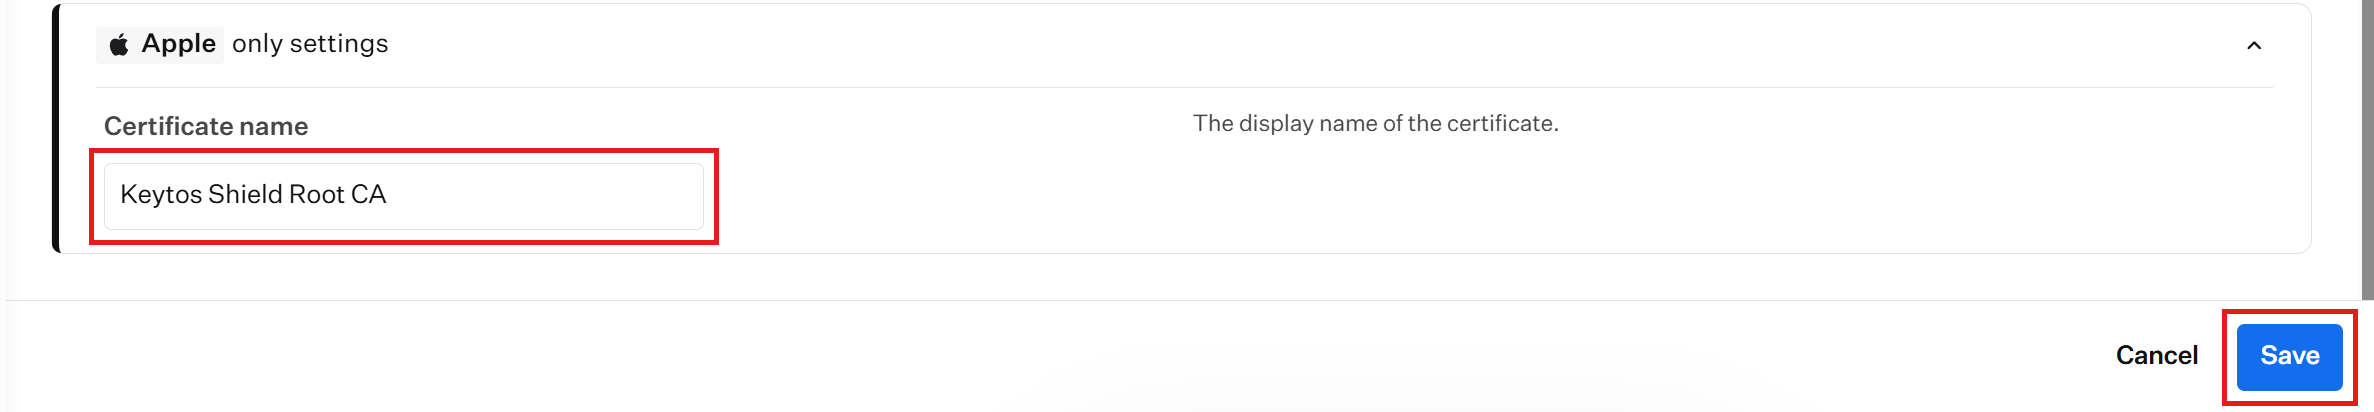
Under Apple only settings, enter a Certificate name, such as
Keytos Shield Root CA. -
Click Save.
Step 4 - How to Get Your Keytos Shield Static SCEP URL and Password
Iru uses your Shield static SCEP URL and password to request a certificate for each device, so you will paste both values into the Wi-Fi profile.
You can copy your static SCEP URL and password from the onboarding guide or from the network profiles page. Keep them handy for the next steps.
If you’re currently going through the onboarding guide, you can copy your static SCEP URL and password in step 6, Set Up Mobile Device Management (MDM).
-
In step 6 of the Keytos Shield onboarding guide, expand Other MDM.
-
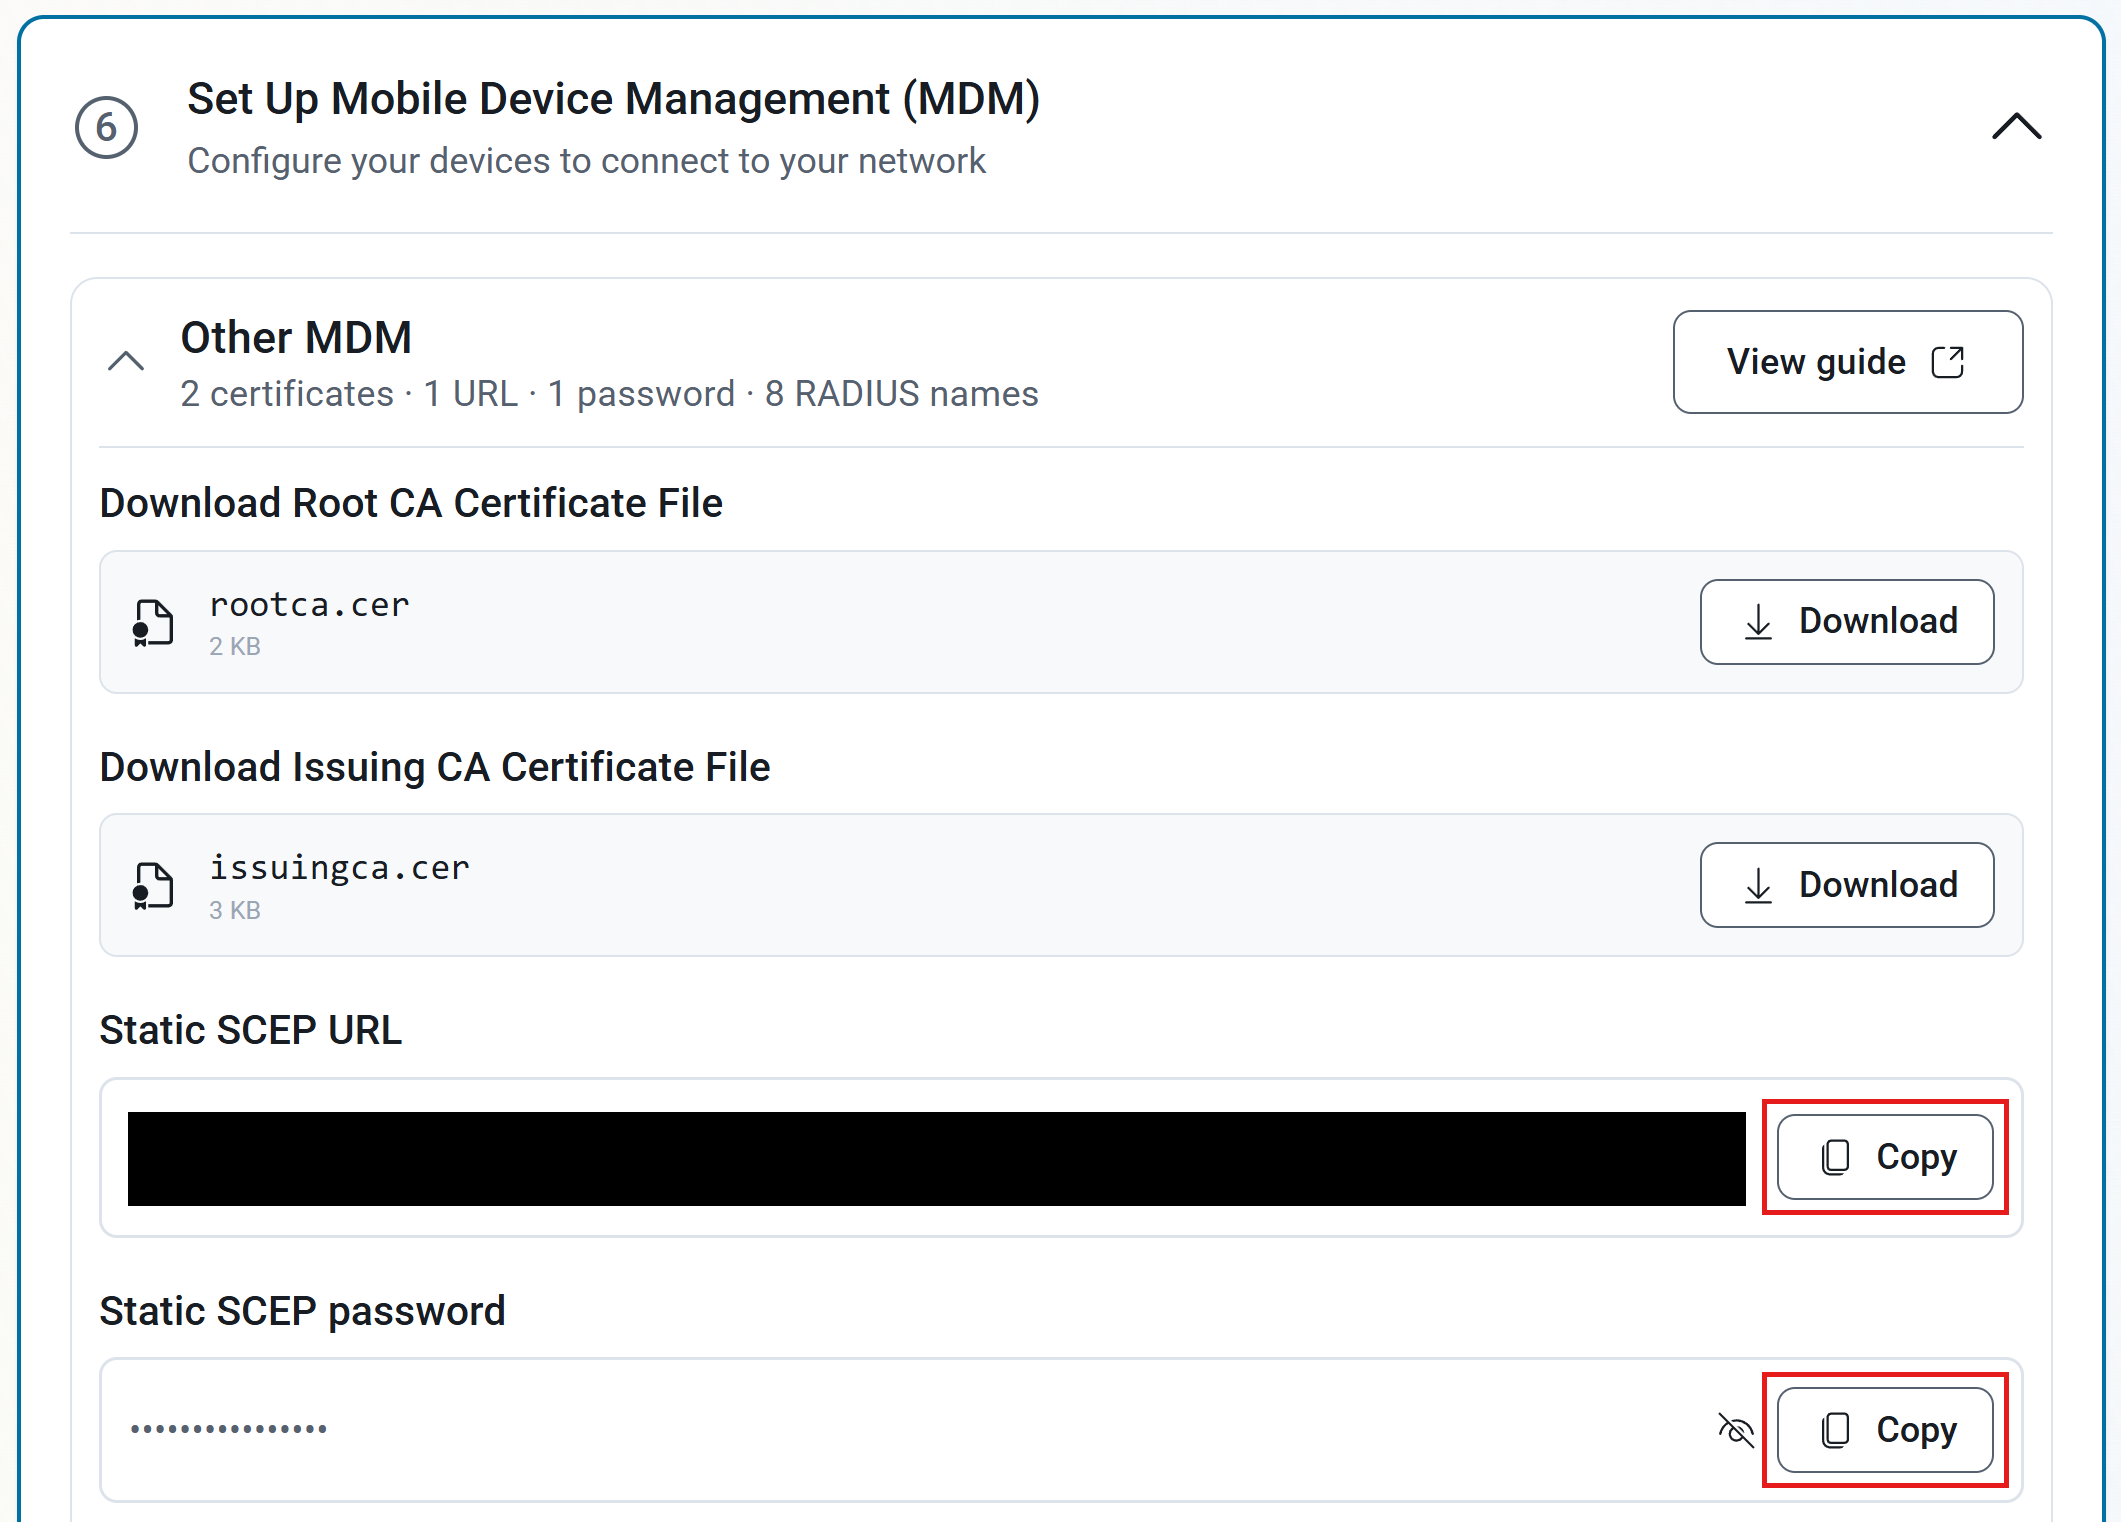
Click the Copy button next to the Static SCEP URL.
-
Click the Copy button next to the Static SCEP password to copy the password without displaying it.
If you’ve already gone through the onboarding guide, you can copy your static SCEP URL and password from the network profiles page. When you expand your MDM, select Other MDM.
-
Log in to your Keytos Shield portal.
-
From the left-hand menu, navigate to Network profiles.
-
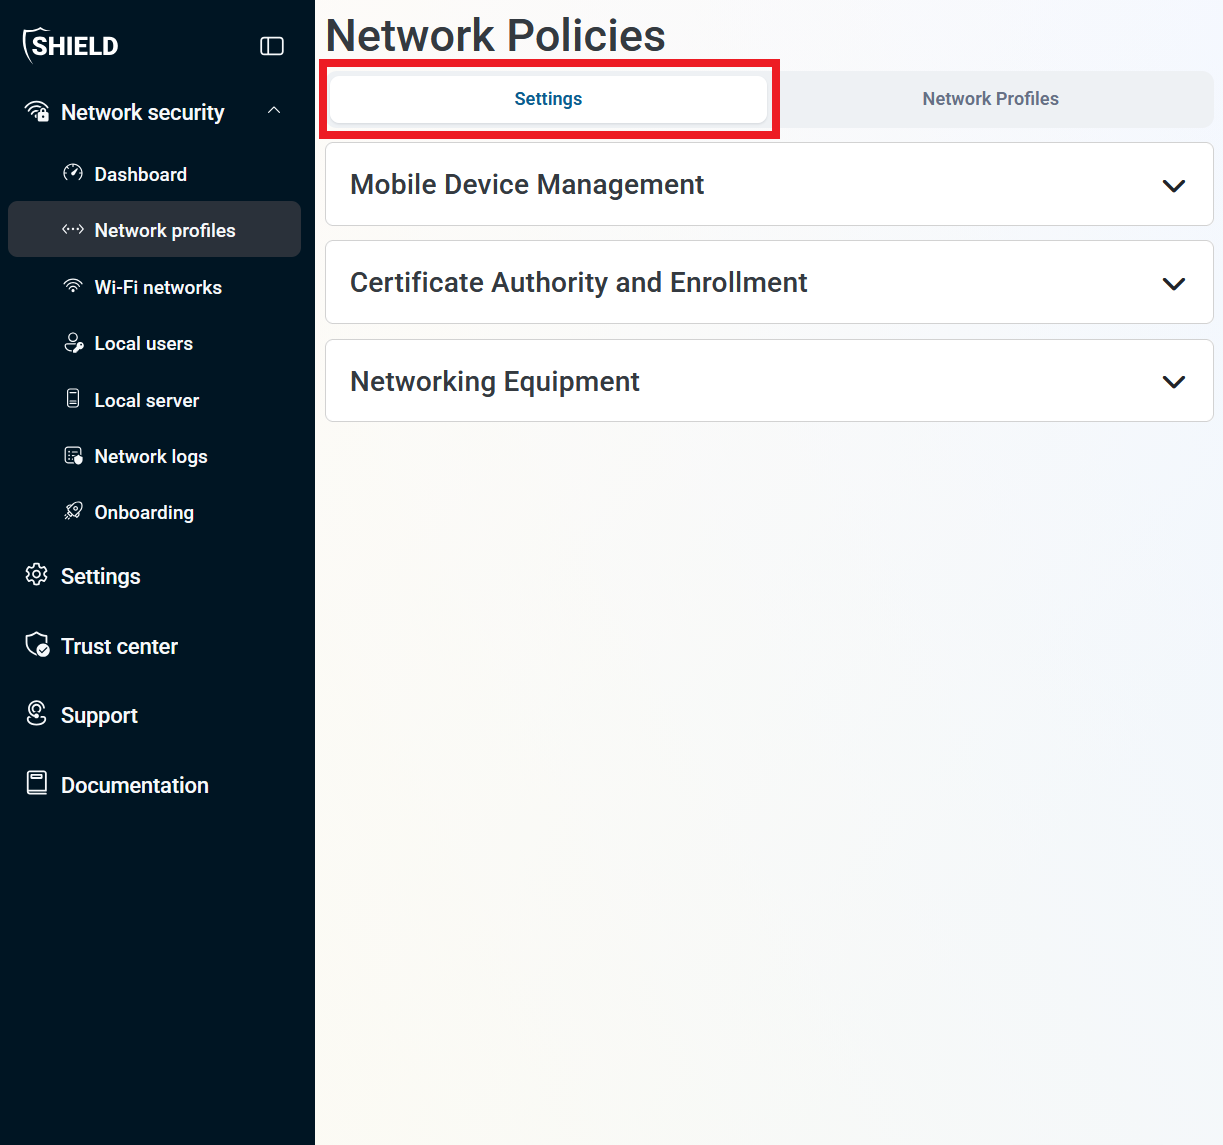
At the top of the page, select the Settings tab.
-
Expand Certificate Authority and Enrollment, and then expand your MDM, such as NinjaOne or SimpleMDM.
Not seeing your MDM? Make sure to enable it under the Mobile Device Management section further up on the page and save your changes.
-
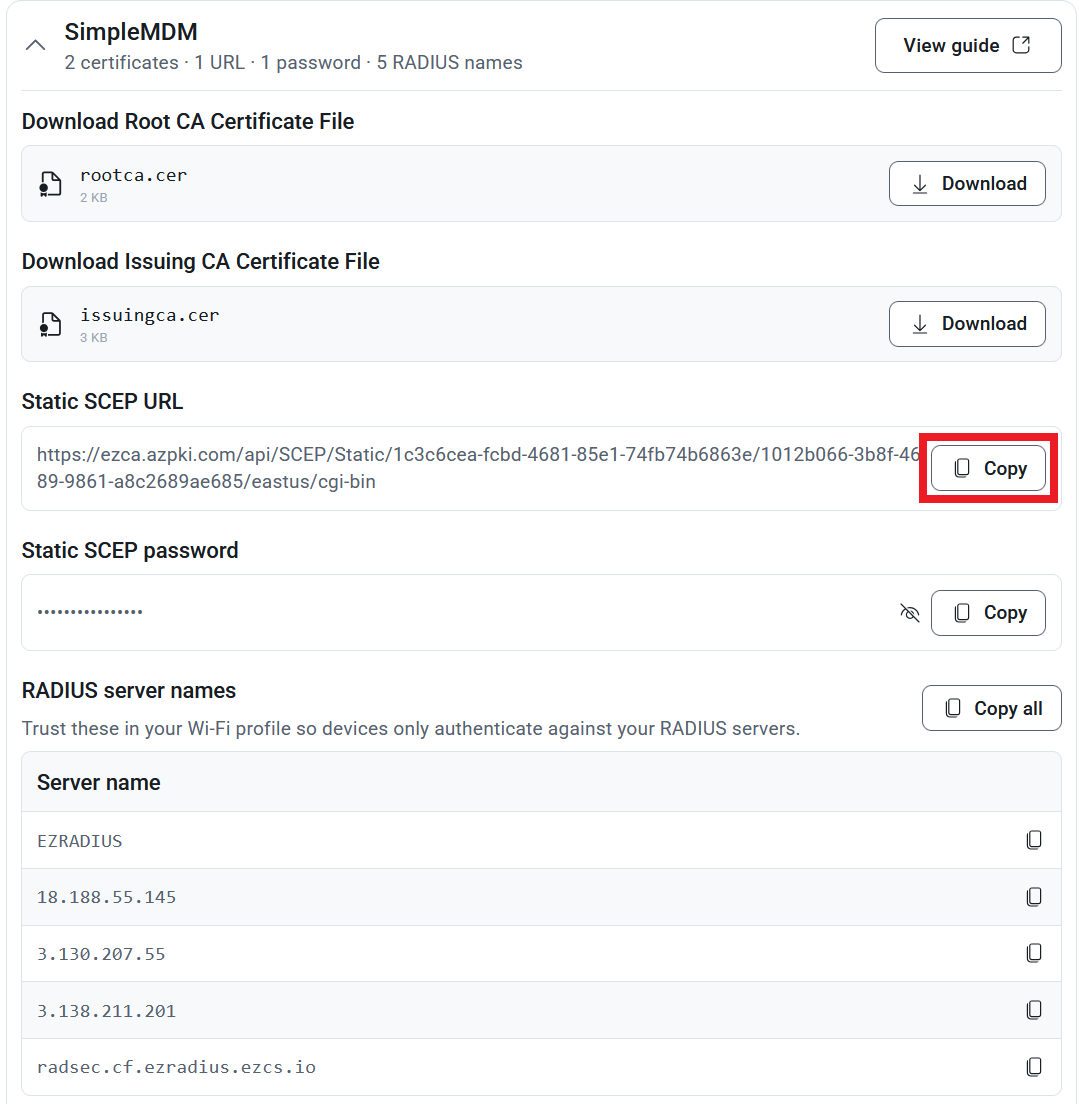
Click the Copy button next to the Static SCEP URL.
-
Click the Copy button next to the Static SCEP password to copy the password without displaying it. You will need both values when you create the SCEP profile in your MDM.
Anyone with your static SCEP URL and password can request a certificate from your Shield CA. Only paste it into your MDM, and don’t share it in email, chat, or tickets.
Step 5 - How to Get Your Keytos Shield RADIUS Server Names
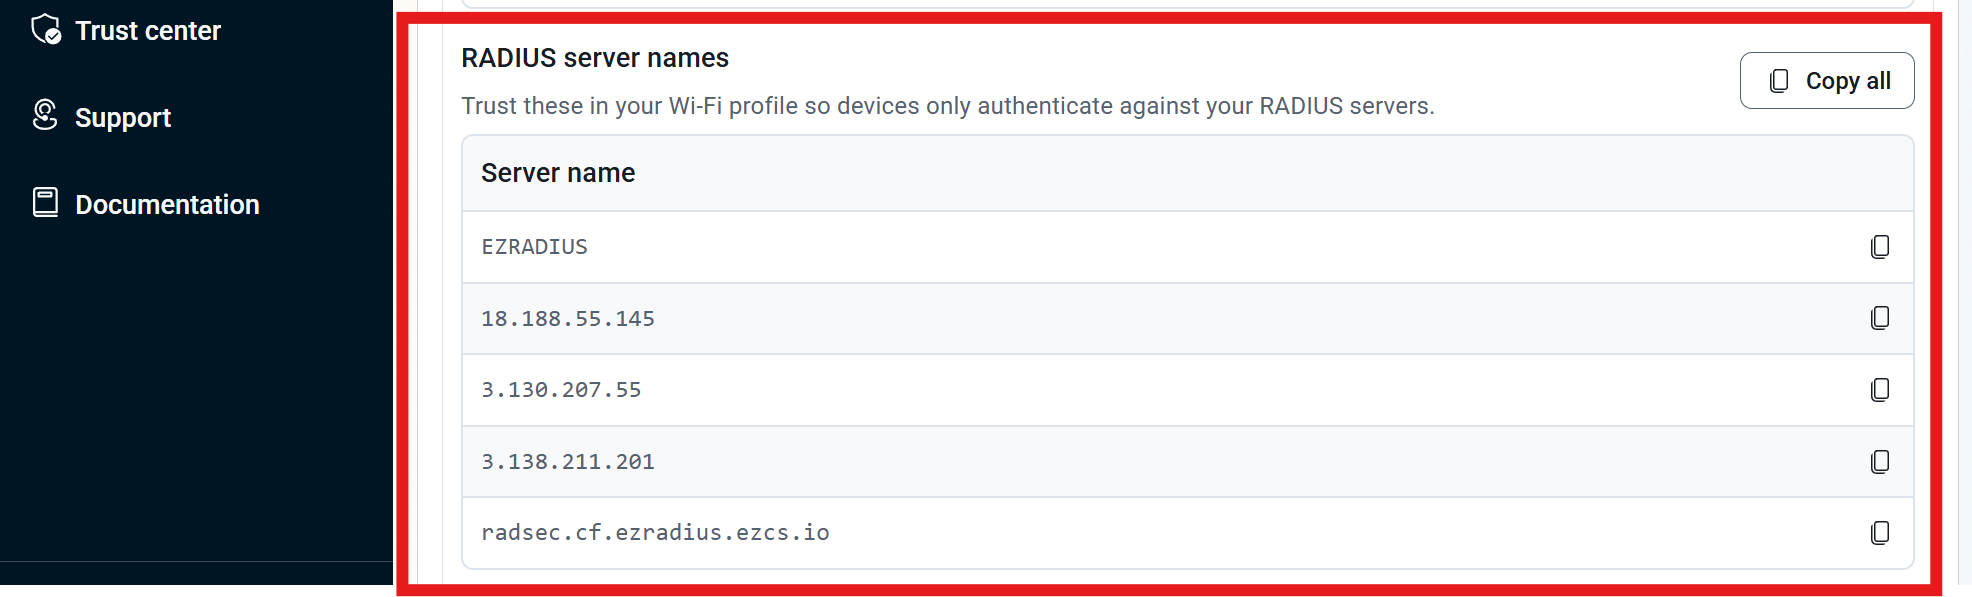
To make sure your devices only send their certificate to your Shield RADIUS servers, the Wi-Fi profile needs the list of RADIUS server names.
You can copy your RADIUS server names from the onboarding guide or from the network profiles page.
If you’re currently going through the onboarding guide, you can copy your RADIUS server names in step 6, Set Up Mobile Device Management (MDM).
-
In step 6 of the Keytos Shield onboarding guide, expand Other MDM.
-
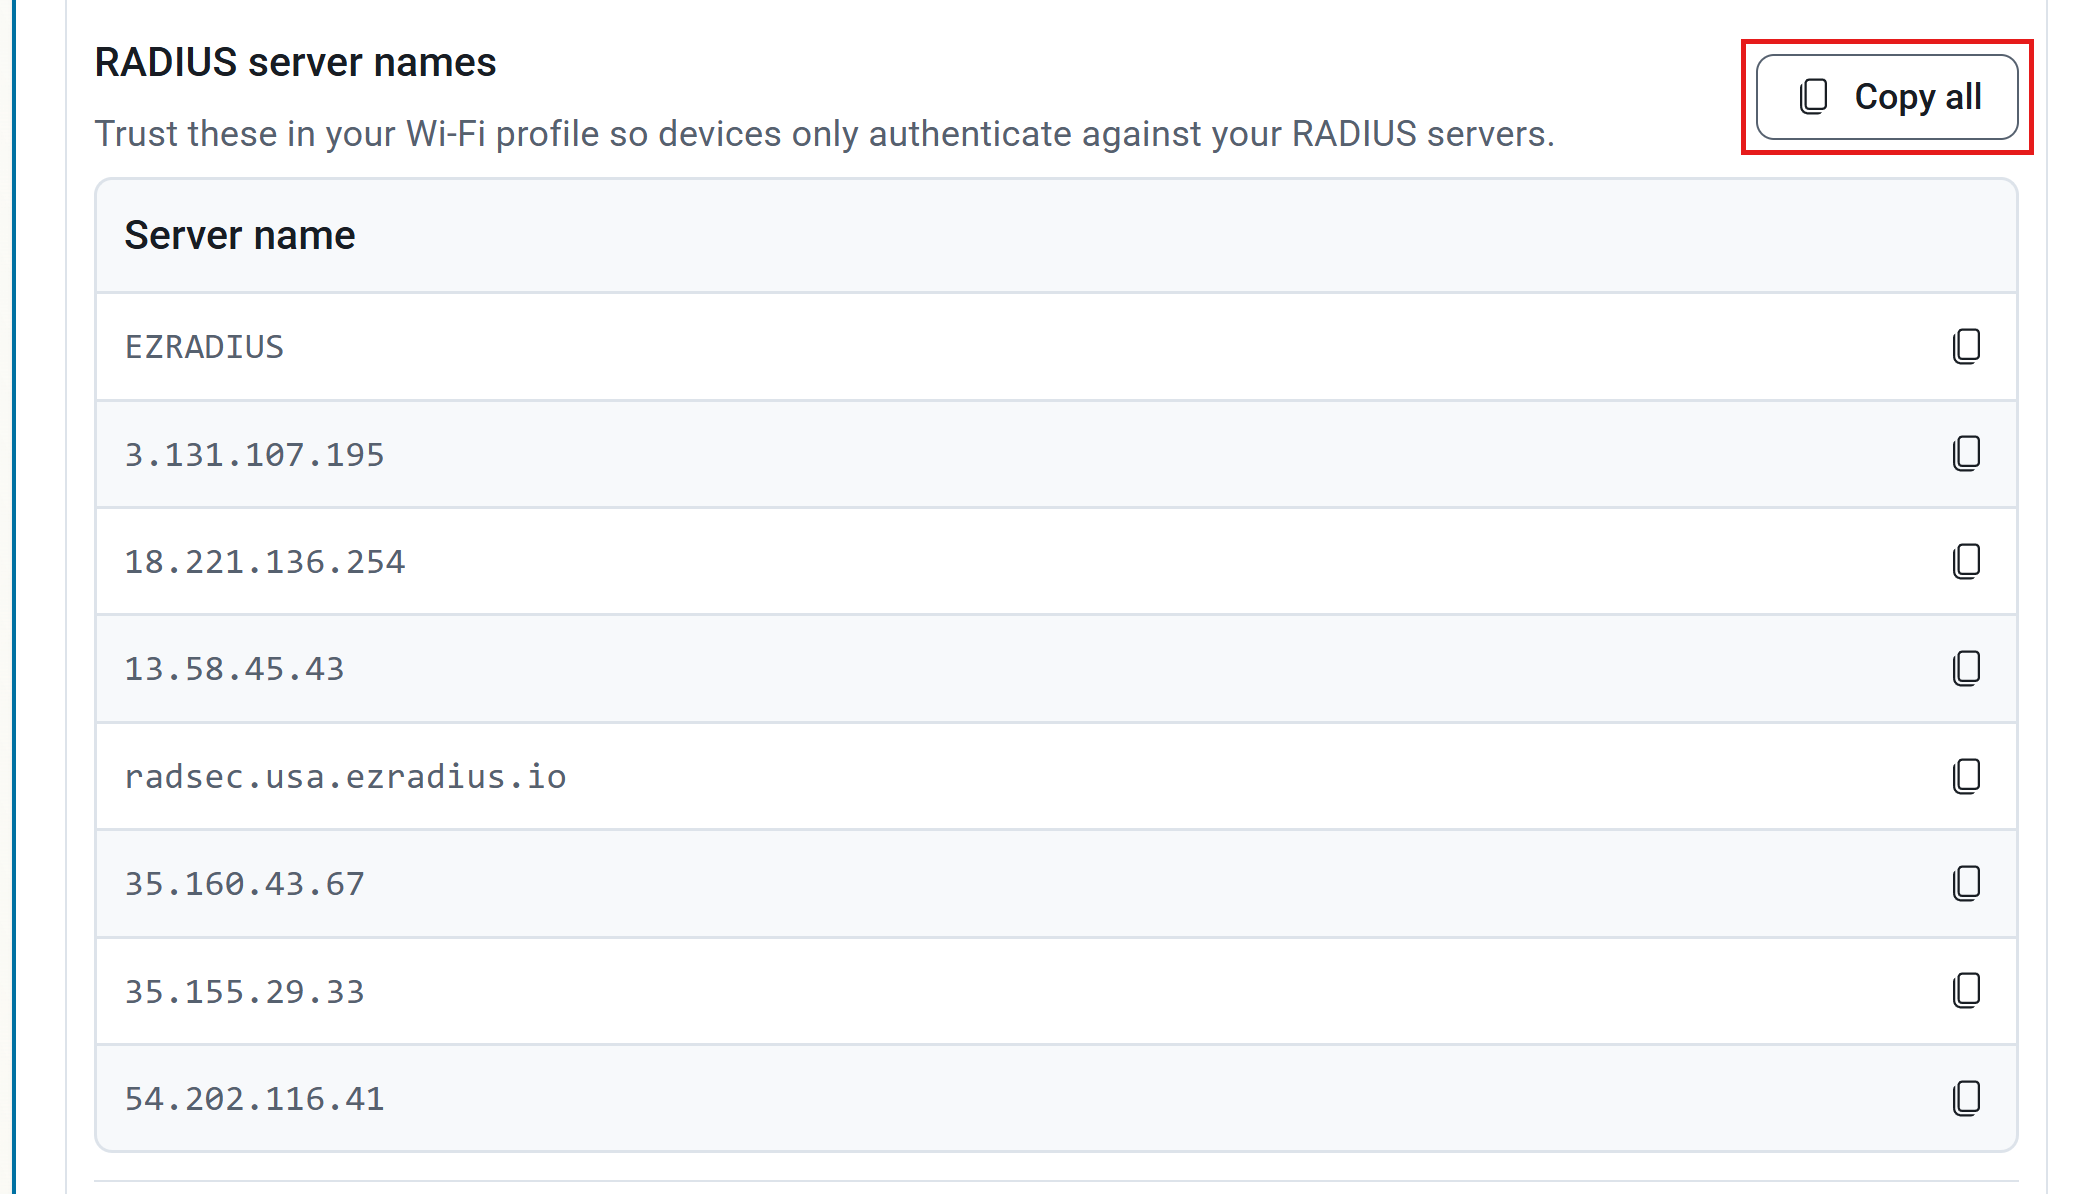
Scroll down to RADIUS server names and click Copy all to copy the full list.
If you’ve already gone through the onboarding guide, you can copy your RADIUS server names from the network profiles page. When you expand your MDM’s section, select Other MDM.
-
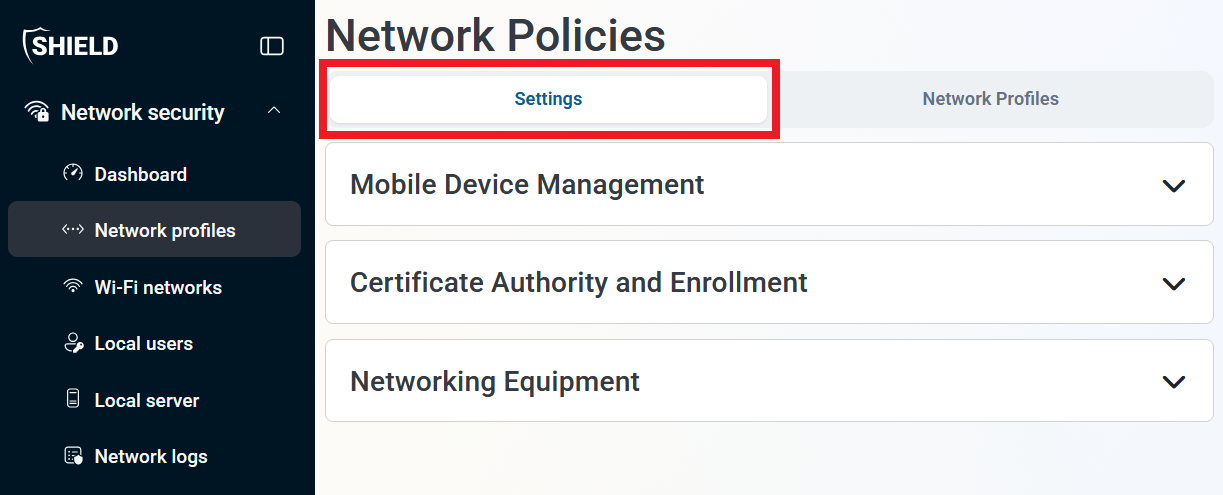
From within Network profiles > Settings in the Keytos Shield portal, expand Certificate Authority and Enrollment.
-
Expand your MDM’s section to view the available configuration options.
-
You will see a list of RADIUS server names for your network profile. You will need these in the next section.
Step 6 - How to Create a Wi-Fi Profile with a Keytos Shield SCEP Certificate in Iru
Next, create the Wi-Fi Library Item. It tells your devices which network to join, requests a unique certificate from Keytos Shield with SCEP, and uses that certificate to authenticate with EAP-TLS.
How to Configure the Wi-Fi Network Settings in Iru
-
In Iru, go to Library and click Add Library Item.
-
Search for
Wi-Fi, select the Wi-Fi profile, and click Add and configure. -
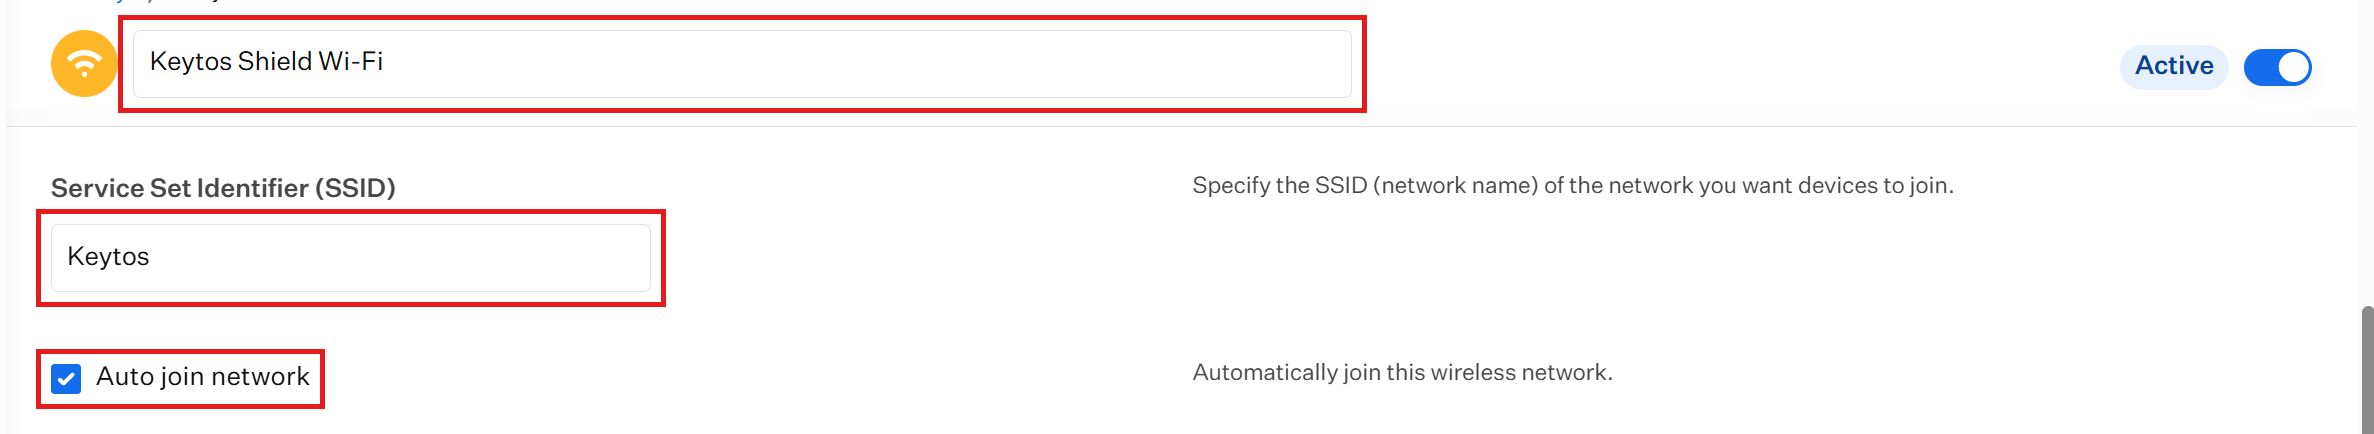
Enter a title for the Library Item, such as
Keytos Shield Wi-Fi. -
Under Service Set Identifier (SSID), enter the name of your Wi-Fi network exactly as it is broadcast. It is case-sensitive.
-
Leave Auto join network checked so devices connect on their own as soon as they are in range.
How to Configure EAP-TLS Authentication in Iru
-
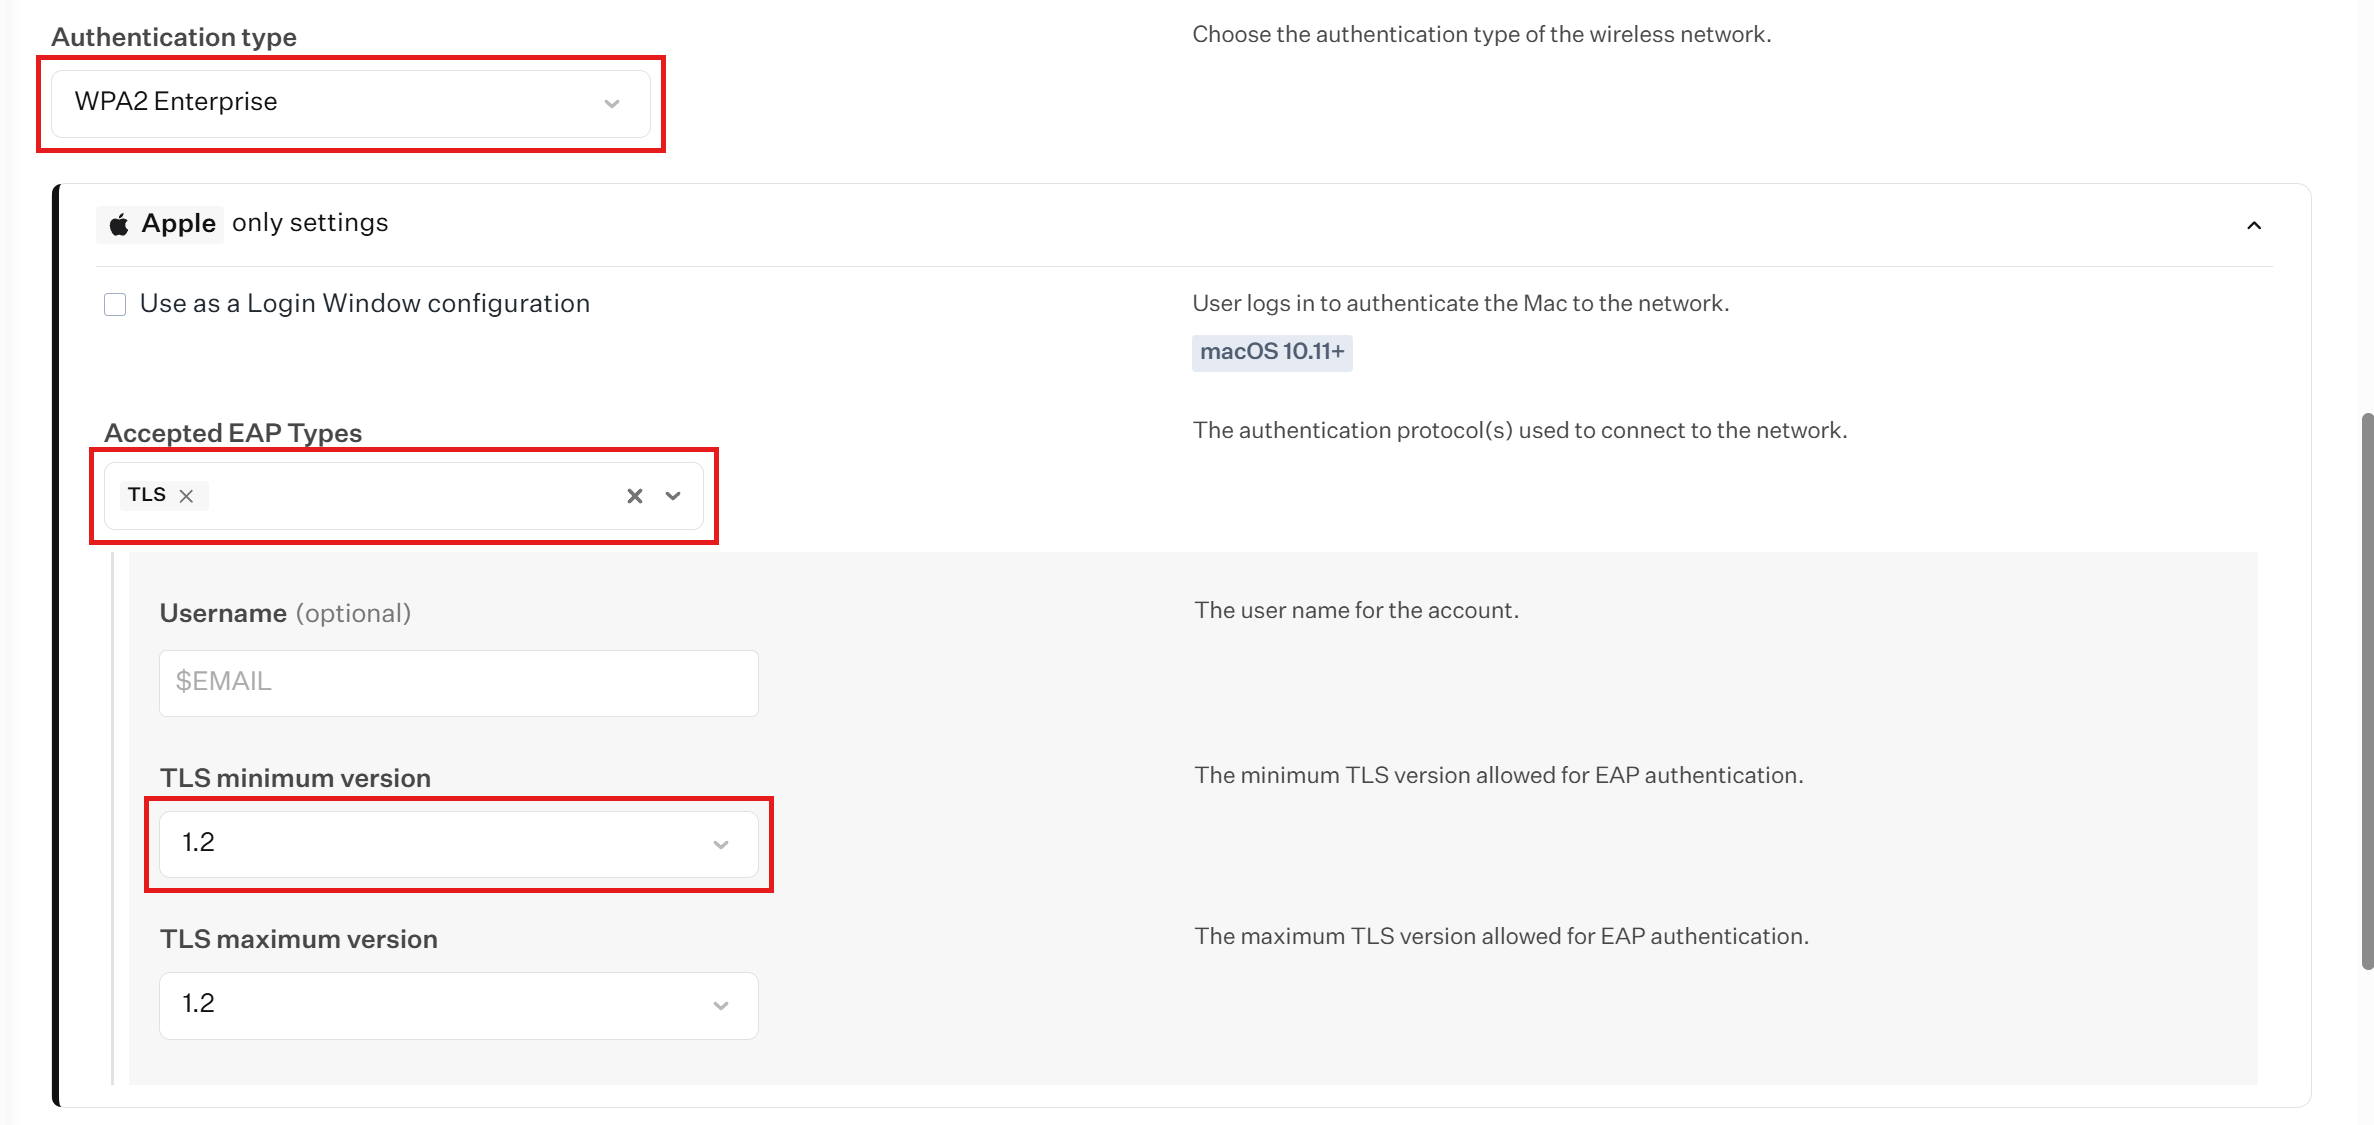
Scroll down to Authentication and set Authentication type to the enterprise security type your network uses, such as WPA2 Enterprise or WPA3 Enterprise.
-
Under Apple only settings, open Accepted EAP Types and select TLS.
-
Leave Username empty. The device identifies itself with its certificate.
-
Set TLS minimum version to 1.2. We recommend blocking older TLS versions, which are no longer considered secure.
How to Configure the Keytos Shield SCEP Certificate in Iru
-
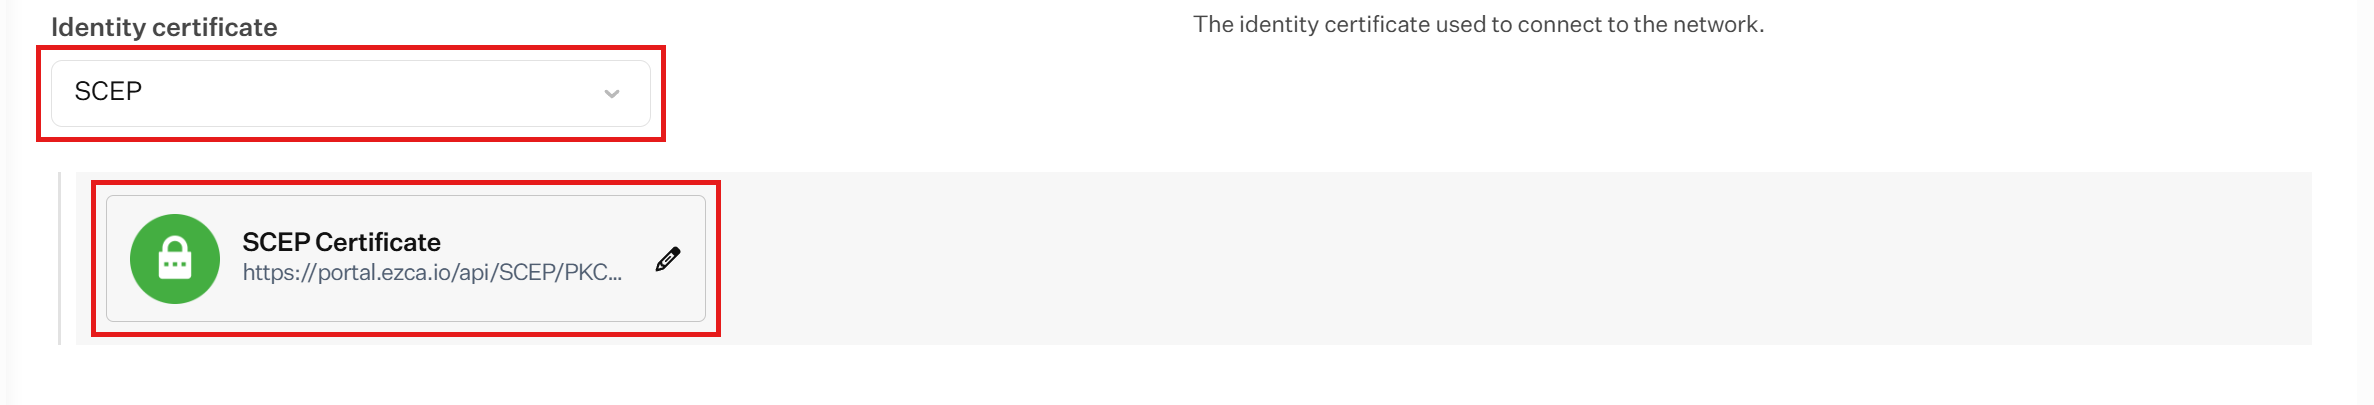
Set Identity certificate to SCEP, then click Configure SCEP Certificate to open the Configure SCEP panel.
-
In URL, paste the Static SCEP URL you copied from Keytos Shield.
-
In Challenge, paste the Static SCEP password you copied from Keytos Shield.
-
In Subject, enter a subject name that identifies the device, such as
CN=$SERIAL_NUMBER. Iru replaces the variable with each device’s serial number. Use only device variables from the Iru global variables for all device families, such as$SERIAL_NUMBERor$DEVICE_ID. Iru also appends its$PROFILE_UUIDvariable to the CN if it is missing, which it needs to renew certificates automatically.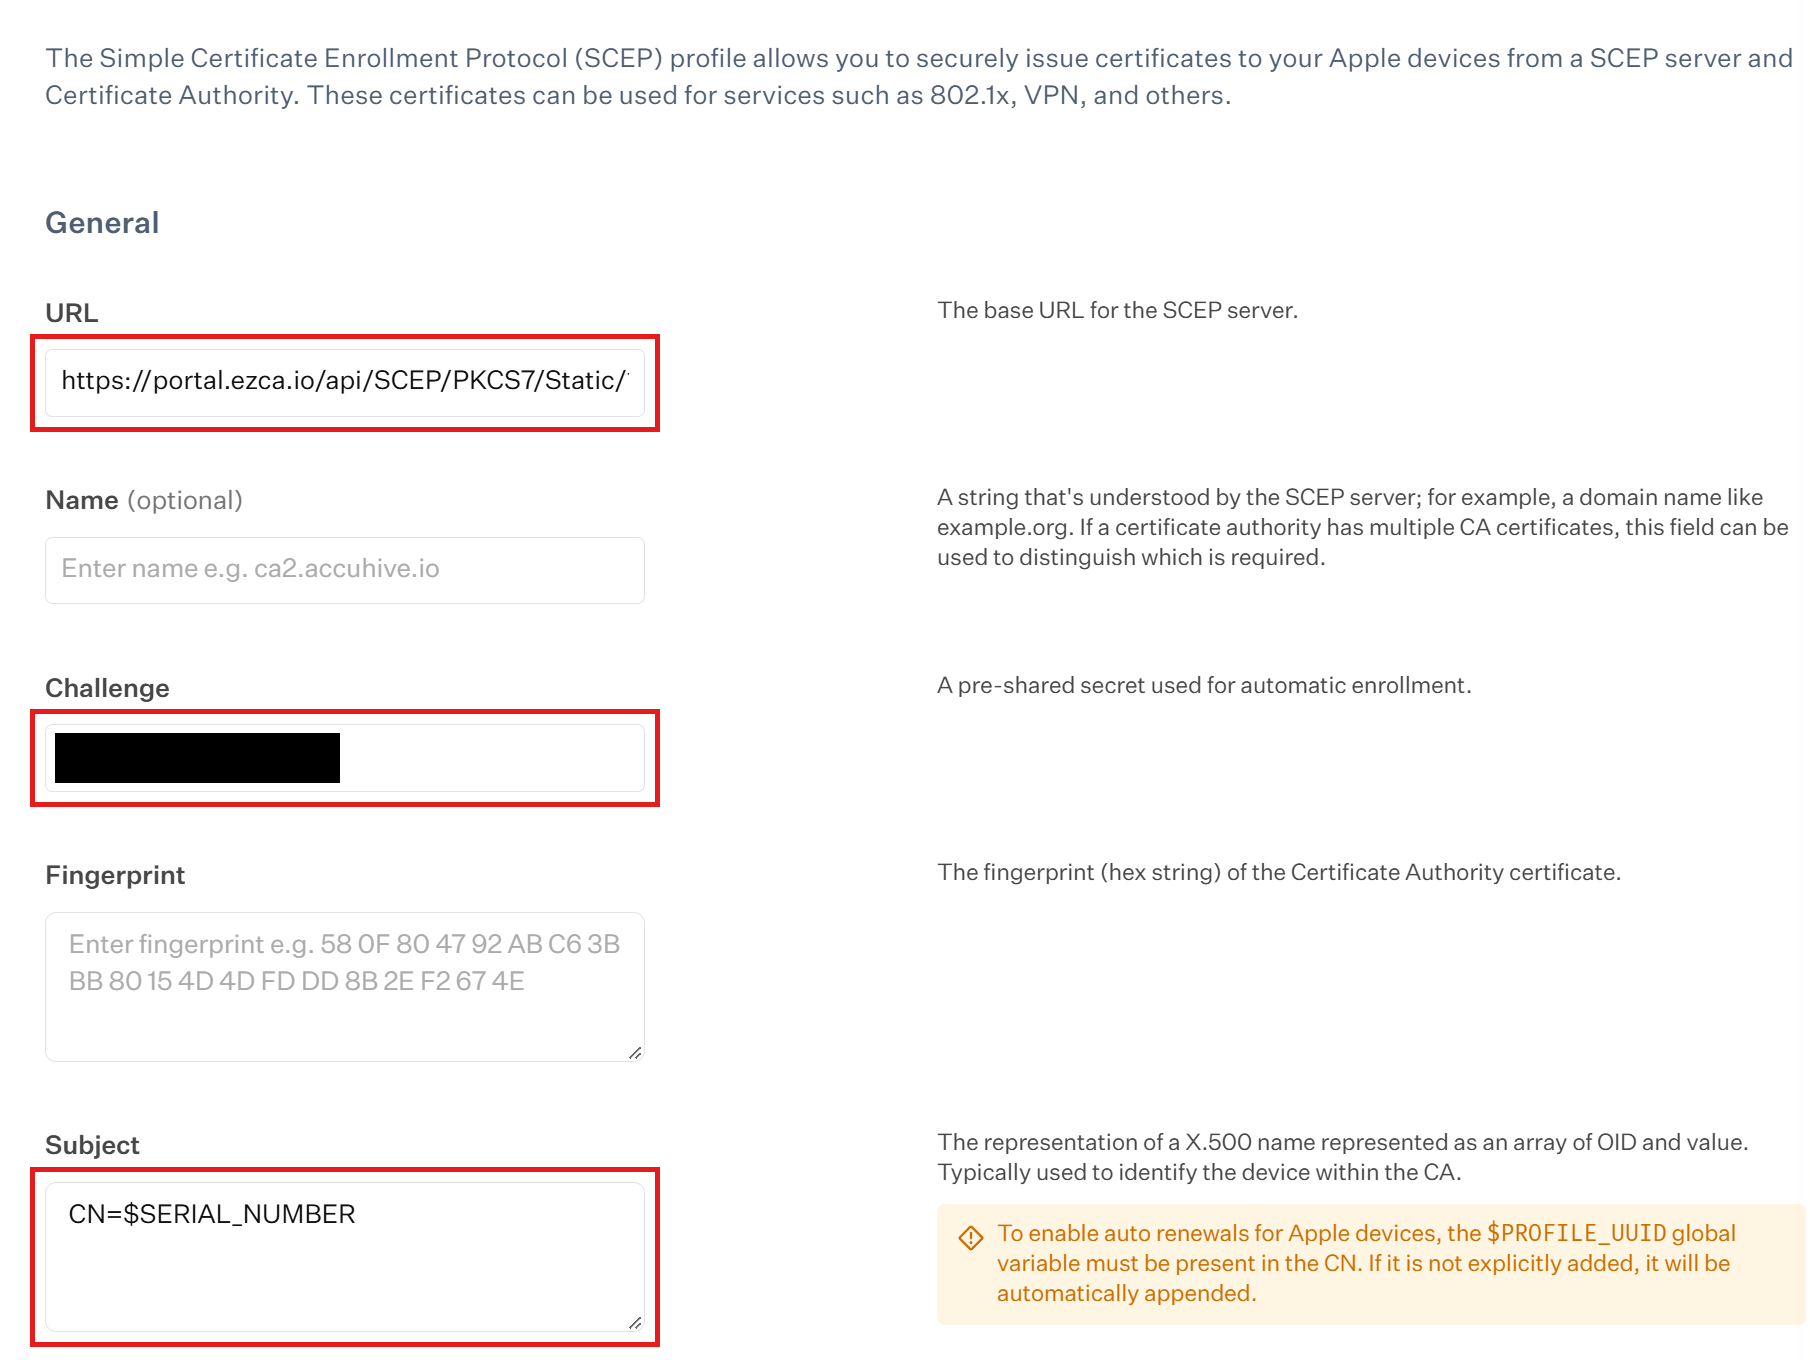
-
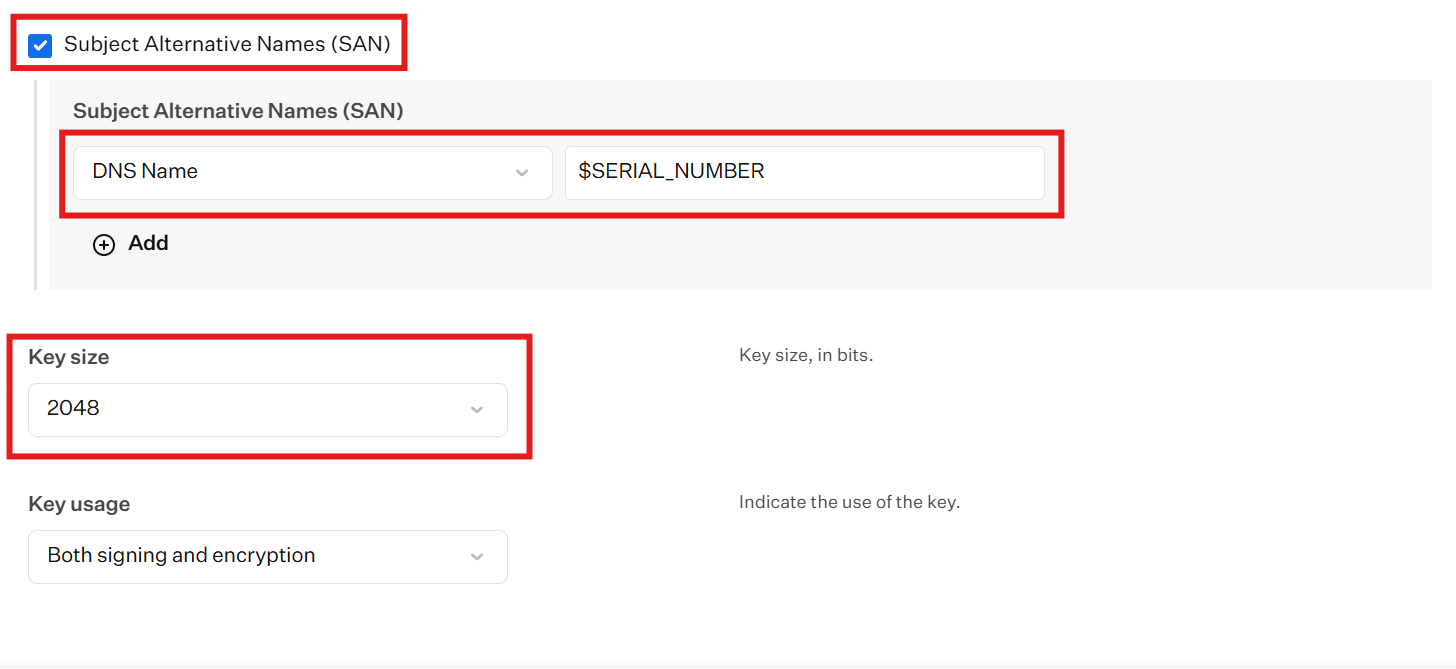
Check Subject Alternative Names (SAN), then set the SAN type to DNS Name and the value to
$SERIAL_NUMBER. This makes the certificate a device certificate that identifies the device, not its user. As with the subject, use only device variables from the Iru global variables for all device families. Don’t use user variables such as$EMAILor$USERNAME: they change when the device is reassigned and are empty when it has no assigned user. -
Set Key size to 2048 or higher. Leave Key usage as Both signing and encryption.
-
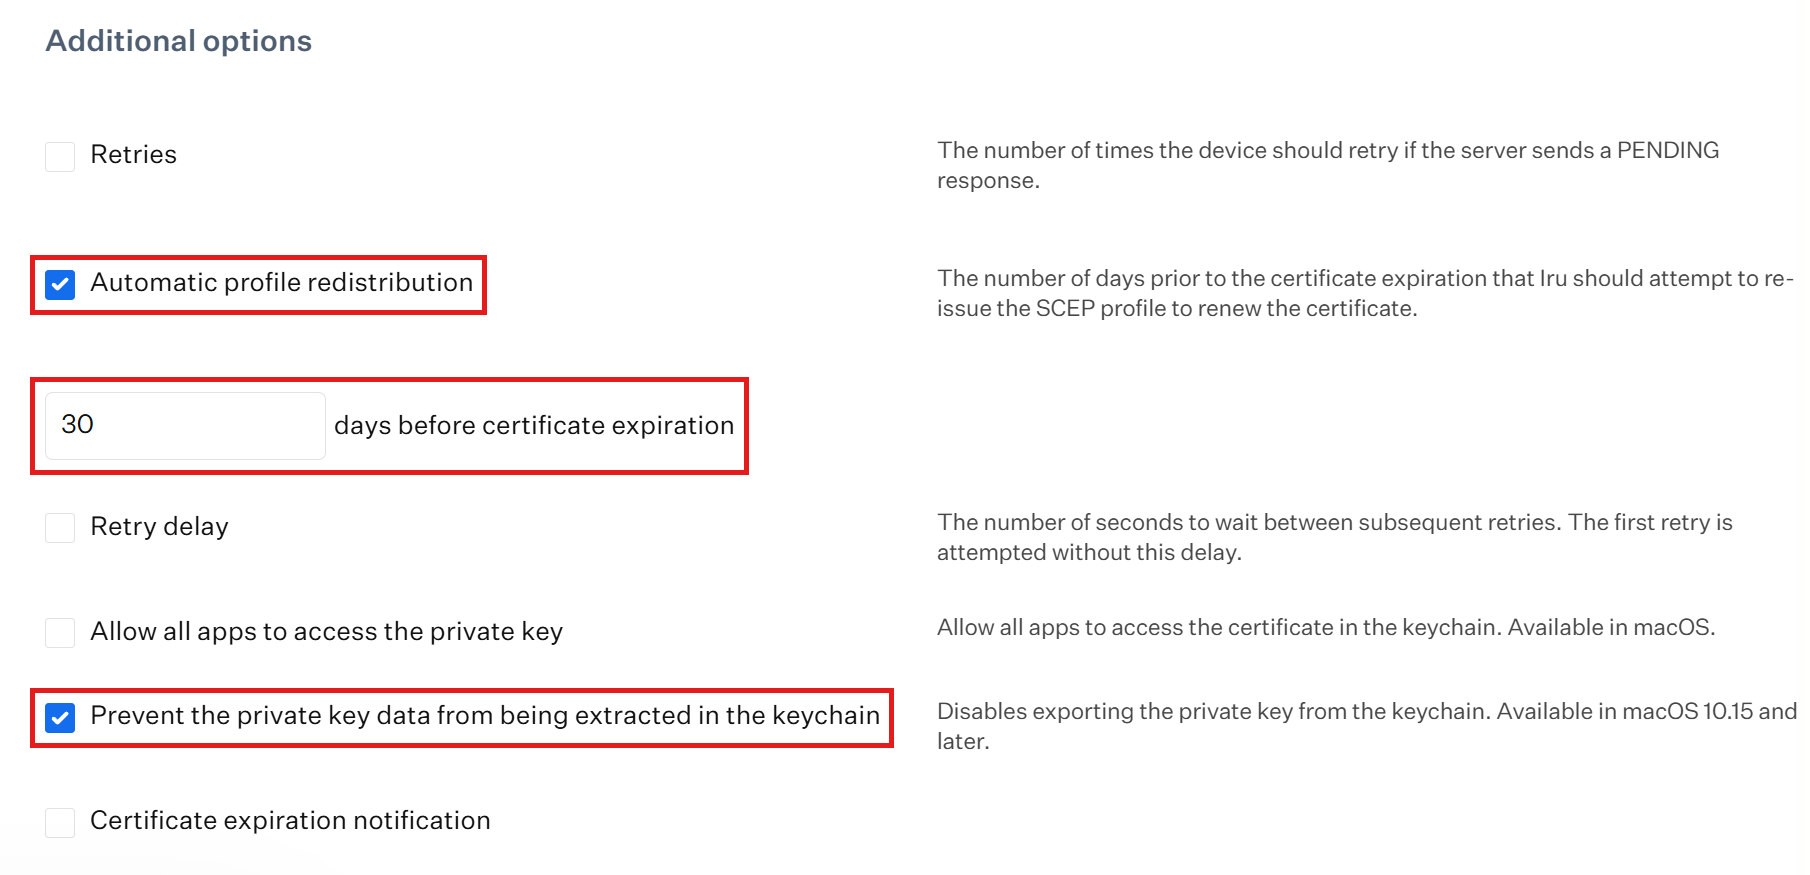
Under Additional options, check Automatic profile redistribution and enter
30days before certificate expiration. We recommend keeping this enabled so Iru renews certificates before they expire. If you disable it, certificates can expire and your devices will lose Wi-Fi access. -
Check Prevent the private key data from being extracted in the keychain, so the certificate’s private key can’t be exported from the device.
-
Click Done to close the panel. The SCEP Certificate now appears under Identity certificate.
How to Configure RADIUS Server Trust in Iru
-
Scroll down to Certificate trust and check Specify trusted certificates.
-
Upload the
rootca.cerfile you downloaded from Keytos Shield.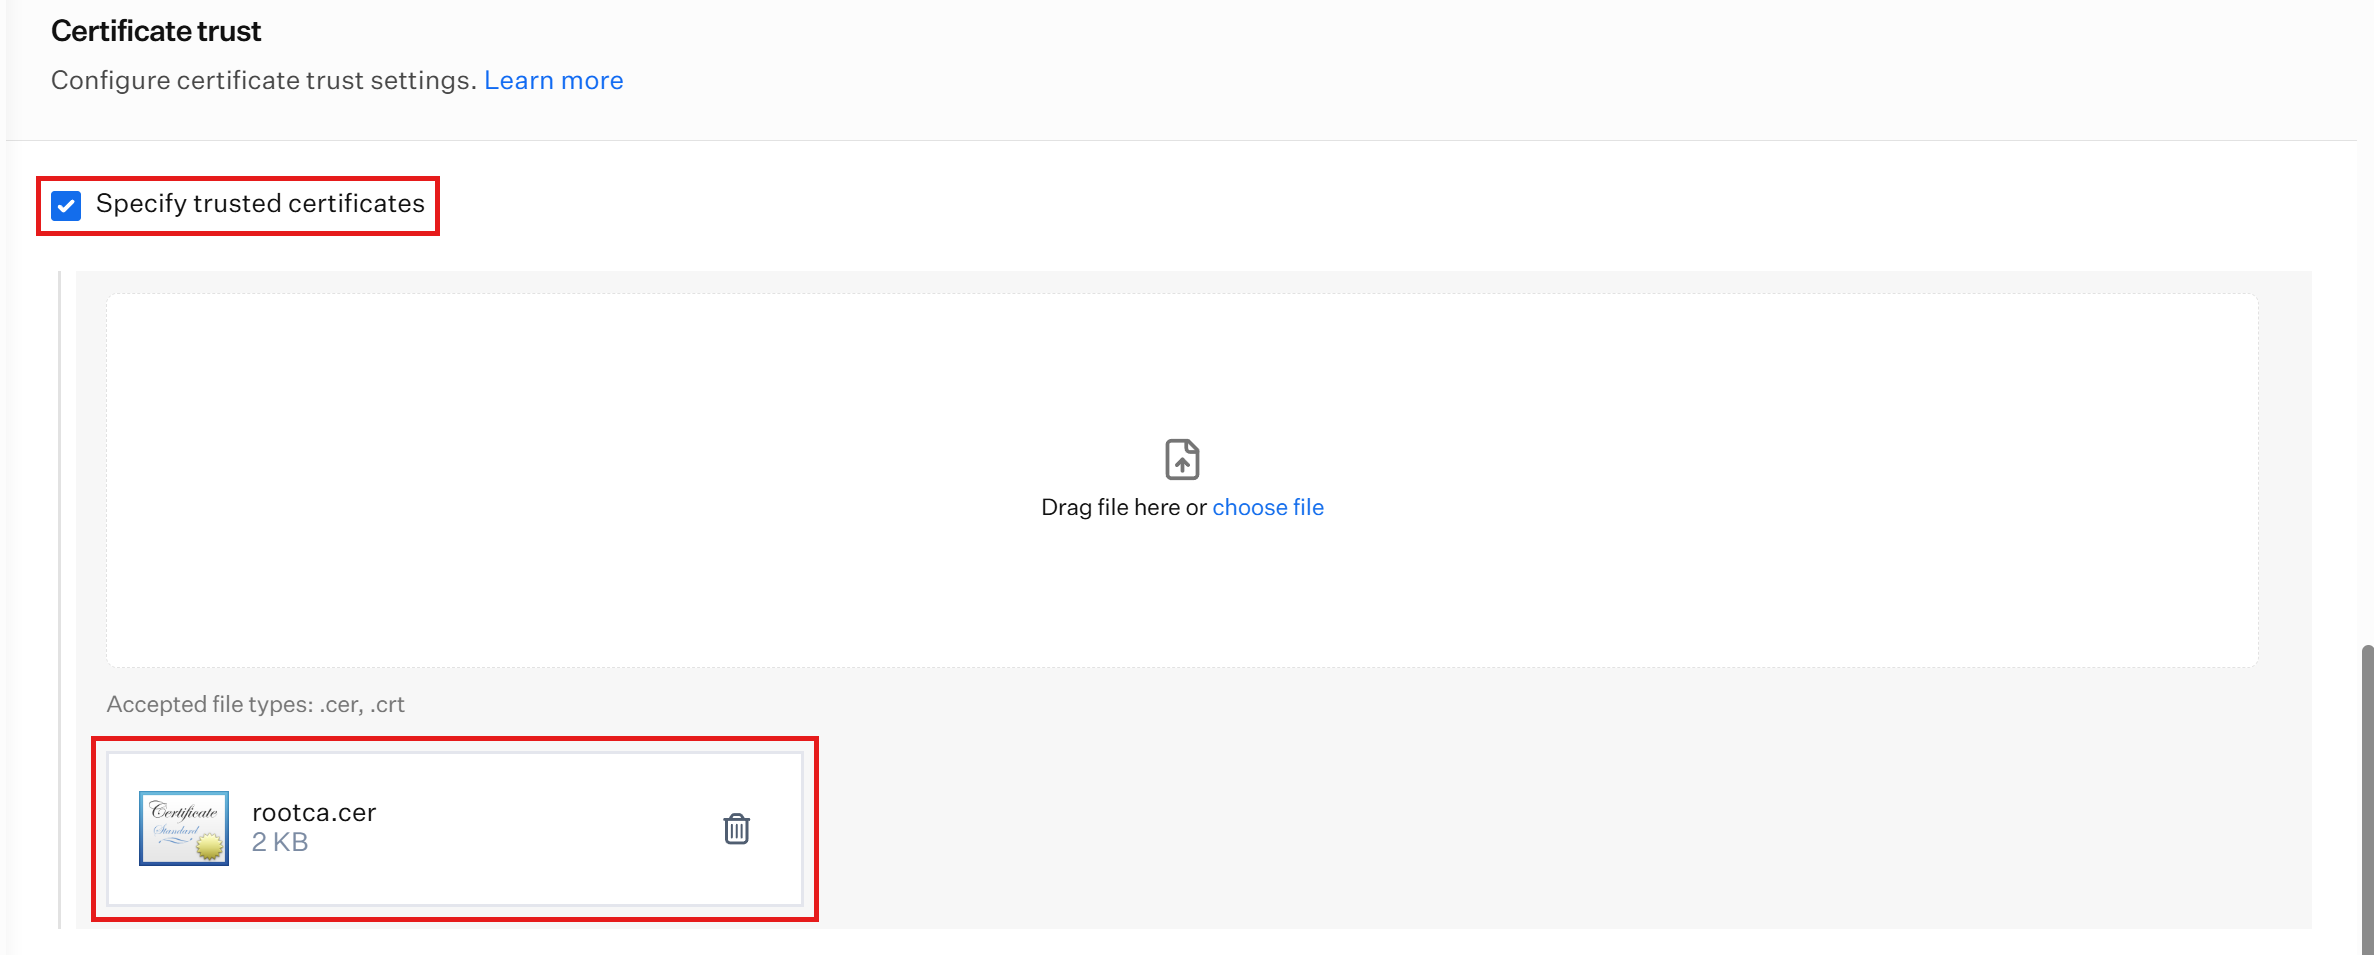
-
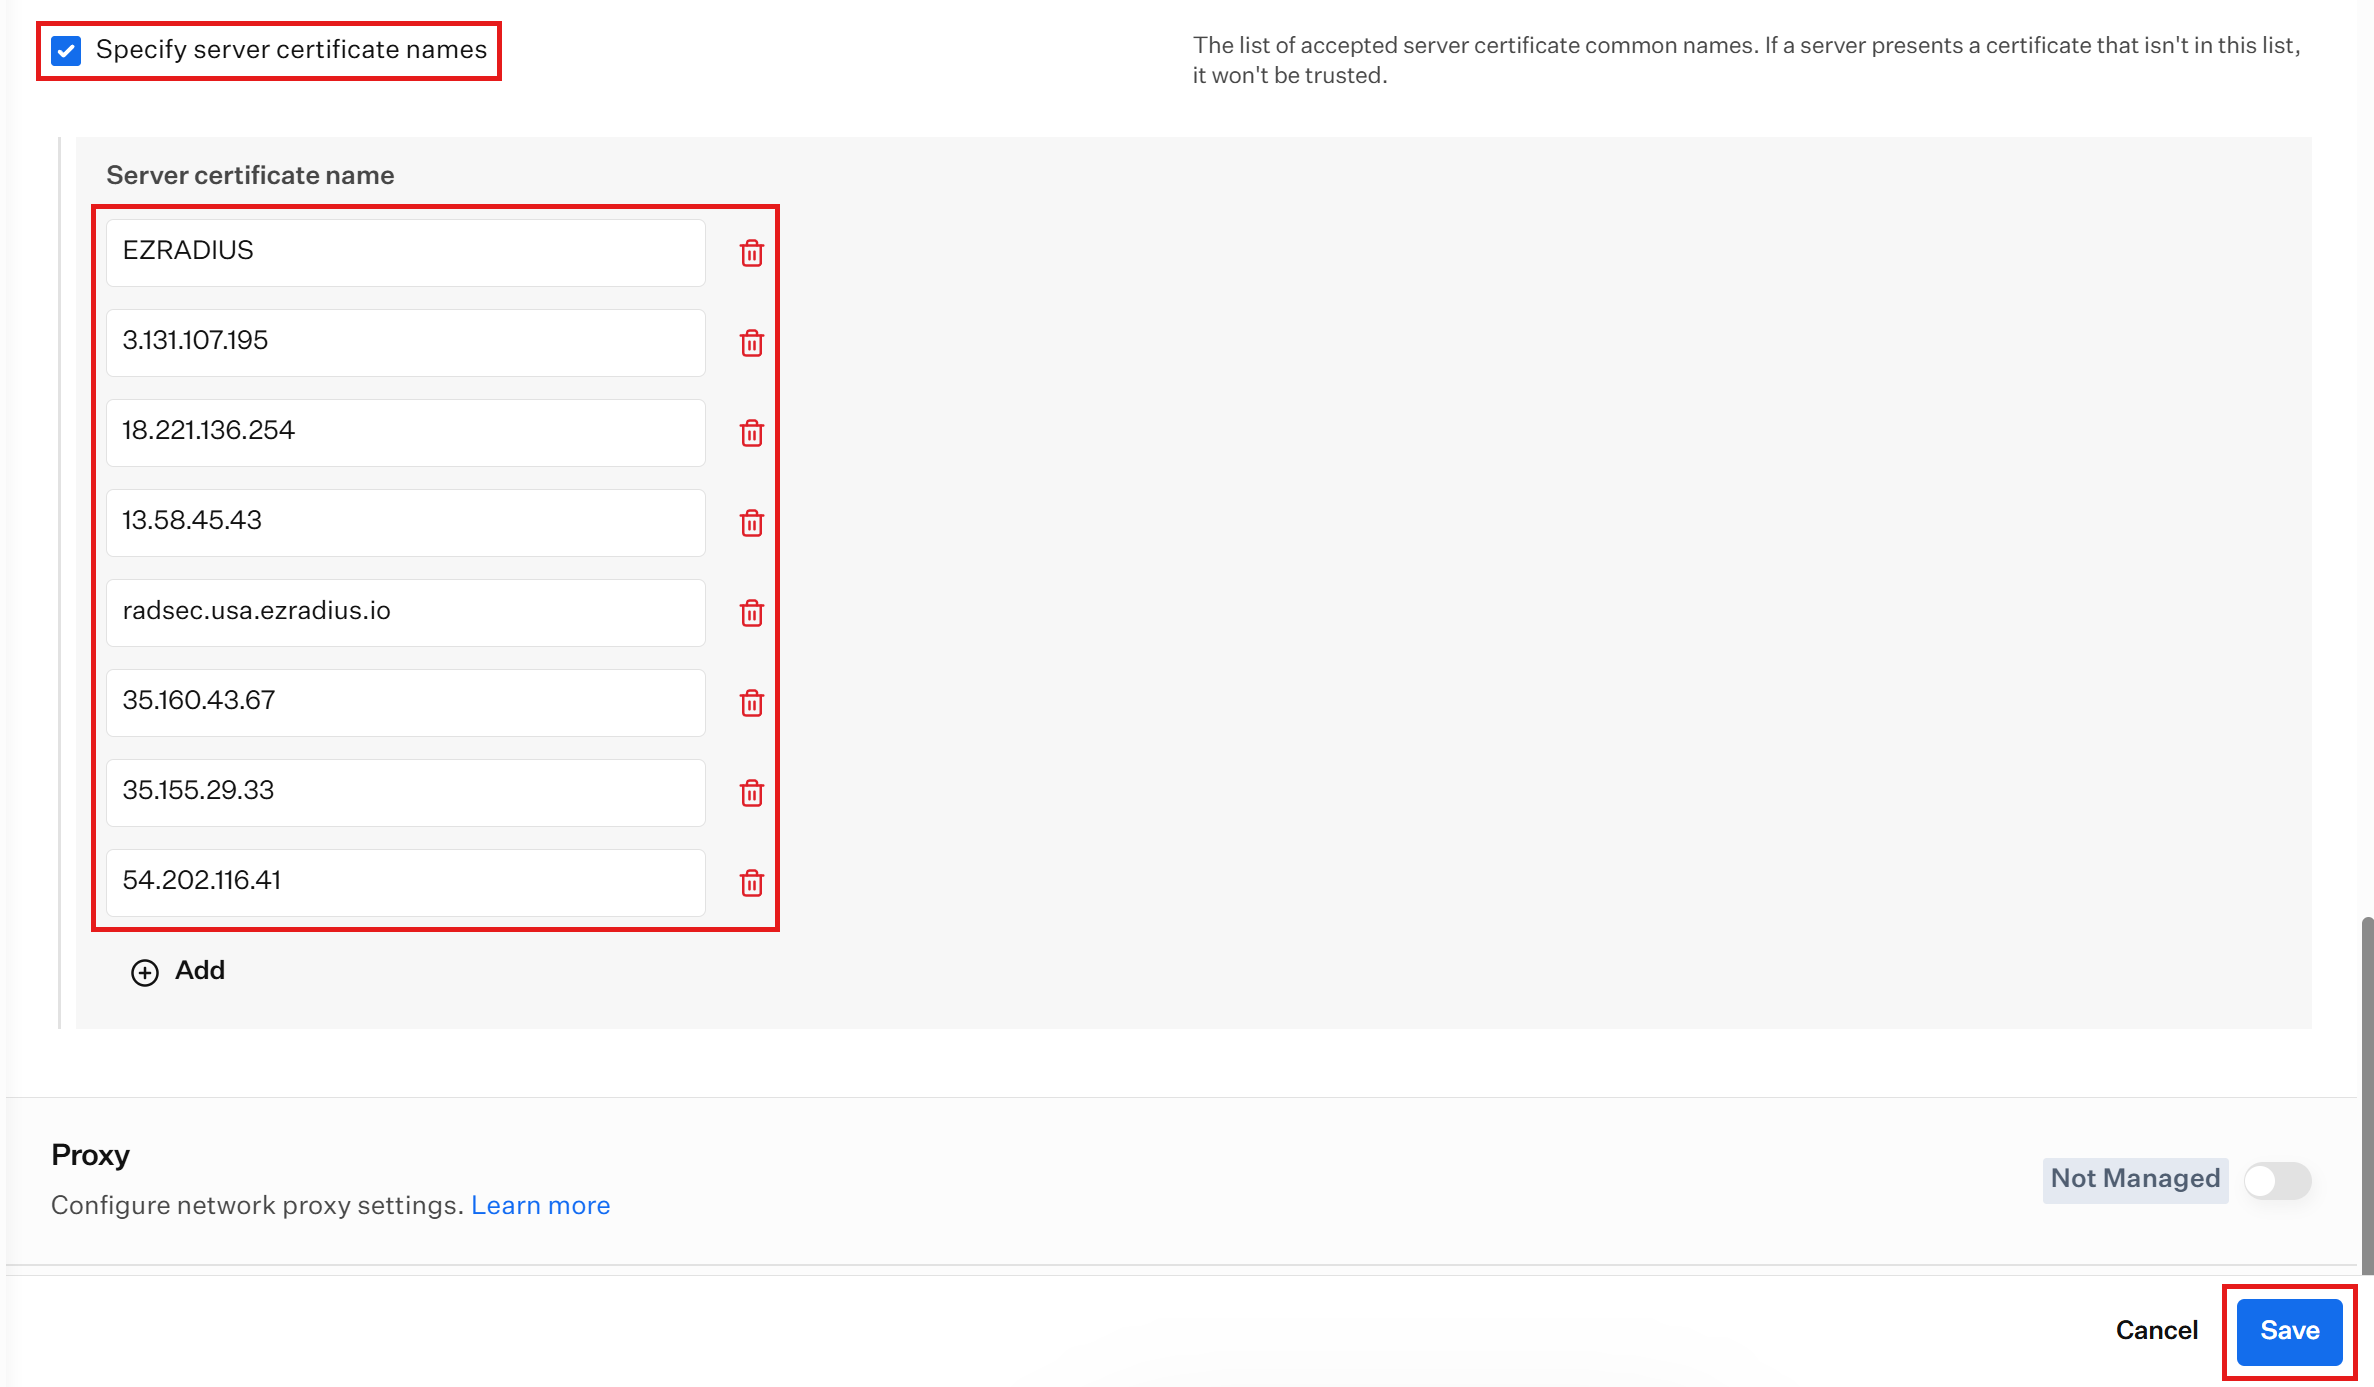
Check Specify server certificate names.
-
Click Add and enter each RADIUS server name you copied from Keytos Shield, one per row. Together with the trusted Root CA, this makes sure devices only send their certificate to your Shield RADIUS servers.
-
Click Save.
Step 7 - How to Assign the Keytos Shield Library Items to a Blueprint in Iru
Iru only installs Library Items that are assigned to a Blueprint. Assign both Library Items to the Blueprint your devices use.
-
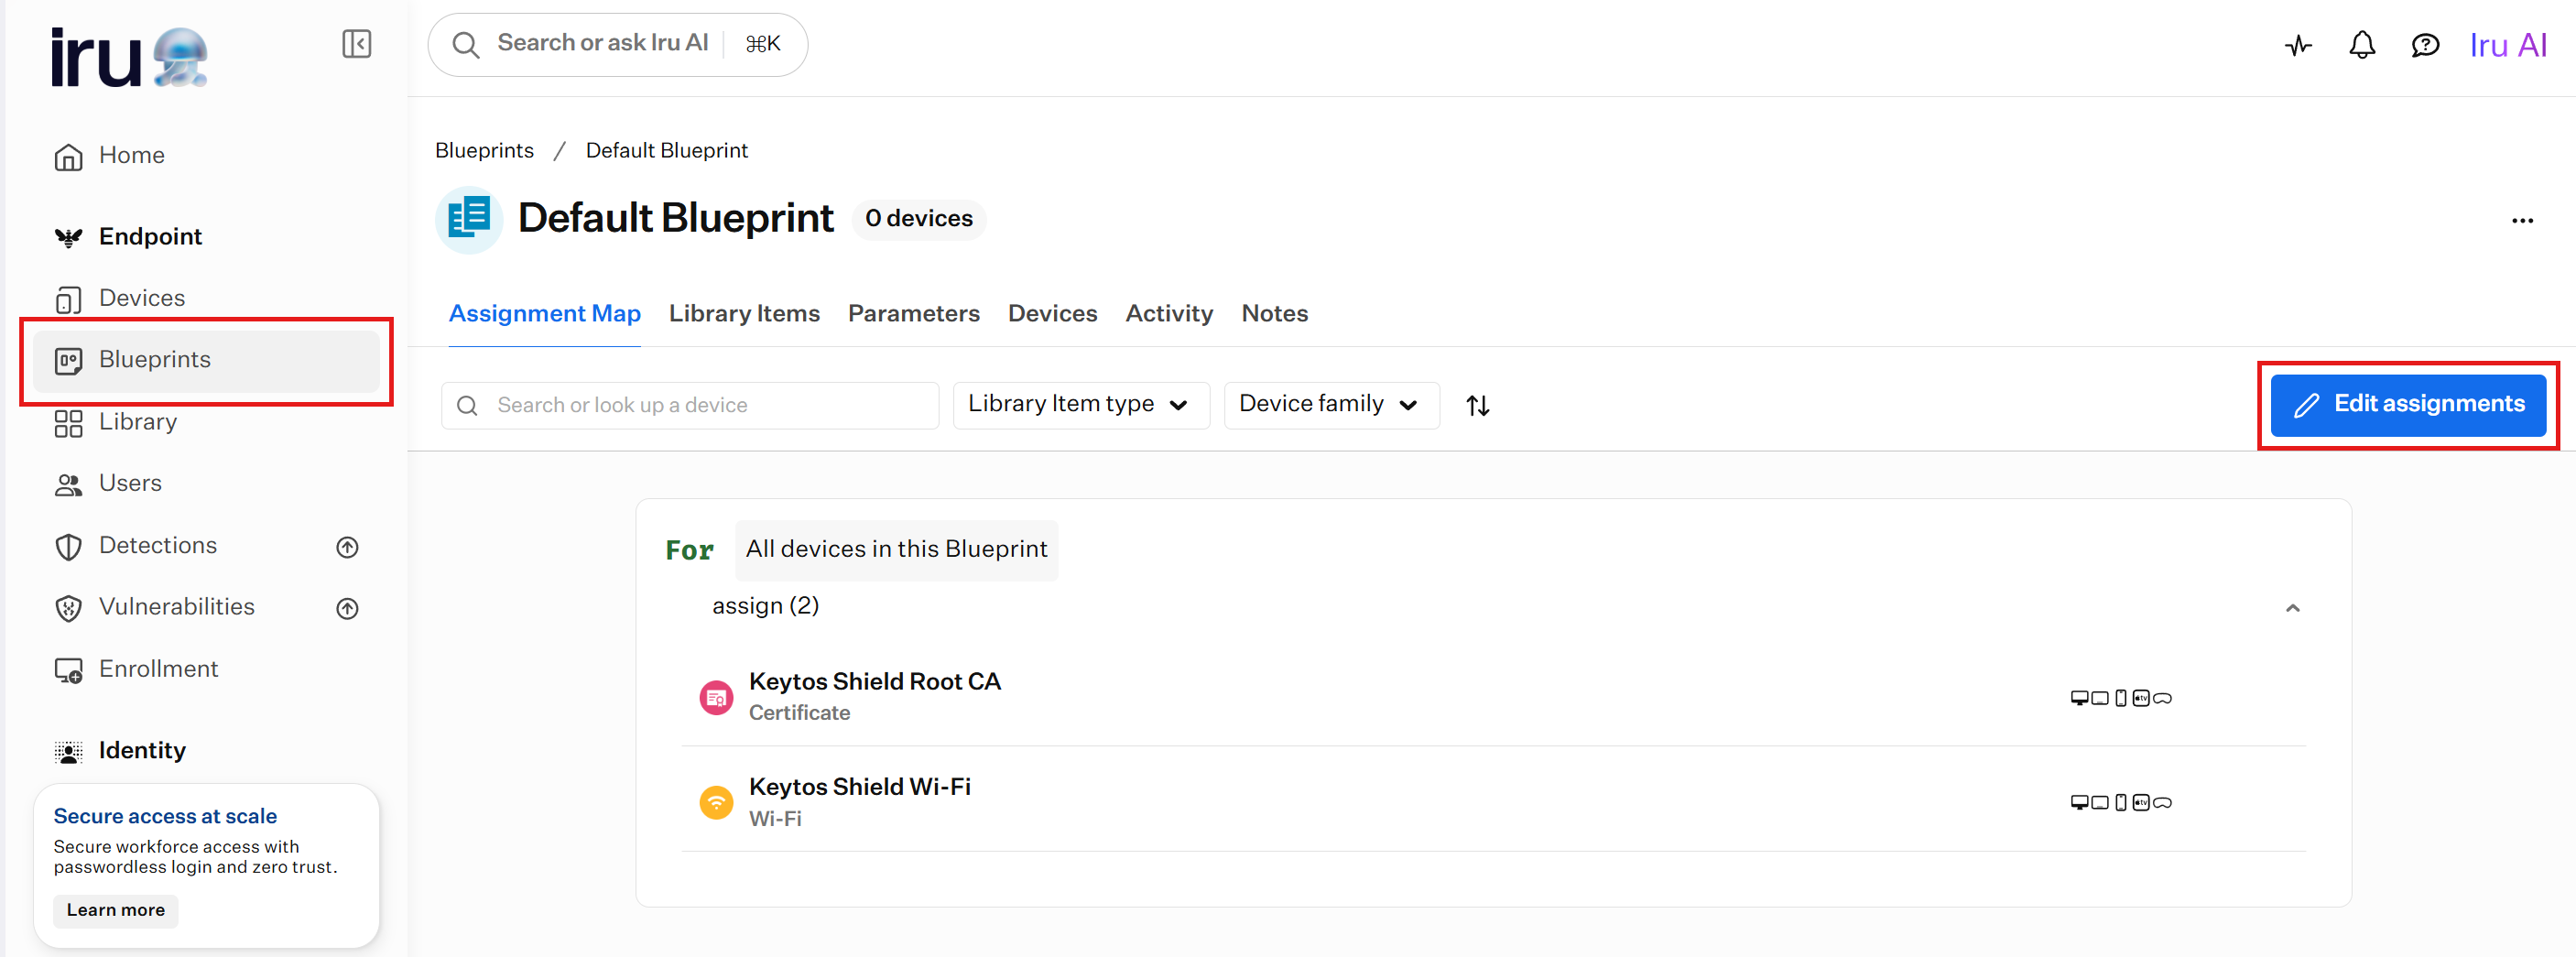
From the left-hand menu, click Blueprints and open the Blueprint your devices use, such as Default Blueprint.
-
On the Assignment Map tab, click Edit assignments.
-
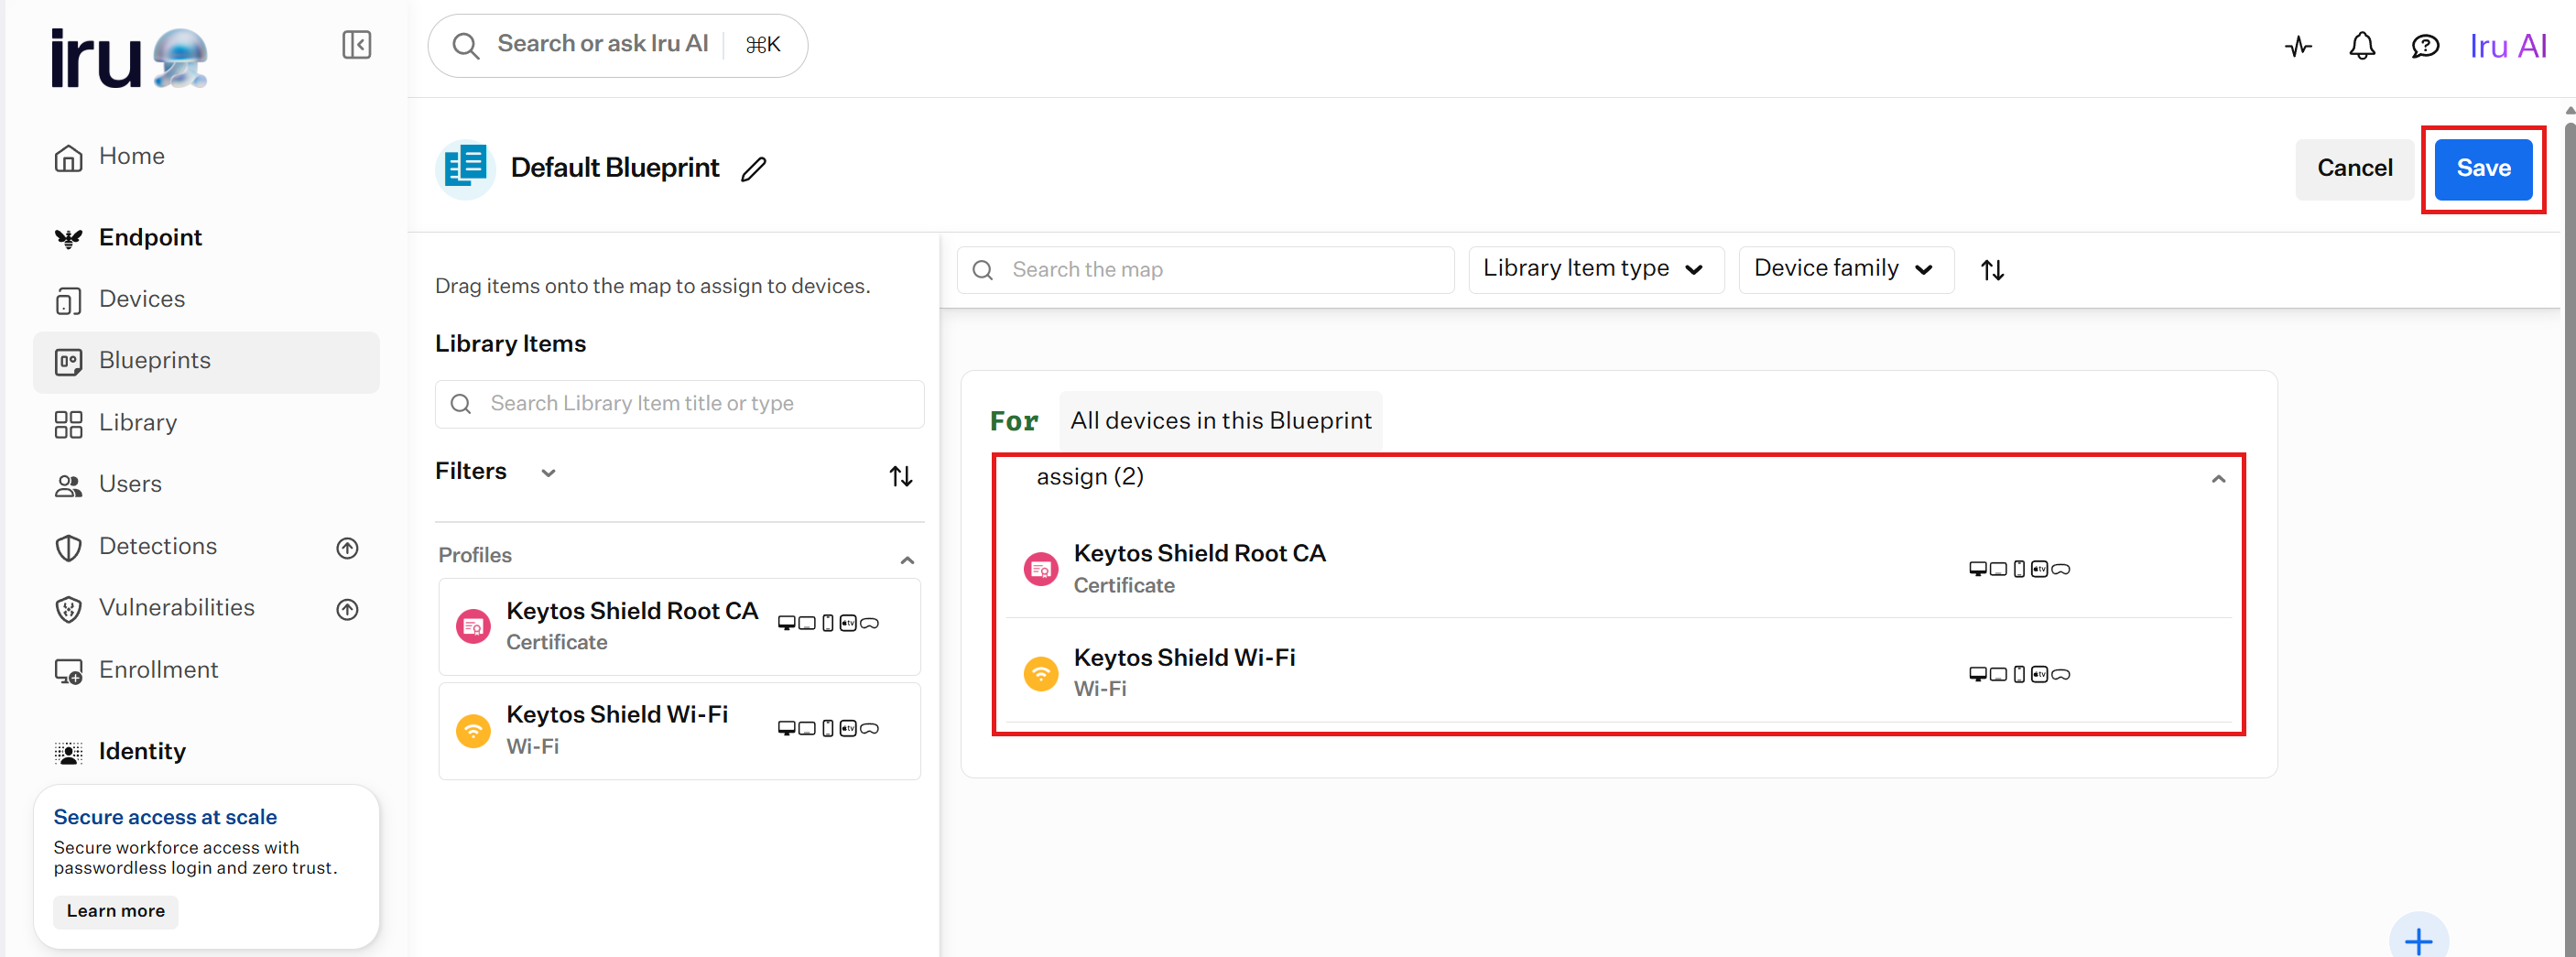
Drag the Keytos Shield Root CA and Keytos Shield Wi-Fi Library Items from the Library Items list onto the map.
-
Click Save, then click Save again in the Save changes? dialog.
Done! The next time your devices check in with Iru, they will install the Shield Root CA, request their own certificate from Keytos Shield, and join your Wi-Fi network automatically.
Step 8 - How to Test Your Keytos Shield Wi-Fi Configuration on macOS
Now that you have configured your Iru Wi-Fi profile to use Cloud RADIUS for authentication, the next step is to test the configuration on a managed macOS device. Follow these steps to test your Wi-Fi configuration:
-
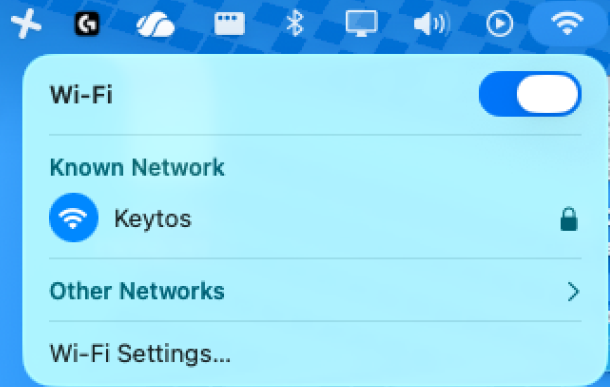
On a managed macOS device, click on the Wi-Fi icon in the menu bar and select the Wi-Fi network that you configured in your Iru Wi-Fi profile.
-
If your configuration is correct, the device should successfully connect to the Wi-Fi network without any prompts.
-
If you are prompted to select a certificate for the network, your Wi-Fi profile is not fully configured: usually the RADIUS server’s Subject and Subject Alternative Names are missing from the trusted server names, a CA in the server certificate chain is not trusted, or the SCEP certificate has not been issued to the device yet.
You can also confirm in Keytos Shield that certificates are being issued. In your Shield portal, click Certificates in the left-hand menu to see each certificate Shield issued, or view your certificate logs.
Frequently Asked Questions About Keytos Shield and Iru
Does Keytos Shield Work with Iru (Formerly Kandji)?
Yes. Keytos Shield issues certificates to Iru managed Apple devices with static SCEP, and Iru pushes the Wi-Fi profile that uses those certificates to connect to your network with EAP-TLS.
Do I Need a Separate SCEP Library Item in Iru?
No. For Wi-Fi, configure the SCEP certificate inside the Wi-Fi Library Item, as shown in this guide. Apple devices require the identity certificate to be in the same configuration profile as the Wi-Fi settings. A separate SCEP Library Item would issue a second certificate that the Wi-Fi profile can’t use.
Why Do I Need to Add My RADIUS Server Names?
Specifying trusted server certificate names, together with your Shield Root CA, makes sure your devices only authenticate against your Shield RADIUS servers. Without them, a device could send its certificate to a rogue access point that impersonates your network.
How to Troubleshoot RADIUS Authentication for Keytos Shield
If your devices can’t connect to your network, refer to our troubleshooting guide.
🔎 Shield RADIUS Troubleshooting Guide