
















How to Distribute Keytos Shield Network Profiles to Your macOS Devices in NinjaOne MDM
Overview - How to Distribute Network Profiles to macOS Devices via NinjaOne
To connect your NinjaOne-managed macOS devices to your network, you need to distribute a configuration profile that includes the necessary network settings, authentication methods, and certificates. This guide will walk you through the steps to configure and push these profiles to macOS devices using NinjaOne for EAP-TLS.
Step-by-Step Guide - How to Distribute Network Profiles to macOS Devices via NinjaOne
Follow these steps to configure and push the necessary NinjaOne configuration policies for macOS devices:
Prerequisites for Configuring Apple Network Profiles via NinjaOne
Before you begin configuring network profiles for macOS devices via NinjaOne, ensure that you have completed all the necessary prerequisites:
- The Keytos Entra ID applications are registered in your tenant.
- You have signed up for a Keytos Shield Plan.
- You have existing access policies in Keytos Shield.
- You are a Subscription Owner or Network Administrator.
- You are an NinjaOne Administrator.
Step 1 - How to Enable NinjaOne Integration in Keytos Shield Subscription
The first step in setting up certificate-based RADIUS authentication for NinjaOne with Keytos Shield is to enable NinjaOne in your Keytos Shield subscription.
In step 2, Tell us about your environment, of the Keytos Shield network security onboarding guide, ensure you have checked NinjaOne, in addition to any other MDMs in your environment.
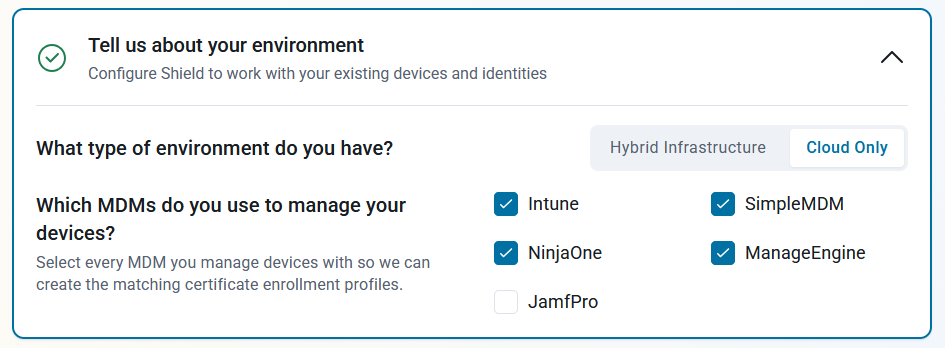
If you’ve already gone through the onboarding guide, you can update the list of MDMs you manage devices with.
-
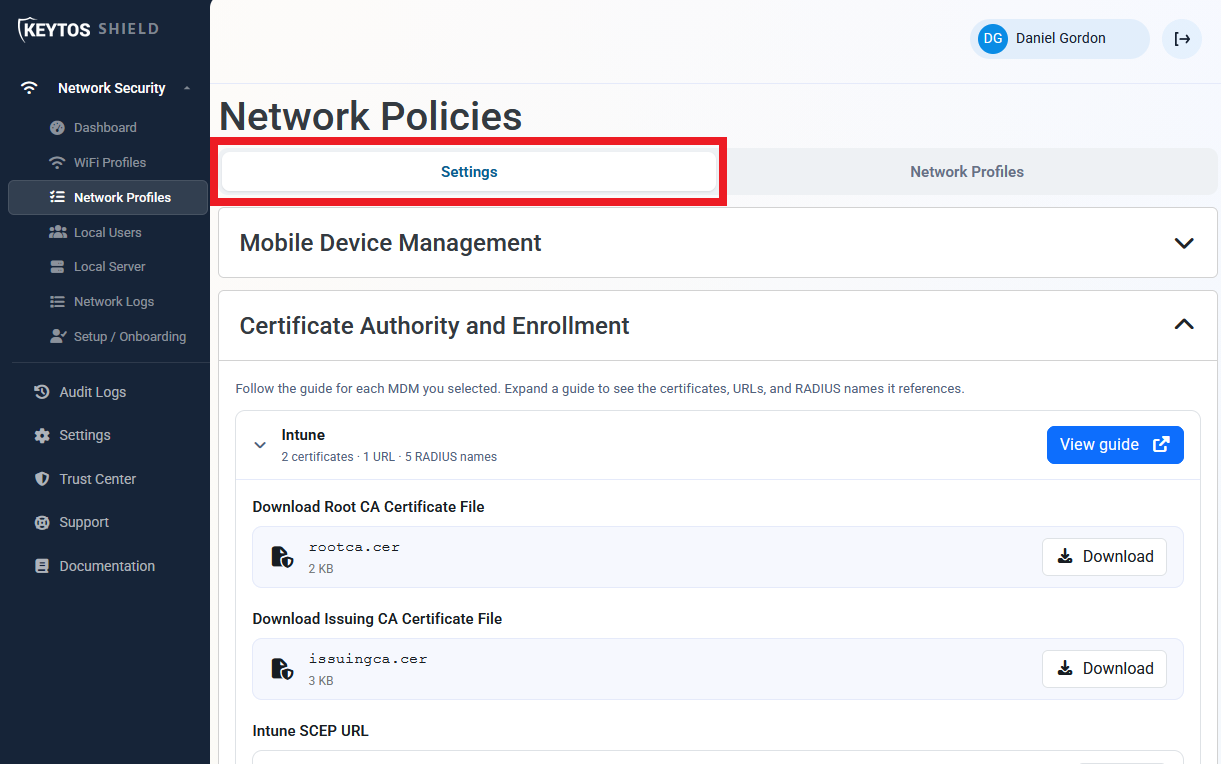
Navigate to the Keytos Shield Network profiles page from the left-hand menu.
-
At the top of the page, select the Settings tab.
-
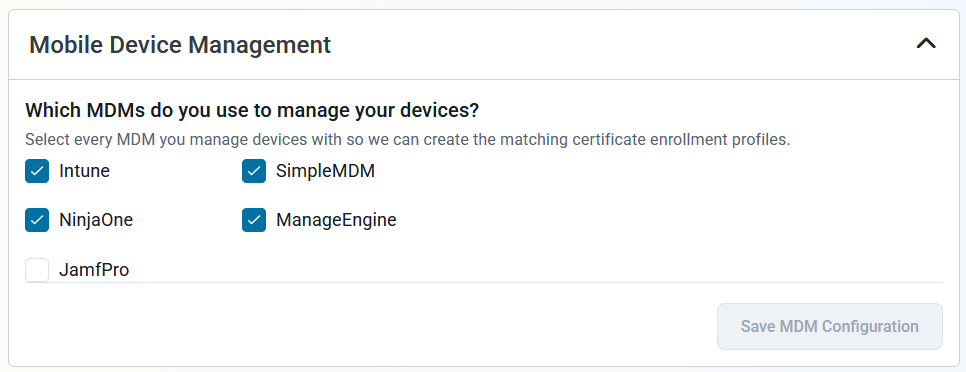
Scroll down to the bottom of the page and expand the Mobile Device Management section.
-
Ensure you have checked NinjaOne in addition to any other MDMs in your environment.
Step 2 - How to Install the Apple MDM App in NinjaOne
To manage and deploy Apple management profiles to your macOS, iOS, and iPadOS devices, you will first need to configure Apple MDM in NinjaOne. This involves creating an Apple MDM push certificate and uploading it to NinjaOne to establish trust between NinjaOne and Apple’s Push Notification Service (APNs). This allows NinjaOne to send management profiles, including the SCEP certificate profile we will create later, to your macOS, iOS, and iPadOS devices.
You only need to configure Apple MDM in NinjaOne once for your organization. After the initial setup, you can deploy Apple management profiles to all your macOS, iOS, and iPadOS devices without repeating this process.
-
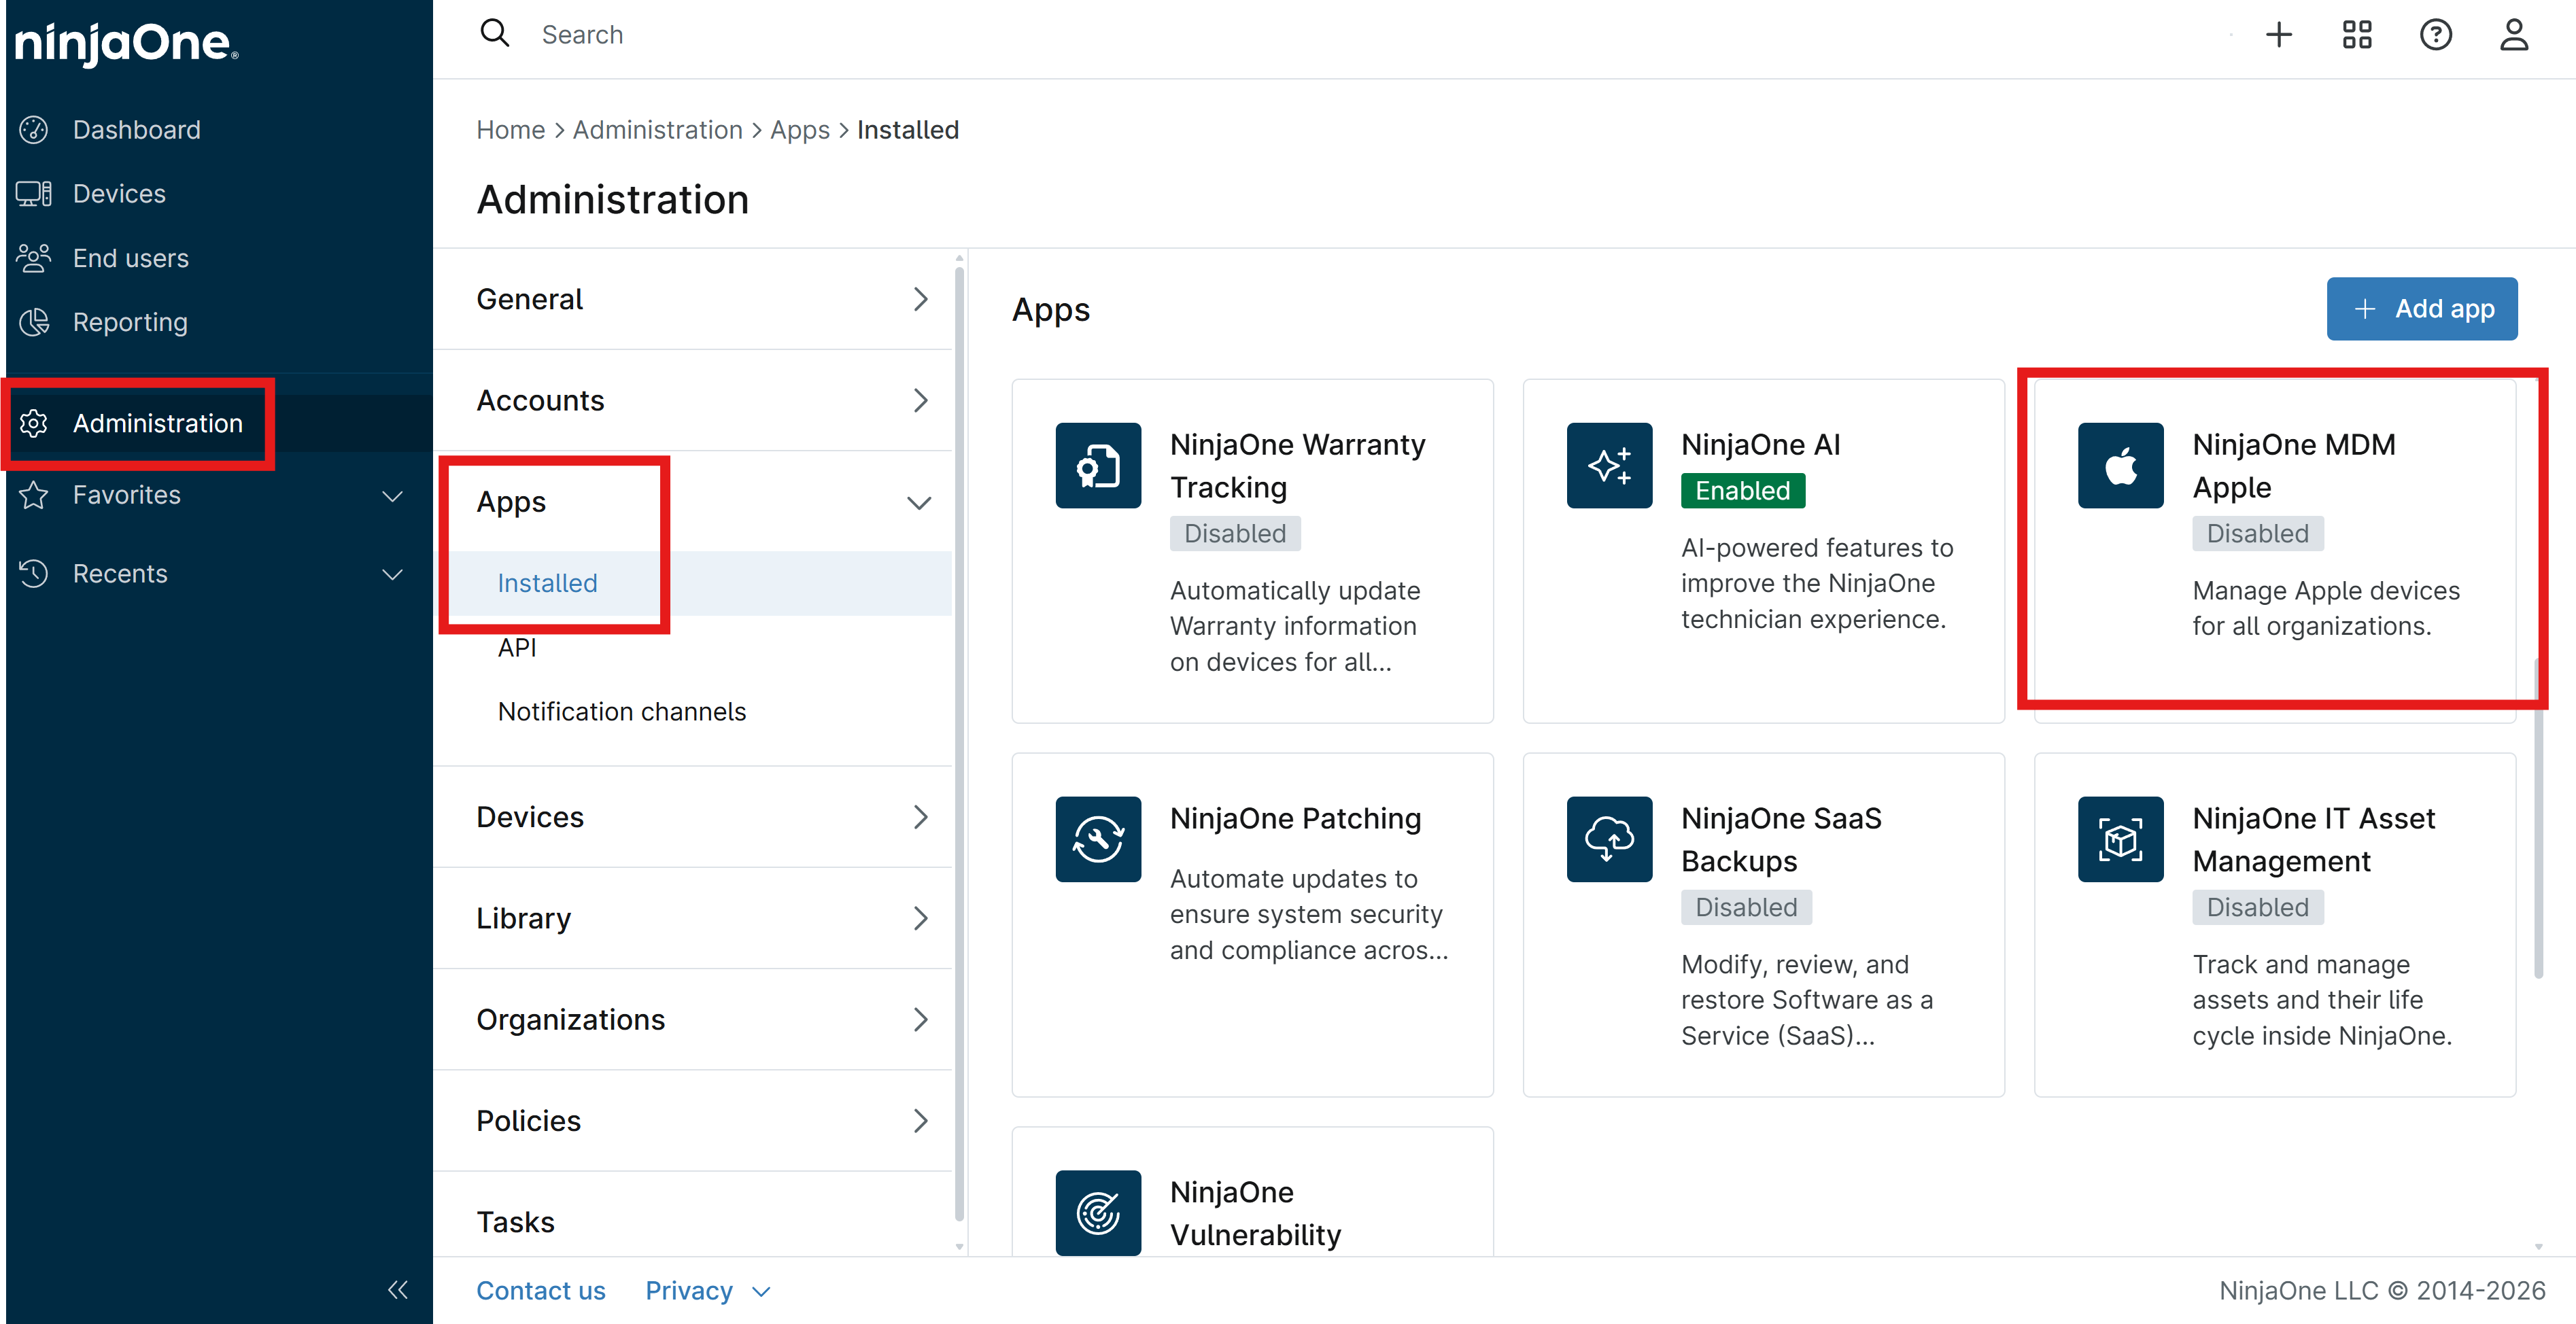
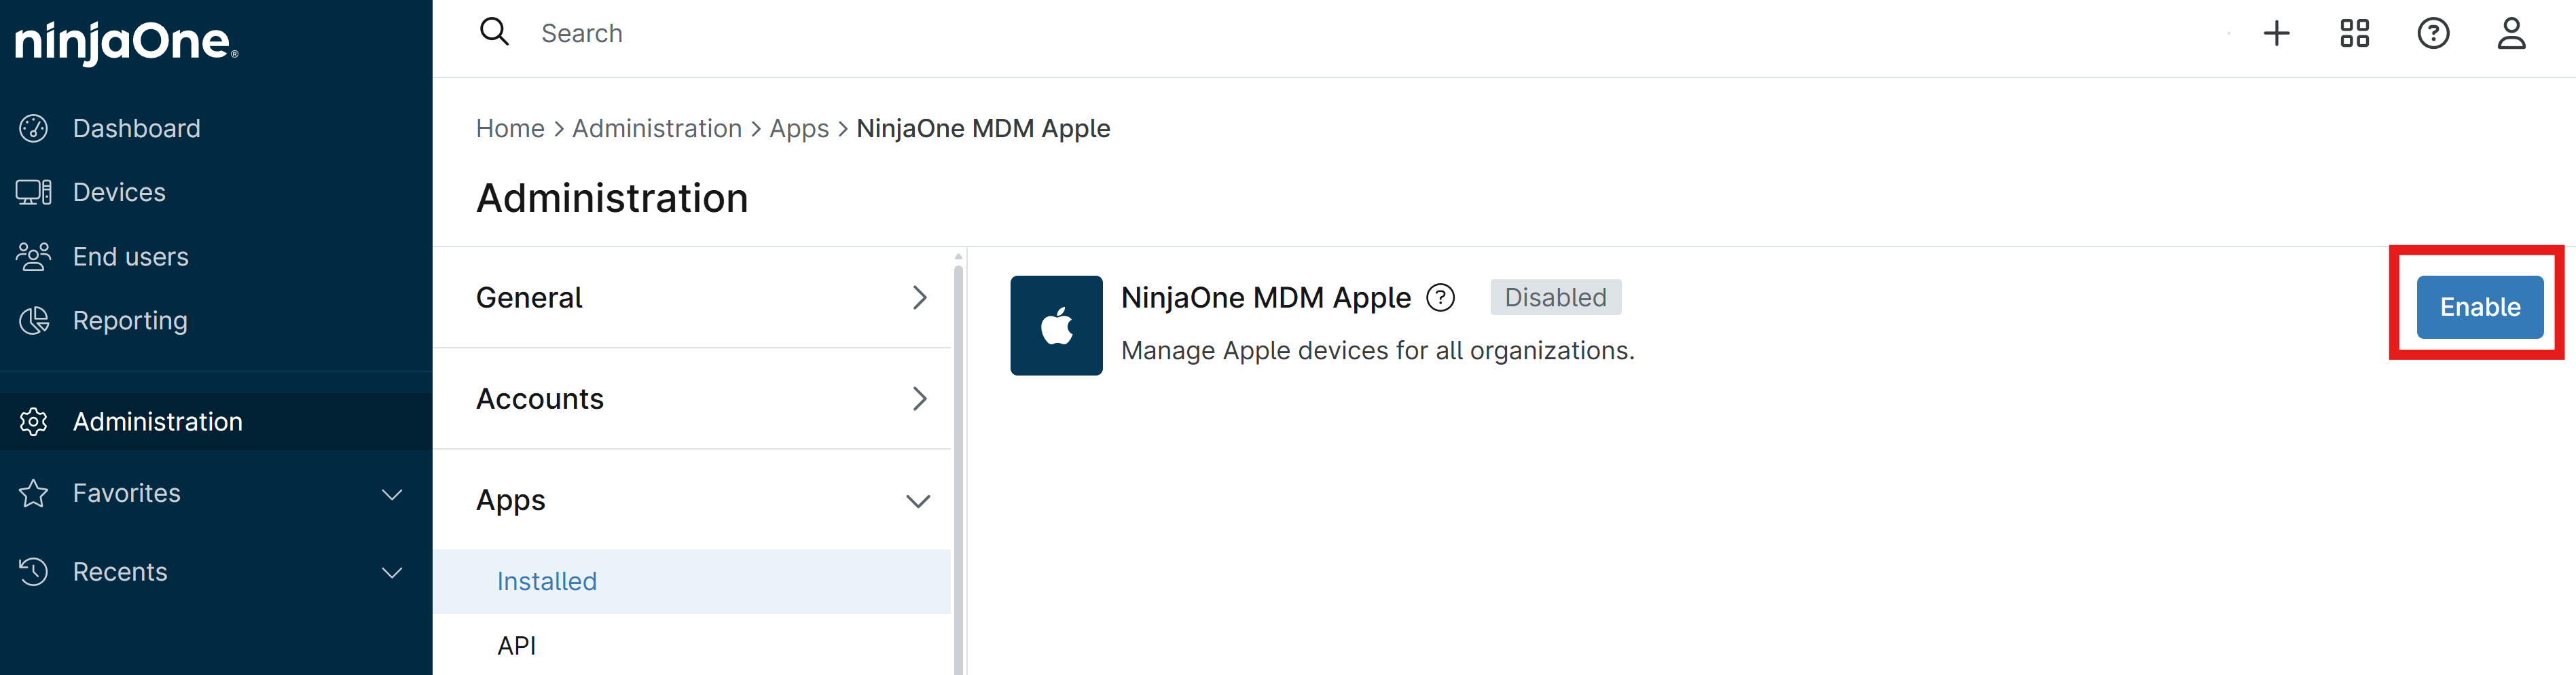
Navigate to Administration > Apps > Installed and select NinjaOne MDM Apple from the list.
-
Click Enable to begin the process of configuring Apple MDM.
-
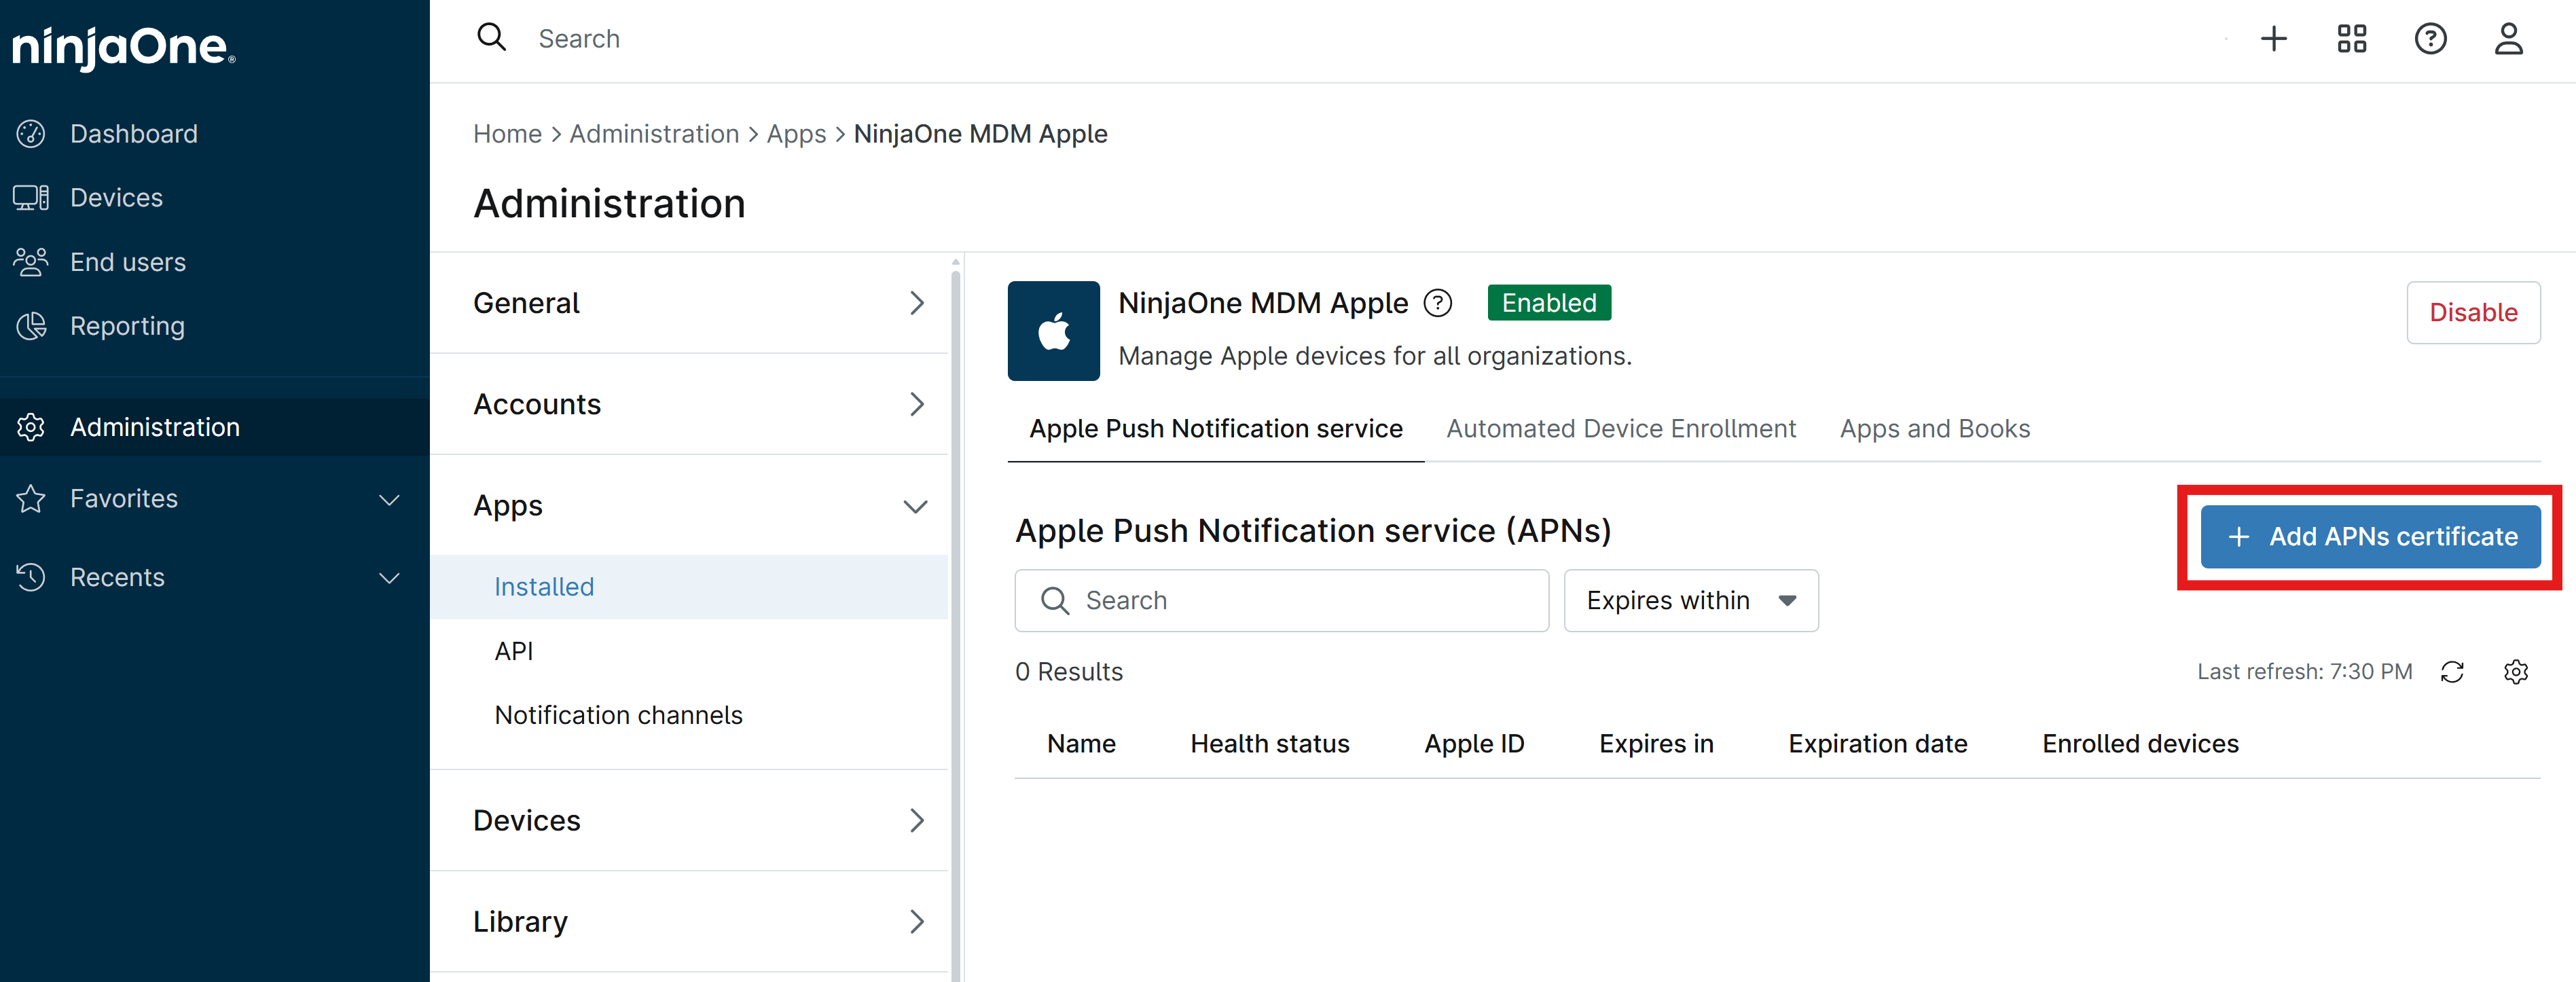
Click + Add APNs certificate to download, sign, and upload your Apple MDM push certificate.
-
Click Download file to download the CSR file that you will need to sign with Apple to create your APNs certificate.
-
Click Apple Push Certificates Portal to open the Apple Push Certificates Portal in a new tab, and sign in with your Apple ID.
-
Click Create a Certificate, read and accept the terms, and upload the CSR file you downloaded from NinjaOne.
-
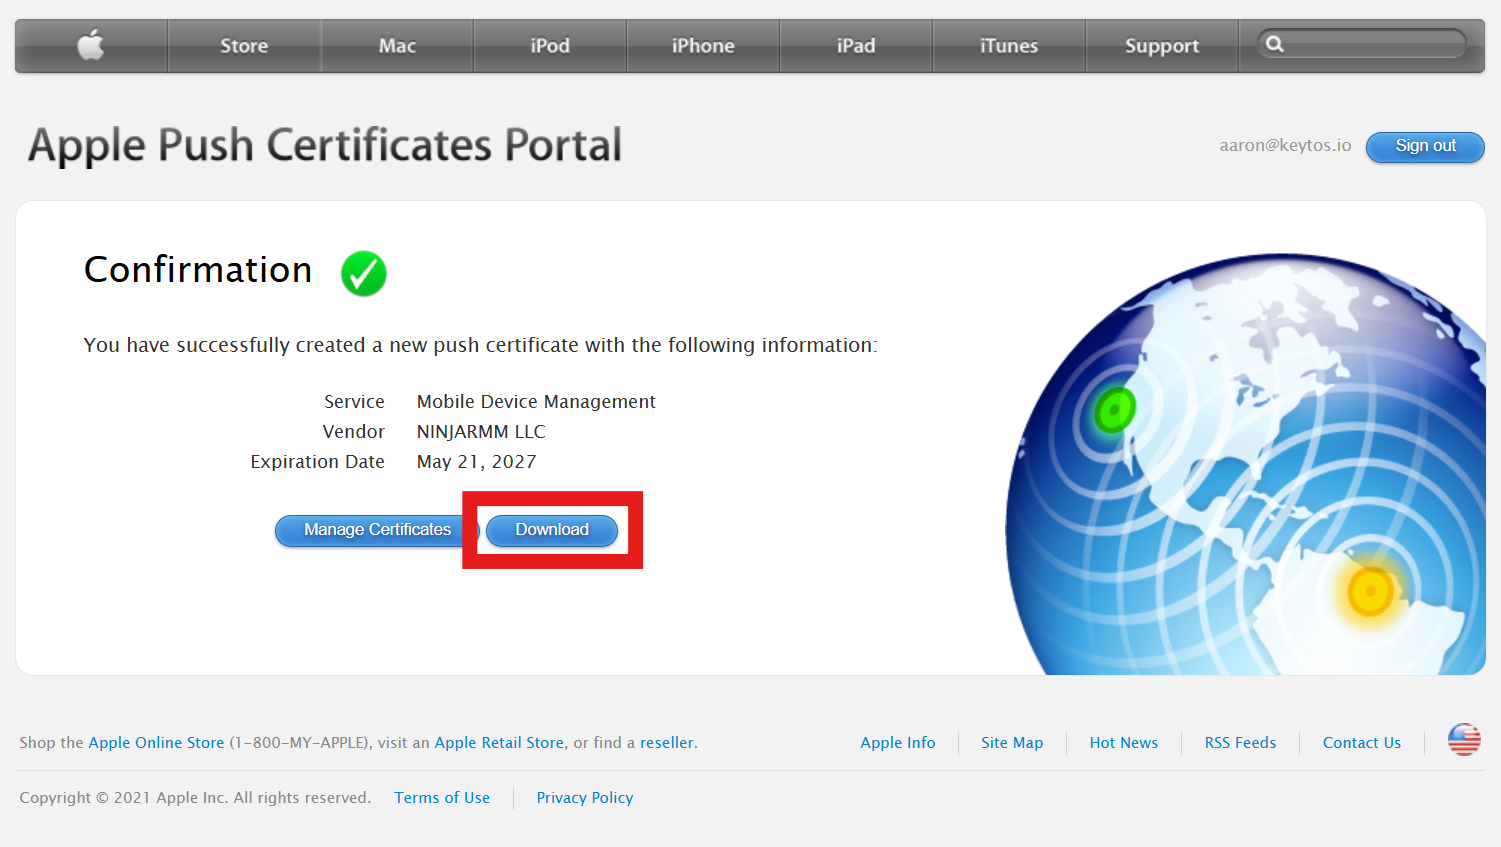
Click Download to download the signed APNs certificate from Apple. Save this file to your computer.
-
Set a calendar reminder for 30 days before the noted Expiration Date to ensure you renew your APNs certificate before it expires, as an expired APNs certificate will cause MDM management and SCEP certificate issuance to stop working until the certificate is renewed and updated in NinjaOne.
-
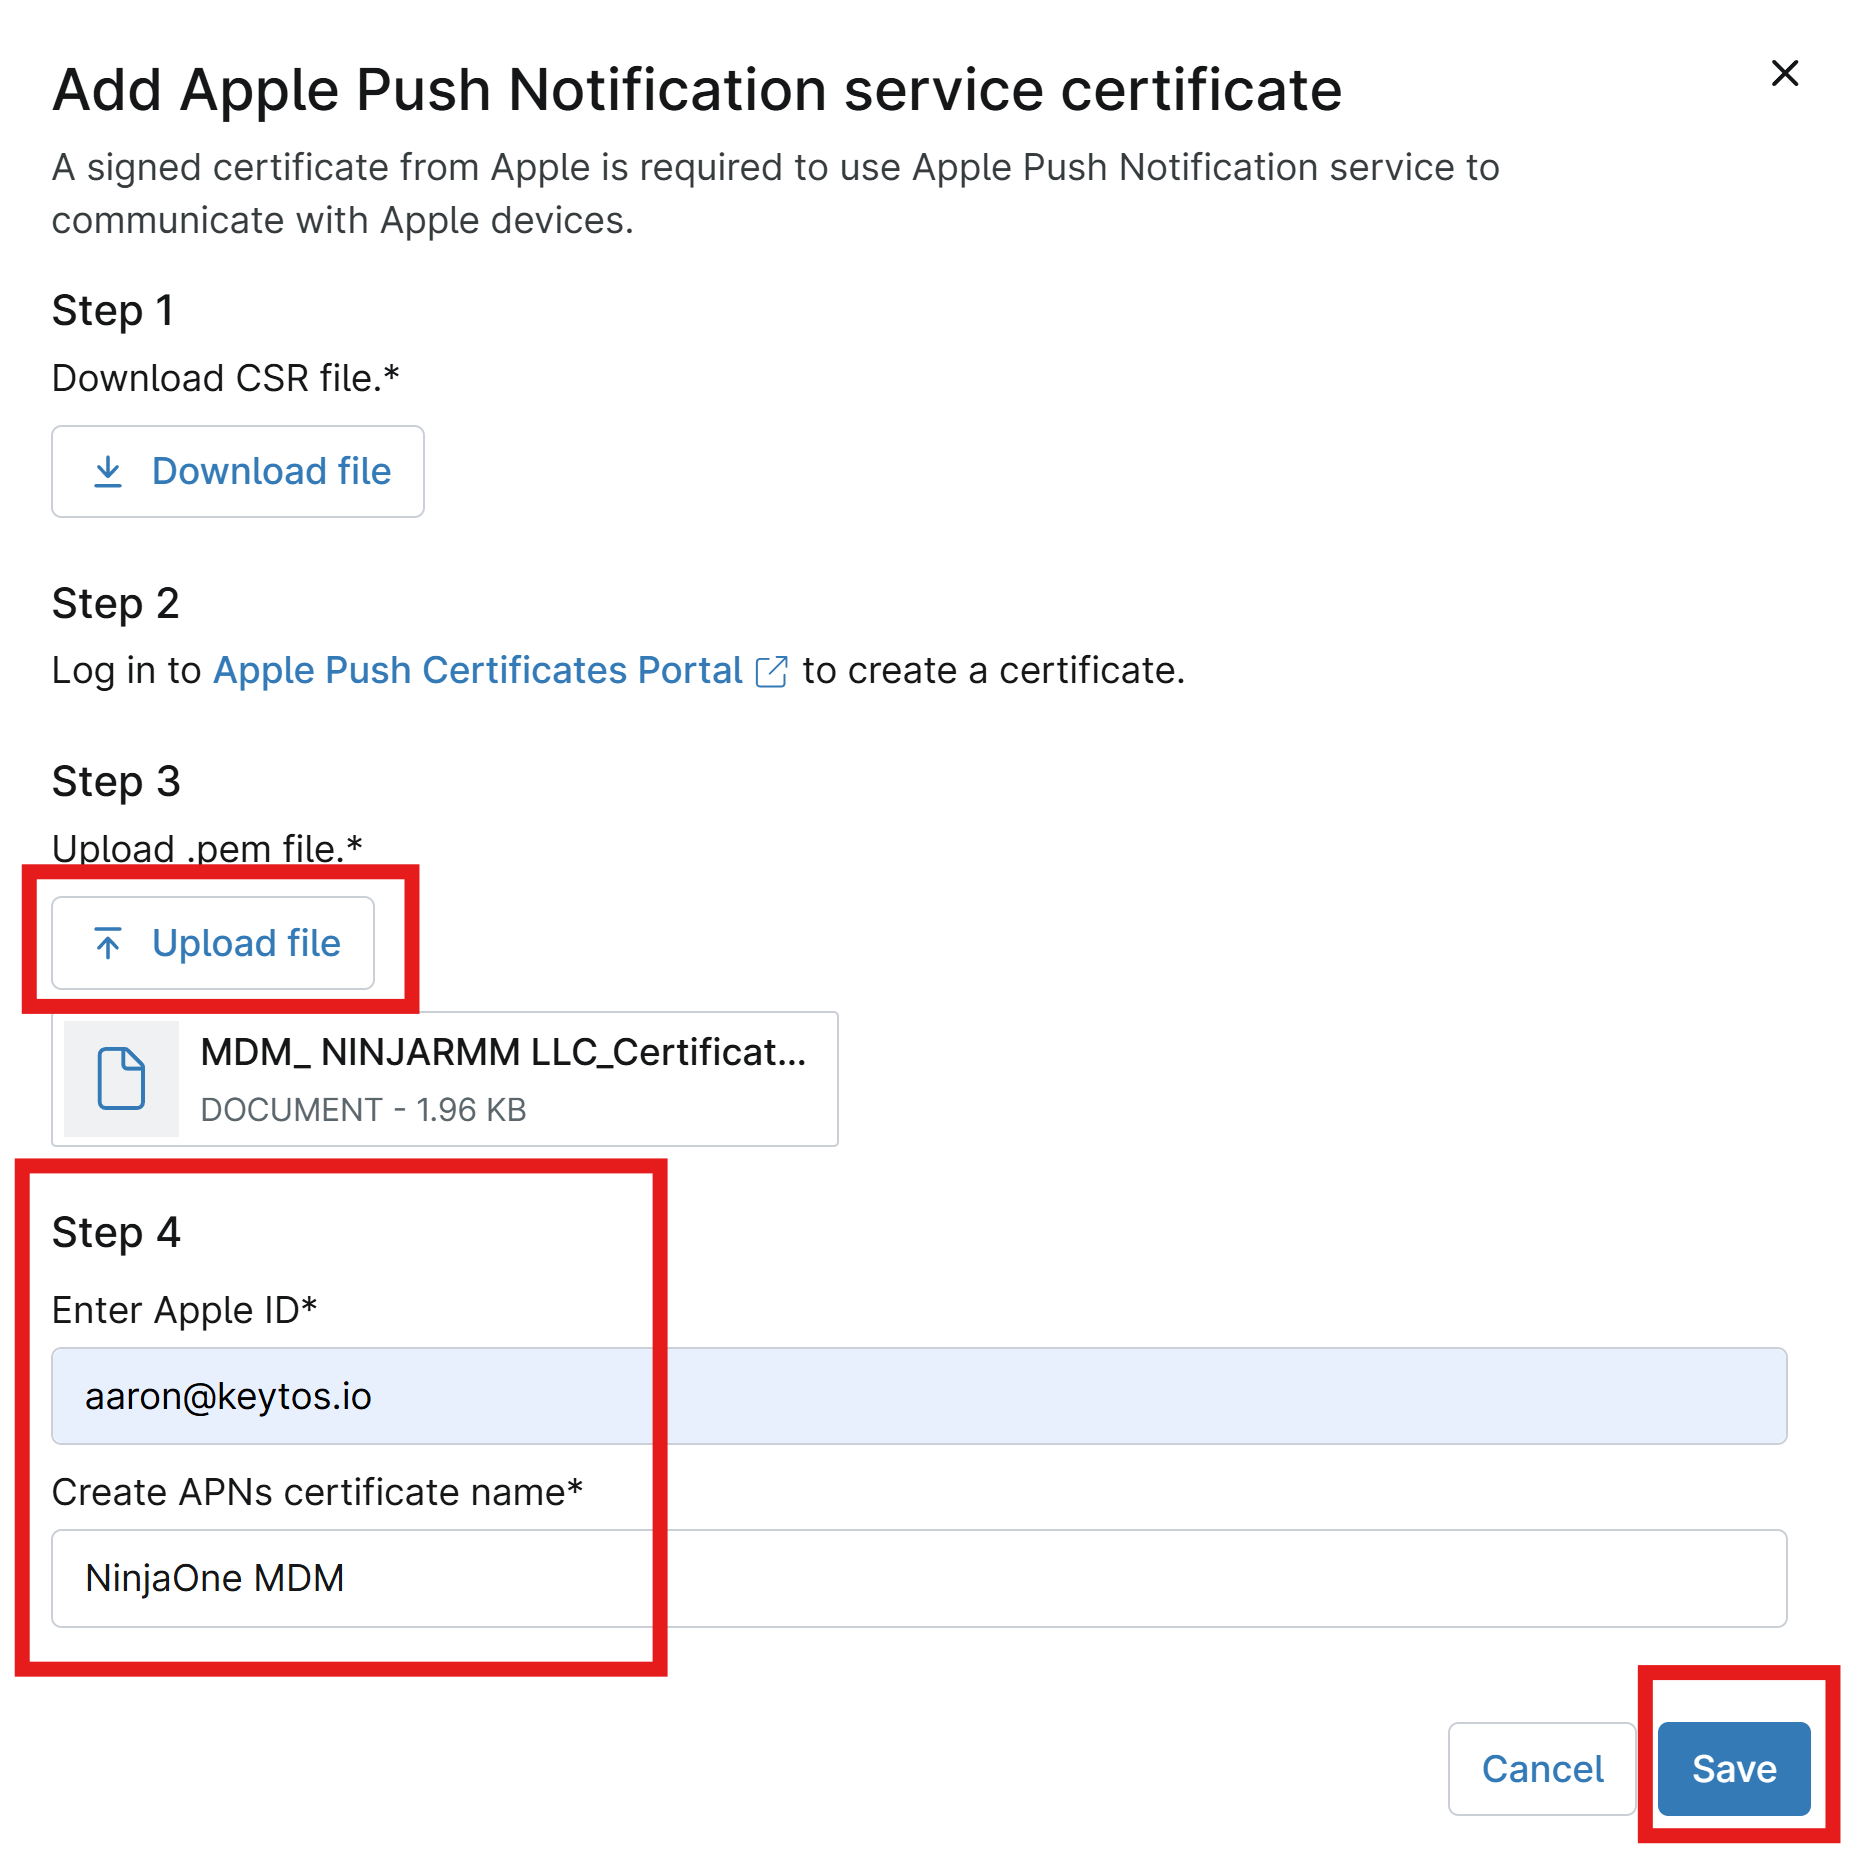
Return to the NinjaOne tab and click Upload file to upload the APNs certificate you downloaded from Apple.
-
Enter your Apple ID that you used to sign the APNs certificate in the Apple ID field, and add a descriptive name for Create APNs certificate name.
-
Click Save to save your APNs certificate in NinjaOne and complete the Apple MDM configuration process.
-
Done. You now have Apple MDM configured in NinjaOne and can deploy Apple management profiles to your macOS, iPadOS, and iOS devices.
Step 3 - How To Configure and Download Your Apple Configuration Profile in Keytos Shield for EAP-TLS
The following steps all require you to have completed the Keytos Shield onboarding steps. Please complete the onboarding steps before proceeding.
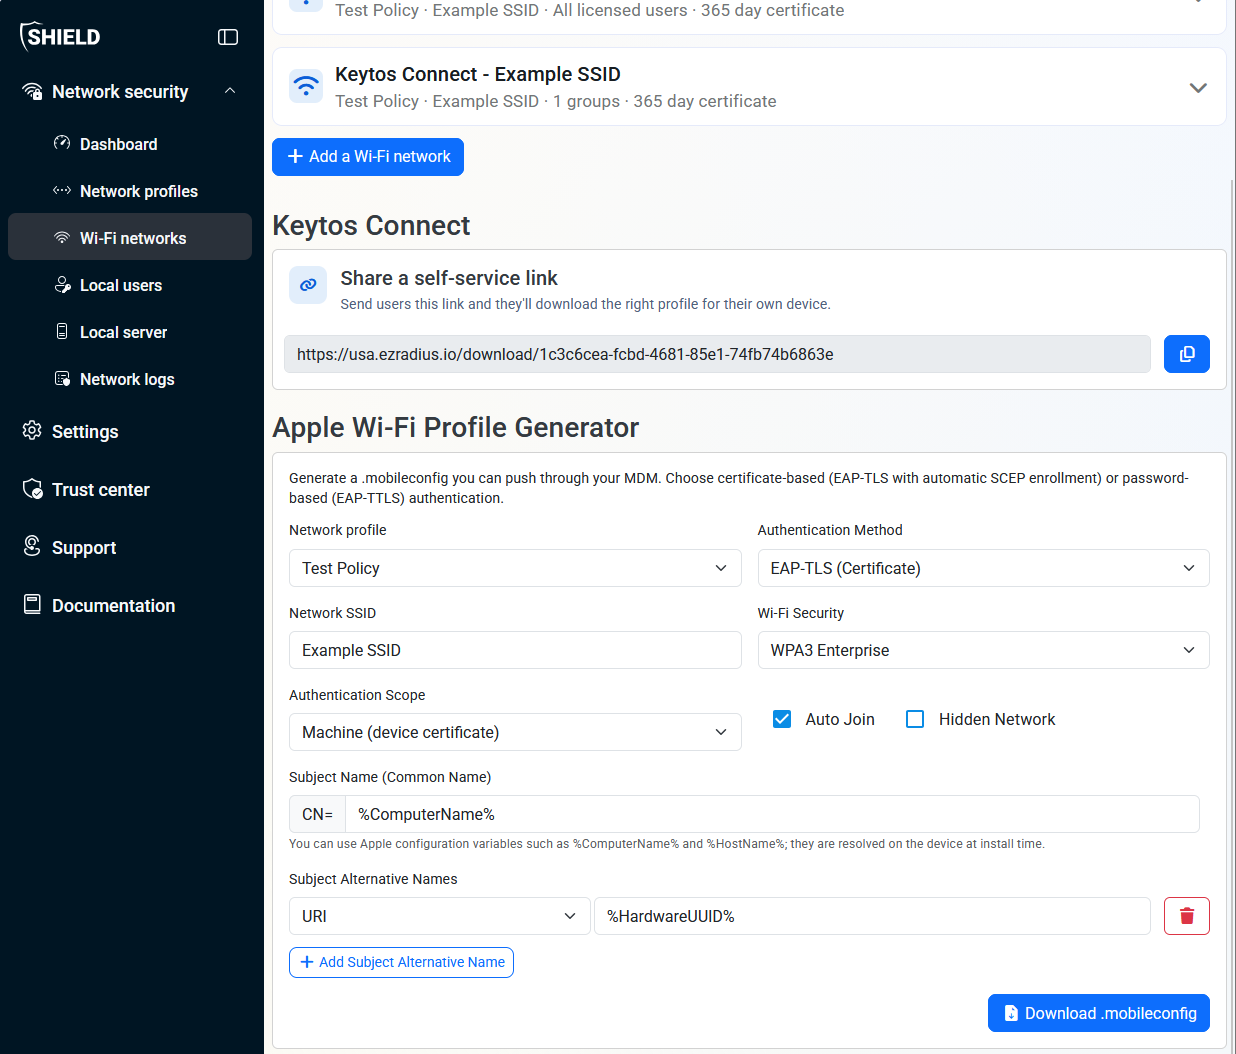
The following section will guide you through the steps to configure and download your network profile to use RADIUS authentication with EAP-TLS for Shield. This will create a .mobileconfig file that includes all the certificates and a Wi-Fi profile needed for certificate-based authentication.
-
Log into your Keytos Shield portal.
-
From the left-hand menu, navigate to Wi-Fi networks.
-
Scroll down until you see the Apple Wi-Fi Profile Generator section.
-
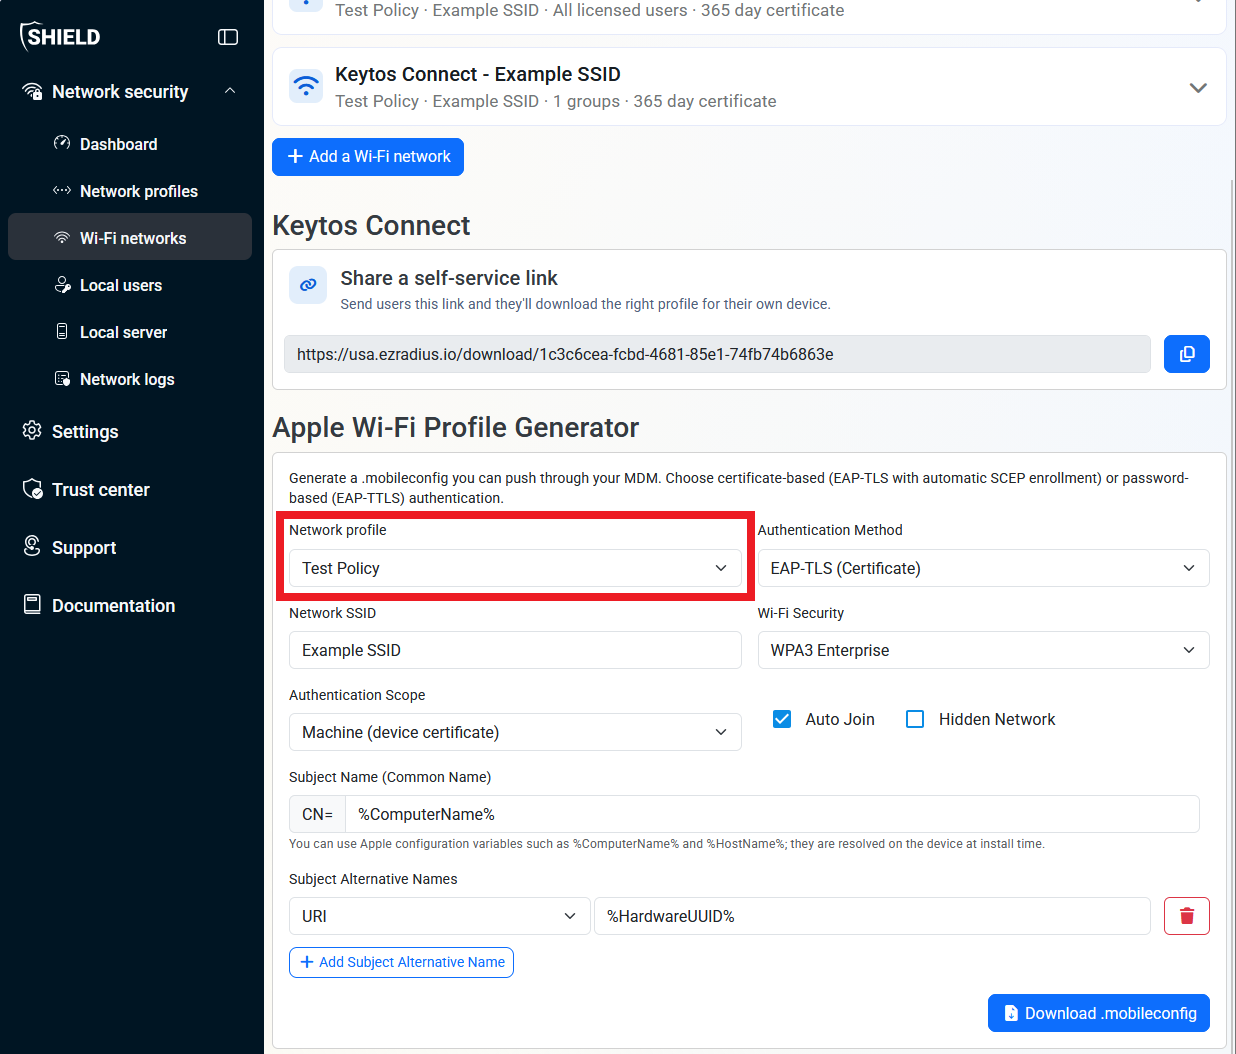
Select your Network profile.
-
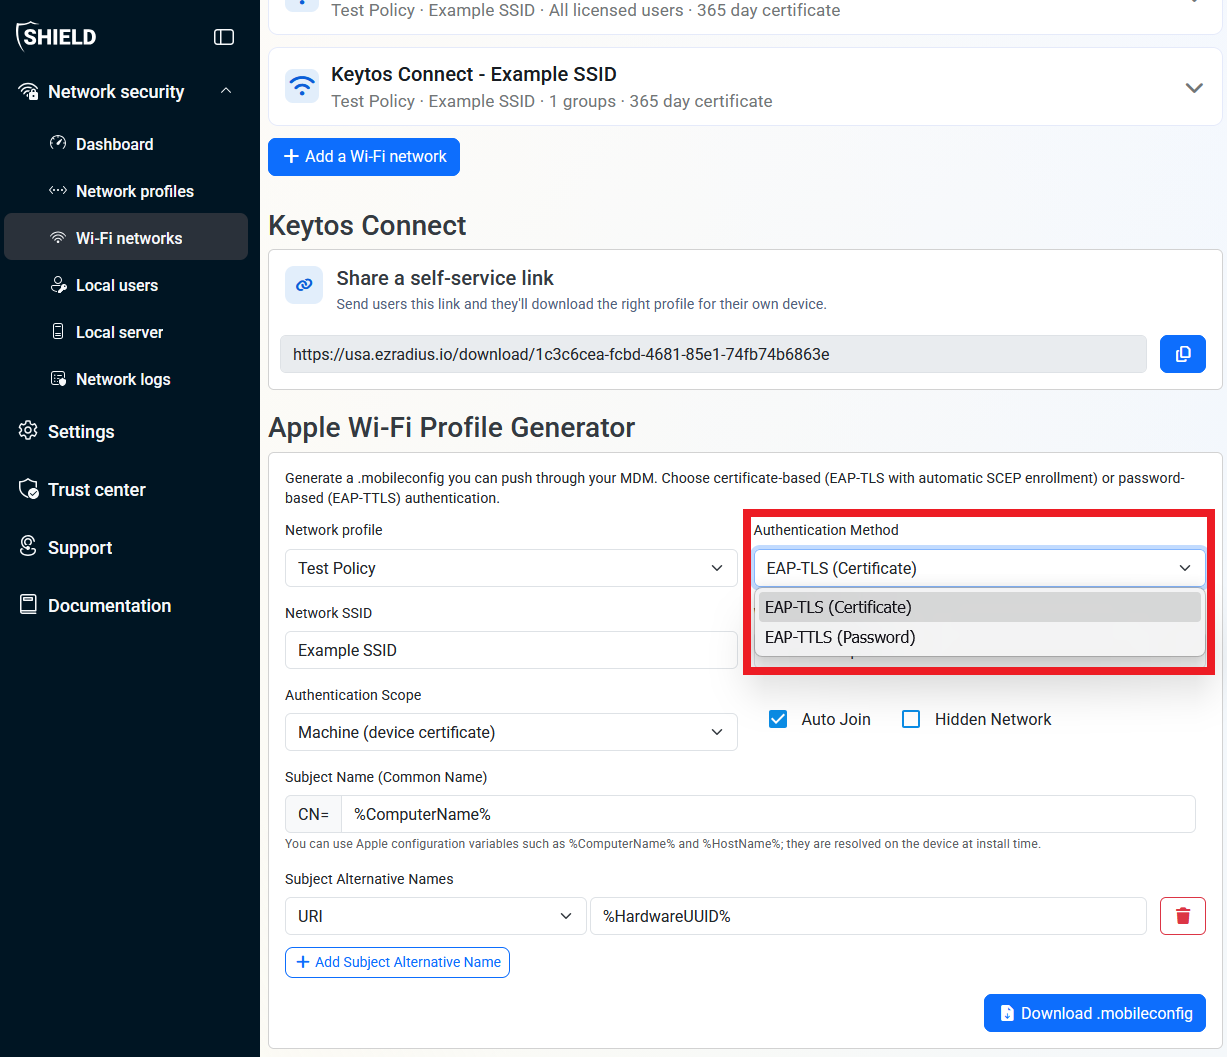
For Authentication Method, select EAP-TLS (Certificate).
-
For Network SSID enter the SSID of your network (This is case sensitive).
-
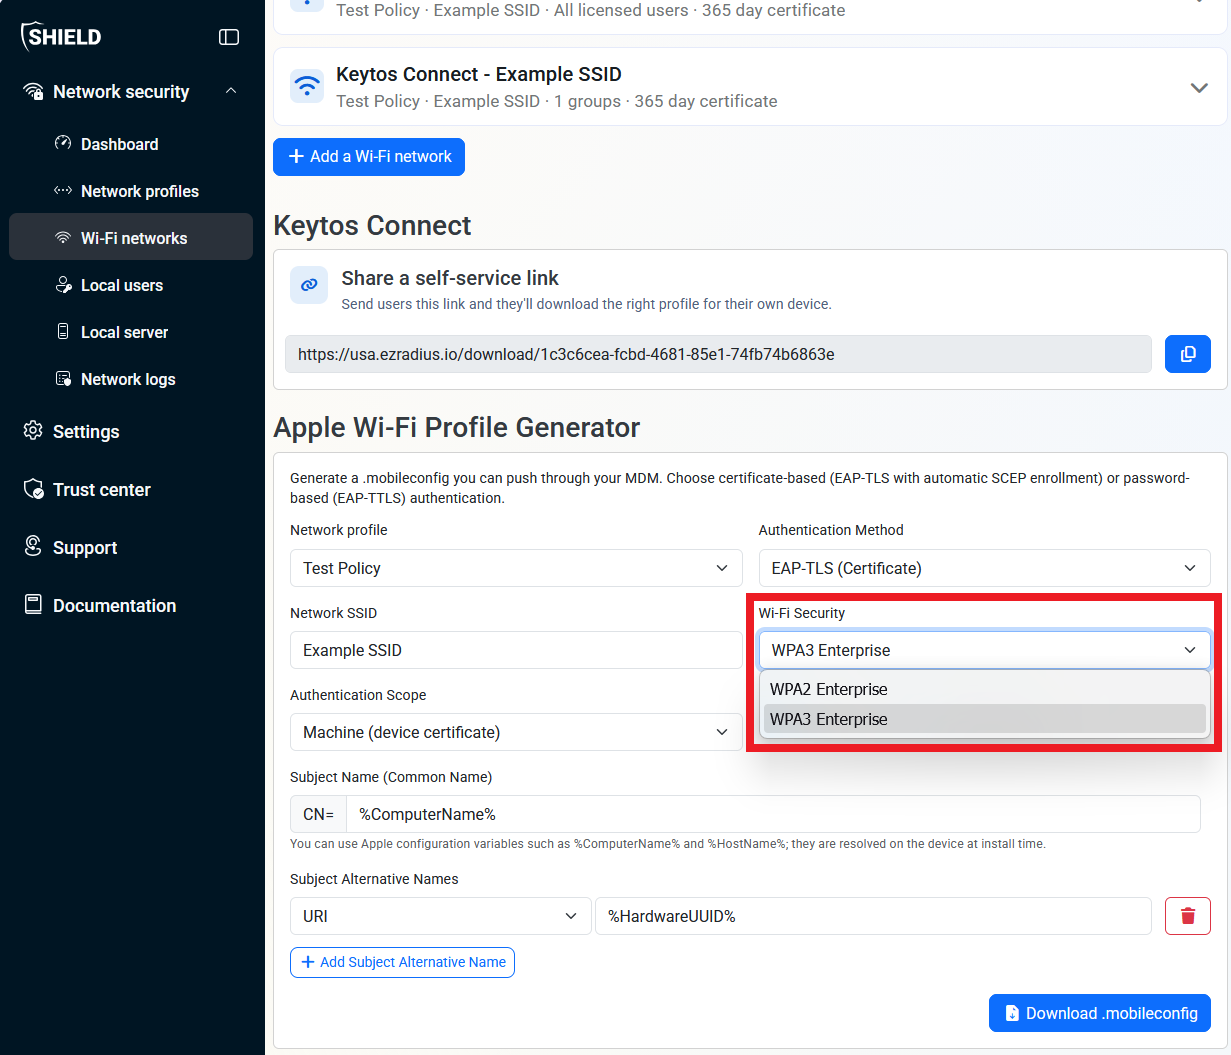
For Wi-Fi Security, select either WPA3 Enterprise or WPA2 Enterprise depending on how your network is configured.
-
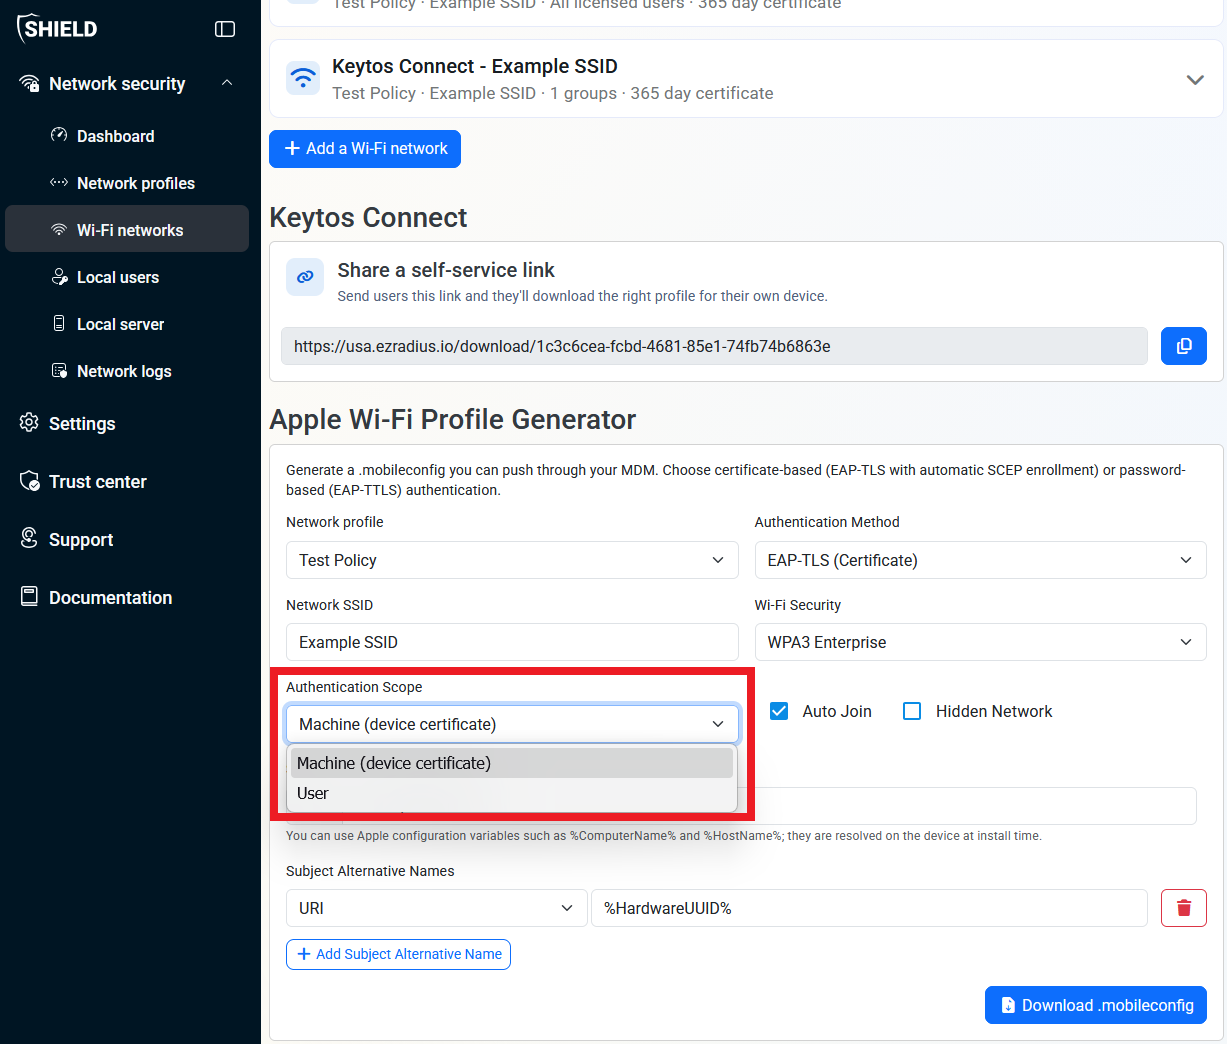
Select Machine (device certificate) to make your Apple Configuration Profile use device certificates or User for user certificates.
Make sure to choose the same auth type you set during onboardingWhen selecting device or user certificates, make sure you match the authentication type you set during the onboarding process. If you’re unsure, check your Network profiles page under Access Policies.
-
Check Auto Join if you would like devices to automatically join the network without prompting users.
-
Check Hidden Network only if your Wi-Fi access point does not broadcast its SSID.
-
Configure the Subject Name and any Subject Alternative Name values you need using Apple or NinjaOne-specific variables.
How do the Apple and NinjaOne variables work?When you set your Subject Name and Subject Alternative Name (SAN) fields in the Configuration Profile, you can use variables that will be replaced with device-specific and user-specific values when the profile is deployed. See the NinjaOne documentation for more information on their available variables and how to use them in your management profiles. You can also use Apple’s built in variables as well, in combination with NinjaOne’s variables and static values.
NinjaOne’s Variables:
Variable Description ${device.location.name}This is the device’s assigned location name value. ${device.location.id}This is the device’s assigned location ID value. ${device.organization.name}This is the device’s organization’s name value. ${device.organization.id}This is the device’s organization ID value. ${device.serialNumber}This is the device’s serial number value. ${device.id}This is the device’s GUID value (unique identifier). ${device.owner.email}This is the device’s assigned user email address value. ${device.owner.firstName}This is the device’s assigned user’s first name value. ${device.owner.lastName}This is the device’s assigned user’s last name value. ${device.owner.displayName}This is the device’s assigned user’s display name value. Apple’s Built-in Variables:
Variable Substitution %ComputerName%The Mac computer’s name, as set in Sharing (in System Settings > General for macOS 13 or later, or in System Preferences for macOS 12.0.1 or earlier). %HardwareUUID%The Mac computer’s unique identifier. %HostName%The Mac computer’s DNS name, such as mac1.betterbag.com. %LocalHostName%The Mac computer’s local network name, such as Mac1.local. %MACAddress%The Mac computer’s Ethernet (en0) MAC address. %SerialNumber%The Mac computer’s serial number. A good set of values to use would be:
- Subject:
CN=%ComputerName% - URI SAN:
%HardwareUUID% - DNS SAN:
%HostName%
- Subject:
-
Once you have configured everything, click Download .mobileconfig. This should download as a
.mobileconfig.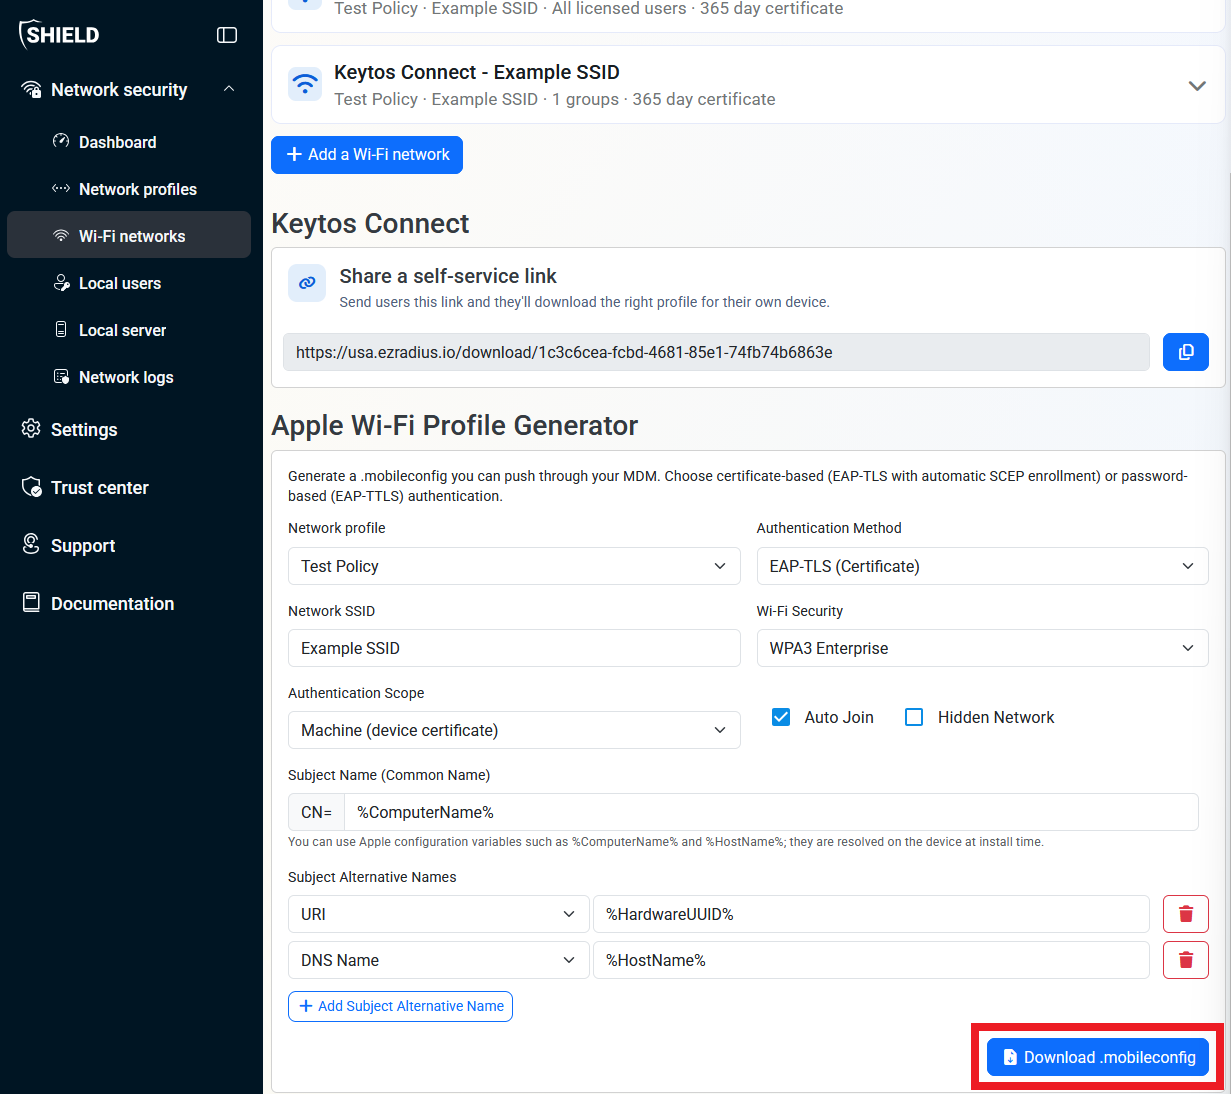
Done! You should now have an Apple Configuration Profile you can distribute to your NinjaOne devices.
Step 4 - How To Distribute Your Apple Configuration Profiles to NinjaOne Devices
-
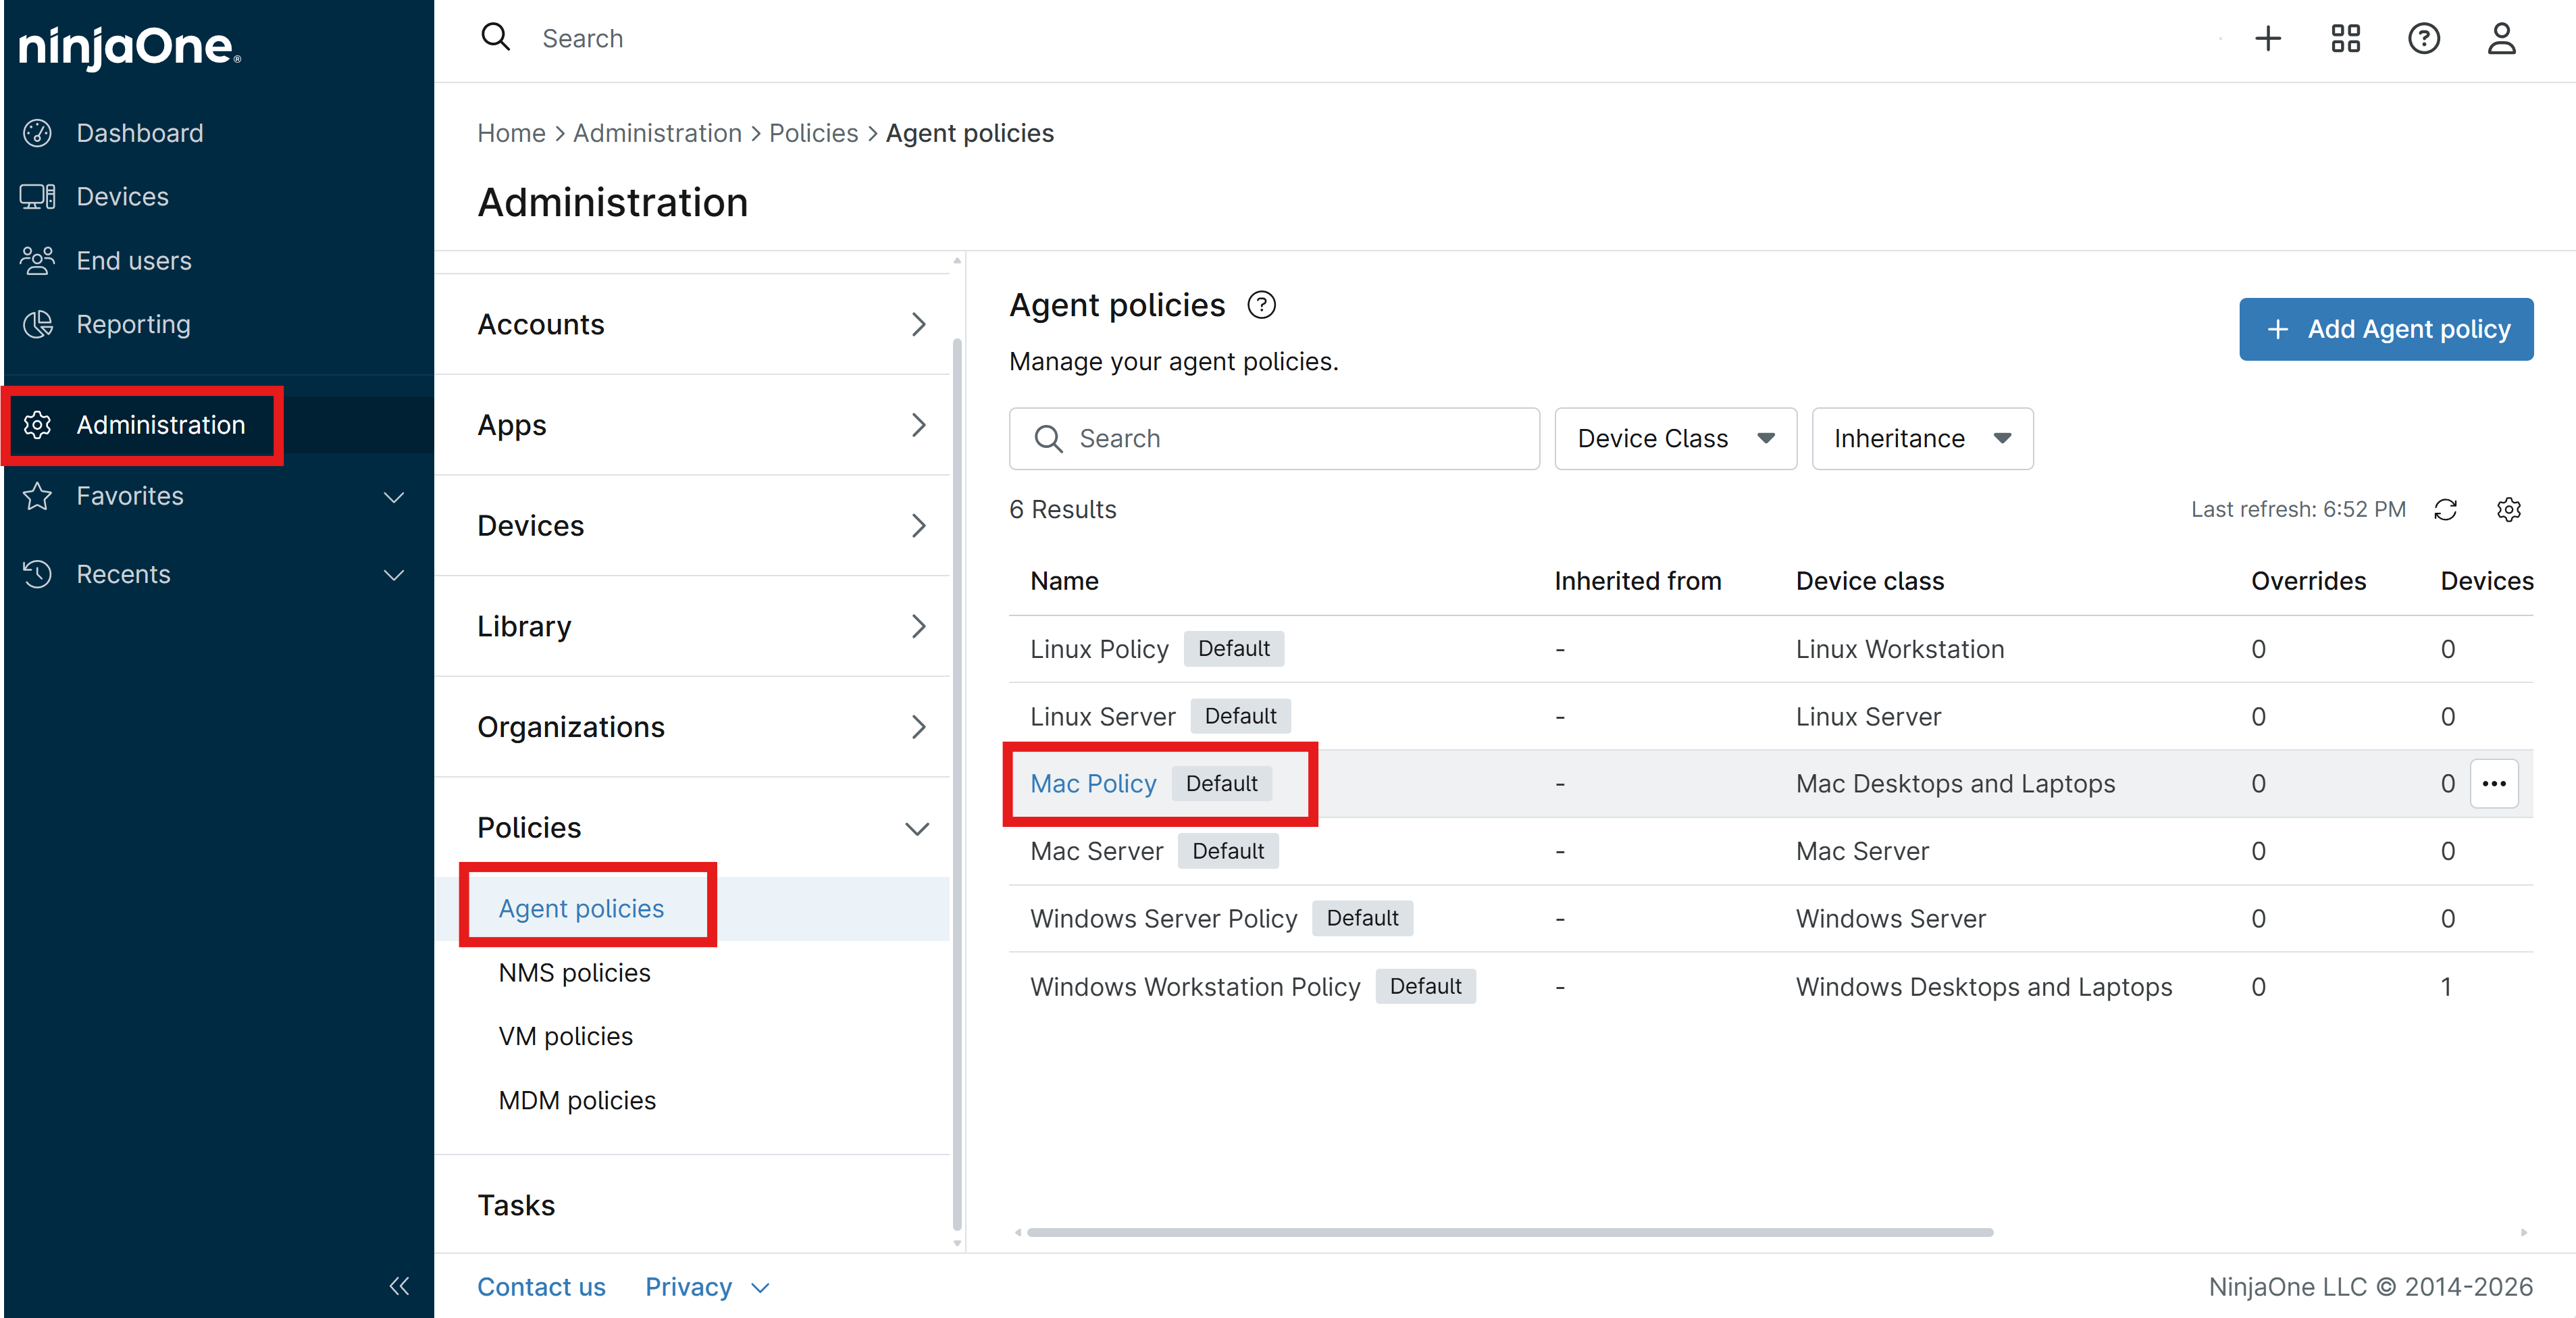
In the NinjaOne portal, navigate to Administration > Policies > Agent policies and select the Mac policy you want to deploy the profile with, or create a new policy if needed.
-
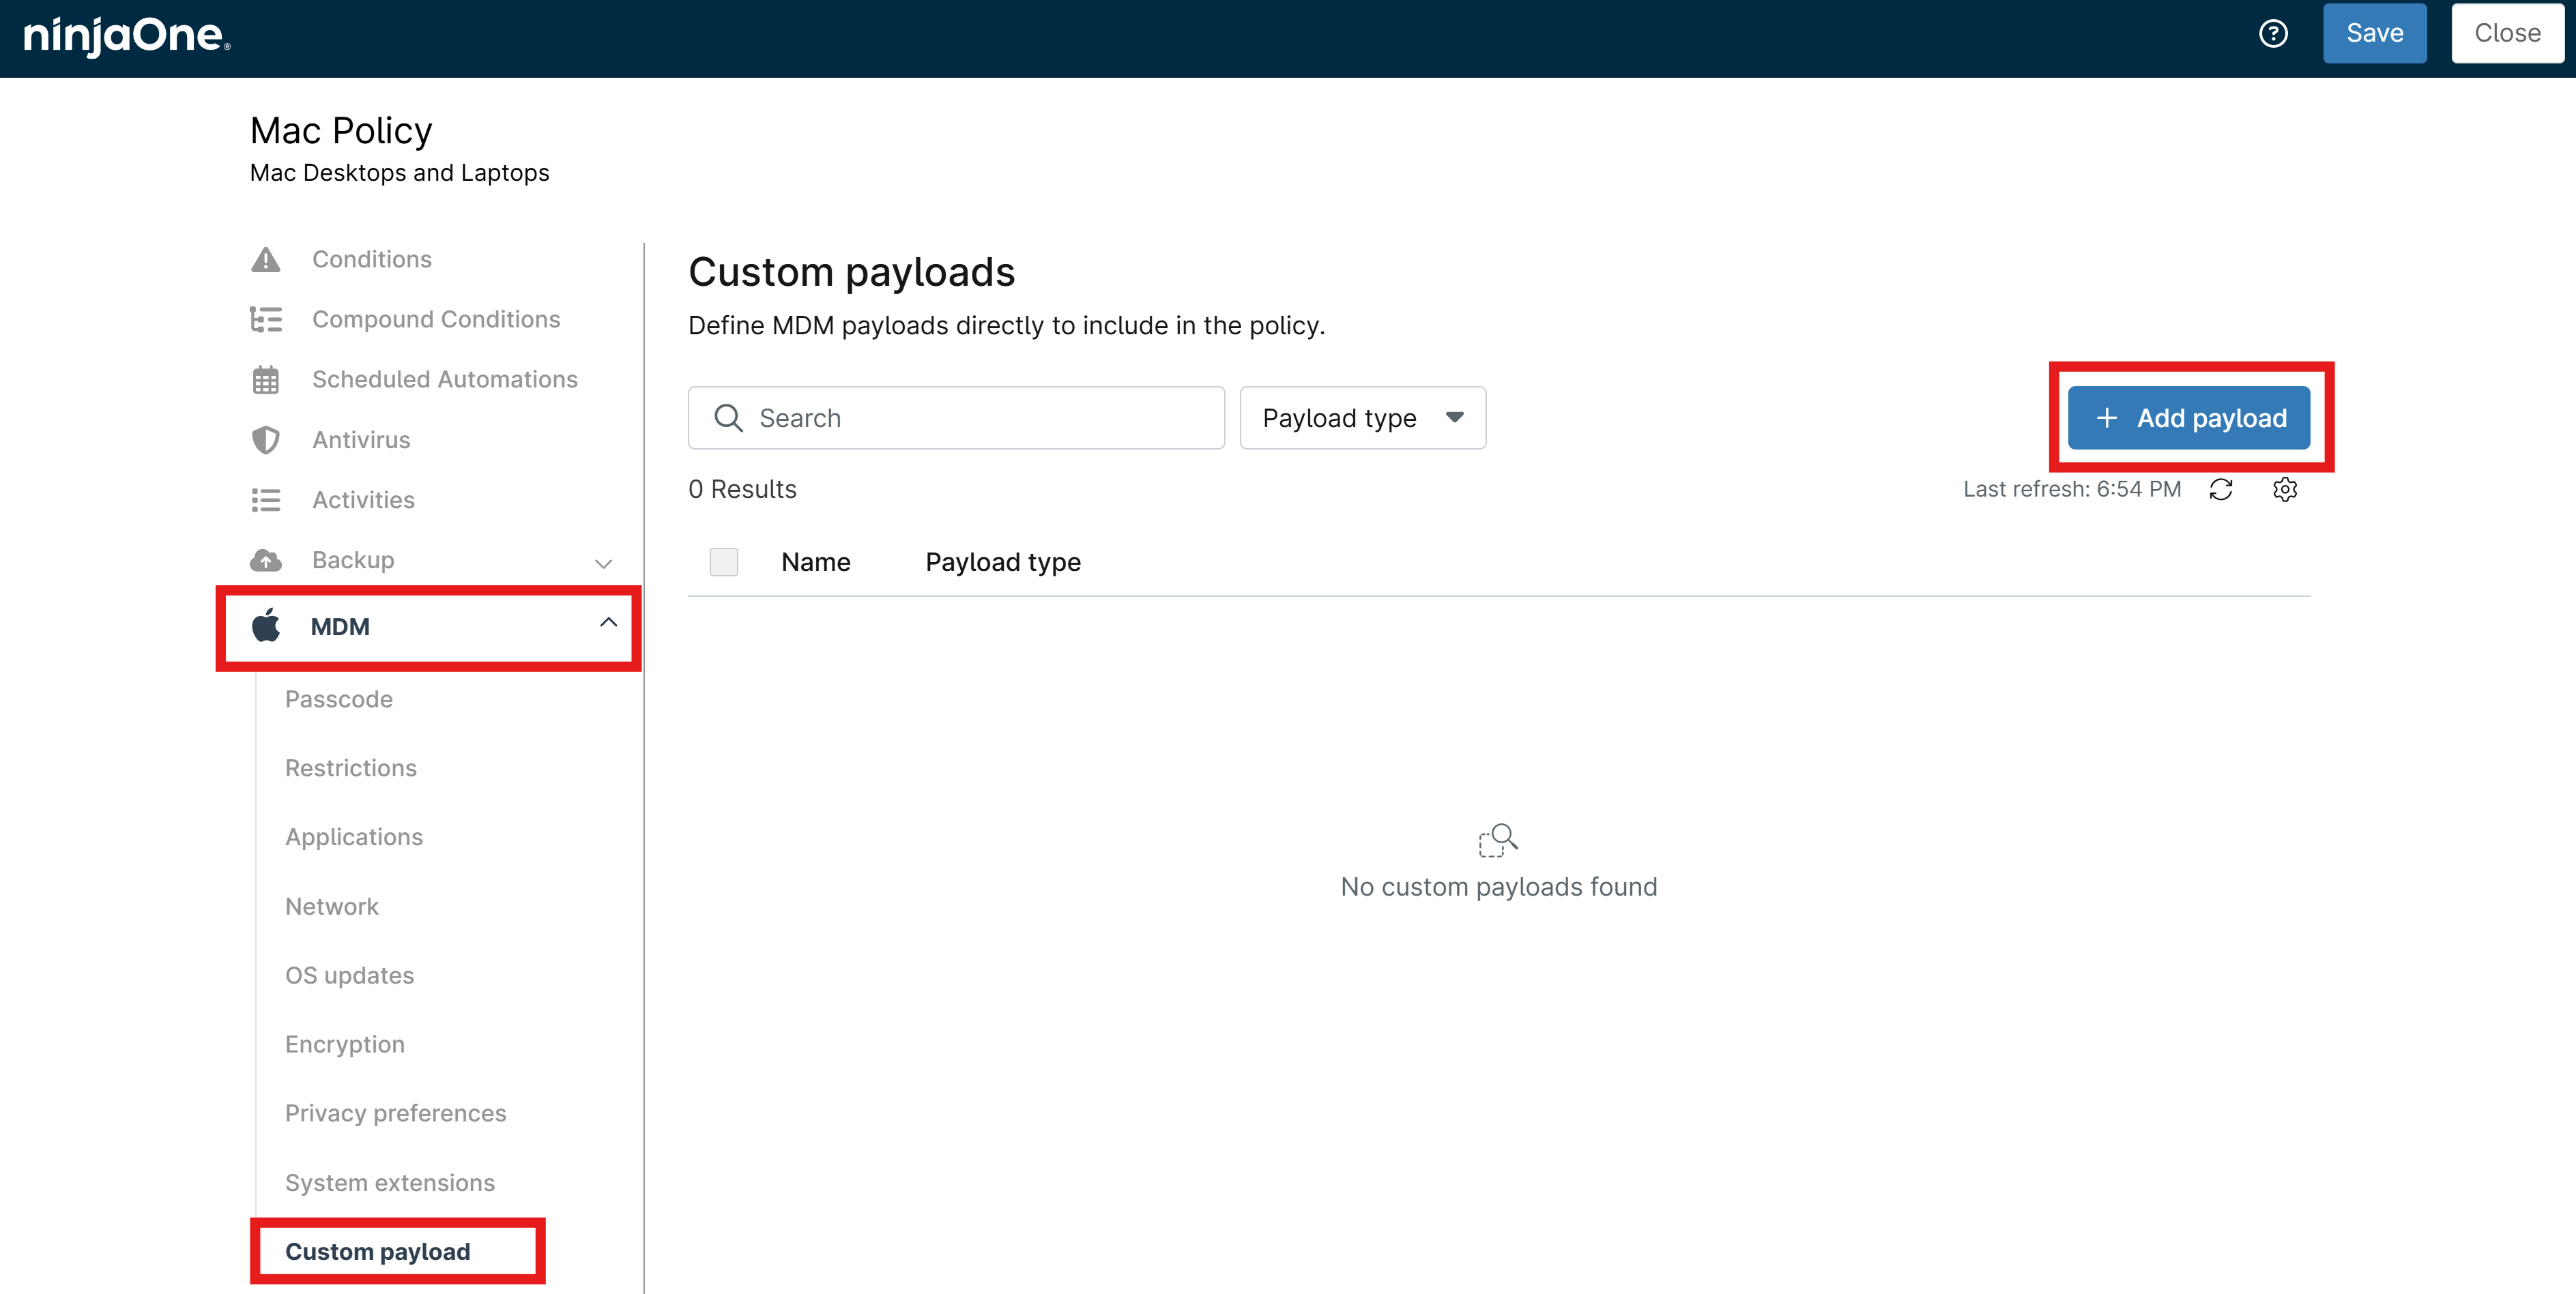
From the left-hand menu, select MDM > Custom payload and click on the + Add payload button.
-
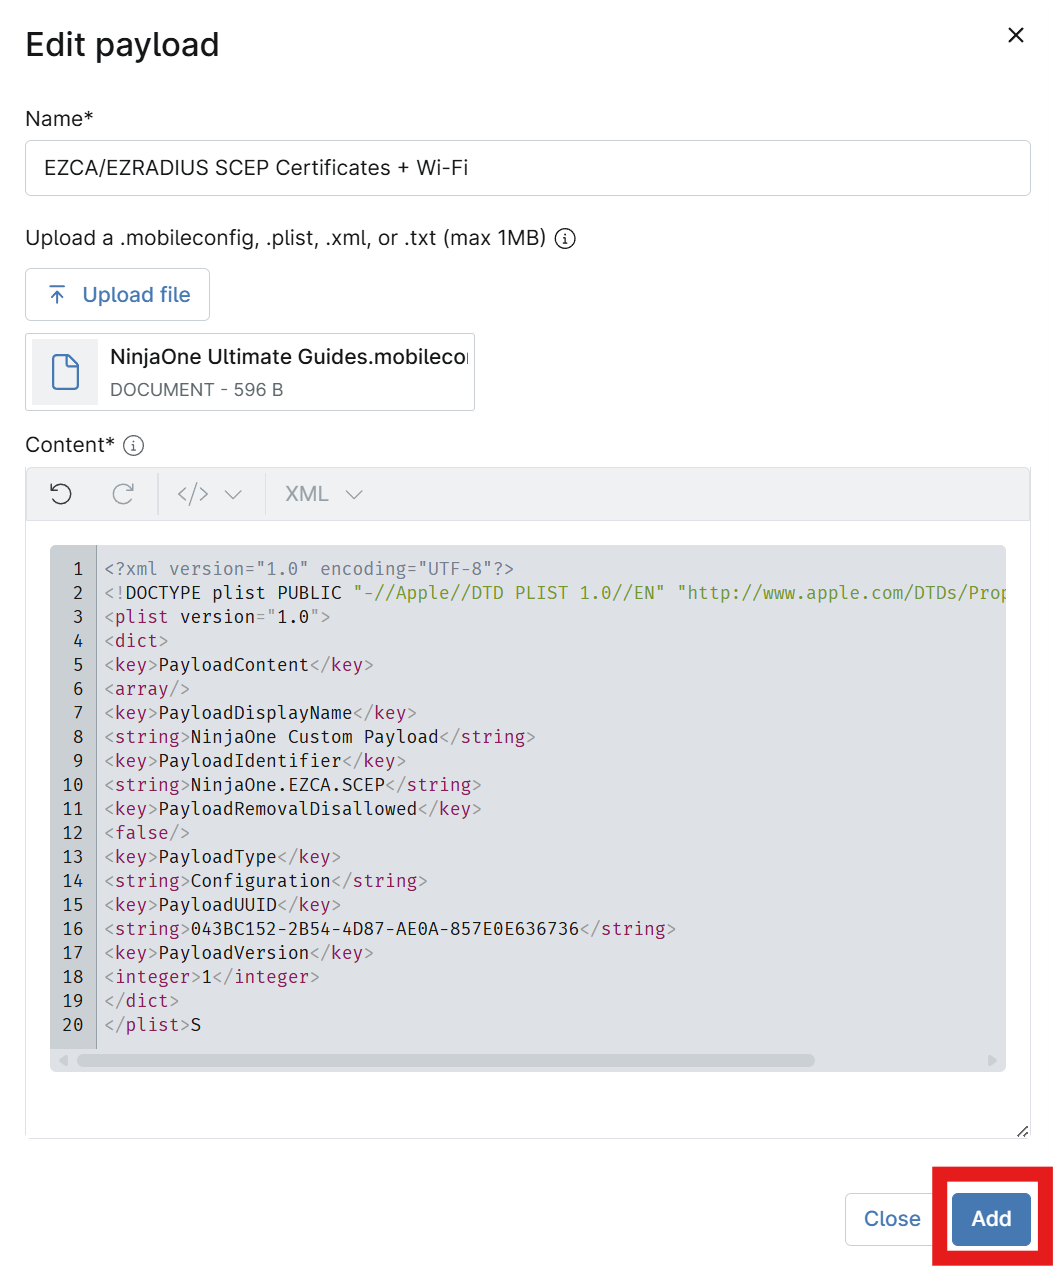
Set the Name to
Keytos Shield - Wi-Fi Profile(or a name of your choice), and click Upload file to upload the.mobileconfigfile you created in the previous step.- If you previously set up SCEP certificate issuance, you can rename your existing SCEP profile to add “Wi-Fi” to the name to make it easier to identify that this profile includes both the SCEP certificate and the Wi-Fi profile.
-
Click Add to add the custom payload to the policy.
-
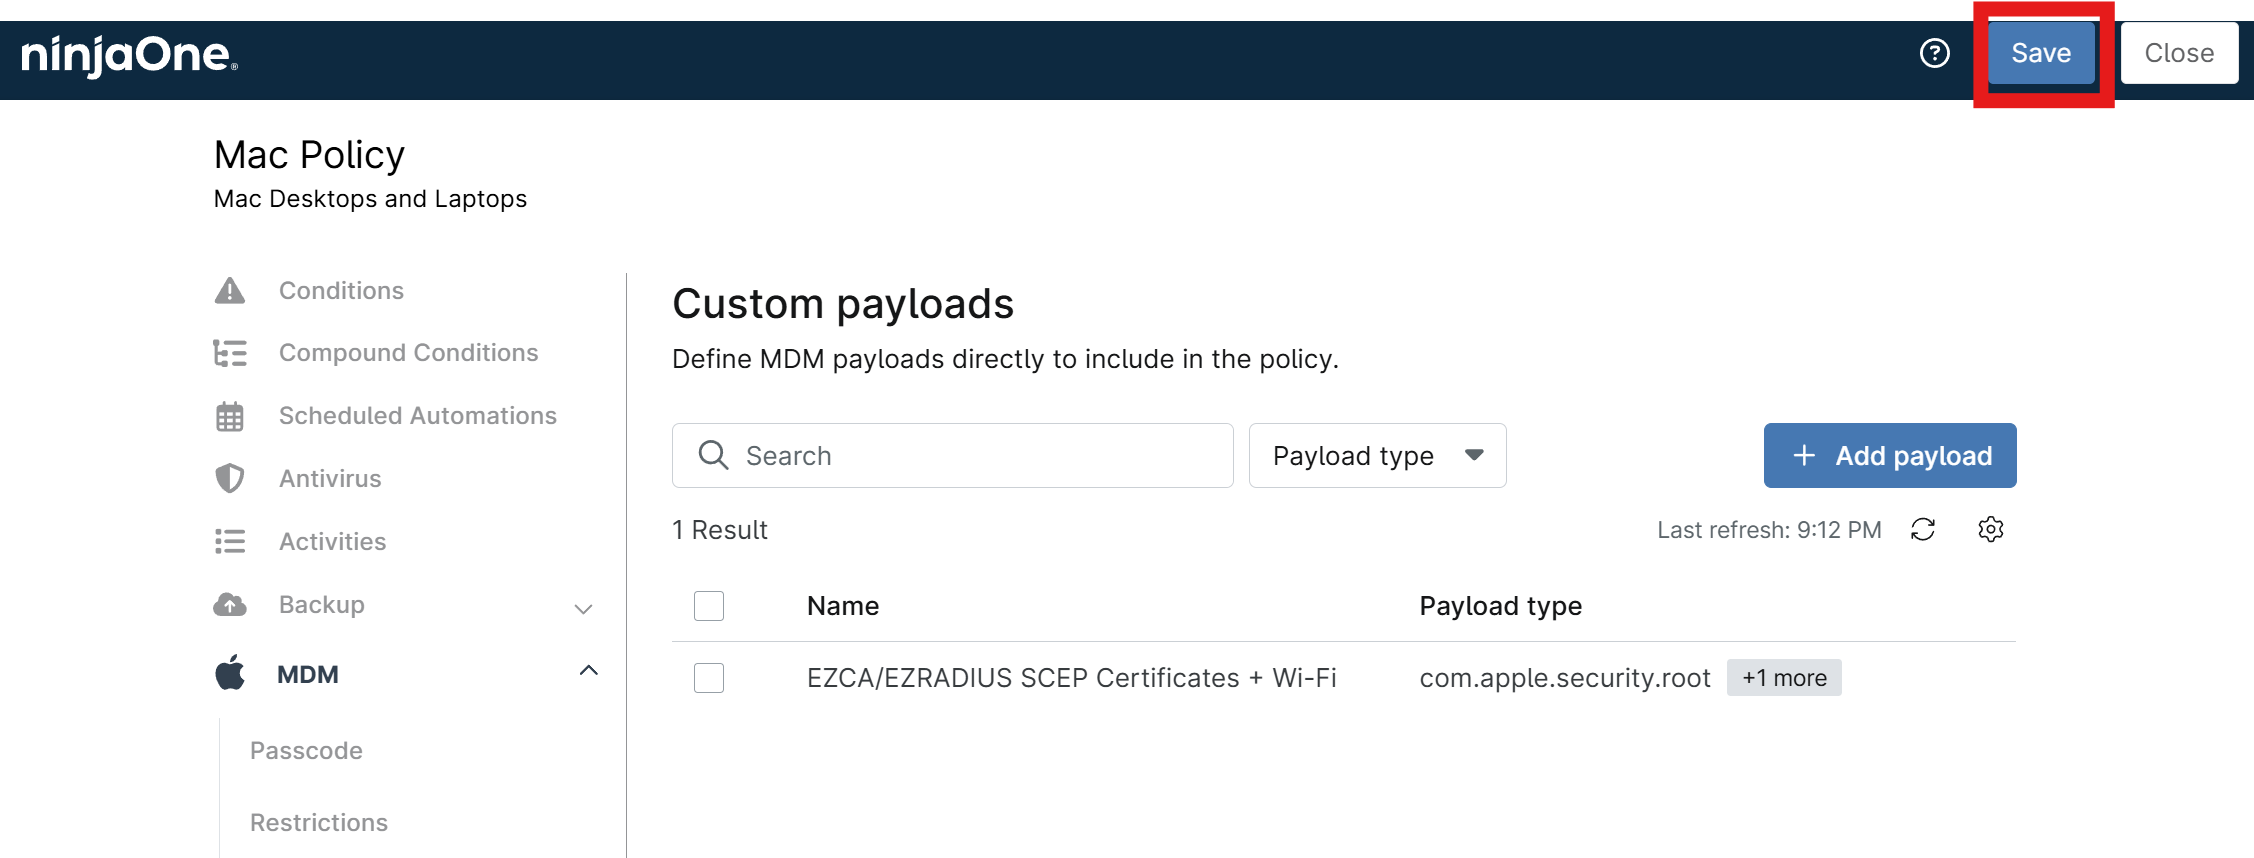
In the top-right corner, click on the Save button to save your changes to the policy.
Step 5 - How to Join Your macOS Devices to NinjaOne via MDM Enrollment to Receive Custom Payloads
In order for your macOS devices to receive the Apple management profile with the Wi-Fi payload that you deployed in the previous step, they will need to be enrolled via the MDM enrollment profile method. Enrolling via a DMG or PKG installer will not work for receiving MDM-deployed custom profiles, as those enrollment methods do not establish the necessary MDM management channel between the device and NinjaOne for deploying profiles.
We will show the steps for enrolling Macs via MDM enrollment, however the steps will be similar for iOS/iPadOS:
-
Navigate to your NinjaOne portal.
-
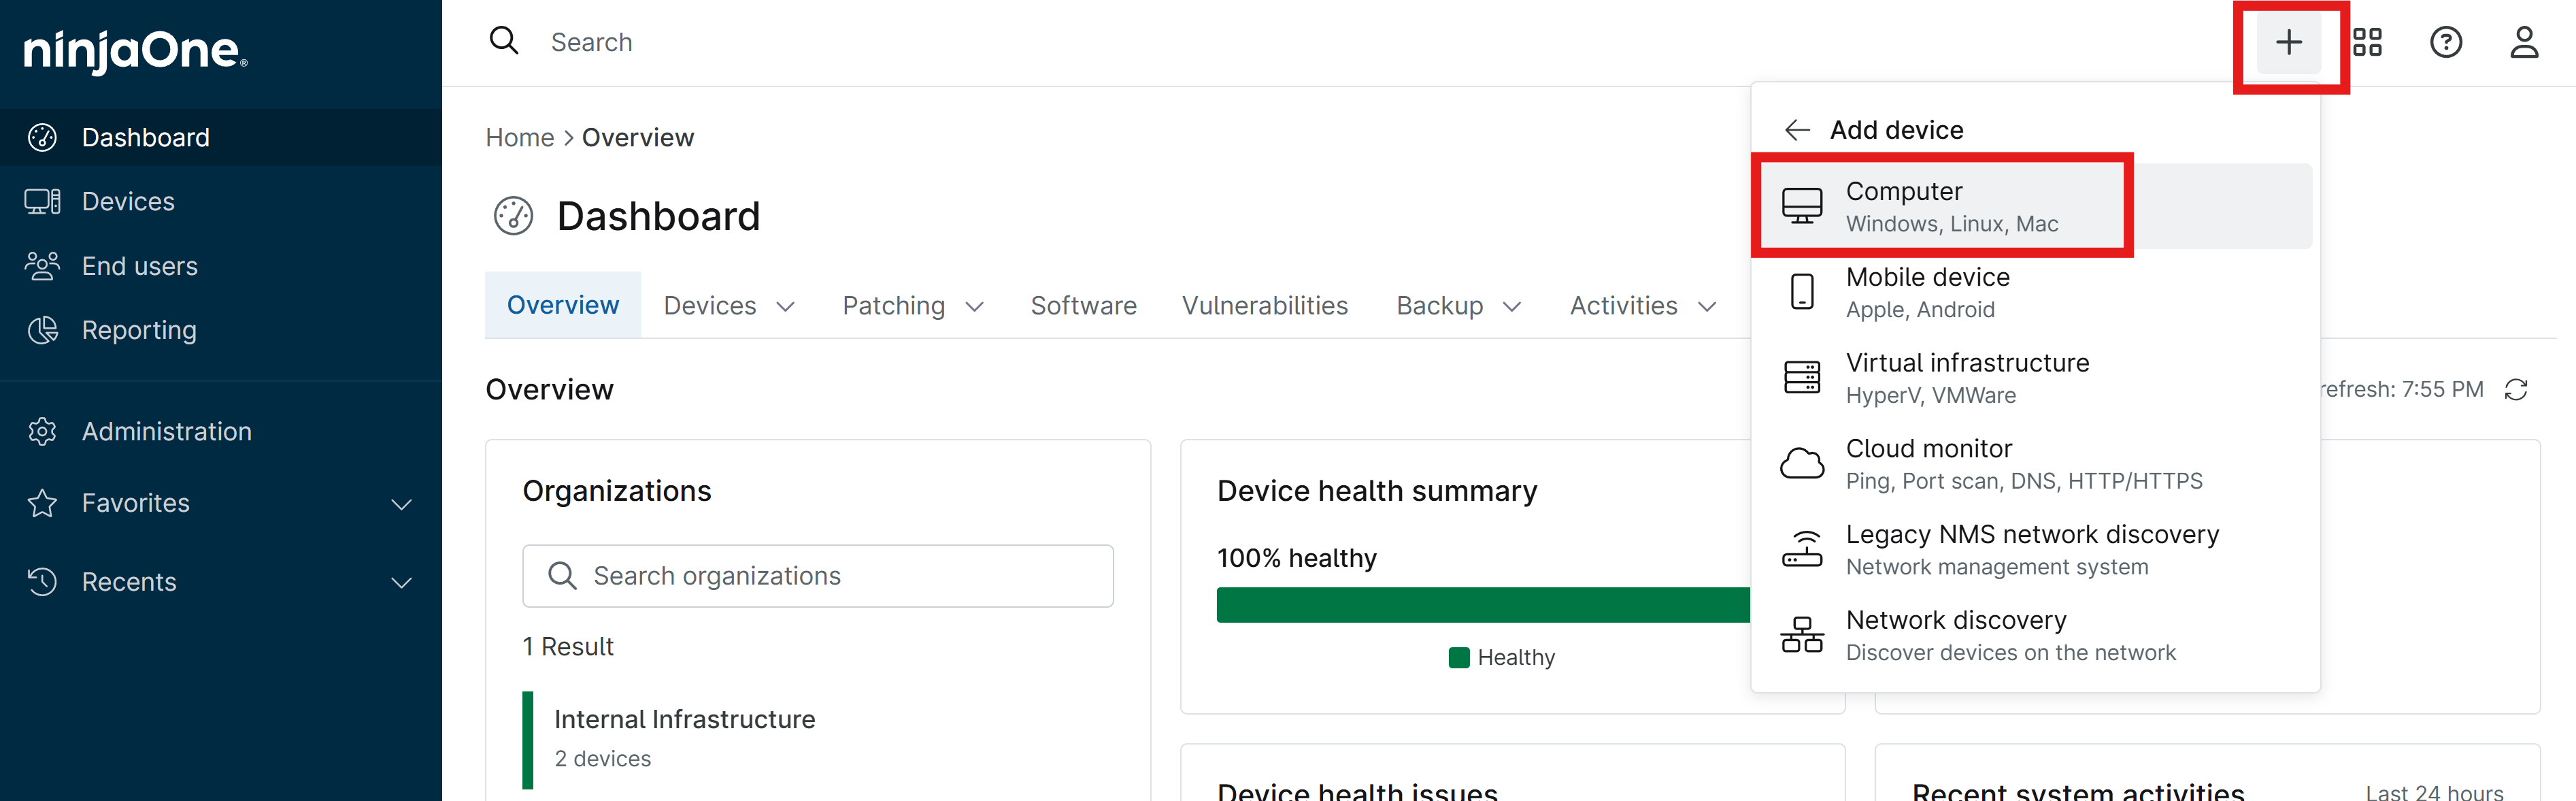
In the top-right corner, click the + button, then Device, then Computer.
-
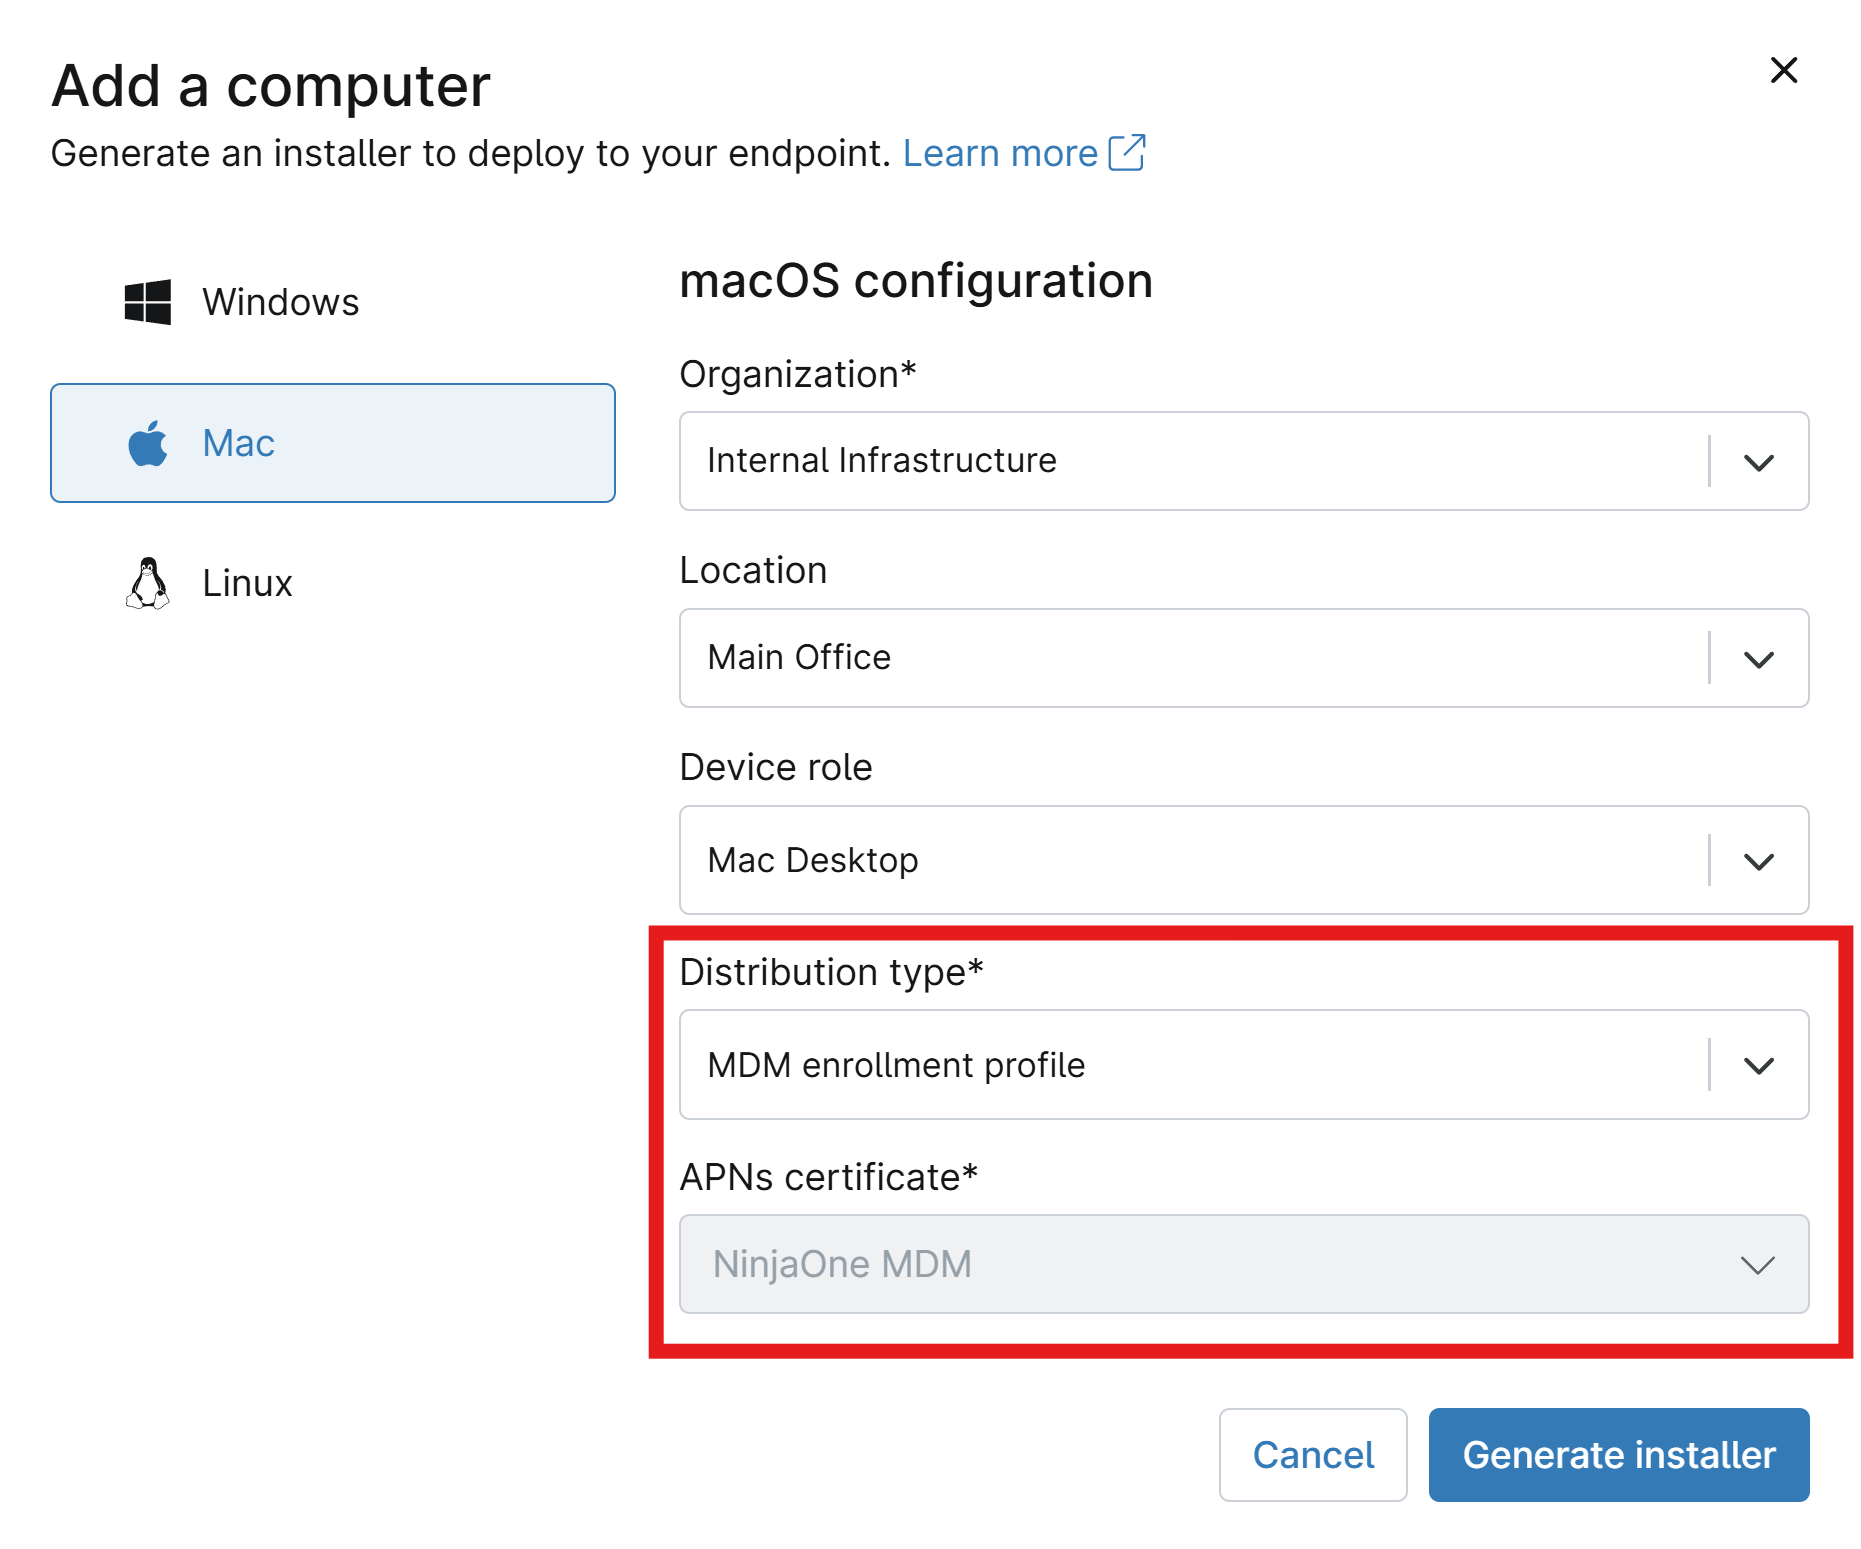
Select Mac and fill in your organization/location/role information.
-
Set Distribution type to MDM enrollment profile and select your APNs certificate if you have more than one.
-
Click Generate installer and distribute the generated
.mobileconfigfile to your users to install on their devices and complete the enrollment process.
Done! Once your users install the NinjaOne enrollment profile, NinjaOne automatically pushes your Shield Wi-Fi profile and the device can connect using its certificate.
How to Test the Wi-Fi Certificate Authentication Setup
Now that you have configured your NinjaOne Wi-Fi profile to use Cloud RADIUS for authentication, the next step is to test the configuration on a managed macOS device. Follow these steps to test your Wi-Fi configuration:
-
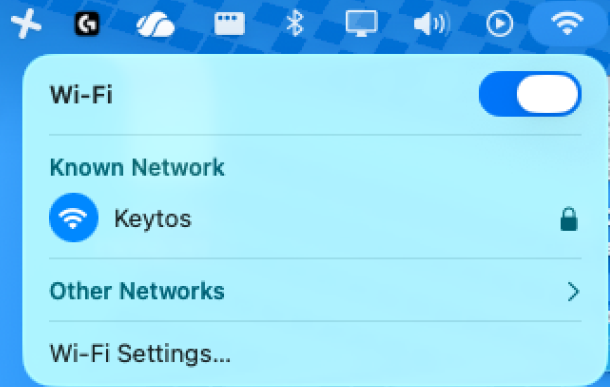
On a managed macOS device, click on the Wi-Fi icon in the menu bar and select the Wi-Fi network that you configured in your NinjaOne Wi-Fi profile.
-
If your configuration is correct, the device should successfully connect to the Wi-Fi network without any prompts.
-
If you are prompted to select a certificate for the network, your Wi-Fi profile is not fully configured: usually the RADIUS server’s Subject and Subject Alternative Names are missing from the trusted server names, a CA in the server certificate chain is not trusted, or the SCEP certificate has not been issued to the device yet.
How to Troubleshoot RADIUS Authentication for Keytos Shield
If you are unable to connect to your network, refer to our troubleshooting guide.
Shield RADIUS Troubleshooting Guide